



André Baptista retweeted

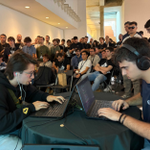
For the second year in a row, Ethiack ran the CTF at @BSidesLisbon. The final match lasted over an hour and 15 minutes, and more than 50 people stayed to watch it live.
We also took the stage: Our Research team brought their DEFCON talk, “Write Once, Shell Everywhere: Turning Arbitrary File Writes into RCE,” to Lisbon.
Huge thanks to our team and to everyone who came to play, watch, and cheer. And to BSides Lisbon for having us back.
Stay tuned. we'll share more details in the coming days!


CTFs ain't dead!
We organized a speed pwning CTF at @Bsideslisbon. No AI, human-only.
Congrats to the winners!
1st- s1gn3rs
2nd- h11p13
3rd- tmv11


André Baptista retweeted

BSides Lisbon is on fire! 🔥
As always every year, the spirit and vibe here are just incredible.
Super excited about the Speed PWN CTF we created at @ethiack !
The finals are tomorrow: 1v1, Humans only
Also, big congrats to @s3np41k1r1t0 and @castilho101 for an amazing talk on stage today!
You guys killed it !
#BSidesLisbon #Ethiack #SpeedPwn


André Baptista retweeted

Just dropped a new blog post! 🔥
blog.orange.tw/posts/2026-10…

Attackers often exploit new vulnerabilities before defenders can react, sometimes before the vulnerability even gets a public ID (a CVE).
In the first half of 2026, 487 vulnerabilities were listed as exploited. For 137 of them (>25%), the exploitation record existed on or before the day the CVE was published.
We built Ethiack Zero to track emerging vulnerabilities from the first public signal (a patch, a GitHub advisory, news, a blog post) and validate actual exploitability before the CVE is officially published.
Check it out below👇


Live hardware hacking is coming to @BSidesLisbon.
Get ready for the @Ethiack SOHO Smashup on Friday, October 30! Inspired by Pwn2Own, we’re dropping real, aging office equipment right on the floor:
• One office router
• One printer
The challenge: Hack them live in the lounge area in front of an audience.
Get creative with your exploits, AI is fully allowed, and we are accepting any kind of vulnerability. Just visit us in the lounge to schedule your time slot.
Goodies await anyone with a successful exploit. See you there 👇


André Baptista retweeted
🚨CVE-2026-111497 (Node2Shell): a critical flaw in Google's Brotli decoder may let remote attackers execute code on servers that decompress untrusted Brotli data.
Affects Node.js and Bun. Patch now: Node.js 22.23.4 / 24.22.1 / 26.12.1, Bun 1.4.4.
ethiack.com/info-hub/researc…

André Baptista retweeted

Published our high fidelity scanner for node2shell: github.com/assetnote/node2sh…
Detection logic was written by @hash_kitten late last week. Open sourcing it to do public good in detecting this issue black box.

André Baptista retweeted
Attackers don’t wait for the CVE. Neither does Ethiack Zero, now live for 3 days.
Here’s why we built it 👇
ethiack.com/info-hub/researc…

André Baptista retweeted
Just published our high fidelity scanner for php2shell: github.com/assetnote/php2she…
See our detection logic here: slcyber.io/research/high-fid…
We've taken care in our detection logic and hope it helps defenders. Congrats to @calif_io and @lcfr_hax for the discovery.

André Baptista retweeted
Two critical RCE flaws in PHP itself: CVE-2026-109618 and CVE-2026-109619 (CVSS 9.2). Every PHP stack is in scope. Fixes ship today at 14:00 UTC.
Early signal flagged by Ethiack Zero. Ethiack now identifies the PHP runtimes you expose and flags EOL ones.
ethiack.com/info-hub/researc…

André Baptista retweeted

The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
We’re continuously reversing the emerging 0days that matter most, sometimes before they get a CVE, and publishing how fast we validate them vs how fast attackers exploit them.
👉 zero.ethiack.com

Yesterday we asked: what if you could turn back the clock?
We can’t, but we can see it sooner.
Ethiack Zero is live: a public record of emerging 0-days. Open feed, API, MCP and methodology. Check our numbers and tell us what’s missing.
zero.ethiack.com
André Baptista retweeted
Yesterday we asked: what if you could turn back the clock?
We can’t, but we can see it sooner.
Ethiack Zero is live: a public record of emerging 0-days. Open feed, API, MCP and methodology. Check our numbers and tell us what’s missing.
zero.ethiack.com
André Baptista retweeted
Think you are the fastest hacker?
Prove your skills in the CTF at @BsidesLisbon 2026 run by Ethiack
For this edition, we are bringing: Speed Pwning CTF
Two players go head to head. Each match presents both competitors with the same CTF challenge at the same moment. The first to submit a valid flag advances. Losers are eliminated.
- 8 participants
- Single-elimination bracket
- 30-minute matches
- No qualifiers
- Brackets are drawn at random
Find all the details and register below↓