
Fortra delivers AI-amplified data security software solutions that help organizations use and protect their data with confidence.
Eden Prairie, MN
Joined July 2015
- Tweets7.4K
- Following1.3K
- Followers2.8K
- Likes653




A ransomware gang claimed it had “morals and a heart” after an attack disrupted care at UNM Health Sciences Center.
BYOD offered free decryption for hospital systems but said it would keep allegedly stolen data.
Graham Cluley reports: hubs.la/Q04CS5120

A deepfake video call convinced an employee to transfer $25 million.
Fortra's Eli Vovsha explains why AI-generated impersonation is getting harder to detect and why verifying requests through trusted channels matters more than ever.
hubs.la/Q04CS4-f0

A sensitive file can move from a server to an inbox to a laptop. Its protections should follow it.
For #CybersecurityAwarenessMonth, Fortra's John Grancarich shares how consistent classification and access controls can make attackers work harder.


Shadow AI can access data, connect systems and take action before security teams know it exists.
Fortra’s Rohit Dhamankar explains why CISOs need greater visibility, stronger controls and ongoing AI red teaming.
Read more: hubs.la/Q04CCkYS0

Who's really winning the cybersecurity cat-and-mouse game?
The latest episodes of The Art of Security explore CalPhishing, AI-powered red teaming, security theater and the shortcuts attackers exploit.
Catch up with Josh Davies, Tyler Reguly and guests: hubs.la/Q04CCkTC0

Discover how cloud email protection uses automated processes to clean up threats and respond to attacks without human intervention.
hubs.la/Q04CCkt-0
Do your AI safeguards hold up outside the policy document?
On Nov. 4, Fortra leaders discuss what AI should be allowed to access and do, how to test controls, and how CISOs can support responsible adoption.
Register: hubs.la/Q04CCkn80

An urgent payment request. A familiar name. A deadline designed to stop you checking.
For #CybersecurityAwarenessMonth, Fortra's JT Newby explains how verification and second approvals make attackers work harder.
Make them wait.


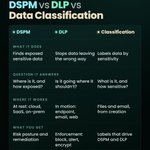
Your DLP can be working perfectly while sensitive data sits in an over-shared cloud folder.
Nobody has moved a file, so there's no outbound event to flag.
See where DSPM, DLP, and data classification each fit into the picture: hubs.la/Q04CrPsF0

UAE IA compliance needs to work in practice, not just on paper.
Fortra helps organizations support key requirements across data classification, data protection, monitoring, security awareness, and audit reporting.
hubs.la/Q04CrPsd0

A fake ChatGPT Plus payment page captures card details, then keeps victims waiting while a live operator decides whether to request their verification code.
FIRE's latest research examines the phishing kit, rotating WordPress hosts, and more:
hubs.la/Q04Cjcv_0

Web, applications, USB drives, printers. Sensitive data moves through multiple channels.
Fortra DLP users highlight endpoint visibility, compliance support, and early detection of unusual activity as valuable capabilities.👇
hubs.la/Q04B_BYk0


A first name and a Social Security number are both PII. They shouldn't trigger the same security response.
Effective data protection needs context, accurate classification, and controls that don't unnecessarily interrupt work.
Explore: hubs.la/Q04B_Bck0

At Black Hat 2026, Fortra’s Josh Davies joined Security Weekly to discuss what FIRE researchers are uncovering and why sharing threat intelligence matters.
hubs.la/Q04B_B7q0

Fake business opportunities are becoming a phishing lure.
Fortra researcher Cadence Riddle tracked a 12-fold rise in malicious RFQ emails, with nearly 73% leading to credential-phishing pages.
Help Net Security covers the findings: hubs.la/Q04C6jM30
Oracle's October Critical Patch Update includes:
• 1,295 new security patches
• 519 CVEs remotely exploitable without authentication
• 95 CVEs rated CVSS 9.0+
Fortra's Tyler Reguly breaks down the critical findings and remediation priorities: hubs.la/Q04B_B5h0

That missing dog post you shared? It might now be advertising a rental scam.
Fake giveaways, concert tickets, and celebrity DMs exploit the trust we place in social media.
Fortra's Tyler Reguly explains: hubs.la/Q04B_zyg0

Deleting a phishing email may not remove the threat.
Fortra's FIRE team found that malicious calendar invites can remain visible, complete with reminders, after the original email is gone.
Daud Jawad explains CalPhishing and what to watch for: hubs.la/Q04BTqNv0

AI can access data, connect systems, and act. Where should CISOs set the limits?
Join Fortra’s Matthew Reck, John Lehmann, and Chris Reffkin Nov. 4 to discuss AI guardrails, risk, and secure adoption.
Register: hubs.la/Q04BTnYH0

Fortra recorded 475% more phishing attacks using remote management tools in Jan–Sep 2026 than in all of 2025.
Attackers are exploiting fake banking support pages to gain remote access to victims' devices.
Our research, covered by Redmond Magazine: hubs.la/Q04BGRzQ0
