

Automating firewall migrations across vendors—with deterministic conversion, validation and expert review. Built for network & security teams. 99.8% accuracy.
Sarasota Florida
Joined August 2026
- Tweets47
- Following3
- Followers8
- Likes1





Chuck Robbins called aging, unpatchable infrastructure “a real emergency” at Cisco Partner Summit.
He's right.
But replacing a firewall isn't just swapping hardware. It's migrating years of policies without breaking production.
That's the challenge we're tackling at NetConverter.ai.
Modernization needs proof.
🤖 Made with AI

Chuck Robbins at Cisco Partner Summit (via SiliconANGLE): getting unpatchable, unsupported gear out of the network is "a real emergency."
Finding it is easy. Moving years of firewall policy with proof a change board accepts is the hard part.
siliconangle.com/2026/10/27/…
Cisco published CVE-2026-76418 yesterday: unauthenticated DoS against ASA/FTD SSL VPN when secondary authentication is configured on a tunnel group. CVSS 8.6. Cisco PSIRT reports active exploitation. No full workaround; upgrade is the fix. A mitigation is to disable secondary authentication on DefaultWEBVPNGroup or affected tunnel groups, with the tradeoffs Cisco documents.
Shadowserver currently tracks 51,000+ internet-exposed ASA SSL VPN devices.
For estates still running aging ASA hardware, every new zero-day is the same decision: patch in place, or migrate with evidence a change board will accept.
Advisory: sec.cloudapps.cisco.com/secu…
Your last security assessment said LOW RISK.
Would it say the same thing today?
AI is lowering the cost and skill required for some attacks.
Legacy firewalls and aging infrastructure can't be ignored forever.
Modernize. Migrate. Validate.
Don't just migrate it. PROVE IT.
🤖 Made with AI

AI is accelerating cyber threats. It can accelerate the defense, too.
We're exploring NetClaw + NetConverter.ai: agentic network orchestration meets automated firewall migration and validation.
Less technical debt. Faster modernization. Human control.
Don't just migrate it. PROVE IT.
🤖 Made with AI

Your firewall config is a credentials file.
Group-IB reports k0t downloaded FortiGate configs after gaining access, then decrypted the stored secrets offline with Fortinet's default key (CVE-2019-6693), including LDAP/AD bind and admin credentials.
Fix: enable private-data-encryption with your own key. Treat any exposed config as a credential disclosure and rotate what's in it.
group-ib.com/blog/stray-cat-…

Same PAN-OS version, different risk.
CVE-2026-111497 (Brotli, CVSS 9.2) matters on affected PA-Series/VM-Series builds only when Brotli inspection AND TLS decryption are both enabled. Brotli inspection is off by default. Palo Alto reports no known exploitation.
Version inventory says "affected." Config inventory says "exposed."
Interim workaround: disable Brotli inspection, then verify with: show system setting brotli
cybersecuritynews.com/brotli…

Your AI agent shouldn't have to reinvent firewall migration logic.
We're building NetConverter.ai to separate AI orchestration from deterministic configuration conversion.
One specialized engine. Multiple potential AI interfaces. Human-governed decisions.
Watch our MCP concept demo. 👇
Tested with Claude and @grok @bot . Other integrations shown are conceptual.
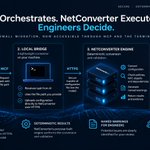
Firewall migration, now accessible through MCP and the terminal.
In our pilot, an AI assistant passes a file path. A local bridge uploads the config to NetConverter over HTTPS—not through the AI model. Engineers review results and warnings.
Pilot access: netconverter.ai #MCP
🤖 Made with AI

Check out my latest article: French Supermarket Cyberattack and the Insurance Coverage Gap linkedin.com/pulse/french-su… via @LinkedIn

AI can identify vulnerabilities faster than enterprises can remediate them.
Bank of America's 1,000 additional contractors illustrate the scale of the challenge.
Network modernization needs a better approach: AI-assisted analysis, deterministic conversion, and engineer review.
netconverter.ai
#Cybersecurity
🤖 Made with AI

The FBI's disruption of North Korean remote IT worker operations highlights a growing challenge: trusted access can become a security risk.
Identity security matters. So does understanding and maintaining the network policies behind that access.
Visibility. Governance. Controlled change.
#Cybersecurity
A new firewall doesn't mean a cleaner policy.
Copy every rule forward and you may migrate years of exceptions and unknown intent.
NetConverter uses AI-assisted mapping, deterministic conversion, and engineer-reviewed exceptions.
Modernize more than the hardware.
netconverter.ai


🚨 FBI + Secret Service warn that FortiBleed continues targeting exposed Fortinet systems, with some victims locked out.
Securing networks is hard enough before layering on legacy configurations and technical debt.
Read the official advisory:
ic3.gov/CSA/2026/261006.pdf


Gartner's latest research points to a growing enterprise gap:
AI investment is accelerating faster than readiness, governance and proof.
Our view:
AI helps understand.
Deterministic systems convert.
Validation checks.
Exceptions get surfaced.
Engineers decide.
Because 99% right can still be wrong.
Don't just migrate it. Prove it.
NetConverter.ai
🤖 Made with AI
