

Every AI · Every API · Every Connection — Secured. Stop managing your attack surface. Eliminate it—with the only identity-first Zero Trust fabric for every mach
Charlotte, NC
Joined January 2017
- Tweets3.6K
- Following3.2K
- Followers1.5K
- Likes2.3K




A person and a machine are different Zero Trust problems. KuppingerCole explains why in their Buyer's Compass on Zero Trust Platforms (commissioned by NetFoundry). Quote in the image. info.netfoundry.io/lp-kc-zer…

22
Stop approving a new firewall exception for every AI agent.
Approve one pattern instead: outbound connectors, identity-bound sessions, per-MCP-tool policy, every request in your SIEM, and a per-vendor kill switch.
“One door you can see, govern, and close beats many doors you cannot.”
netfoundry.io/ai/the-securit…

19
Most AI security asks what an agent can do once it’s connected. The better first question: what should it be able to reach at all?
Zero Trust for Agentic AI with @NetFoundry + @Carahsoft
Dec 8, 11am ET
carahevents.carahsoft.com/Ev…
#ZeroTrust #AgenticAI

19
"In the KuppingerCole Leadership Compass on Zero Trust Platforms 2026, NetFoundry is rated as Product, Innovation, and Overall Leader." — KuppingerCole Analysts
Get the Buyer's Compass (commissioned by NetFoundry): info.netfoundry.io/lp-kc-zer…

16
"Zero Trust cannot be bought and switched on."
— @KuppingerCole Analysts
Their new Buyer's Compass (commissioned by NetFoundry) shows how to choose a platform for the traffic it actually carries: people, workloads and AI agents. info.netfoundry.io/lp-kc-zer…

34
Enterprise-Managed Authorization decides who can use an MCP server. It doesn't build the private path to reach one.
Our CEO Galeal Zino @gilzino on the two problems enterprise MCP has to solve, and why you don't have to wait for EMA.
#MCP #ZeroTrust
netfoundry.io/uncategorized/…

1
49
A service shouldn't be reachable before anyone's authorized to use it, or after that authority ends.
Our Philip Griffiths for @cloudsa on Identity-Defined Reachability: no path by default, and none once authority ends.
#ZeroTrust #AgenticAI
cloudsecurityalliance.org/bl…

16
Zero Trust connectivity won’t fix the vulnerable code. What it does is take away what attackers need. If a service has no open listening ports, an unauthenticated attacker has nowhere to send the payload.

1
1
170
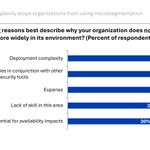
41% of orgs say deployment complexity keeps them from using microsegmentation more widely (Omdia).
The fix isn't more firewall rules. It's segmenting by identity, not IP.
Free Omdia report: info.netfoundry.io/lp-omdia-…

1
25
PHP2Shell runs before your application wakes up. The two critical PHP flaws (CVE-2026-109618 and CVE-2026-109619, CVSS 9.2) fire in PHP’s request parser. That parsing happens before your login, your middleware or any access rule you’ve written.
1
148
Omdia put NetFoundry's identity-based microsegmentation through a live demo across Google Cloud and AWS. No open ports. No firewall rewrites. No downtime.
Get the free Technical First Look: info.netfoundry.io/lp-omdia-…

32
AI agents reversed the SaaS model. Vendor agents now call into your ERP, databases and MCP servers, so you own the public front door and the job of defending it.
Part 1 of our Zero Trust for AI Agents series: netfoundry.io/ai/ai-agent-at… View article

4
5
334
88% of organizations run more than one cloud. Most of them also run more than one segmentation policy model, and that’s where the trouble starts.
1
2
78
Your host firewall can’t tell your AI agent apart from the legitimate service running next to it.
We built a different model.

6
5
694
Every AI agent pilot starts as "just a test." Then it gets wired into a real tool, a real database, a real API key, and nobody remembers to turn it off.
That's the pattern our CMO Mark Jaffe flagged in this week's Reachability Watch: protections that technically exist but only switch on if someone configures them. A fresh install doesn't know it's about to become production.
Our take: you shouldn't have to win the defaults lottery to stay safe. When identity decides who can reach a service at the network layer, an auth setting left off doesn't leave the door open to the whole internet.
Worth a quick audit this Friday: how many agent pilots are running in your cloud right now, and who can reach them?
#ZeroTrust #AISecurity #MCP #IdentityFirstReachability
lnkd.in/p/e9BS3U7a

1
1
31

99% of organizations are implementing or planning microsegmentation.
Only 9% have actually protected more than 80% of their critical systems.
That gap is the whole story. And it's not a tooling problem — it's a sequencing problem.
74
An AI agent doing damage under a shared credential is invisible in your logs. One of the most capable AI labs in the world spent over a week unable to answer "which agent did this" — because the agents involved didn't have identities of their own.
Our new guide breaks down why that changes everything: netfoundry.io/resources/the-…

1
30
🥇 OpenZiti just landed the #1 spot on @startidentity's Top 7 Open-Source Zero Trust Tools for 2026 — beating Pomerium, Teleport, Headscale, NetBird, Boundary & Authelia.
Called "the most complete open-source zero trust networking platform," Apache 2.0 top to bottom.
startwithidentity.com/articl…
#ZeroTrust #OpenSource

