

Welcome to Tenable. Your exposure ends here.
Columbia, MD
Joined April 2009
- Tweets11.3K
- Following238
- Followers88K
- Likes3.5K




.@Atos selected Tenable to power its Continuous Threat Exposure Management (CTEM) service, enabling global organizations to shift from reactive remediation to proactive cyber risk reduction.
Gabriela Gorzycka, VP, Head of Cybersecurity for Germany, Austria and Central Europe at Atos, discusses the power of #ExposureManagement and what organizations should prioritize first to help shrink the attack surface. Read the press release here: spr.ly/6012BHFucp
Tenable Hexa AI in action: Automate fixes
One prompt orchestrates remediation automatically, with a human in the loop.
Learn more: spr.ly/6011BHvTHh
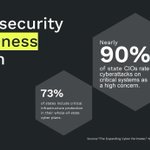
#AI is widening the attack surface of the critical infrastructure facilities and services that state, local, and education (SLED) organizations run. In the final post of our #CybersecurityAwarenessMonth series, we explain how a whole-of-state security approach can help SLED agencies protect their critical infrastructure. spr.ly/6016BHUgsy

#PHP2Shell drew instant Log4Shell comparisons, but a week of testing showed the key difference: a working exploit has to be tuned to each target's exact PHP build. The exception is devices that all run the same build, like network appliances.
Our post-mortem covers why both are true, and what it means for your patch prioritization queue: spr.ly/6017BHUjsP

Acceleration is the word of the day. Q3 2026 results from Tenable exceeded guided metrics again, and we once again raised our full-year 2026 outlook!
Full #earnings results here: spr.ly/6017BHlswx

As a mentor at Notre Dame Prep, Elizabeth shares her advice for the next generation of cyber talent: stay driven, stay open and enjoy the journey. Watch Elizabeth’s insights about career development. #OneTenable
.@Atos, a global leader in AI-powered digital transformation, selected Tenable One for unified, AI-driven visibility across IT, cloud, identity and OT environments to power its global CTEM operations. Learn more: spr.ly/6015BHcYOW
#ExposureManagement

#TenableResearch is diving into #Brotli2Shell. The team explores CVE-2026-111497, an out-of-bounds write vulnerability in the Google Brotli C decoder library. Classified as a "Vulnerability of Interest," an attacker can trigger the flaw by getting an application to decompress crafted Brotli data, with impact ranging from a process crash to potential remote code execution.
Read the blog to learn about patches, mitigations and PHP connections. spr.ly/6011BHckeL

Security teams, we know you're racing to stay ahead of the recently disclosed #PHP2Shell vulnerabilities. Finding affected assets quickly and applying updates is a top priority.
Our blog offers practical tips for how Tenable #ExposureManagement solutions can help - from discovering externally facing PHP assets to prioritizing remediation. spr.ly/6019BH9QKH

#ShadowAI used to be confined to a few simple scenarios, such as AI chatbots and AI browser extensions. Today, it spans a broad spectrum of complex vectors, making it harder to detect and control.
In the latest installment of our #CybersecurityAwarenessMonth blog series, learn how employee security training, AI usage governance, and #ExposureManagement can help you tackle shadow AI successfully. spr.ly/6010BH9KB6
#CISA and other global government organizations have issued urgent requests for organizations to patch two critical remote code execution (RCE) vulnerabilities in PHP. The vulnerabilities could allow attackers to remotely execute code on affected PHP servers.
#TenableResearch published an advisory blog outlining the vulnerabilities, affected versions, available detection capabilities and recommended actions. Visit the blog for updates as new information becomes available. spr.ly/6014BHkaIY

Tenable Hexa AI in action: Automate ticketing
One prompt finds exploitable CVEs with open attack paths, builds the tickets and routes them to owners once you approve.
Learn more: spr.ly/6011BHn2sf
Introducing Tenable OPEN for AI: validated, ready-to-run workflows that use your preferred AI systems to connect Tenable exposure data with security partners including @BeyondTrust, @SentinelOne, @snyksec and @splunk.
Pick a use case or prompt, run it in your AI tool of choice, and build from there. Learn more: spr.ly/6011BHT2ZJ
Win big at #SWARMGlobal, happening Nov 2-6. Prizes include:
💰 $10K in Claude credits (split among 1st, 2nd, 3rd place)
🎟️ A spot at EXPOSURE 2027
💻 Publication to the CyberAgents Exchange
🏆 SWARM Winner’s patch
Register here: spr.ly/6012BHRSb4
#Tenable #Anthropic #Cybersecurity @CyberAgentEx

Unpatched legacy OT systems are exposing critical infrastructure to a new wave of #AI-driven attacks.
In our new #CybersecurityAwarenessMonth blog, Tenable VP Jamie Brown breaks down CISA's latest guidance to protect organizations and the essential services they provide: spr.ly/6015BHMTjS
Mark your calendars: #SWARMGlobal is coming Nov 2-6. A virtual agentic AI build event, sponsored by Tenable with support from Anthropic. All skill levels are welcome. Cool prizes to win! Register: spr.ly/6010BH8l2E
@CyberAgentEx
“Citizen coders” are non-technical employees building workplace apps with #AI using natural language prompts. Here’s how to mitigate the risk from AI-generated apps they are building. spr.ly/6017BGfKFv
#CybersecurityAwarenessMonth
New feature alert! @CyberAgentEx, powered by Tenable, has added Exchange Inspector to help organizations more securely deploy open source AI agents, skills, and MCP servers in production environments.
To earn the Exchange Inspector vetted tag, select community-built AI agents, skills, and MCP servers must pass three rounds of enterprise-grade security review. Learn more: spr.ly/6015BG4cwR
Welcome to Tenable, Charlie Bell! The Microsoft and former AWS executive joins our Board of Directors, strengthening its technical depth as we help organizations reduce risk with AI-powered #ExposureManagement. spr.ly/6012BG0LUM

It's #CybersecurityAwarenessMonth! This year's theme is "Securing the Next 250." Follow along as we share ways to secure your business, critical infrastructure and government agencies by seeing your entire attack surface. #ExposureManagement
