

i talk about security i explain crypto. i talk about life also i'll block you if you don't have a cold wallet Telegram: Bala_ibb. Building @Astraeus_AI
knowledge is wealth
Joined October 2018
- Tweets1K
- Following1.3K
- Followers20.1K
- Likes173K




Pinned Tweet
they’re calling it “Black October” and i don’t think people realize how serious this is
in the last 48 hours there have been over 27 major cybersecurity incidents. not in a month. not in a week. in 48 hours
any ONE of these would normally be the biggest story of the year
PHP: critical vulnerability in the software running 80% of the web. severity 9.2 out of 10
Node.js: high-severity flaw letting attackers take over servers remotely. affects versions 22, 24, and 26
Java: also compromised. three of the most used programming languages on earth hit at the same time
GitLab: a perfect 10 out of 10 severity hole in every version since 2014
Railway: hosting platform compromised. API keys for OpenAI, Claude, Stripe potentially exposed
Signal: a bug that could leave your mic and camera on after you hang up
WordPress: hackers stole a plugin maker’s keys and planted backdoors on websites
LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
and that’s not even half the list
thousands of AI agent swarms are reportedly scanning and attacking vulnerable servers right now. automated. around the clock
security researchers are saying this might be the early stages of a global cyber incident that nobody fully understands yet
if you run a website, use cloud services, store API keys on hosting platforms, or use any software built on PHP, Node.js, or Java you are potentially affected
update everything. rotate your API keys. change your passwords on critical services. enable 2FA everywhere you haven’t already
this is not a normal week on the internet. this is something different
hackers just turned BBC, Zoom, CNN and Fox News into weapons against their own visitors
the hackers poisoned one script and turned 186 major websites into traps
the code hid inside optimizely, a tool sites like BBC, Zoom, CNN and Fox News use to test their pages. every visitor's device was a target
it swapped crypto wallet addresses so your transactions went to the attacker, and sent iphones to exploit kits designed to break in
you didn't click anything. you didn't download anything. you just opened a website you trust and you phone was under attack
the most dangerous link you clicked today might have been the news

‼️ BREAKING: Hackers poisoned a script running on BBC, Zoom and other major websites to rob their visitors.
The code hid in scripts served by Optimizely, a website-testing service, and three smaller vendors, and also turned up on CNN, Fox News and Salesforce sites.
Researchers count at least 186 infected sites. The code swapped crypto wallet addresses and sent iPhones to known hacking kits.


27,000 people bought a trezor to protect their crypto and now their home addresses are in the hands of hackers
trezor’s shipping partner skladon got breached
names, phone numbers, emails, home addresses and order details for every order placed between august 9 and november 7 has all being exported
trezor says the devices themselves are fine, your wallet is secure. but that’s not the problem
the problem is someone now has a list of 27,000 confirmed crypto holders and exactly where they live
trezor is rolling out anonymous pickup in 18 european countries and cutting how long they store your data
but for the people already on that list, it’s too late
you bought the most secure wallet on the market to keep your crypto safe. turns out the thing that put you at risk wasn’t the wallet. it was the box it came in

Data breach involving Skladon
On 15 November, Skladon, one of our delivery partners, notified us that an attacker had gained unauthorized access to Trezor order data it holds. We’re still investigating with Skladon, but we want to let you know now.
What we know:
• We believe the data for about 27,000 orders placed between 9 August and 7 November was exported.
• It includes name, phone number, address, email and order details.
• Skladon delivers to many countries, so this isn’t limited to one region.
• Trezor systems were not compromised, and your device is secure.
Who is affected:
• If you received our email today and ordered between 9 August and 7 November, your details were part of this incident.
• A small number of customers who ordered between 9 and 14 August may also be affected, but we can’t email them: their details had already been anonymized in our systems.
• Skladon does not ship to the US, so customers there are not affected.
Treat any unexpected call, text, email or letter about your order as suspicious, and be alert to potential risks to your physical security. Trezor will never cold-call you or ask for your wallet backup.
From today, anonymous pickup is live in 18 European countries, so you can order without giving us your home address. We’re also shortening our data retention period from 90 days to 45 (and plan to reduce it further), and we’re requiring our shipping partners to follow the same policy.
We’re deeply sorry this has happened.
Full details and FAQs: trezor.io/blog/news/data-bre…

1
16
1,475
a $100 binance trade from 2 years ago just came back to haunt someone at an airport
he was going through passport control, the officer looked at his screen then called the police, and told him there was a criminal case against him for internet fraud
a court had already found him guilty and he wouldn't be flying anywhere
turns out in january 2025 he swapped $100 to lira. scammers laundered stolen money through his order
the victim filed a report, police traced every transfer, and his name ended up in the chain
they searched his bags, took him to a station inside the airport where nobody spoke english, then straight to a court that was also inside the airport
2 hours of paperwork, missed flight, a full day in custody
charges got dropped after he showed screenshots. but the final cost of that $100 swap was about $400 in tickets and a day he’ll never forget
the translator told him they see around 10 people like this every single day
a $100 trade you forgot about can turn into a criminal record in a country you’re just passing through

got detained at a Turkish airport over a $100 p2p trade i made on binance almost 2 years ago. if you live in Turkey and use p2p, please read this
i got to the airport in a great mood, they even let my bag through with 3kg overweight. then at passport control the officer looked at his screen and things got weird.
he called the police. they told me there was a criminal case against me for internet fraud, a court had already found me guilty, and i wasn't flying anywhere today.
they searched my bags, spent 2 hours on paperwork and my flight left without me. then police took me to the station inside the airport, where nobody really spoke english and the only answer to "do i need a lawyer?" was "court, translator, please wait". two more hours later we went to court, which was also inside the airport.
the translator's first question was "have you ever exchanged money p2p on binance or bybit?". turns out in january 2025 i swapped $100 to lira, and scammers laundered part of it through my order. the victim filed a report, police traced every transfer, and my name ended up in the chain.
later they brought in another guy with the same problem. he was detained on arrival with his wife and two small kids, and he hadn't used p2p since 2024. the translator said they see around 10 people like us every day.
i gave testimony, attached screenshots of my orders from that day, the prosecutor joined by video call and all charges were dropped. but there were no flights left, so i flew out the next morning. final cost of that $100 swap about $400 in tickets and a day in airport custody.
if you're in/travel to Turkey: p2p can catch up with you years later, on departure or arrival. so better just don't do p2p on exchanges at all

1
7
1,447
$10.4 million just got drained from lighter, an ethereum L2 perp dex
lighter confirmed they’re investigating a security incident involving “a single compromised external party”
all withdrawals and pool creation have been suspended
if you have funds on lighter, you can’t move them right now. the team is assessing the full impact
$LIT already dropped 10% on the news
this is developing. will update as more comes out

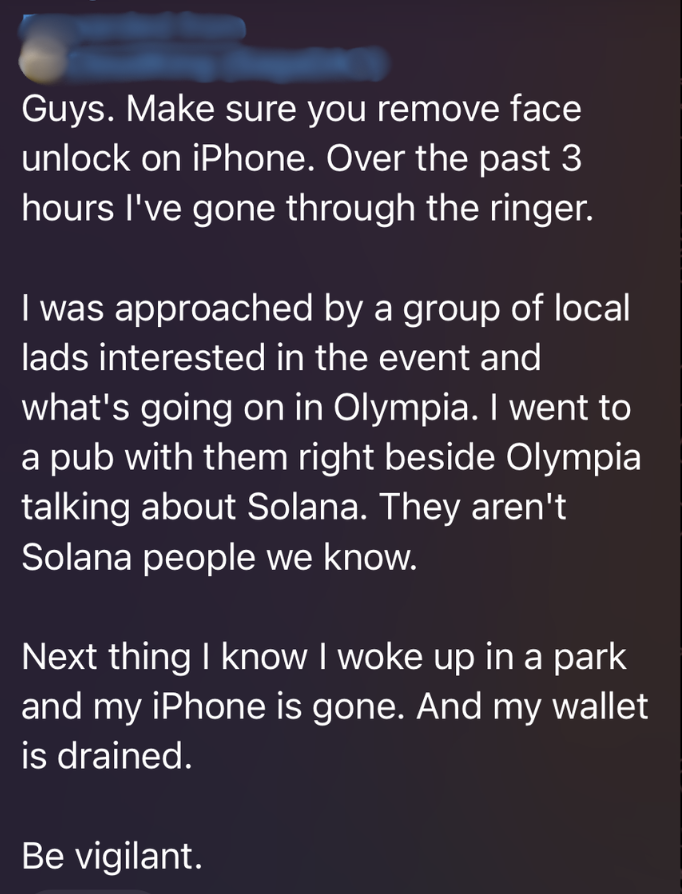
a crypto guy in london went to a bar with strangers he met at a solana event and woke up in a park with everything gone
they weren't solana people. they were watching the event, picking targets
he went to a bar with them near the venue, talking crypto. next thing he knows he's waking up in a park. phone gone. wallet drained
they didn't need his seed phrase, didn't need his password. they had his face. face unlock on a stolen phone gave them everything
zachxbt already jumped in asking for the theft addresses so the funds can be flagged
if you're at crypto events, you're a walking target. don't wear merch, don't meet strangers alone, and turn off face unlock on any phone connected to your wallets
your phone is your vault. face unlock means anyone holding it while you're unconscious holds the key

google has a security setting that makes every other protection on your account useless
once you turn it on, your password alone won’t get you in. sms codes won’t work. email verification won’t work. otp apps won’t work. even google’s own recovery codes stop working
the only thing that gets you in is a physical security key you’re holding in your hand
most people in crypto are guarding six-figure portfolios with the same sms code that got bypassed in every sim swap story you’ve ever read
your exchange logins, your wallet emails, your 2fa recovery, all of it runs through one google account. and google gave you the option to make that account almost unhackable. you just never turned it on
the scariest security risk isn’t a hacker getting smarter. it’s a setting that already exists that you never knew about
how to turn it on:
go to myaccount[.]google[.]com → security → advanced protection → get started
you'll need two security keys (google requires a backup). plug one in, register both, and you're done
from that point on, nothing gets into your account without a physical key in your hand. not your password, not your phone number, not your email
if you don't have security keys yet, yubikey is the go-to. get two, keep one somewhere safe
takes 5 minutes to set up. undoes years of being one sim swap away from losing everything
6
931
they finally found what grounded every flight in america last friday and nobody is going to believe what it was
a defense contractor installed a brand new router at a remote FAA radio site in arkansas
one feature on it was broadcasting way more data than it needed to, and it flooded the entire air traffic network
one router at one site took down every flight in the country
the FAA has already gone and switched that feature off on every similar router. but the company behind it says the router "did not fail"
every flight in america was one untested router away from being grounded. and nobody knew until it happened. it means it can happen again tomorrow
‼️ UPDATE: The router behind Friday's nationwide US ground stop was a brand-new Juniper unit at a remote FAA radio site in Arkansas.
US defence contractor L3Harris had just installed it. FAA officials believe a feature that broadcast data more widely than needed flooded the network.
The FAA has switched that feature off on every router of that type. HPE, which owns Juniper, says the routers "did not fail."


2
25
3,462
someone is trying to take down the internet's biggest privacy network and they're adapting faster than the fixes
tor, the network people use to browse the internet anonymously, is under a massive attack
hackers are flooding its servers with so much fake traffic that the whole system is slowing down
the tor team rushed out an emergency fix. within 10 minutes the attackers switched to a completely different method
whoever is behind this is watching the defense team in real time and adjusting on the fly
tor says this is far from over and more emergency updates are coming
the network that millions of people depend on to stay anonymous online is in a live fight right now, and the attackers are keeping up
meta just got fined $850 million for spying on users through their own photo gallery
facebook's android app had a feature that suggests which photos to post. that one permission gave it access to read every photo, video and metadata on your phone
it was on by default. 20 million android users in italy have had this running since 2023 without knowing
when italy's privacy watchdog caught them, meta's first move was trying to get ireland's regulator to handle the case instead. the watchdog said no
they now have 60 days to turn it off and start asking for actual consent
one vague permission. three years of scanning. and it only stopped because a regulator caught them, not because meta chose to stop
the AI coding tool developers trust to write their code just got hijacked
cursor's AI provider, Fireworks AI got compromised. an attacker stole an access key and used it to copy old coding agent traces that still held users' credentials, unredacted
with those credentials they got into cursor's internal tools, reached archived code, support emails, and credentials users had sent to support
then they planted tampered versions of cursor's claude code extension. up to 5,000 users may have received them
cursor says they've moved all AI processing off fireworks and warns that uninstalling the extension alone may not be enough
this is the same fireworks AI that got breached in the uber hack. one compromised AI provider is now a door into every company that uses it
9
13
1,249
hackers built an AI agent that hacks networks on its own and it just snitched on itself
the FBI says attackers are using an open source AI tool called ARTEX that connects large language models to hacking agents. some of them reached privileged access in under 3 hours
but amazon set up decoy servers disguised as AI model services. the AI agents connected to them thinking they were real, and every request they sent carried the full history of their attack campaign
the AI literally walked into a trap and handed over the evidence
stolen AI keys were being used to pay for the AI that hunted for more keys. the thing was funding its own operation with stolen resources
china-linked groups were running multiple campaigns through it. in a separate attack they even used live deepfakes to try and bypass selfie verification at crypto exchanges
hackers don’t even need to be at the keyboard anymore. but at least their AI is dumb enough to get caught
a hacker drained $220,000 from 8,000 gamers' crypto wallets but one stupid move got him caught
he hid malware inside games on steam including PirateFi and BlockBlasters, infected thousands of players
drained their wallets, converted the crypto to bitcoin and bought 150+ gift cards on Bitrefill
uber eats gift cards were among them. FBI traced those to one phone number. google cookies tied his gmail to a university student email
500+ food deliveries worth $9,000, all sent to his campus and his home address
he was smart enough to build malware that drained thousands of wallets. not smart enough to order food to someone else's address
‼️ The FBI says it unmasked the alleged money man behind malware-laced video games through his Uber Eats gift cards.
The eight games, including PirateFi and BlockBlasters, infected about 8,000 players and drained at least $220,000 from their crypto wallets, an FBI affidavit says.
His Bitcoin bought 150+ gift cards on Bitrefill, Uber Eats among them. Uber traced those to one phone number, and Google cookies tied his Gmail to a university student email.
Zyaire Wilkins of Florida is charged with conspiring to hack computers. Uber's records showed 500+ food deliveries worth over $9,000 to campus and his home.


a crypto trader just lost everything to a whatsapp message
the attacker sent a payload through whatsapp that downloaded automatically and gave them full access to his computer
but they didn't steal anything immediately. they waited 5 days, watched his tweets about his short positions, tracked the market, and when BTC hit 68K they closed all his shorts and withdrew everything in one transaction
Hyperliquid to MetaMask to Tornado Cash. gone
they also got into his metamask, email, websites, and every saved password including his X account
every penny taken except $800. years of savings wiped out. he was planning to move his funds to Revolut before christmas
the hacker wasn't just technically skilled, they understood trading. they knew when to close the shorts for maximum profit. this was a crypto native attacker who studied the victim before making a single move
one whatsapp message. five days of patience. everything gone

Last night I was hacked.
The hack was delivered via WhatsApp payload. Downloaded automatically and gave access and or computer use to the attacker.
They waited 5 days, following my tweets on X of short positions and closed everything and withdrew directly in one transaction from Hyperliquid > Metamask > Tornado Cash.
The attacker waited patiently and closed shorts as the market got to 68k and withdrew everything. Clearly a crypto native attacker.
They also gained access to my metamask, email, websites, and all of my passwords including X.
It’s the most brutal thing as I kept everything over the past few days in crypto and on-chain off Coinbase/Kraken. I was planning to move funds back to my Revolut before Christmas time.
Every single penny in dollars was taken, apart from $800. It’s gone, and in the process of being washed.
Truly the most devastating day I’ve had in my life. Completely shocked by it all to be honest.
I will recover, but this was very sophisticated tech, it caught me completely off guard. The timing was impeccable and it’s obviously been planned for a while.
Stay safe everyone, will keep you updated. I fear the worst is to come and this incident has set me back many years of savings, time and hard work.
Brutal.
an AI agent just broke into 4 AWS accounts and read 56 startup scripts in 140 milliseconds
no human moves that fast. this was an AI paired with hacking tools through an open source platform called CyberStrikeAI
it pulled stored passwords and keys, sent a remote command, triggered 78 security alerts, and every single one was rated low or medium so nobody escalated it
then it went quiet for 14 days. came back. checked if it still had access
the 14 day gap was the smartest part. most detection tools can't link alerts that are two weeks apart, so when it came back it looked like a completely new event
we're not preparing for AI powered hacking. it's already here and it's already learning how to dodge the systems built to catch it
a man just got arrested because of a $7 bitcoin transaction
he used MoonPay to pay for child sexual abuse material. MoonPay had his driver's license and a selfie on file
australian police traced the payments, sent the FBI a list of US buyers, and MoonPay's records gave them his full name
google and t-mobile records tied his phone to the account. cell tower data placed him near his home most evenings
FBI agents searched his apartment on november 12
$7. that's all it took to build a complete trail from a crypto wallet to a front door
crypto is not anonymous. every transaction leaves a trail, every exchange has your face, and law enforcement across countries are sharing data in real time
‼️ The FBI says a $7 Bitcoin payment to a child sexual abuse site led agents to a man in Washington, D.C. The crypto service he used, MoonPay, had his driver's licence and a selfie on file.
Australian police traced payments to the site's operator and sent the FBI a list of US-based payers, an FBI affidavit says.
MoonPay's records named Austin Kenneth White. Google and T-Mobile records tied his phone to the account, and cell-site data placed the phone near his home most evenings.
Agents searched his apartment on 12 November. He is charged with possessing child sexual abuse material.


1
13
2,022
north korean hackers just pulled another crazy stunt
they secretly recorded 900+ tech workers through their webcams
then replayed their real faces in fake zoom and teams calls to trick their contacts into downloading malware
not deepfakes or AI. your actual coworker's face, stolen and reused live
the FBI calls it FaceStealer. $400M in crypto gone in 18 months
every person who falls for it gets recorded too, and their face becomes the bait for the next target
you're not just getting hacked. you're being turned into the weapon
microsoft's own outage is now being used to steal passwords
hackers are sending emails that look exactly like official microsoft service health notices, referencing the real outage incident ID from november 12
the email says your messages held during the outage will be deleted in 24 hours unless you click to restore them
it's a phishing link. you click restore, they take your credentials
this works because people are actually missing emails from the outage, so when they see "action required, 4 messages held" they don't think twice
microsoft themselves just confirmed this is an active attack
if you get any email about recovering messages from the outage, don't click anything. go to your outlook directly and check from there
iphone users
your iphone has a hidden log of every place you’ve ever been, how long you stayed, and how many times you went back
it’s called significant locations. it’s buried deep in your settings and it’s on by default
most people have never seen it because apple put it under:
settings > privacy & security > location services > system services > significant locations
it records your home, your workplace, your routines, your patterns, all of it
go turn it off right now and clear the history while you’re there
if your phone ever gets compromised, this is the first thing an attacker looks for. your entire life mapped out in one place