Pinned Tweet
You get more confidence. More control. To put AI agents in charge.
See how. Live. Nov. 17.
Register for the reveal: bit.ly/4BSCE5F
Attackers are searching for a PHP2Shell exploit that actually works.
In an underground forum, participants requested exploits and questioned the code being shared. One assessment: "Didn't test but seems legit."

ALT Cover of a report by Cato Networks titled "Attackers Are Searching for a PHP2Shell Exploit That Actually Works." Includes three illustrated icons: a computer monitor with text, a document with code, and a stack of storage devices.

ALT A graphic from Cato Networks titled "CTRL Threat Intel" shows translated excerpts from an underground forum discussion. The text reads: "Does anyone have it?" and "Didn't test but seems legit." A summary states that participants asked for an exploit and questioned the effectiveness of the circulating code. Icons of two computer monitors and documents are at the bottom.
2
178
For defenders, those doubts raise questions about prerequisites, reliability and the evidence behind an exploit claim. Public analysis discussed in the report examined how PHP version, server settings and target knowledge could affect some circulating PoCs.
🤖 Made with AI
1
84
@CatoCTRL’s Guy Waizel and Etay Maor examine what was being requested, what was circulating and what remained unverified.
Read the full research: catonetworks.com/blog/cato-c…
52
AI is helping ransomware operators run more attacks at once and keep extortion conversations going around the clock.
2
136
In his latest @Forbes article, Cato’s Etay Maor examines how AI is changing the speed and scale of ransomware operations, separating documented uses from sellers’ unproven claims.
1
42
What looks like a tax document could give an attacker remote access to your computer.
Cato CTRL investigated a phishing campaign targeting Israeli organizations with emails impersonating the Israel Tax Authority.
1
194
The lesson extends beyond this Israeli campaign: legitimate remote-support software can be misused when employees are tricked into running and installing it.
Cato’s intrusion prevention system blocked a web request to infrastructure used by this campaign.
1
52
Cato also automatically blocks confirmed campaign indicators, without requiring customers to add those indicators manually.
Read the Cato CTRL research for the delivery chain, warning signs, and Cato’s protection: bit.ly/4efYsOx
55
Your AI apps may be working, but are they working well?
As employees and developers rely more on AI tools, IT teams face a new challenge: understanding the quality of their AI interactions before performance issues start affecting their productivity.
1
156
Cato DEM helps IT teams see the difference by measuring AI interaction latency and errors, with the context to investigate where performance issues are occurring.
1
45
Learn how Cato DEM gives IT teams a clearer picture of the real AI experience before users start reporting problems
Read our latest blog: bit.ly/4syHZKY
41
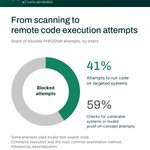
The same day PHP2Shell fixes arrived, Cato observed attackers checking for systems they could exploit and early proof-of-concept attempts against systems running PHP.
2
178
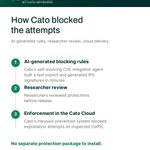
Customers did not need to install a separate protection package. Cato delivered and enforced the signatures through its cloud, helping reduce exposure while application owners upgraded PHP.
1
56
Read the Cato CTRL research for how the activity unfolded, what attackers tried, and how Cato blocked the attempts: bit.ly/4A4vv0k
50