

Director of Research @BeyondTrust @btphantomlabs. Former @SpecterOps; @Microsoft. "Old man yells at cloud" vibes
Charlotte, NC
Joined November 2015
- Tweets1.3K
- Following359
- Followers6.7K
- Likes2.8K





Ryan retweeted

New research from @datadoghq Security Labs! We spent some time poking at Jev to see how we could steer its evaluations.
We found a method that dropped its prompt-injection detection rate from ~83% to ~4% in our tests. We also used the technique to bypass LangChain’s experimental Jev-based tool-risk gating feature. Read more below:
securitylabs.datadoghq.com/a…

One of the best attributes someone new to this industry can have is to not be afraid to ask questions. It doesn't hurt to try things yourself, but struggling silently doesn't help anyone, especially yourself. The best researchers I know aren't afraid to ask for help.
Ryan retweeted

Today I'm dropping how myself and @Haus3c got admin credentials to every Dataverse/Copilot Studio sandbox in the world!
beyondtrust.com/blog/entry/c…
Come see the talk at 3:30pm mainstage Track 4 tomorrow.

It has been a few years since I've done a talk, but excited to share I'll be speaking at @defcon this year on how we bypassed an AI code interpreter in Azure and discovered tons of interesting things in a sandbox. hackertracker.app/defcon34/c…
Ryan retweeted

🚨Slight change of plans for this Thursday!🚨
We’re excited to welcome @Haus3c, Director of Research at @btphantomlabs, on June 11 at 11:30 AM EST.
From offensive security to identity research, AzureHound, and the Azure Threat Research Matrix, Ryan has covered a lot of ground. Tune in for a great conversation on his work and current research.

🚨Podcast Announcement!🚨
@olafhartong is joining us next Thursday (June 11th) at 2:30pm EST on the #ThePayloadPodcast! We will be diving into:
- Identity Attacks
- How AI has changed Detection Engineering/Threat Hunting
- Maybe we can get Olaf to show off or talk about FalconHound👀
Come hang out and ask questions!

Ryan retweeted

New research! Security Researcher, Sergio Garcia (@MrCloudSec) uncovers a major risk in AWS Bedrock API keys: the “phantom user” problem.
Check it out: beyondtrust.com/blog/entry/a…
#AWSBedrock

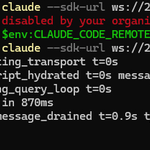
I genuinely don't think people are talking about this enough. --sdk-url is a non-documented Claude Code argument that circumvents your corporate Claude 'remote control' policy and allows outbound connections to any server. Claude can quite literally be considered a C2 framework.

Claude Code's remote control protocol lets developers orchestrate instances programmatically. @tyholms reverse engineered it and found an undocumented flag that redirects any instance to attacker-controlled infrastructure, silently bypassing all permission checks.
originhq.com/blog/reversing-…

After doing just cloud stuff for so long, I figured I should hop on the AI train, so this is my first dive into AI security research beyondtrust.com/blog/entry/c…

I'm looking for a senior/staff level researcher to join my team @btphantomlabs. I'm looking for someone who:
- Has research experience in the Cloud, identity, and/or AI space
- Understands attack path management + graph theory
- Active directory knowledge is a plus
- History of making blog posts/webinars/conference talks/etc. is also a huge plus
This is a full time research role on a dedicated research team. Fully remote, competitive salary.
Apply here:
beyondtrust.com/company/care…
Ryan retweeted
Breaking: Newly uncovered OpenAI Codex vuln enables command injection via GitHub branch names in task creation requests.
Attackers could steal GitHub user access tokens & sensitive data.
Full breakdown by Tyler Jespersen: lnkd.in/ewdTaiEa
#OpenAI #BTPhantomLabs
🤖 Made with AI

Ryan retweeted

Introducing Praxis, an adversarial framework for discovering, controlling, and orchestrating computer-use agents running on endpoints.
Announcement → originhq.com/blog/praxis-ann…
Get Praxis → praxis.originhq.com

🦀🦀In the beginning was the Prompt, and the Prompt was with the Void, and the Prompt was Light. 🦀🦀 jpcaparas.medium.com/ai-agen…
Easily the funniest thing I've read so far this year

Dusting off the ol' blog with some notes on Azure Storage Accounts attacks and detections. hausec.com/2025/12/15/azure-…

Fun fact: If you're forwarding events from Azure to Log Analytics, the TenantId field isn't your EntraID tenant. It's the Log Analytics workspace ID. Because that makes sense.

I merged a PR from @ScoubiMtl that now includes compatibility with BHCE. Thanks @ScoubiMtl ! github.com/hausec/Bloodhound…

Ryan retweeted

I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: dirkjanm.io/obtaining-global…