

Homo Aptus. Vincit qui se vincit - Publilius Syrus. Consulting, Training, Technology, Cyber domain, and more... @x33fcon founder.
POLAND, EU
Joined April 2019
- Tweets1.4K
- Following349
- Followers17.2K
- Likes1.6K




Pinned Tweet
Big announcement!
We're launching a new platform with new content, refreshed videos, opsec considerations and detection opportunities.
New website: sektor7.institute
Current users will be migrated from an old platform in the coming weeks.
Enjoy!
#maldev #malwaredevelopment #redteam #blueteam


Mapping every Windows syscall.
NTSleuth automatially extracts syscalls from ntdll.dll and win32u.dll across ARM64, x64 and x86, resolves parameters via the PHNT database, and exports JSON or C headers.
A tool by Alex Hagenah (@xaitax)
Source: github.com/xaitax/NTSleuth
#redteam #blueteam

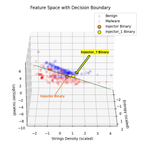
Evading an ML malware classifier.
Training a toy logistic-regression detector on three static features: entropy, strings density and file size, to nudge a shellcode injector across its decision boundary.
Dynamically resolving WinAPI calls and stripping the CRT raises string density just enough to score "benign" while the loader's functionality stays identical.
A post by @0xTriboulet
Source: steve-s.gitbook.io/0xtriboul…
#redteam #blueteam #infosec #machinelearning


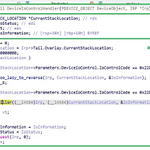
Reversed and Weaponized Microsoft-Signed Driver Used to Kill CrowdStrike EDR.
15+ variants of a kernel driver (PoisonX) used in BYOVD attacks against EDRs - all carrying valid Microsoft signatures, none blocked, revoked, or detected by any AV vendor.
Reverse engineering revealed a single IOCTL (0x22E010) that takes a PID as an ASCII string and calls ZwOpenProcess() + ZwTerminateProcess() against PPL-protected processes.
A post by Jehad Abudagga
Source: medium.com/@jehadbudagga/rev…
#redteam #blueteam #byovd #edr #windowssecurity

Bypassing a top EDR in a crystal clear way.
Building a Crystal Palace reflective loader that hides a Cobalt Strike beacon from EDR by overloading a sacrificial DLL and transferring execution with NtContinue() and synthetic stack frames.
Loader API calls are spoofed with Draugr, sleep is masked by encrypting sections at rest, and Crystal Palace YARA signatures get stripped.
A post and tool by Lorenzo Meacci.
Source: lorenzomeacci.com/bypassing-…
#redteam #blueteam

Making call stacks lie to EDRs.
LACUNA Chain spoofs Windows call stacks using ".pdata" gaps - ghost code in signed DLLs that unwinds cleanly, leaves no artifacts, and fully evades Elastic, Bitdefender, and Kaspersky.
A post by Mohamed Alzhrani (@0xMaz)
Source: 0xmaz.me/posts/LACUNA-Chain-…
#redteam #blueteam

No C2 allowed? Beacon over Microsoft Teams.
Reverse engineering Teams' meeting APIs and WebRTC data channels to run a C2 over Microsoft traffic that the infrastructure already allows.
A post by Clément Labro (@itm4n)
Source: blog.scrt.ch/2026/04/21/from…
#redteam #blueteam


Make your payload "sleep" to look like any real Windows activity.
BusyWork is a Rust library that swaps each pause for randomized real work - hashing, file enumeration, registry queries, DNS lookups - drawn from 76 tasks across seven categories with ±30% jitter on every parameter.
No two "pauses" produce the same API sequence, and no timing primitives survive in the compiled binary.
A post by Daniel (@PatchRequest)
Source: patchi.fyi/blog/busywork-sle…
#redteam #blueteam

Backdooring LLMs with triggered tool execution.
Untrusted model weights + privileged tools = trouble.
@pdiscoveryio reshaped Qwen2.5-7B via QLoRA to hide a secret trigger causing Codex to execute a command exfiltrating secrets.
A post by Prince Chaddha.
Source: projectdiscovery.io/research…
#redteam #blueteam

EDR evasion with LLM behind a steering wheel.
Run an LLM in a "while" loop against Cortex XDR with Binary Ninja attached, and it extracts decrypted YARA rules, thousands of behavioral detections, and even the product's local ML models.
A post by Adam Chester (@_xpn_)
Source: specterops.io/blog/2026-06-2…
#redteam #blueteam

Swarmer - persistence that never touches the registry.
It turns a .reg export into an NTUSER.MAN hive that Windows loads over a user's own hive, abusing legacy Mandatory User Profile behavior.
No registry APIs are called, so EDR sees no writes, and it works without admin rights.
A post and tool by @praetorianlabs
Source: github.com/praetorian-inc/sw…
#redteam #blueteam
A searchable catalog of detection artifacts.
Detection Wiki merges ETW manifests, MOF definitions, real .evtx captures, and community docs into a single static reference covering Windows events across over a 1000 providers.
Source: detection.wiki/blog/introduc…
#blueteam #redteam #windows

Launching payloads via a service recovery.
RecoverIt crashes a broken Windows service so its recovery action launches a given payload. No Event ID 7045 fired.
A tool by @TwoSevenOneT
Tool: github.com/TwoSevenOneT/Reco…
Post: hackers-arise.com/defense-ev…
#redteam #blueteam

Entropia - a compiled language for Windows shellcode.
It collapses the usual chain of compiler, linker and position-independence transform into one compiler that emits PIC x86-64 shellcode or Cobalt Strike BOFs directly.
OPSEC tricks like polymorphism, direct syscalls and ETW/AMSI patching ship as plain compiler flags.
A tool by @EntropyKit
Source: github.com/entropykit/entrop…
#redteam #blueteam

Windows Projected File System internals - a deep dive by @JonnyJohnson_
Source: huntress.com/blog/windows-pr…
#redteam #blueteam

Proxying Red Team comms via WebSockets and SSH - a case of Chisel.
A post by Benedikt Strobl
Source: nsideattacklogic.de/socks-pr…
#redteam #blueteam

EDR traffic and the roadblocks...
Windows Firewall COM API to "shape" the traffic originating from the machine.
A tool by Jony Schats (@_0xJs_).
Source: github.com/0xJs/BlockEDRTraf…
#redteam #blueteam

Using Ghidra in malware analysis.
Manual identification, decryption and fixing of encrypted strings of Vidar Malware sample.
A post by Matthew (@embee_research).
Source: embeeresearch.io/ghidra-basi…
#redteam #blueteam

Analysis of Meduza stealer's techniques and attack vector.
A post by Teoderick Contreras.
Source: splunk.com/en_us/blog/securi…
#redteam #blueteam
