

Offensive security company. Dojo of many ninjas. Red teaming, reverse engineering, vuln research, dev of security tools and incident response.
France
Joined April 2012
- Tweets1.9K
- Following274
- Followers21.8K
- Likes1K




At the CERT-EU conference, @k3vinTell and @hugow_vincent presented #CodeQLLM: combining CodeQL's precision with locally run LLMs to help security auditors identify vulnerabilities through white-box analysis.
📑 Explore the slides: synacktiv.com/sites/default/…

Synacktiv retweeted

You don't always need direct access to a system to compromise it. Sometimes, the permissions you already hold are enough. 👀
Wilfried Bécard and @hugow_vincent from @Synacktiv explored this reality in this webinar.
▶️ Watch the full webinar: youtube.com/watch?v=-w0p51n4…
🤖 Made with AI
A recent audit of the #GLPI application conducted by Tedi revealed a mass assignment vulnerability that could lead to MFA bypass and account takeover.
Refer to the security advisory ⬇️
synacktiv.com/en/advisories/…

Two of our experts on stage at #hacklu last week:
@us3r777 - Improving wordlists with tooling & methodology
@_remsio_ - Deep dive into Livewire: from weak typing to pre-auth RCE
🎯 Locked outside your target? Have a look at:
▪️ github.com/synacktiv/dicozor…
▪️ github.com/synacktiv/Livepyr…

CI/CD pipelines are prime targets for attackers. Is your organisation prepared?
Join @matthieubjl & @hugow_vincent at #InsomniHack for 2 days of hands-on training on GitHub Actions, GitLab CI/CD, runner hijacking and secret extraction.
Explore the training & register ⬇️
insomnihack.ch/session/88c02…

Come by our booth, take on our challenge and win some awesome prizes🎁
The grand finale takes place tonight 🏆
Don’t miss out!
#Hexacon26

🚀 Synacktiv is at @hexacon_fr!
We’re catching up with the offensive security community, sharing expertise and exchanging ideas. 🤝
📍 Here too? Come say hello!
🔗 hexacon.fr/


J-1 before @hexacon_fr!
We’ll be at the Palais Brongniart tomorrow.
Looking forward to seeing you there 🚀

During a security assessment, our ninja @ImNotFl0 found vulnerabilities allowing to execute commands as root in the Danfoss SM800a, SM800 and SC255 controllers, mainly used to monitor and configure industrial fridges. Patch now! synacktiv.com/sites/default/…
synacktiv.com/sites/default/…

🔎 Authentication bypass - Danfoss SM800 & SC255/SC355 : synacktiv.com/sites/default/…
🔎 Multiple vulnerabilities - Danfoss SM800A : synacktiv.com/sites/default/…
🥊 #Rikugan vs #Frontkick: who wins the agentic AI showdown?
Rikugan is open-source and making waves on IDA. Frontkick is built for Binary Ninja.
ToolAgent or CodeAct? Aiglematth breaks down the contenders.
Read the article ⬇️
synacktiv.com/en/publication…

In 2023, @Synacktiv researchers identified an authentication bypass in #Danfoss SM800 and SC255/SC355 controllers. The same vulnerability, reported again in 2025, could be linked to the recent supermarket refrigeration attack.
🔎 Authentication Bypass - Danfoss SM800 & SC255/SC355: synacktiv.com/sites/default/…
🔎 Multiple Vulnerabilities - Danfoss SM800A: synacktiv.com/sites/default/…
How can an HTTP Range request help exfiltrate files and secrets from VMs?
At T-REX 2026, @TG91aXMK presented Fusetea, a tool we use during TLPT engagements to speed up Red Team ops.
🔎 Discover Fusetea: github.com/synacktiv/fusetea…
📑 Check out the slides: synacktiv.com/sites/default/…
@oenb

Synacktiv retweeted

🚀 Ready to compete old-school style (No 🤖)? Join our speedrun CTF at the @Synacktiv booth Day 1!
🔥 Qualifiers: 15-min try, 1 challenge. Top 8 fastest advance!
🏆 Finals: Friday 16th @ 9 PM (Social Event). 1v1 BO3 bracket
💻Pwn, Web, Crypto, Reverse
🔐 What if your Group Policy Objects were an attacker’s best friend?
As part of @nullcon Berlin, join @wil_fri3d & @hugow_vincent for a webinar on GPO exploitation in Active Directory.
📅 Oct 12 | 11:30 AM-12:30 PM
Register ⬇️
events.teams.microsoft.com/e…

Synacktiv retweeted
Crossword cracked? Now take on enterprise AD. 👀
Join Wilfried Bécard and Hugo Vincent of @Synacktiv for Active Directory Intrusion Tactics: Advanced Level at #NullconBerlin2026.
Register now: nullcon.net/training/active-…
#NullconBerlin2026

Our CEO Renaud Feil shared his insights on how AI is shaping cybersecurity at @BSidesCbr 🇦🇺
While we wait for the official video, check out and download the slides here: synacktiv.com/sites/default/…
Thanks to the organizers and everyone who attended!
During a Red Team assessment, @l4x4 discovered multiple vulnerabilities on Ubika WAAP Gateway, including a pre-auth RCE as root.
Technical details are available here ⬇️
synacktiv.com/advisories/ubi…

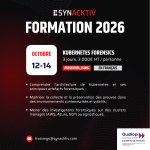
🚨 Un cluster Kubernetes est compromis.
Où sont les preuves ?
Conteneurs éphémères, logs distribués, workloads volatils… l’investigation forensique dans #Kubernetes ne s’improvise pas.
Retrouvez notre formation : Kubernetes Forensics ⬇️
synacktiv.com/offres/formati…

Synacktiv retweeted

🔥 What are you bringing to #Entrypoint?
New technique? Tool release? Real-world compromise? Deep technical offensive security talk?
🎤 CFP closes 20 September.
📅 19-20 March 2027 | 📍 Paris
➡️ cfp.entrypoint.fr/entrypoint…
