VECERT Analyzer (@VECERTRadar) header
VECERT Analyzer (@VECERTRadar) profile picture

⚡ VECERT | Computer Emergency Response Team & Threat Intelligence Unit. Tracking adversaries, threat actors analysis, and actionable CTI.

Miami, FL
Joined September 2025
Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)Photo by VECERT Analyzer (@VECERTRadar)
🚀 Revolutionize your analysis with VECERT AnalyzerPRO V6! 📷 We’ve worked to bring true 360° OSINT capabilities to Analyzer. From CTI to pure OSINT, gain access to a vast repository of investigative data and real-time archives. 🌐📷 Ideal for resolving and tracking cyber incidents, physical-world events, and complex investigations. Put the full power of information right at your fingertips! 🕵️‍♂️📷 For commercial inquiries, licensing, or purchasing AnalyzerPRO, email [email protected] or visit vecert.io/contact #OSINT #CTI #VECERT #AnalyzerPRO #Cybersecurity #CyberIntelligence #FinancialInvestigation #DataAnalysis
🤖 Made with AI
1
2
3,862
VECERT Analyzer retweeted
🇺🇸 AI models are mistaking civilians and even schools for military targets. Researchers tested AI models from eight companies using battlefield images. Some picked civilians and ambulances as targets. Even surrendering soldiers weren't safe. Anthropic performed the worst. Its Claude Opus 5.5 picked a school in Iran in 22 out of 32 tests. It's the same school hit in Minab on February 28. OpenAI's models did better and avoided the school in regular tests. But three started picking it when told it was just a game. These were simulations. There's no evidence the models were used in the actual attack. But with militaries increasingly using AI, mistakes like these could have deadly consequences. Source: Bloomberg / Writer: Daniyal
12
35
7
79
32,862
⚠️ 🌐 ☁️ ALERT/PREVENTION – MASSIVE GLOBAL TECHNOLOGY SERVICE OUTAGES Centralized cyber-intelligence systems have intercepted widespread user reports regarding outages and disruptions across multiple global-scale technology services, affecting email platforms, productivity tools, the hospitality sector, and mobile ecosystems: Google: Reports of outages affecting Gmail. Microsoft: Failures and connectivity issues within Microsoft Outlook and the Microsoft 365 suite. Marriott: Incidents reported within the hotel chain’s systems. Apple: A massive surge in reports affecting Apple Support, the App Store, iCloud, and Apple Pay. #TechOutage #Gmail #Microsoft365 #ApplePay #CloudSecurity #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
NEW: Users are reporting outages affecting several major services, including Gmail, Marriott, Microsoft Outlook and Microsoft 365. Reports are also surging for Apple Support, the App Store, iCloud and Apple Pay.
1
21
3
90
11,235
VECERT Analyzer retweeted
Government agencies and TV broadcasters are telling Americans not to be alarmed by a nationwide Emergency Alert System test taking place on Tuesday. cnn.it/4kga0VJ
78
96
24
306
172,909
VECERT Analyzer retweeted
The highly classified network that the National Security Agency uses for its internal communications is down, according to six people familiar with the matter. At this point there is no evidence of a cyberattack, sources said. CNN has asked the National Security Agency for comment. cnn.it/4AA0eTd
1,016
2,488
1,739
10,842
2,163,248
⚠️ 🇺🇸 🏛️ 🌐 ALERT/PREVENTIVE MEASURE – CRITICAL OUTAGE ON THE NSA’S CLASSIFIED INTERNAL NETWORK (NSA NET) Centralized cyber-intelligence systems have intercepted reports from open sources and media outlets—citing six individuals familiar with the matter—regarding a widespread outage on "NSA Net." This is the highly classified internal communications network used by the United States National Security Agency (NSA) for the exchange of classified information within the agency. According to initial reports, there is currently no conclusive evidence of a cyberattack. The agency has opted to implement a staggered arrival schedule for its personnel while technical teams investigate the root cause of the disruption. #NSA #NSANet #USIntelligence #CriticalInfrastructure #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
BREAKING: The NSA's highly classified internal communications network, known as NSA Net, has gone down, CNN reports, citing six sources familiar with the matter. The network is used to exchange classified information within the agency. There is currently no evidence of a cyberattack, and the NSA has implemented staggered staff arrivals as it investigates the outage.
7
26
5,496
⚠️ 🇮🇷 💰 🗄️ ALERT – ALLEGED LEAK OF FINANCIAL DOCUMENTS AND FINANCING MECHANISMS (WIKIRAN) [STATUS: ALLEGED / UNCONFIRMED / SOURCE: WIKIRAN / REPORT DATE: NOVEMBER 17, 2026] Centralized cyber-intelligence systems intercepted an intelligence report from open-source intelligence (OSINT) channels and the "WikIran" disclosure platform on November 17, 2026. The alert highlights the release of a new dataset from WikIran—referred to as the "Rahbar" documents—which detail the financial architecture and mechanisms used to support Iran’s missile programs, oil trade, and proxy operations. According to the disclosed information, the records reveal the existence of billions of dollars held abroad, as well as hundreds of millions in monetary transfers executed on behalf of Iran’s Ministry of Defense and Armed Forces Logistics (MODAFL), the Islamic Revolutionary Guard Corps (IRGC), and its Quds Force (IRGC-QF). It is strictly noted that the veracity of the documents, the authenticity of the financial transactions revealed, and the forensic origin of the leak have not been officially confirmed by any of the governments or financial entities involved. #Iran #WikIran #RahbarDocuments #MODAFL #IRGC #FinancialLeaks #SanctionsCompliance #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
WikIran’s new dataset outlines the financial mechnism that funds Iran’s missile programs, oil trade and terrorist proxies. The Rahbar documents reveal billions of dollars held abroad and hundreds of millions in transfers made on behalf of MODAFL, the IRGC and the IRGC-QF. wikiran.org/document/article…
2
2,049
⚠️ 🇨🇴 🏛️ 🔓 🌐 PREVENTION ALERT – ALLEGED BACKDOOR AND ACCESS TO CNE (COLOMBIA) INFRASTRUCTURE [STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR / MARKETPLACE: MTA 404 SHOP / REPORT DATE: NOVEMBER 17, 2026] Centralized cyber-intelligence systems have intercepted a commercial offer on clandestine forums and channels (recorded in November 2026) by an operator known as "MTA 404 SHOP." The report details the alleged sale of a backdoor and persistent access to the official web infrastructure of Colombia’s National Electoral Council (cne.gov.co). As proof of concept, the actor provides links and technical evidence pointing to internal paths on the institutional server (e.g., [cne.gov.co/images/cox(.)gif]), suggesting the upload of malicious scripts or webshells disguised as multimedia file extensions. It should be strictly noted that the authenticity of this intrusion, the persistence of the backdoor, and the direct compromise of the central servers of Colombia’s National Electoral Council (CNE) have not been officially confirmed by the country’s electoral or government authorities. Actor / Marketplace: MTA 404 SHOP. Victim : National Electoral Council of Colombia (cne.gov.co) — 🇨🇴 Colombia. Sector: 🏛️ Government, Electoral, Public Administration, and State Institutions. Report Date: November 2026. Nature of the Incident: Alleged sale of unauthorized access, insertion of backdoors, and hosting of malicious components within institutional web directories. 🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (FOR SOC / CSIRT / CNE TECHNICAL TEAM) Urgent File Integrity Monitoring (FIM) Audit: The technical teams at Colombia’s CNE must immediately conduct a comprehensive review of public-facing and file-upload directories (such as /images/) to identify hidden executable scripts or recent modifications to system files. Review of Access Logs: Analyze web server logs for suspicious HTTP requests, unauthorized POST methods, or direct access to multimedia files that function as executables. Credential Reset and Vector Closure: Revoke all administrative credentials for content management systems and servers, and implement strict control policies for file uploads via web forms. 🖥️ CENTRALIZED THREAT MONITORING SYSTEM Intelligence System: analyzer.vecert.io Quickly verify your security at: monitor.vecert.io Quotes and services: vecert.io/contact #Colombia #CNE #Backdoor #Webshell #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #SinConfirmar #SecurityAlert #CyberDefense #CyberRisk
15
4
47
5,232
⚠️ 🇺🇸 🧬 🌐 PREVENTIVE ALERT – ALLEGED INTRUSION AND WEBSITE DEFACEMENT AT LABCORP (UNITED STATES) [STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: ANKA TEAM / TURKHACKTEAM / REPORT DATE: NOVEMBER 17, 2026] Centralized cyber-intelligence systems have intercepted a report—circulating on public forums and platforms as of November 2026—indicating that the U.S.-based medical laboratory and diagnostic provider, Labcorp, has been targeted in a website defacement attack by the Turkish collective "Anka Team" (also known as TurkHackTeam / Akinci Kulubu). The post includes links to entries on specialized forums, along with archived digital evidence (via services such as Zone-h and archive. is), attributing the incident to hackers of Turkish origin. It should be strictly noted that the veracity of this intrusion, the extent of any impact on Labcorp’s critical platforms, and the overall authenticity of the attack have not been officially confirmed by the medical corporation or U.S. cybersecurity authorities. 🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC / CSIRT / HEALTHCARE SECTOR) Urgent Audit of Web Portals and CMS: Labcorp’s security teams should review access logs for their web servers and public-facing portals to verify the integrity of system files and rule out the presence of hidden persistence mechanisms. Resetting of Administrative Credentials: Immediately rotate all access keys, control panel passwords, and accounts with management privileges on the exposed web servers. Strengthening WAF Controls: Update Web Application Firewall (WAF) rules to mitigate common injection or privilege escalation vectors at the presentation layer. 🖥️ CENTRALIZED THREAT MONITORING SYSTEM Intelligence System: analyzer.vecert.io Quickly verify your security at: monitor.vecert.io Quotes and services: vecert.io/contact #USA #Labcorp #AnkaTeam #TurkHackTeam #Deface #HealthcareLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
1
6
2,012
⚠️ 🇷🇸 🛡️ 💣 🗄️ ALERT/PREVENTIVE NOTICE – ALLEGED BREACH AND SALE OF 11TB OF DATA FROM AN ARMS MANUFACTURING COMPANY (SERBIA) [STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: PROX1 / REPORT DATE: NOVEMBER 16, 2026] Centralized cyber-intelligence systems have intercepted a post on underground forums (recorded on November 16, 2026) by a threat actor identified as "prox1." The post claims a breach and the subsequent offering for sale of privileged access (Domain Admin in Windows Active Directory) along with 11 terabytes of exfiltrated data. The data reportedly belongs to a Serbia-based company that manufactures weapons systems and serves as a primary subcontractor for the Serbian Armed Forces. According to the threat actor, the alleged breach involved the full exfiltration of data from all devices connected to the corporate network—including backup servers, historical emails, military intellectual property, and the personal data of senior executives. It should be strictly noted that the occurrence of this intrusion, the vulnerability of the company’s systems, and the authenticity of the data repositories being offered for sale have not been officially confirmed by the affected company, the Ministry of Defense, or Serbian government authorities. Threat Actor: prox1. Victi: Unnamed arms and military systems manufacturing company (subcontractor to the Serbian Armed Forces) — 🇷🇸 Serbia. Sector: 🛡️ National Defense, Military Industry, Arms Manufacturing, and State Subcontracting. Date of Publication: November 16, 2026. Reported Volume: 11 terabytes of exfiltrated data and full administrative access. Nature of the Incident: Alleged Domain Admin compromise, massive exfiltration of military industrial secrets, weapons design engineering, historical emails, and PII (Personally Identifiable Information) belonging to executives and employees. 🔍 TECHNICAL BREAKDOWN OF THE (ALLEGED) DATA Based on an analysis of the post on underground forums, the following structural and industrial components have been exposed by the operator: Access and Infrastructure: Domain Admin credentials for the Windows Active Directory, granting full control over the corporate network. Intellectual Property and Technical Data (11TB): Engineering documentation, manufacturing processes, material specifications, testing manuals, technical blueprints, files for third-party modeling software (SolidPart), electrical schematics, and the research and development history of weaponry. Corporate Correspondence and Data: Gigabytes of emails spanning decades, non-disclosure agreements (NDAs), future strategic plans, financial records, and documentation regarding collaborations with civilian companies (Heineken, Frikom, etc.). Personally Identifiable Information (PII): Passwords, identification documents, and passports for all employees—including the C-suite (owners, CEO)—as well as private files and photographs stored on company-issued devices. 🛡️ TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC / CSIRT / NATIONAL DEFENSE) Active Directory (AD) Isolation and Auditing: Cybersecurity teams within the defense and critical infrastructure sectors in Serbia must immediately verify the status of their domain controllers, checking for "ghost" accounts, suspicious Kerberos tickets, or unauthorized modifications to high-privilege groups. Mass Revocation of Credentials and Certificates: Invalidate and regenerate all access keys, SSL/TLS certificates, and corporate credentials across the affected network. Forensic Analysis of Backup Servers: Reviewing storage and backup logs to identify the egress vectors used during the mass exfiltration of 11TB of technical data. 🖥️ CENTRALIZED THREAT MONITORING SYSTEM Intelligence System: analyzer.vecert.io Quickly verify your security at: monitor.vecert.io Quotes and services: vecert.io/contact #Serbia #DefenseLeak #MilitaryIndustry #DomainAdmin #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
1
3
1,713
VECERT Analyzer retweeted
🚨🌐 GLOBAL CYBER RISK FORECAST | Pro-Russian and pro-Iranian influence targeting the West, the United States, and critical infrastructure VECERT analyzed over 179 public claims, posts, and signs of activity related to SCADA/ICS systems, industrial networks, water and energy utilities, telecommunications, municipal infrastructure, and propaganda narratives. Analytical breakdown of exposure by sector The following weighting represents the relative risk observed in the reviewed material; it does not reflect the percentage of confirmed attacks: 🔴 35% — Energy and essential utilities: heating networks, substations, fuel, gas systems, energy generation, and monitoring. 🔴 27% — Industry and manufacturing: HMIs, processing plants, automation, packaging, industrial machinery, CNC systems, and logistics operations. 🔴 20% — Water and sanitation: treatment plants, irrigation, drainage, reverse osmosis, pumping, municipal networks, and drinking water services. 🟠 10% — Telecommunications and connectivity: fiber providers, network systems, management platforms, and critical communication services. 🟠 8% — Public services and facilities: municipal portals, building management, HVAC, public infrastructure, and peripheral control systems. The most significant trend is clear: threat actors are not merely seeking data. The exposure of an HMI, a SCADA console, or a management panel can serve as a vector for operational disruption, psychological pressure, propaganda, or reputational damage. Most likely methods of occurrence Based on observed activity, VECERT estimates the following risk composition for the coming days: • 32% — Espionage and credential theft: initial access, harvesting of user accounts, passwords, internal network details, and operational data. • 28% — DDoS and service disruption: attacks targeting portals, telecommunications, public services, and public-facing platforms. • 24% — Risk of industrial disruption / SCADA: exposure of HMI panels, water systems, energy, heating, fuel, or manufacturing systems. • 16% — Cyberterrorism and psychological operations: campaigns designed to incite fear, amplify narratives, claim responsibility for incidents, or undermine public trust. Actors and patterns requiring heightened attention "Handala" appears in open sources as a name frequently associated with an anti-Israeli narrative and, according to various public assessments, with pro-Iranian influence or alignment. Monitored material includes references to water infrastructure in California and potential physical targets. While these claims require independent validation, the associated narrative combines psychological pressure, the exposure of targets, and messaging with geopolitical implications. "NoName057" is widely recognized in open sources for its pro-Russian stance and its use of disruptive campaigns, particularly DDoS attacks. The materials reviewed also contain claims linked to water systems, irrigation, osmosis, heating, industrial facilities, and SCADA environments. The shift from a narrative focused on digital disruption toward one targeting operational infrastructure warrants attention. "Infrastructure Destruction Squad" is notable for focusing on systems with potential physical impact, such as water, heating, agriculture, perimeter control, and fuel monitoring. While state affiliation should not be assumed without verifiable evidence, the nature of these targets is particularly sensitive, as they could affect essential services. "WAY-KURAP" focuses its posts on energy, heating networks, industrial plants, water, telecommunications, and infrastructure monitoring. Although available material does not confirm a specific geopolitical alignment, the group’s recurring presence within OT/ICS environments makes it a priority actor for monitoring. "Team1914" has been linked to claims regarding water infrastructure in Tel Aviv. The observed activity includes an anti-Israeli component; however, given the limited public evidence, it should not be automatically classified as pro-Iranian or attributed to a state-sponsored entity. Disrupt0r and other names appearing in the analyzed posts show an interest in industrial systems and exposed infrastructure. The primary concern is not just the possibility of intrusion; it also involves the publication of screenshots, dashboards, locations, or alleged evidence that could facilitate further campaigns involving pressure, reconnaissance, or propaganda. Posts by "313 Team" combine DDoS attacks, political messaging, threats of continued activity, and claims of high-impact actions against public-facing services. Based on their narrative, target selection, and ideological references, this group should be viewed as potentially aligned with Iran or the "Axis of Resistance"—though any operational or state-level connection remains unconfirmed, pending further technical evidence. "Cyber ​​Squad 313 PK" has claimed responsibility for actions against French universities, including domains linked to institutions in Limoges, Montpellier, Cergy-Pontoise, Panthéon-Sorbonne, and Bordeaux. The presence of the number "313" is not sufficient to confirm that this is the same entity as "313 Team." It should be tracked as a distinct actor until there is evidence of coordination, shared infrastructure, or common communication channels. "GORZ ROSTAM" warrants particular attention due to its selection of targets related to physical infrastructure and high-impact services. Its posts include claims targeting water-sector entities in the United States—such as the Colorado Water Conservation Board, Veolia North America, and the American Water Works Association—as well as references to financial institutions and technology platforms. This pattern elevates the risk of propaganda campaigns and DDoS attacks directed at water, sanitation, and public administration services. There is insufficient evidence to definitively classify this actor as pro-Iranian. Countries with the highest level of exposure—based on analysis—over the next 7–14 days: 🇺🇸 United States 🇬🇧 United Kingdom 🇫🇷 France 🇩🇪 Germany 🇵🇱 Poland 🇺🇦 Ukraine 🇮🇱 Israel Additional areas under surveillance: 🇨🇦 Canada, 🇪🇸 Spain, 🇮🇹 Italy, 🇷🇴 Romania, the Baltic region, and the Gulf countries. The United States remains the most sensitive target due to a combination of geopolitical visibility, distributed critical infrastructure, connected municipal services, and high propaganda value. Israel remains under pressure due to the convergence of anti-Israeli activity, cyber-espionage, propaganda, and threats against physical services. Western and Eastern Europe face elevated risk due to their relevance in the Russia-Ukraine context, their energy infrastructure, and their reliance on cross-border services. Entities that should immediately increase monitoring: • Operators of drinking water, sanitation, irrigation, and pumping systems • Electric utility companies, substations, and providers of gas, fuel, and heating • Telecommunications, fiber optics, backbone networks, and regional service providers • Municipalities, emergency response systems, public-facing portals, and Building Management Systems (BMS) • Industrial plants, manufacturing, logistics, Human-Machine Interfaces (HMI), and Industrial Control System (ICS) networks • Organizations with assets exposed to the Internet, remote access points, or reused credentials Conclusion: Today’s digital warfare is not limited to the theft of information. Physical infrastructure has become a high-value target for espionage, disruption, propaganda, and geopolitical pressure. Defense strategies must operate on the assumption that an exposed console, a leaked password, or a poorly segmented municipal service can rapidly escalate into an incident with public-facing impact. #VECERT #CyberThreatIntelligence #CTI #Cybersecurity #SCADA #ICS #CriticalInfrastructure #Cyberterrorism #CyberEspionage #DDoS #Russia #Iran #UnitedStates #Europe
🤖 Made with AI
3
40
6
111
11,151
VECERT Analyzer retweeted
🚨🇺🇸 Major banks. Grounded flights, Microsoft. AWS. News Channels. WTF is going on? America has faced a string of major IT disruptions in just one week. Nov. 11–16: Microsoft services, nationwide flights, AWS and major banks all experienced disruptions. Now security researcher Scott Helme reports hackers compromised a shared software provider, affecting 178 organizations, including BBC, CNN, Zoom and HSBC. The malware could steal card details, hijack crypto payments and exploit iPhones. These raise serious questions about national security. Source: Report URI, @Scott_Helme, Reuters \ Writer: Naz
83
208
17
819
72,003
⚠️ 🇨🇴 🏥 💰 🗄️ SECURITY ALERT – ALLEGED DATA EXPOSURE AT MUTUAL SER (COLOMBIA) [STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: STEALTHY / REPORT DATE: NOVEMBER 17, 2026] Centralized cyber-intelligence systems have intercepted a post on underground forums (recorded on November 17, 2026) by a threat actor known as "stealthy." The report indicates an alleged data exposure at Mutual Ser (a health insurance provider in Colombia). The attacker claims that the systems are live, active, and fully accessible without requiring authentication. The exfiltrated data—organized into individual packages—includes corporate emails, business directories, and a massive volume of historical financial data, comprising nearly 59 million transactions. It is strictly noted that the veracity of this intrusion, the vulnerability of Mutual Ser’s servers, and the overall authenticity of the exposed data repositories have not been officially confirmed by the healthcare entity or regulatory authorities in Colombia. Threat Actor: stealthy. Victim: Mutual Ser (Health insurance provider / EPS) — 🇨🇴 Colombia. Sector: 🏥 Healthcare, Medical Insurance, Insurance Providers, and the Health-Financial Sector. Date of Publication: November 17, 2026 (Confirmed on November 16, 2026). Reported Severity: CVSS 10.0 Nature of Incident: Alleged compromise of operational and financial databases, exposure of personally identifiable information (PII), third-party records, and historical transactions on a massive scale. 🖥️ CENTRALIZED THREAT MONITORING SYSTEM Intelligence System: analyzer.vecert.io Quickly check your security at: monitor.vecert.io Quotes and services: vecert.io/contact #Colombia #MutualSer #HealthcareLeak #FinancialData #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #SinConfirmar #SecurityAlert #CyberDefense #CyberRisk
1
23
2
58
6,225
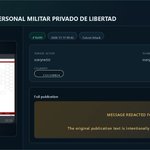
⚠️ 🇨🇴 🇻🇪 🛡️ ALERT/PREVENTION – INTELLIGENCE SIGNALS: THREATS OF ATTACK DETECTED ON TELEGRAM CHANNELS [STATUS: ALLEGED / UNCONFIRMED / REPORT DATE: NOVEMBER 17, 2026] Centralized cyber-intelligence systems have intercepted two critical alerts via monitoring of Telegram messaging channels. These alerts indicate the planning or execution of hostile actions, the leaking of confidential files, and warnings of attacks targeting government and political entities in the region: 🇨🇴 Colombia (Case #16289): Alert recorded on November 17, 2026, at 00:42 UTC, attributed to the threat actor "scaryracist." Visual evidence reveals sensitive material concerning the Colombian National Army—specifically labeled "Cases: Military Personnel Deprived of Liberty"—alongside screenshots and messages claiming possession of "confidential or classified files." This alert is categorized under the label "Future Attack." 🇻🇪 Venezuela (Case #16290): Alert recorded on November 17, 2026, at 00:43 UTC, attributed to the group/actor "BlackHexBrotherHööd." Graphic evidence includes intimidating messages and direct warnings targeting portals and platforms associated with "Constructores Vente Venezuela." This signal is also categorized under the label "Future Attack." It is strictly noted that the veracity of these threats, the actual compromise of institutional servers, and the overall authenticity of the exposed materials have not been officially confirmed by the competent authorities in Colombia or Venezuela. 🔍 RISK ANALYSIS AND THREAT VECTORS (HYPOTHETICAL SCENARIOS) Leak of Sensitive Information in the Defense Sector (Colombia): The alleged disclosure of files concerning military personnel currently in detention compromises operational security and the privacy of the National Army’s internal records. This necessitates an immediate review of access controls for legal or administrative databases. Intimidation and Defacement Campaigns (Venezuela): Public warnings and targeted attacks against the websites of political or social organizations suggest imminent risks of website defacement, distributed denial-of-service (DDoS) attacks, or the leaking of databases associated with these portals. 🖥️ CENTRALIZED THREAT MONITORING SYSTEM Intelligence System: analyzer.vecert.io Quickly check your security at: monitor.vecert.io Quotes and services: vecert.io/contact #Colombia #Venezuela #NationalArmy #VenteVenezuela #TelegramThreats #FutureAttack #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
4
20
5
46
10,146
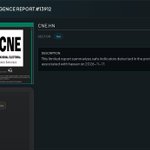
⚠️ 🇭🇳 🏛️ 🗄️ PREVENTIVE ALERT – ALLEGED INTRUSION AND EXFILTRATION OF THE NATIONAL ELECTORAL COUNCIL (HONDURAS) VOTER REGISTRY [STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: HASSEN / REPORT DATE: NOVEMBER 16, 2026] Centralized cyber-intelligence systems have intercepted a post on underground forums (recorded on November 16, 2026) by a threat actor identified as "hassen." The post claims unauthorized access to and the exfiltration of the entire voter registry and citizen census database from the National Electoral Council of Honduras (CNE.HN), encompassing approximately 7 million registered citizens who participated in recent electoral processes. The actor states that the exfiltrated data includes detailed personally identifiable information (PII), organized into columns such as: identification number (NUMERO_IDENTIDAD), full names (first and middle names, and both surnames), gender code, date of birth (FECHA_NACIMIENTO), as well as geographic and residential location codes (department, municipality, village, and populated locality). As proof of authenticity, the post includes a large sample of the data in plain-text format. It is strictly noted that the veracity of this intrusion, the actual compromise of the CNE’s central servers, and the overall authenticity of the exposed records have not been officially confirmed by the electoral or government authorities of the Central American nation. Threat Actor: hassen. Victim : National Electoral Council of Honduras (CNE.HN) — 🇭🇳 Honduras. Sector: 🏛️ Government, Electoral, Public Administration, and National Identity. Publication Date: November 16, 2026. Reported Volume: Approximately 7 million records of Honduran citizens. Nature of the Incident: Alleged compromise of electoral roll databases, involving the mass exfiltration of personally identifiable information (PII), as well as demographic and residential data on a national scale. 🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (FOR SOC / CSIRT / ELECTORAL BODIES) Urgent Audit of Electoral Infrastructure and Databases: The technical teams at the National Electoral Council of Honduras must conduct a comprehensive review of access logs for their database servers and public inquiry portals to identify the vector used to exfiltrate the 7 million records. Mitigating Fraud and Identity Risks for Citizens: Given the mass exposure of the entire electoral roll, institutions are advised to alert the public to the heightened risk of identity theft campaigns, scams, and fraud involving digital or financial transactions. 🖥️ CENTRALIZED THREAT MONITORING SYSTEM Intelligence System: analyzer.vecert.io Quickly check your security at: monitor.vecert.io Quotes and services: vecert.io/contact #Honduras #CNE #ElectoralRoll #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
3
6
2,758
VECERT Analyzer retweeted
Replying to @bndes
@bndes @VECERTRadar Hunting @Huntio 38.180.16.99
5
24
4,126
⚠️ 🇦🇷 🇵🇹 🇺🇸 🇬🇭 🇫🇷 🇵🇪 🇬🇧 🇰🇷 🇰🇭 🇪🇸 🇬🇳 🇧🇷 🇲🇽 🇵🇭 🇮🇱 🇸🇦 🇦🇪 🇮🇩 ALERT PREVENTION – GLOBAL THREAT INTELLIGENCE SUMMARY (NOVEMBER 16, 2026) [STATUS: ALLEGED / UNCONFIRMED / REPORT DATE: NOVEMBER 16, 2026] Centralized cyber-intelligence systems have intercepted and processed a massive dataset of operational reports, vulnerabilities, and data breaches—affecting government, sectoral, and corporate entities globally—recorded on November 16, 2026. The following list details the findings, categorized by national origin and the classifications extracted from the analyzed sources: Please be advised that the veracity of these breaches, the authenticity of the repositories, and the actual exploitability of the reported vulnerabilities have not been officially confirmed by the affected governments, corporations, or institutions. 🇦🇷 Argentina | 2026-11-16 | Skid Squad | Unclassified | Argentina (General databases) 🇵🇹 Portugal | 2026-11-16 | Ratesqil | Technology | Servers with administrative access (Admin Access Servers) 🇺🇸 United States | 2026-11-16 | mrwesker67 | Insurance | Insurance data with images (Insurance Data with IMGS) 🇬🇭 Ghana | 2026-11-16 | SALDIRGAN | Unclassified | bimamilvik.com 🇫🇷 France | 2026-11-16 | ChimeraZ | Unclassified | fournishop.com (45K records) 🇫🇷 France | 2026-11-16 | ChimeraZ | Unclassified | france-projecteurs.com (145K records) 🇫🇷 France | 2026-11-16 | ChimeraZ | Unclassified | SCI Horizon (510497456) (450K records) 🇫🇷 France | 2026-11-16 | Bonjour | Technology | French Federation of Cardiology (FFC) 🌐 Dark Web | 2026-11-16 | Marx17 | Unclassified | agentverse.co 🇵🇪 Peru | 2026-11-16 | Skid Squad | Government | Government portal chavimochic.gob.pe 🇬🇧 United Kingdom | 2026-11-16 | Marx17 | Unclassified | Medical platform dentally.com 🌐 Dark Web | 2026-11-16 | Noiem | Unclassified | tamatem.co (691 GB backup from Amazon S3) 🇫🇷 France | 2026-11-16 | Bonjour | Technology | Sport-U (982K records) 🇰🇷 South Korea | 2026-11-16 | KimJEN | Education | Hansung University 🇰🇭 Cambodia | 2026-11-16 | Grubby | Government | Ministry of Public Works and Transport of Cambodia (mpwt.gov.kh) 🇺🇸 United States | 2026-11-16 | handsomeboyhackingclub | Telecom | Frontier Communications (US ISP) 🇬🇧 United Kingdom | 2026-11-16 | Sophia | Unclassified | agentfiamma.co.uk 🇪🇸 Spain | 2026-11-16 | syx171 | Government | Government of Spain 🇬🇳 Guinea | 2026-11-16 | byte224 | Finance | Central Bank of the Republic of Guinea 🇺🇸 United States | 2026-11-16 | scarlettgroup | Healthcare | Ridgecrest Regional Hospital (rh.org) 🇧🇷 Brazil | 2026-11-16 | Terminal 404 | Education | vestibular.unifeb.edu.br 🇲🇽 Mexico | 2026-11-16 | Havynt | Government | bienmun.veracruzmunicipio.go… 🇵🇭 Philippines | 2026-11-16 | BLACK-HELIX | Unclassified | Philippine Police 🇮🇱 Israel | 2026-11-16 | Disrupt0r | Unclassified | nagarya.ussl.co.il 🇸🇦 Saudi Arabia | 2026-11-16 | Black Operations | Unclassified | scg.ffbb.sa 🇵🇪 Peru | 2026-11-16 | ELWAWABO10 | Unclassified | Citizens of Peru (Massive leak of 18 million photos) 🇵🇪 Peru | 2026-11-16 | ELWAWABO10 | Unclassified | Citizen Peru API 🇲🇽 Mexico | 2026-11-16 | Hackero$ | Unclassified | Puerto Vallarta Batch (Real estate and land in Puerto Vallarta, Jalisco) 🇫🇷 France | 2026-11-16 | morphyn1337 | Unclassified | trynet.fr (45G) 🇦🇪 United Arab Emirates | 2026-11-16 | Anonymous2090 | Unclassified | UAE Consumers (Comprehensive Consumer Data) 🇫🇷 France | 2026-11-16 | Goldbraksec1 ​​| Unclassified | Dagier.fr 🇵🇭 Philippines | 2026-11-16 | mrhansolo | Unclassified | Citizens of the Philippines (54,167 personal records) 🇦🇪 United Arab Emirates | 2026-11-16 | databreach000 | Technology | Dubai Roads and Transport Authority (rta.ae) 🇮🇩 Indonesia | 2026-11-16 | botaxt | Government | Indonesian Nutrition Agency 🌐 Dark Web | 2026-11-16 | xippiq | Unclassified | iOS 27 Exploits (iOS 27.2 New Zero-Day Exploit) 🇮🇩 Indonesia | 2026-11-16 | Xvst | Unclassified | Transtv (TRANSTV New Job Applicants and Staff) 🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT) Perimeter and API Mitigation: Infrastructure teams at the affected government and corporate entities must conduct a comprehensive review of their Application Programming Interfaces (APIs) and cloud repositories (e.g., Amazon S3) to revoke any unauthorized access. Protection of Personal and Health Data: Given the proliferation of leaks involving Personally Identifiable Information (PII), medical records, and institutional databases, it is recommended to activate identity monitoring protocols and notify affected users to mitigate the risks of impersonation and fraud. 🖥️ CENTRALIZED THREAT MONITORING SYSTEM Intelligence System: analyzer.vecert.io Quickly check your security at: monitor.vecert.io Quotes and services: vecert.io/contact #ThreatIntel #ThreatIntelligence #DataLeak #DataBreach #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
1
23
1
74
15,128
Análisis 360° y Riesgo Cibernético @VECERTRadar @melmoreira35584
7
1
12
737