

Ethical Hacker & Pentester 👾 || Red Teaming || SaaS || Networking
terminal
Joined July 2022
- Tweets71
- Following6
- Followers11
- Likes40


Pinned Tweet
Hey, Quham here. I love connecting with people who build cool things and those who break them.
Let’s talk if you’re into:
→ Pentesting & Red Teaming
→ AI & AI Agents
→ SaaS
→ Web App Security & CTFs
→ Full-Stack Dev
Always down to collaborate. Drop a 👋 or send a DM.
Looking to connect with active cybersecurity communities focused on ethical hacking, web app security & red teaming. 🔐
Discord, Slack or local groups? If you know a solid community sharing writeups, labs & feedback, drop an invite or DM me!
21
🚨 Devs, DROP EVERYTHING!
Google is sponsoring DevFest Ibadan 2026! 🤯
Use code GOOGLE at checkout. My ticket just dropped to ₦0!
Only the first 100 get this deal. DON'T WAIT. GO NOW! 🚀
#DevFestIbadan #NigeriaTech #DevFest
22
It's time I stopped building alone.
I've been applying for hackathons, and one thing keeps coming up: having a team. It's becoming a limiting factor.
I'm looking to connect with people who enjoy building, solving problems, and turning ideas into reality.
Let's build. 🚀
2
1
54
As a founder, I’m realizing building the product is only half the battle. 😮💨
You can build something useful, but if nobody knows it exists, how will they use it?
Founders, how are you getting your product in front of the right people? 🚀
6
I need honest answers from devs on this one 👇
At what point does building become procrastination?
#webdev
35

Quham Raheem ⚡ retweeted
Hey, Quham here. I love connecting with people who build cool things and those who break them.
Let’s talk if you’re into:
→ Pentesting & Red Teaming
→ AI & AI Agents
→ SaaS
→ Web App Security & CTFs
→ Full-Stack Dev
Always down to collaborate. Drop a 👋 or send a DM.
🔓 Your frontend looks secure. But what if your API exposes another user's private data?
As developers, we need to ask more than "Does it work?" We must ask, "How could someone exploit it?"
Think like an attacker. Build like a defender. 🛡️
#InfoSec #OffensiveSecurity
I’m building Q-Book, a bookkeeping product for Nigerian small businesses.
I’d love to connect with people interested in startups, growth, customer research, and building tech for African markets.
Let’s connect and build! 🚀
#BuildInPublic #Startups
4
5
98
Gearing up for the @CyberWarFareLab CRTA exam! 🎯 If you've conquered it, I want to hear from you. What was the hardest part of the labs?
My DMs are open. Slide in, share your experience, and let’s talk red teaming! 👻
25
Network ping! 🌐
I’m an Ethical Hacker bridging the gap between offensive security and SaaS development. When I’m not in the lab hunting vulnerabilities or red teaming, I’m researching the future of AI agents. If you're in Infosec, Web Dev, or AI, let's connect. 👾
1
1
23
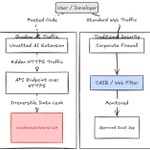
Standard security hygiene isn't enough for Cybersecurity Awareness Month. Building full-stack web apps & running pen tests, I see firsthand that the real threat redefining 2026 is Agentic AI and the explosion of Shadow AI. 🧵
#CybersecurityAwarenessMonth
1
17
In multi-agent setups, risks escalate fast. When high-privilege orchestrators blindly trust sub-agents, attackers pivot to trigger cascading failures (ASI08). Traditional scanners miss this because commands are hidden in standard HTTPS traffic.
1
2
Connecting the dots between #CyberSecurity, #RedTeaming, and building #AI #SaaS products. Let's grow! 👾
8