
Security researcher | Independent thinker | Found +200 H/M | 90+ audits
dark forest
Joined August 2010
- Tweets8.2K
- Following509
- Followers303
- Likes10.7K






Pinned Tweet
Stablecoins are becoming a significant absorber of US debt. They mint stable, buy US debt with your dollars, pocket the 4-5 % yield, give you zero, and in the process become a huge, price-insensitive buyer of US debt pushing bill yields down and the dollar up. Bitcoin was created by US gov to save his economy.

0xbepresent retweeted

The Arbitrum Security Council has taken emergency action to rescue the 74,559,805 ARB and 8,425 ETH being held in the address on Arbitrum One that is identified as connected to the Binance exploit. The Security Council acted by weighing its commitment to the security and integrity of the Arbitrum community and Arbitrum governance without impacting any Arbitrum users or applications.
After significant technical diligence and deliberation, the Security Council identified and executed a technical approach to move funds to safety without affecting any other chain state or other Arbitrum users.
As of October 30, 2026 time, the funds have been successfully transferred to an intermediary frozen wallet. They are no longer accessible to the address that originally held the funds, and can only be moved by further action of the Security Council or a vote of Arbitrum DAO governance, which will be coordinated with relevant parties.
0xbepresent retweeted

A friend responsibly disclosed a critical fund drain vulnerability to a protocol.
They downgraded the severity. Paid him $75 "appreciation" and told him to use it for his Claude subscription (which costs $200). Then refused to fix the bug.
Today that same protocol got drained from the exact exploit he reported.
If you have substantiatial money in DeFI, i advice you pull it out. Some of these protocols you're trusting with your funds genuinely do not care about securing them.
0xbepresent retweeted

Our AI found a bug that let anyone mint infinite XRP, with $94B at risk. It had been hiding in one of the most audited codebases in crypto for nearly a decade, and earned us the maximum $250K bounty.
Here's how it went unnoticed, and how we found it.
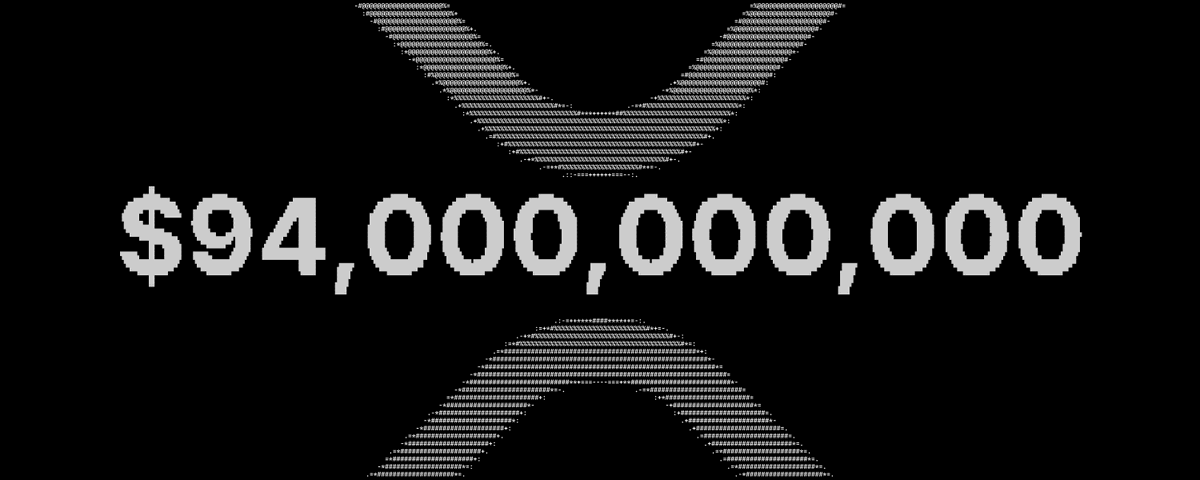
0xbepresent retweeted

The next top hackers won't be the ones who know the most. They'll be the ones who can operate their minds at full speed without burning out


0xbepresent retweeted

⚡️Let me tell you why you’re here.
You’re here because you know something.
What you know you can’t explain, but you feel it.
You’ve felt it your entire life, that there’s something wrong with the world.
You don’t know what it is, but it’s there, like a splinter in your mind, driving you mad.
If you spend enough time on the charts, the price delivery algorithm becomes visible, the imbalances (bugs) waiting to be balanced (fixed).
Just like a bug bounty…except the market judges instantly.
nitter.cf/0xjuaan/status/2081685…

trading is kinda similar to auditing/bug bounties.
in both, you get rewarded for deeply understanding a system and uncovering nuances that others haven't spotted.
1
279
An incredible trip, thank you for everything 🫡 @code4rena nitter.cf/code4rena/status/20544…

After careful consideration, we’ve made the decision to wind down @code4rena. This community has meant a great deal to everyone who has been part of building it, and sharing this news is not easy.
151
0xbepresent retweeted

"Coded" by Claude on Feb 1st.
"Audited" by Claude on Feb 2nd.
"Fixed" by Claude on Feb 3rd.
Deployed to mainnet (by Claude?) on March 19th.
Funded on April 24th.
Rekt (by Claude?) on April 28th.
Welcome to the future. 🤡🤡🤡🤡🤡🤡🤡

It seems a @tradingprotocol vault, i.e., YieldCore-3rd-deal, was exploited with $398k loss.
There is a missing check on the caller authorization, which is exploited to drain all funds from the vault.
Here is the related tx:
etherscan.io/tx/0x6b04344d56…

The number of truly decentralized protocols can be counted on one hand. In fact, devs of these protocols need opsec in case any 3-letter agency is interested. Regulations are coming—create the problem, offer the solution. nitter.cf/arbitrum/status/204643…

The Arbitrum Security Council has taken emergency action to freeze the 30,766 ETH being held in the address on Arbitrum One that is connected to the KelpDAO exploit. The Security Council acted with input from law enforcement as to the exploiter’s identity, and, at all times, weighed its commitment to the security and integrity of the Arbitrum community without impacting any Arbitrum users or applications.
After significant technical diligence and deliberation, the Security Council identified and executed a technical approach to move funds to safety without affecting any other chain state or Arbitrum users.
As of April 20 11:26pm ET the funds have been successfully transferred to an intermediary frozen wallet. They are no longer accessible to the address that originally held the funds, and can only be moved by further action by Arbitrum governance, which will be coordinated with relevant parties.
92

0xbepresent retweeted

When a single private key can drain the protocol by design - it's probably not DeFi, it's CeDeFi. And that's ok, but it requires DevOps being very well organized.
I prefer building real DeFi

These Resolv guys are straight-up clowns 🤡
Looks like the “exploiter” was basically an insider — probably some engineer who knew exactly how sloppy their security was.
Total damage by now: ~11,318 ETH (~$23.8M), now just chilling on this address:
0x8ed8cf0c1c531c1b20848e78f1cb32fa5b99b81c
What’s even funnier — the exploiter casually spent 4 HOURS swapping wstUSR into USDC/USDT, patiently waiting for traders to buy the depeg back up lol (and even now keep swapping). On top of that, they kept abusing the mint bug multiple times over several hours. Team must’ve been on weekend mode with laptops fully closed.
Either way, no shot they’re covering a $23.8M hole. But the real comedy is how they handled the situation (spoiler: as badly as possible).
At this point, only a full reboot could justify holding USR.
RIP RESOLV 💀

0xbepresent retweeted

Your brain is under attack by a trillion dollar adversary intent on destroying it.
This is your David vs Goliath.
Resist the algorithm.

Thinking more about that deterministic tools + AI bridge...
If AI can reach high confidence on bugs by cross-verifying with tools like CodeQL (querying code paths precisely, no hallucinations), why not speed up judging in audit contests?
Attack vector hypothesis → AI runs CodeQL queries + maybe generates/runs PoC tests → flags/validates issues faster. Human judges focus on edge cases & severity debates instead of initial triage.
Could make contests way more efficient (fewer duplicates, quicker payouts). Built a tiny prototype with Ouroborus and it already feels promising.
nitter.cf/0xbepresent/status/202…

Been vibecoding lately and it's honestly changing how I see smart contract audit.
What if we built better bridges between deterministic tools (like Slither) and AI? Created a quick CLI called Ouroborus that pipes Slither findings → AI verification (using CodeQL to double-check issues in the code). Super basic, but context engineering + focused inputs = way less hallucination and sharper focus.
Built the whole thing in ~2 days and cool... hacking just got even more interesting and fun.
github.com/0xbepresent/ourob…
1
1
194
Been vibecoding lately and it's honestly changing how I see smart contract audit.
What if we built better bridges between deterministic tools (like Slither) and AI? Created a quick CLI called Ouroborus that pipes Slither findings → AI verification (using CodeQL to double-check issues in the code). Super basic, but context engineering + focused inputs = way less hallucination and sharper focus.
Built the whole thing in ~2 days and cool... hacking just got even more interesting and fun.
github.com/0xbepresent/ourob…
1
4
361
"There will even be people who continue to defend the system; most aren't ready to be unplugged." nitter.cf/i/status/2018624544991…
1
1
292

