

The official account for 13Cubed Studios LLC.
Georgia, USA
Joined April 2019
- Tweets374
- Following0
- Followers8.3K
- Likes884


Pinned Tweet
🎉 Big news! Investigating macOS Endpoints is now live—plus our new *NIX Bundle and XPlat Bundle Complete (all 13Cubed courses in one package). Thanks for patiently waiting! Dive in now 👉 training.13cubed.com #DFIR #macOS #Linux
Investigating Windows Endpoints has already been validated with the updated tooling. Like all our courses, we have you download the latest versions of all tools, so you're always working with the latest and greatest. 👇

1/ EZ Tools 2026.10 is out, all on .NET 10 (LTS)
✅ More accurate: 331K more event log records, hive logs replayed as Windows does, every test hive loads
⚡ Faster: up to 9x; EvtxECmd and Registry 2x
📉 Less memory: up to 82% less
Update with Get-ZimmermanTools 🧵 #DFIR

It's time for a new 13Cubed episode, and this one's a bit special.
I spent nearly six years at Microsoft. Then, right after getting promoted, I quit.
In this episode, I'm stepping away from the usual technical content to tell that story, and explain why I decided it was time to walk away.
▶️ youtube.com/watch?v=OnavGwRI…
#DFIR #DigitalForensics #Forensics #ComputerForensics #WindowsForensics

🎉👇

🏆 What a finish to our September competition!
Participants tackled a real case simulating an Iranian APT campaign, tracing the attack through the evidence. The leaderboard stayed close throughout. 🔎
Congratulations to the top three:
🥇 Bombolone (Carlo Luciani) - Prize: "Investigating Windows Endpoints" course courtesy of @13CubedDFIR 🙏
🥈 @KoifSec - Prize: x2 months of Threat Hunting Labs access
🥉 aboelrous (Omar A.) - Prize: x1 month of Threat Hunting Labs access
Thanks to everyone who took part and made it such a great event! 🔥 The lab that was used in this competition is available for our labs subscribers with a full report.
Each question has a walkthrough video courtesy of Andrew from Empirical Training. Go check out his YouTube channel youtube.com/@andrewcyberjone…
Check out 13Cubed Training courses: training.13cubed.com/
Lab: threathuntinglabs.com/threat…

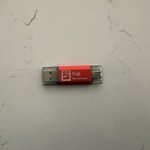
13Cubed is proud to support the development of Fuji from @thelazza, our go-to tool for macOS forensic acquisition.
We were lucky enough to receive this limited-edition Fuji USB, pre-loaded and ready to make acquisitions even easier. 🔥
Check out Fuji in action 👇
youtube.com/watch?v=9ZkLdFod…


Another impressively in-depth review of a 13Cubed course from Krzysztof Kuzin. This time, he takes a deep dive into Investigating Windows Memory (IWM).
Check out the full IWM review here 👉
krzysztofkuzin.substack.com/…
And if you missed his review of Investigating Windows Endpoints (IWE), you can find that here 👉
krzysztofkuzin.substack.com/…
Great to see these courses covered in this level of detail!
13Cubed retweeted

Threat Hunting League is open for registration with less than 10 days to go!
Intrusion: Iranian APT Campaign
Sep 25–27 · 4-hour personal lab run
Entry: $15 or 12 THL credits
Prizes:
1st — 13Cubed Investigating Windows Endpoints ($795)
2nd — 2 months of Threat Hunting Labs + a 30-minute coaching session
3rd — 1 month of Threat Hunting Labs
Thank you @13CubedDFIR for backing the first competition!
threathuntinglabs.com/compet…

🏆 Introducing the XPlat Forensic Investigator (XPFI) credential from 13Cubed.
Digital forensics doesn't stop at one OS. Real cases cross Windows, Linux, and macOS.
XPFI recognizes exactly that: earn certifications in four 13Cubed courses and you're recognized across all three major operating systems.
✅ Included, no extra cost
✅ No separate exam
✅ Issued automatically
✅ Never expires
Certification attempts have always been included with 13Cubed courses. XPFI is no different.
training.13cubed.com/certifi…

A new 13Cubed episode is out! 🍎
Windows forensics on a Mac usually means firing up a VM first. Not anymore.
IRFlow Timeline is a free, open-source DF/IR timeline tool built natively for macOS. Feed it EVTX, Plaso, $MFT, or $J and go straight to process inspection, lateral movement, persistence, and VirusTotal enrichment.
Featuring the tool's author, @r3nzsec 👇
youtube.com/watch?v=W9xHbNgZ…

🧟 Abeebus is back from the dead. v2.1 is out.
It pulls IPv4 addresses out of any file and gets GeoIP data for each one from ipinfo.io.
🔧 The big fix: it used to read the entire file into memory. Fine for email headers, not so great for a memory image. It streams now.
Also keeps your results if you hit the ipinfo.io rate limit.
If you prefer a native Windows binary, try SharpAbeebus.
github.com/13Cubed/Abeebus
github.com/13Cubed/SharpAbee…

The first 13Cubed mini course, Architecting the Hunt, is now available! 🎉
An entry-level, hands-on introduction to threat hunting, learn a repeatable framework, then put it to work in a self-contained lab. No prior experience needed.
Watch the launch video 👉 youtube.com/watch?v=cFxwYz5T…
Enroll 👉 training.13cubed.com/archite…
#ThreatHunting #DFIR #BlueTeam
Coming this Monday, August 10!

The very first 13Cubed mini course is coming, and we couldn't be more excited! 🔥
🎯 Architecting the Hunt takes you from zero to confident threat hunter with a repeatable framework, then drops you into a hands-on lab with 100 hosts and 9M+ events to hunt through. 🕵️
✅ Entry-level
✅ Hands-on lab (yours to keep!)
✅ No experience needed
The waitlist is OPEN 👇
training.13cubed.com/archite…

13Cubed retweeted
Registration is open for the first Threat Hunting League competition
Prizes:
🥇 13Cubed’s Investigating Windows Endpoints course, worth $795 USD
🥈 Two months of complimentary Threat Hunting Labs access, plus a private 30-minute one-to-one threat hunting coaching session
🥉 One month of complimentary Threat Hunting Labs access
Investigate the Iranian APT Campaign Against Aerodyne Engineering and hunt for the evidence-based objectives.
- Competition window: September 25–27
- Personal lab run: 4 hours within that window
- Entry: $15 or 12 THL credits for active subscribers while allocation space remains
Open to all experience levels!
A big thank you to @13CubedDFIR for supporting our first Threat Hunting League competition!
threathuntinglabs.com/compet…
🤖 Made with AI

🔥👇
The very first 13Cubed mini course is coming, and we couldn't be more excited! 🔥
🎯 Architecting the Hunt takes you from zero to confident threat hunter with a repeatable framework, then drops you into a hands-on lab with 100 hosts and 9M+ events to hunt through. 🕵️
✅ Entry-level
✅ Hands-on lab (yours to keep!)
✅ No experience needed
The waitlist is OPEN 👇
training.13cubed.com/archite…
The very first 13Cubed mini course is coming, and we couldn't be more excited! 🔥
🎯 Architecting the Hunt takes you from zero to confident threat hunter with a repeatable framework, then drops you into a hands-on lab with 100 hosts and 9M+ events to hunt through. 🕵️
✅ Entry-level
✅ Hands-on lab (yours to keep!)
✅ No experience needed
The waitlist is OPEN 👇
training.13cubed.com/archite…
🔥 A new 13Cubed episode is out!
In this episode, we'll look at a tool that can run multiple Volatility 3 plugins simultaneously, automating your memory analysis and saving you valuable time during investigations.
👉 Watch now: youtube.com/watch?v=0GMTydim…
#DFIR #DigitalForensics #IncidentResponse #MemoryForensics #Volatility3 #CyberSecurity
13Cubed retweeted

📣 I partnered with @13CubedDFIR for a summer giveaway! 🎁
🏆 Five winners will receive a 13Cubed course of their choice from the list below + a Retro Forensicator T-Shirt.
13Cubed Courses:
- Investigating Windows Endpoints
- Investigating Windows Memory
- Investigating Linux Devices
- Investigating macOS Endpoints
Each course comes with a Certificate of Completion as well as Certification attempts!
On August 1st, entries across social media platforms will be combined, and the five winners will be selected.
To Enter:
✅ Like
✅ Share
✅ Comment with the course you want to win the most
For more information ⬇️
Link to 13Cubed Training: training.13cubed.com/
13Cubed Merch Store: shop.13cubed.com/
#DFIR #IncidentResponse #DigitalForensics

🎉 A new 13Cubed episode is up!
This time we're exploring the USN Journal on a live system. How can we view it while Windows is actively running, and does the reality match the common explanations? Let's find out!
youtube.com/watch?v=eSLHyqZl…
#DFIR #DigitalForensics
🍎 Happy #WWDC26 week!
🚀 We've just released a major update to Investigating macOS Endpoints, featuring an all-new hands-on macOS forensics scenario.
Put your investigative skills to the test in a realistic case environment and gain experience tackling challenges you'll encounter during real-world macOS investigations.
👉 youtube.com/watch?v=tRvw13e3…
