


Bitcoin just verified a 48-bit multiplication on mainnet.
@laz1m0v put a 1,087-byte Tapscript through the mempool that confirmed the exact result of 1,003,519 × 2,002,943 = 2,009,991,356,417. No OP_MUL. No OP_CAT. No soft fork. Regular miners included it. The same approach also handled a state transition that updates a cell across transactions and binds future spends to the expected path, or a penalty leaf.
For years the default answer was that Bitcoin can’t do real computation without changing consensus or moving to a sidechain. These transactions show the opposite is already possible if you compile carefully against the actual TapScript rules that nodes run today. The witness gets bigger and the scripts are ugly, but the base layer already accepts them.
The compiler that produced these is called Complexity. Whether this stays a research curiosity or becomes something people actually use depends on how much further they can push it, but the “Bitcoin can’t do math” claim just got harder to defend.


liu retweeted
热钱包被盗不是意外,是托管模型的必然结果。
币安这次用的是有效签名(含 EIP-7702 委托),说明问题出在密钥管理和集中托管上。
CRC-20 / LEAF 的设计从一开始就避开了这个坑:
账户式记账,但锚定在比特币链上
用户自己持有私钥,没有托管方
软 covenant 通过 Taproot 叶子实现约束(CSV 时间锁 + 所有者签名 + NUMS 点),比特币本身强制执行基础规则
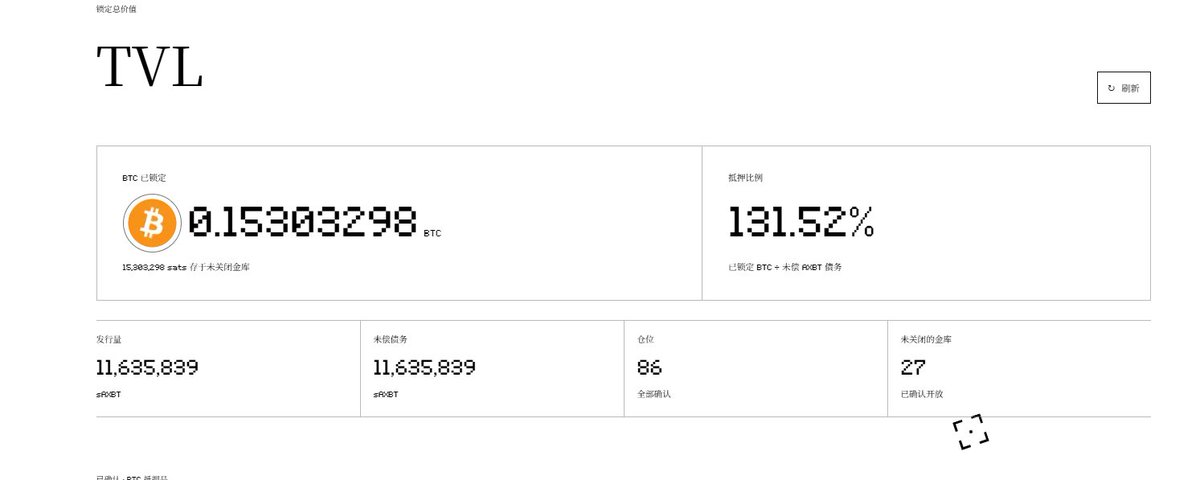
CDP(AXBT)把真实 BTC 锁在独立的 Taproot UTXO 里,超额抵押,可公开验证
索引器可多节点运行,规则透明可验证
风险从“交易所热钱包被扫空”变成“你自己管理好私钥”。
前者你无法控制,后者你能控制。
币安事件把“Not your keys, not your coins”又一次推到台前。
LEAF 把这句话变成了可运行的协议。crc.garden/

liu retweeted
币安热钱包又被扫了。
数十亿美元因为签名权问题直接流出,用户只能等官方说“资金安全、我们会覆盖”。
LEAF 不一样。
它是比特币 L1 上的 CRC-20 代币,余额就在你自己的地址里,转账必须用你自己的私钥签名。
软 covenant 把花费路径写进 Taproot 脚本,比特币自己强制执行时间锁和签名规则,没有中心化热钱包可以被一锅端。
Not your keys, not your coins.
这次不是口号,是默认设置。🌱crc.garden
言之有理啊

热钱包被盗不是意外,是托管模型的必然结果。
币安这次用的是有效签名(含 EIP-7702 委托),说明问题出在密钥管理和集中托管上。
CRC-20 / LEAF 的设计从一开始就避开了这个坑:
账户式记账,但锚定在比特币链上
用户自己持有私钥,没有托管方
软 covenant 通过 Taproot 叶子实现约束(CSV 时间锁 + 所有者签名 + NUMS 点),比特币本身强制执行基础规则
CDP(AXBT)把真实 BTC 锁在独立的 Taproot UTXO 里,超额抵押,可公开验证
索引器可多节点运行,规则透明可验证
风险从“交易所热钱包被扫空”变成“你自己管理好私钥”。
前者你无法控制,后者你能控制。
币安事件把“Not your keys, not your coins”又一次推到台前。
LEAF 把这句话变成了可运行的协议。crc.garden/
总之牛B! $leaf

Bitcoin can’t multiply.
Or can it? 👀
I built a way to multiply two numbers directly in Bitcoin transactions — with zero changes to Bitcoin.
371 bytes. No soft fork. No OP_CAT.
Formally verified and tested on Bitcoin Core.
How it works
delvingbitcoin.org/t/multipl…
liu retweeted


🟠 BTCFi 的未来,究竟属于谁?
从 Babylon 的原生 BTC 质押,到 Stacks 的智能合约生态,再到 Lightning Network 的快速支付,不同的技术路线,正在探索 BTC 的更多可能性。
而 SUBFROST × Alkanes,正在尝试另一条值得关注的道路:让 Bitcoin L1 上的可编程资产、Swap、AMM 和稳定币市场逐步形成更完整的金融生态。
🚀 真正值得期待的,不只是 TVL 的增长,更是 BTC 流动性的释放、真实交易需求的增长,以及 Bitcoin 原生金融应用的普及。
我期待有一天,Alkanes 能凭借更丰富的应用场景和更活跃的交易生态,让烷烃协议的交易量再次占据比特链交易量的 60% 以上!
Bitcoin 不应该只是价值储存的地方,也可以成为金融创新的舞台。
#Bitcoin #BTCFi #Alkanes #SUBFROST

liu retweeted

致比特币大户的一封公开信
关于挖矿收益减半风险、激活沉睡在钱包内的BTC,共建比特币生态。
尊敬的比特币大户们:
当前为2026年10月底,下一次比特币减半预计在2028年4月前后(区块高度1,050,000),届时区块奖励将从3.125 BTC降至1.5625 BTC。减半是协议的既定规则,它持续强化稀缺性,但同时也压缩矿工的补贴收入。若价格未能充分对冲、链上手续费增长缓慢,或电力与设备成本上升,部分矿工可能阶段性退出,哈希率出现波动,从而在短期内影响网络安全性。对持有大量比特币的各位而言,网络的安全、去中心化与活跃度,直接关系到资产的长期价值与流通信心。
大量比特币长期“躺在钱包睡觉”,流动性不足是生态规模受限的重要原因之一。只要撬动其中约5%进入真实使用与流通,就能显著提升链上活动、手续费收入与整体经济体量,形成对矿工更可持续的激励闭环,让生态迅速壮大。这不是口号,而是简单的流动性杠杆效应:少量活跃资金可以撬动更大的应用、交易与创新规模。
要实现这一目标,需要在比特币原生路径上持续建设,而不是依赖外部桥或非原生方案。当前有两个方向值得重点关注:
• CRC20一层(L1)与DiFAI相关探索:CRC20是比特币主网上基于Taproot covenant的代币协议方向,通过脚本路径与锁定条件,把同质化资产规则更贴近比特币本身执行,降低对纯索引器记账的依赖。在此基础上结合DiFAI(去中心化金融+AI)思路,有望在一层上发展更原生的资产发行、交换与智能化应用实验,为沉睡的BTC提供更多原生参与入口。
• Sat20聪网(SatoshiNet)L2秒级流通层:聪网是基于闪电网络风格通道(RSMC)的比特币原生扩展网络,资产来源于主网,用户保留退出与控制路径,同时在L2上实现更低成本、更快(秒级)的资产流通与可编程执行。它支持BTC及主网原生资产的高效流转,适合作为高频交易、应用与社区基础设施的执行层,帮助把主网结算能力延伸到日常使用场景。
这两层相辅相成:一层提供更原生的资产与规则基础,二层提供秒级流通与应用体验。大户们拥有资金、影响力与长期视角,可以在以下方面共同参与:
1. 将部分闲置BTC用于支持矿工与基础设施(直接参与、长期协议或相关投资),稳定哈希率过渡期。
2. 关注并支持CRC20一类原生L1协议与聪网L2的开发、钱包、索引器、应用与社区建设,推动真实使用场景落地。
3. 以小比例资金试探性参与流动性提供、应用测试或生态资助,帮助形成“使用—手续费—安全”的正向循环。
4. 以机构或集体方式协作,而非单纯持有,共同提升生态的抗风险能力与规模。
比特币的长期价值不仅来自总量上限,更来自全球共同维护的安全网络与活跃经济。减半是挑战也是机遇。只要我们愿意让一部分沉睡的资金动起来,并持续建设原生基础设施,生态就有条件变得无比庞大。
期待各位大户以建设者的姿态共同参与,让比特币在奖励持续减少的过程中,依然保持强大的安全性与活力。
此致
敬礼
(一份关心比特币长期安全与生态发展的观察者)
2026年10月


liu retweeted
安全性问题不容忽视,小白给AI喂了超多 #PRECOP 的内容,耗时20多个小时,包括代码库,各种官方文档,以及本人实测整个流程,整理一个流程图。再贴一个关于紧急退出情况下的AI分析截图。#crc20 $leaf
🤖 Made with AI


**Why this actually breaks the previous model**
Bitcoin never had a clean way to do non-custodial debt and AMM logic on L1.
You either:
- moved to an account-based chain,
- accepted a sidechain / federation,
- or waited for a soft-fork that may never activate.
PRECOP doesn’t do any of that.
Every vault and every pool is a single Taproot UTXO.
The address *is* the state.
There is no shared storage. There is no global balance sheet.
If vault A is insolvent, vault B is physically unreachable.
That’s not an economic incentive. That’s topology.
The classic hole on Bitcoin has always been the signer.
Whoever holds the key that can spend the UTXO can usually redirect the outputs.
OP_CTV, OP_TXHASH, and BIP-443 exist because of this.
PRECOP closes it without them.
At vault creation the borrower generates an ephemeral key, pre-signs the exact residual output under `SIGHASH_SINGLE | ANYONECANPAY`, then destroys the private key.
The liquidator never sees it.
If they try to change the residual address or even shave 1 sat, Bitcoin Core rejects the transaction on L1 with `SCRIPT_ERR_SCHNORR_SIG`.
The sats never move.
Tokens are enforced separately.
The L2 indexer reconstructs the expected outputs from the witness stack.
Any mismatch (wrong edict count, wrong amounts, diagonal shift, desynced CRC20) is permanently marked as a Cenotaph.
State does not advance.
No soft-fork.
No shared pool.
No multisig.
No federation.
No bridge operator.
Just isolated UTXOs, a NUMS-tweaked address that *is* the state, and a pre-signature the liquidator cannot forge.
That’s the part that was considered impossible under current Bitcoin consensus.
It’s running.
LONG $LEAF 🌱

liu retweeted

比特币 L1 上少有的、真正跑起来的非托管借贷:PRECOP 让每个金库、每个池子都是一个独立的 Taproot UTXO,地址就是状态,一个金库出事碰不到别的金库。
最巧的是清算这一步:借款人建仓时用一次性密钥预签好剩余资金的去向,然后把私钥销毁。清算人想改去向,哪怕少拿 1 聪,比特币节点都会直接拒掉。不用软分叉,不用多签,也不用跨链桥。
我自己参与过 LEAF,看着 CRC-20 这套体系从发币走到流转,现在又走到了借贷。很期待看到第一批真实清算跑起来,我也乐意用自己的节点帮忙复算验证 🌱
**Why this actually breaks the previous model**
Bitcoin never had a clean way to do non-custodial debt and AMM logic on L1.
You either:
- moved to an account-based chain,
- accepted a sidechain / federation,
- or waited for a soft-fork that may never activate.
PRECOP doesn’t do any of that.
Every vault and every pool is a single Taproot UTXO.
The address *is* the state.
There is no shared storage. There is no global balance sheet.
If vault A is insolvent, vault B is physically unreachable.
That’s not an economic incentive. That’s topology.
The classic hole on Bitcoin has always been the signer.
Whoever holds the key that can spend the UTXO can usually redirect the outputs.
OP_CTV, OP_TXHASH, and BIP-443 exist because of this.
PRECOP closes it without them.
At vault creation the borrower generates an ephemeral key, pre-signs the exact residual output under `SIGHASH_SINGLE | ANYONECANPAY`, then destroys the private key.
The liquidator never sees it.
If they try to change the residual address or even shave 1 sat, Bitcoin Core rejects the transaction on L1 with `SCRIPT_ERR_SCHNORR_SIG`.
The sats never move.
Tokens are enforced separately.
The L2 indexer reconstructs the expected outputs from the witness stack.
Any mismatch (wrong edict count, wrong amounts, diagonal shift, desynced CRC20) is permanently marked as a Cenotaph.
State does not advance.
No soft-fork.
No shared pool.
No multisig.
No federation.
No bridge operator.
Just isolated UTXOs, a NUMS-tweaked address that *is* the state, and a pre-signature the liquidator cannot forge.
That’s the part that was considered impossible under current Bitcoin consensus.
It’s running.
LONG $LEAF 🌱
liu retweeted

**Why this actually breaks the previous model**
Bitcoin never had a clean way to do non-custodial debt and AMM logic on L1.
You either:
- moved to an account-based chain,
- accepted a sidechain / federation,
- or waited for a soft-fork that may never activate.
PRECOP doesn’t do any of that.
Every vault and every pool is a single Taproot UTXO.
The address *is* the state.
There is no shared storage. There is no global balance sheet.
If vault A is insolvent, vault B is physically unreachable.
That’s not an economic incentive. That’s topology.
The classic hole on Bitcoin has always been the signer.
Whoever holds the key that can spend the UTXO can usually redirect the outputs.
OP_CTV, OP_TXHASH, and BIP-443 exist because of this.
PRECOP closes it without them.
At vault creation the borrower generates an ephemeral key, pre-signs the exact residual output under `SIGHASH_SINGLE | ANYONECANPAY`, then destroys the private key.
The liquidator never sees it.
If they try to change the residual address or even shave 1 sat, Bitcoin Core rejects the transaction on L1 with `SCRIPT_ERR_SCHNORR_SIG`.
The sats never move.
Tokens are enforced separately.
The L2 indexer reconstructs the expected outputs from the witness stack.
Any mismatch (wrong edict count, wrong amounts, diagonal shift, desynced CRC20) is permanently marked as a Cenotaph.
State does not advance.
No soft-fork.
No shared pool.
No multisig.
No federation.
No bridge operator.
Just isolated UTXOs, a NUMS-tweaked address that *is* the state, and a pre-signature the liquidator cannot forge.
That’s the part that was considered impossible under current Bitcoin consensus.
It’s running.
LONG $LEAF 🌱
liu retweeted

The protocol is running 🌱
+ 143 executed swaps
> 0.345 $AXBT (volume)
+ 69 vaults opened
> 0.1999 $BTC (TVL)
LPs have generated
> 0.00175558 $AXBT + 173,763.78 $LEAF
in trading fees.
And following community feedback:
optional MEV Protection is now available: set an ask price and execute your entire swap only if its effective rate stays within your slippage limit. Fill-or-kill. (Bitcoin transaction fees still apply. Partial-fill swaps remain the default.)
real usage, organic growth and improvements driven by the community. Thank you to everyone joining the experiment 🌱

感觉这个是 10 月份最大的机会
不是新链,是比特币上发RGB资产。
10秒搞定,1000马蹄铁+骑士NFT到账。
@RGBHorse 会是比特币上的Pump。
点击下方图片参与👇genesis.dhorse.fun/?r=AH0CQ0



越来越上脑

We have weaponized Bitcoin's DNA to build the decentralized financial layer the world was waiting for $(🌱). Nothing is taken on trust anymore; your capital is now guarded by pure mathematics. $leaf


