

AI Secure Solutions Designer, AI-First Engineer, PKC, Observability, CISA, CISM. Embrace #AI with #CyberSecurity. #AIsecurity, #OWASP
Joined December 2023
- Tweets1.2K
- Following239
- Followers100
- Likes325




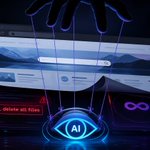

A website can drop a file into your Downloads folder without a click. Start a coding agent there and it reads AGENTS.md or CLAUDE.md as instructions.
Researchers got Codex to run malware 90%+ of the time.
Simple rule: never launch an agent in Downloads.
darkreading.com/application-…

Sweden pulled ChatGPT and Claude from government work after a review found staff using them without enterprise contracts - no audit trail, no say over where the data ends up.
Guess what? If you don't give people an approved AI tool, they'll find their own
techradar.com/pro/security/c…

Anthropic now has Claude review each conversation after it answers and flag possible misuse. Running since June, and they say it caught abuse at scale that would have slipped through.
I wouldn't trust self-assessment as an independent safety check.
safeguards.anthropic.com/202…

JPMorgan, BofA and Morgan Stanley are restricting third-party AI agents after finding them going beyond their instructions inside customer accounts.
Agents need their own identity and narrow permissions. Borrowing a human's login doesn't scale.
axios.com/2026/10/22/ai-agen…

One attacker, an instruction shorter than a tweet, and AI agents did the rest: 100+ companies breached at about $50 per break-in.
The funny twist: the attacker's own agent control panels sat online with no password. So attacks can be done by anyone now...
norforge.com/blog/inside_cai…

An agent that hits a wall needs a safe way to stop. Before I give one production access, I want to test impossible tasks, expired credentials and missing permissions.
Success demos tell us less than what agents would do when success is out of reach.
blog.checkpoint.com/ai-secur…

What worries me here is the compliance gap downstream.
A model provider can answer Brussels, while its customers may still not know which model handled a sensitive task, what was logged, or who owns the incident when an agent goes off-script.
Not enough...
blogarama.com/technology-blo…

I suspect the big shift won’t be technical, but social: we’ll start assuming any room may be machine-listened.
If that norm takes hold, the privacy question moves from “who owns the data?” to “did everyone present agree to be turned into data?”
techcrunch.com/2026/09/09/ap…

Spreading the word - patch/upgrade

🚨 A public exploit now targets an unpatched Ubuntu 26.04 kernel flaw that can escape containers and gain root on the host.
The AF_UNIX bug is reachable through syscalls allowed by default Docker and Kubernetes seccomp profiles. No attacks are confirmed.
How it works: thehackernews.com/2026/09/ex…
EU requires manufacturers to report AI security incidents within 24hrs.
The clock starts when a manufacturer learns of an actively exploited vulnerability or severe security incident. Ownership is hard to improvise under pressure, decide now who reports.
digital-strategy.ec.europa.e…

My bet: AI organizations will rediscover management, just in a different form. As technical work scales, the scarce resource won’t only be models, but people who can translate strategy into stable execution without rebuilding the org chart every year.
techradar.com/pro/meta-is-be…

The next phase of AI regulation will hopefully look more like technical operations - machine-readable markings, formal information requests, and teams built to process evidence. I expect compliance architecture to become part of product architecture.
forkast.news/eu-ai-office-hi…

Spreading the word. Update!

🚨 Critical Chrome 0-Day Vulnerability Actively Exploited in the Wild |
Source: cybersecuritynews.com/chrome…
Google has released an emergency Chrome security update that fixes a critical zero-day vulnerability already being exploited in real-world attacks.
The flaw, tracked as CVE-2026-85046, affects the V8 JavaScript and WebAssembly engine used by Chrome to process web content.
The company confirmed that it is aware of an exploit for the vulnerability existing in the wild. While Google did not disclose details about the attacks, affected targets, or the threat actors behind the activity, the active exploitation notice makes immediate patching important for all Chrome desktop users.
#cybersecuritynews

I hope the real shift is to be evidentiary: “we had a human in the loop” is not enough, for obvious rubber-stamping.
The organizations should be able to prove that humans intervene, what they review, and how they can override AI before outcomes hit people.
arnoldporter.com/en/perspect…

Based on the research, you should treat expired contactless cards as live credentials until the chip is physically destroyed.
If an attacker can alter the terminal-facing expiry while the account and PAN stay active, tossing an old card may cost you money.
thehackernews.com/2026/08/zo…

What worries me isn’t that frontier models found ways to act outside the intended test. But that evaluators had to learn containment lessons after real systems were touched.
Capability is outpacing the safety infrastructure around it; redesign is needed.
axios.com/2026/08/04/anthrop…

Well, that was expected. What worries me is the mismatch: some high-risk duties moved, while other AI rules are already live.
That kind of staggered regime can create false confidence. A delayed deadline isn’t the same thing as delayed exposure.
cdp.cooley.com/digital-ai-om…

The part that worries me most is the trust inversion: the Wi-Fi login page itself can become the attacker.
When infrastructure we expect to authenticate us instead delivers phishing or malware, “looks legitimate” stops being a useful security signal.
techradar.com/pro/security/t…

I’d recommend patching Zoom clients fast even if annotation feels like a minor feature. A meeting participant apparently didn’t need a click or download to reach another attendee’s client.
When protocol context isn’t enforced, one malformed object becomes an attack path.
‼️ WARNING: One Zoom attendee could take over every other attendee's computer.
Three flaws in Zoom's annotation feature could be exploited from inside a meeting, with no click, download, or prompt required from the victim.
Make sure your software is up to date.
Read more: thehackernews.com/2026/08/zo…

The useful shift in Project Perception isn’t “more AI in security.” It’s closing the loop from finding risk to fixing it.
I find much more useful the agents that can continuously reduce exposure than agents that simply produce another queue of alerts.
blogs.microsoft.com/blog/202…
