

Head of Research @icmdotrun Crypto Class of 2021 | On-Chain Sleuth | $ICM $SOL $BNB https://nitter.cf/t.co/vxYY8MIptQ
International
Joined August 2021
- Tweets11.3K
- Following1.7K
- Followers3.5K
- Likes17K




Pinned Tweet
For people who do not understand how bad the situation is, their most liquid pool is on ETH which has $2.8M. When this gets liquidated, selling this stake on that pool today gets you $2.8M (basically the whole pool).
@Dolomite_io has no way to liquidate this and come out as whole from this situation. The stablecoins that were borrowed belonged to people who people who deposited on Dolomite for earning yield. When they go to withdraw it, they will not be able to do so.
@CoreyCaplan3 is the founder of @Dolomite_io and the CTO of @worldlibertyfi. He has not commented so far but he seems to be in the right position to suggest this Dolomite rug. It is at the expense of depositors on Dolomite.


🚨 $WLFI Team has now borrowed $150M worth of USDC against 5% of $WLFI supply. $WLFI has less than $10M in core assets all their DeFi pools on all chains combined.
@Dolomite_io is rugging. Their founder is the CTO of @worldlibertyfi so you know he's aware of this. Despite several alarms raise, he hasn't said anything on this topic.
Binance hack continued:
- XRP was actually hit first, at 20:05 UTC: 233M XRP left Binance accounts
- 970K SOL followed at 20:10
- the attacker raced the freezes, swapping 435M USDT to ETH and borrowing 19,762 ETH on Aave against 60M USDT, 12 seconds before Tether’s blacklist
- Binance 14 was swept five times in total; the hijack was only revoked at 00:10 UTC, 3h50m after the takeover
- Arbitrum’s Security Council froze $30.5M
- Binance says it will cover all losses; deposits and withdrawals are suspended
~$6.2B taken across 9 chains. $2.54B frozen, per Binance.

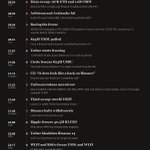
The Binance hack so far:
- attacker deploys a sweeper contract, gas paid through Tornado Cash
- attacker’s address starts receiving funds on Base, then Optimism
- 18,270 BTC leaves a Binance hot wallet
- 612.7M USDT and 46M TRX are taken on Tron
- Binance 14 gets pointed at the sweeper via EIP-7702
- one call sweeps 167K ETH and 1.6B USDT from it, $2.54B
- Binance 16, Arbitrum and Avalanche wallets send more
- 823M USDC is pulled from a Binance smart account
- Tether starts freezing, 1.57B USDT in total
- Binance 14 gets swept a second time
- Circle freezes 823M USDC
- CZ: “It does look like a hack on Binance”
- attacker moves unfrozen tokens and starts selling UNI, PEPE and RLUSD
- third sweep takes 200M USDT, which lands frozen
- Binance halts withdrawals until the security issue is resolved
- Ripple freezes 40.5M RLUSD
- Tether blacklists Binance 14 itself
- WLFI and BitGo freeze 27.8M USD1 and 48.5M WLFI
~$5.8B taken. ~$2.7B frozen. ~397K $ETH and 18,270 $BTC still with the attacker.
Binance 14 is still pointed at the attacker’s sweeper.

The Binance hack update:
- Binance's first finding: a compromised DevOps engineer's laptop let the attacker into a service container that could submit withdrawals, with no sign of a private key leak
- its 08:47 UTC update says the investigation has since found additional points of breach
- TRM Labs attributes the hack to North Korea's TraderTraitor unit, with high confidence. Chainalysis also says North Korea
- Chainalysis says the stolen funds are mixing with money from last month's $387M Bitget hack
- a Tron wallet fed with stolen TRX is swapping through THORChain into the same Ethereum address as that Bitget money
- more stolen TRX went through Bitget Wallet's bridge to an address linked to the 2025 Phemex hacker
- Binance says outflows stopped when it paused withdrawals. On-chain, about $55M more was swept from Binance 14 after it said at 22:15 that withdrawals were paused, until the 00:10 revoke
- the attacker tried to bridge gas money to Optimism, where 44.2M stolen OP sits. The transfer has been stuck at LayerZero verification for over 3 hours
- 17,260 ETH moved to a new wallet, the 18,270 BTC and 233M XRP haven't moved
- withdrawals are due back in about 45 hours. Deposits are working
~$6.3B taken, ~$3B frozen.

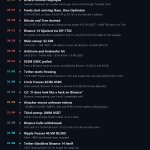
The Binance hack so far:
- attacker deploys a sweeper contract, gas paid through Tornado Cash
- attacker’s address starts receiving funds on Base, then Optimism
- 18,270 BTC leaves a Binance hot wallet
- 612.7M USDT and 46M TRX are taken on Tron
- Binance 14 gets pointed at the sweeper via EIP-7702
- one call sweeps 167K ETH and 1.6B USDT from it, $2.54B
- Binance 16, Arbitrum and Avalanche wallets send more
- 823M USDC is pulled from a Binance smart account
- Tether starts freezing, 1.57B USDT in total
- Binance 14 gets swept a second time
- Circle freezes 823M USDC
- CZ: “It does look like a hack on Binance”
- attacker moves unfrozen tokens and starts selling UNI, PEPE and RLUSD
- third sweep takes 200M USDT, which lands frozen
- Binance halts withdrawals until the security issue is resolved
- Ripple freezes 40.5M RLUSD
- Tether blacklists Binance 14 itself
- WLFI and BitGo freeze 27.8M USD1 and 48.5M WLFI
~$5.8B taken. ~$2.7B frozen. ~397K $ETH and 18,270 $BTC still with the attacker.
Binance 14 is still pointed at the attacker’s sweeper.

Update: it’s far bigger. About $5.6B was taken across 7 chains, starting 20:16 UTC.
Ethereum: $3.4B, incl. 823M $USDC from a Binance smart account
Bitcoin: 18,270 $BTC ($1.45B)
Tron: $628M
Arbitrum, Avalanche, Optimism, Base: $62M
Frozen: ~$2.4B (Tether 1.567B $USDT, Circle 823M $USDC).
Out of reach: ~386K $ETH, still sitting on-chain, and the $BTC, already split into 1,000 BTC chunks.
Live tracker of the attacker’s 51 addresses (Arkham):
arkm.com/explorer/entity/21a…


Stablecoin issuers are acting.
@circle froze 823M $USDC
@tether froze 971M $USDT
Reaction time matters. It's great to see Crypto coming together to help out 🫶
🚨 Binance seems to be hacked. At least $2.6B went to one fresh wallet.
20:20 UTC: the wallet was pointed at a sweeper contract via EIP-7702. That change has to be signed with the wallet’s own key.
20:24 UTC: one call swept 167K ETH and 63 tokens, including 1.6B USDT ($2.54B).
20:24 UTC: a second @binance wallet sent 28K ETH and 8 tokens to the same address.
It looks like theft, not a migration: the gas came from Tornado Cash. Binance hasn’t commented.
Will update further.
And an update from @cz_binance
nitter.cf/cz_binance/status/2115…

🚨 Binance seems to be hacked. At least $2.6B went to one fresh wallet.
20:20 UTC: the wallet was pointed at a sweeper contract via EIP-7702. That change has to be signed with the wallet’s own key.
20:24 UTC: one call swept 167K ETH and 63 tokens, including 1.6B USDT ($2.54B).
20:24 UTC: a second @binance wallet sent 28K ETH and 8 tokens to the same address.
It looks like theft, not a migration: the gas came from Tornado Cash. Binance hasn’t commented.
Will update further.
Binance 14: 0x28C6c06298d514Db089934071355E5743bf21d60
Receiving wallet: 0x5227f603C1eE34CE3C06eFe6477003BDfCCB2f8c
Sweep tx: 0x53bd38b816c23e74134786c29a8c18d792777998a3b9326047b583100e88e2f3
Already moving: 700M USDT out in two transfers, and 195,460 ETH to 0x8532FA14ACAf483729C449b8458aedDb900543D4.
At 20:41 another 780M USDC landed in the receiving wallet from an unlabeled contract. Source not identified yet.
As of 20:44 UTC Binance 14 still points to the sweeper contract, so new funds landing there can be swept too until Binance resets it.
This is real.
One wallet took about $2.6M from at least 33 @Polymarket accounts in 35 minutes (17:26–18:02 UTC).
Positions were moved straight to the attacker and balances were swapped into POL. The wallet now holds 28.6M POL.
Early analysis points to a malicious script on the site hijacking logged-in sessions. Not confirmed yet, and Polymarket hasn’t commented.
Don’t open the site until the team says it’s safe.
Attacker wallet below.
This quoted post is unavailable.
Attacker wallet (Polygon):
0x3F99139F1C5854bb628c2e576Aaf638e99dFfc18
Positions came in from 33 wallets, 17:26–18:02 UTC. Balance: 28.6M POL (~$2.6M).
Wallet and script analysis first posted by @0xRacerAlt: nitter.cf/0xRacerAlt/status/2115…
polygonscan.com/address/0x3F…
This quoted post is unavailable.
Dear Mr. Hacker,
It is with the deepest admiration that we write regarding your recent undertaking on-chain.
With a single valid signature, you relieved the EP vault of 612,506 EP and converted the whole of it into approximately 1,050 USDT. We observed, moreover, that you paid the full 10% sell tax without complaint, a portion of which was burned in the project’s honour. Such civic-mindedness is rarely seen in your line of work.
We must also apologise for the tone of certain correspondence sent to you on-chain. One party addressed you plainly and demanded the return of the funds. We were mortified. As a more refined correspondent has since reminded us, one should begin with “Mr. Hacker, can I have my money back?”
It is in that spirit that we most humbly ask whether you might see your way to returning some portion of the sum. We appreciate that it may already have departed for Monero, from which, we are told, few return.
Should you decline, please know that you remain in our most respectful thoughts.
We have the honour to be, Mr. Hacker, your most obedient and humble servants,
On-chain Participants
P.S. The gentleman who recommended the respectful tone has asked us to state, for the record, that he is not you.


🚨 @predictdotfun users got drained again today. It’s the second time in 5 days, and at least $390K is gone.
What happened:
• Today, 21 accounts lost their USDT. At least $265K. Most of it happened in 34 minutes, starting at 05:31 UTC.
• On Oct 22, the same setup hit 4 accounts for almost $125K.
• The money was moved to Ethereum and 115 ETH went into Tornado Cash, a mixer that hides where funds go.
I checked this on-chain. Every drained wallet is an account on the platform, and the attacker didn’t touch wallets from any other app, from my scan.
This wasn’t a hack of the platform’s smart contracts. It also wasn’t the usual “you signed a bad approval” scam.
Each withdrawal was signed with the victim’s own wallet key. It just wasn’t done through the app. Transactions from the app and from the attacker look completely different on-chain. Same keys, different door.
So someone was able to sign for these accounts. It could be leaked keys, a problem with how the keys are stored, or a hijacked login.
If you keep a large USDT balance sitting idle there, consider moving out what you’re not actively using until the team explains. So far only USDT balances have been taken, and open positions weren’t touched.
CC @dingalingts


Update: @predictdotfun has confirmed the incident. They put the losses at about 400,000 USDT, which is in line with what I found on-chain across both waves (at least $390K).
They say all affected users will be fully reimbursed.
Their early finding is that their API documentation site, which a third party hosts, may have been compromised. The site is offline until the investigation is done, and they’ve promised a full post-mortem.
On-chain, every theft was signed with the account’s own key. So the open question is how those keys were exposed.
nitter.cf/predictdotfun/status/2…

We are aware of a small number of users who have experienced unauthorized transfers of funds from their wallets, totaling approximately 400,000 USDT.
Our preliminary investigation suggests that our API documentation site, which is hosted by a third-party provider, may have been compromised, potentially affecting a small number of users over a short period of time. The API documentation site has been taken offline as a precaution and will remain offline until our investigation is complete.
At Predict.fun, we take the security of our users and their funds extremely seriously. As such, we will fully reimburse all affected users for any funds lost as a direct result of this incident.
Once our investigation is complete, we will publish a full post-mortem detailing what happened and the steps we're taking to prevent similar incidents in the future.

The details, for anyone who wants to check.
Where the money went today -
Each drained account sent its USDT to a brand-new wallet, and each of those wallets bridged it to Ethereum within seconds:
0x0299b21d5a285e3ee5505c12299b4e33d3bab102: 60,500 USDT (1 account)
0xcd34891c7fc9299f86da30e4797232ae6f4f685c: 53,700 USDT (1 account)
0xbe754caab768f114b1d610982dfe981e13fc83b8: 50,510 USDT (4 accounts)
0x002c755b902dfc0fff94bb5ba05789d8ead8a2e4: 41,000 USDT (1 account)
0x8b001d7378dbc19c1c62e39c0fc9ffad84182fba: 24,655 USDT (7 accounts)
0x435f8c80de1190a96adf625532faab76b24fb2d4: 23,815 USDT (3 accounts)
0x31383cec40efc929f293c4cf54e29219b70076e9: 7,415 USDT (2 accounts)
A 100 USDT drain at 5:10 UTC. One account was hit a second time at 06:18 UTC, for 3,538 USDT. A smaller ones followed (111 USDT). The last of those was at 08:49 UTC, after people had already started posting about it.
Into Tornado Cash -
On Ethereum, these 7 wallets put 115 ETH into Tornado Cash between 05:41 and 07:26 UTC. The first deposit landed 10 minutes after the first drain, while the drain was still going on:
0xd500a43442253a4b92a025f6604df2dd57d78e6f: 30 ETH
0x85cd3ee47307bcaf9e1ada4230cc7646e603d429: 22 ETH
0x5b51e000f08eeaf34484ea6b7e16f536773fe4ee: 20 ETH
0x93b94f8db5655064f35b2cbc5b8e37e34443747c: 20 ETH
0x3c9f6411cd1fbefaf33397145514ed2bf662eef9: 10 ETH
0x294dc89990f70ddb3067b0a8c917413a3e8d7c13: 10 ETH
0x44870558ef468eaf3caef7c802945a6697ec30a5: 3 ETH
The first wave, Oct 22 -
0xd14ca6d1173a710706149a222b7e20324003a660 lost 82,000 USDT to 0xeda13cffb9b1bb71b948c2b0132f04cf466de710, plus 27,000 USDT bridged to 0x177e67f11a0390edc735d220f4d553e1182ab5f3 on Ethereum.
0xa5162f5bb972a508dee6bb1092ceb22ebd1e4d40 lost 13,920 USDT to 0x420c85800903dc93424dde4ace10d0e229534a5b.
0x773b2b07f2c7fcb23ad72394e18bcb9eec618e4a lost 1,410 USDT and 0x8ae78a3d93cc30fc85dc2720f9ae5ee875c5c0d0 lost 535 USDT, both to 0xe5f3bcf5ae7818da8e0122352e1558b79c7fbff9.
How it worked -
For every drained account, the theft was the first transaction of this kind it had ever made. It took two steps. First, allow a gas service to charge the account in USDT and then send the whole balance out. Both steps were signed with the account’s own key, but in a format the app doesn’t use.
Of 9,568 normal predict.fun transactions over two days, only 3 used a gas service like this. All 80 accounts I checked sign in the app’s standard format. All 70 of the attacker’s transactions used the gas service and the other format.
Relayer: 0x3cfdc212769c890907bce93d3d8c2c53de6a7a89
Gas service (owned by that relayer): 0x8b1f6cb5d062aa2ce8d581942bbb960420d875ba
Example, @dethective’s account: bscscan.com/tx/0x5e5b9e4d888…
How I know these are predict.fun accounts
All 30 wallets the attacker touched run the wallet contract from predict.fun’s own code (0xbac849bb641841b44e965fb01a4bf5f074f84b4d). They use the same signer module (0x845adb2c711129d4f3966735ed98a9f09fc4ce57), and they have permissions set on predict.fun’s trading contracts, such as 0x8a289d458f5a134ba40015085a8f50ffb681b41d. Normal predict.fun users look exactly the same.