
Founder @HiveSecLtd, AI / . / Offensive Security
Wales, United Kingdom
Joined February 2012
- Tweets1.3K
- Following2.2K
- Followers2.2K
- Likes14.9K





Anthony. retweeted

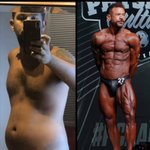
We have had a lot of comments (understandably) about Anthony and the level he’s at and I feel like this is missing a lot of context.
This, was his starting point. I cannot express the level of work, dedication and sacrifice has gone into this and I can honestly say, I don’t believe even Anthony knew this transformation was possible at the time.


Anthony. retweeted
7am at the lair.
I know it’s a hard sell.
Vegas can eat you alive.
The heat, the parties, the peer pressure and even just the time away from life to hang out with your hacker friends.
All of those things can remain true and you can still show up for what’s important to you.
This lot did, all week - and I respect it.
It was early, we didn’t always want to.
But. We do it anyway.
#wehackhealth


Anthony. retweeted
Twelve years ago I walked in to a gym in Belfast, Peak Physique on the Lisburn Road. I had one goal - change my body.
All I wanted was to fit into my clothes properly. Purely aesthetics.
I thought that change could give me the confidence I had been missing for my entire adult life.
At the time I had no direction…in anything.
I was coasting. Week to week. Party to party. Drink to drink. Taking shortcuts, making excuses, doing just enough to get by.
I wasn’t unhappy enough to change but I wasn’t happy enough to stay there either.
The gym looked like a way to lose weight and build some muscle. Looking back, it was the first promise I ever made to myself and actually kept.
I signed up for an 8-week transformation.
652 weeks later I'm writing this from Las Vegas, at @BlackHatEvents and @defcon
This and every opportunity over the past 12 years can be traced back to one decision, not because of the gym itself - but because of the person it helped me become.
It taught me to do the things I said I was going to do - not because I felt like it or was motivated to - but because I said I was going to.
It showed me that no matter where I was at in life, it was my fault - a product of my decisions and no one else is to blame. That can be hard to sit with - but the freedom of it lies in the decisions you can then make and the life that you can build.
It taught me about consistency, failure, accountability, delayed gratification and everything in between.
But most importantly - it taught me that I did not need to change my body a much as I needed to change my environment and my identity.
The gym was never the thing I fell in love with. Neither was fitness. It was change. Watching someone become a different person on purpose.
After two years I looked at how far I'd come and wanted other people to have it. So I quit my job, got qualified, and started again on the gym floor working with clients 1-1.
6 years ago I started coaching @hackingdave and he introduced me to a world that I didn’t even know existed - cybersecurity.
Over time I started working with more people in the industry and the more time I spent with them, the more I saw the same problems I had, just dressed differently. Same failure loops and the same frustrations, just in a seemingly alternate universe.
None of this was planned, but now I spend my days helping then people that are protecting the digital world build more resilient versions of themselves, systems that survive chaos and showing them the importance of prioritising their health.
Which is why I am here this week.
Not to tell you to join the gym, but to further understand the industry. The pressure, the stress, the hours and the things that people have quietly sacrificed over time to stay in it.
The mission at @wehackhealth is to set a new standard for health, performance and quality of life for people in cybersecurity.
You can't fix a system you don't understand. So this week I'm not talking. I'm listening.
The goal is simple: talk to as many people as possible.
Find out what this industry is really like.
Where people are struggling.
And where people have already made the change - how they did it without their career falling apart.
So if you're in Vegas, burnt out and don't know where to start, or you've built something that survives the chaos. I want to hear it.
Twelve years ago I made one decision that helped me change my entire life.
This week, maybe I can show you how you can do the same.
B

Anthony. retweeted
This year @defcon we are bringing @wehackhealth on the road with @DC_BHV - 𝘁𝗵𝗲 𝗰𝗼𝗹𝗹𝗮𝗯 𝘆𝗼𝘂 𝗱𝗶𝗱𝗻'𝘁 𝗸𝗻𝗼𝘄 𝘆𝗼𝘂 𝗻𝗲𝗲𝗱𝗲𝗱.
The goal is to tell stories from real hackers who levelled up their health...
My question is - who's story do you want to hear?


Anthony. retweeted

Announcing a new Claude Code feature: Remote Control. It's rolling out now to Max users in research preview. Try it with /remote-control
Start local sessions from the terminal, then continue them from your phone. Take a walk, see the sun, walk your dog without losing your flow.
Anthony. retweeted
New goals don't deliver new results. New lifestyles do. And a lifestyle is a process, not an outcome. For this reason, all of your energy should go into building better habits, not chasing better results.
Anthony. retweeted

LLM apps are getting probed nonstop - prompt injection, tool/RAG exfil attempts, instruction smuggling.
I built Raxe CE to keep defences local, explainable, and low-latency so you can see what hit and why.
github.com/raxe-ai/raxe-ce

Anthony. retweeted

We are live!
15 canary token providers (10 persistent, 5 ephemeral) - all designed to exploit an adversary's decision making process.
(And has the added fun consequence of making folk say "wait, that's a canary token??" in a demo)

Once in a blue moon as a red teamer, we encountered environments with canary technology deployed across their infrastructure. The tables flipped. Blue teams caught us immediately.
Canary technology uniquely detects adversaries by exploiting their behavior - digital assets with no legitimate use that trigger immediate, high-fidelity alerts when interacted with.
However, most organizations struggle to extract these benefits. Existing canary solutions don't provide the primitives, token catalog, automation, and tooling needed for deployment and management at scale. They require dedicated security engineers to own and maintain.
As a result, high-fidelity detection has remained reserved for the most mature security teams.
For organizations already utilizing canary technology - did it catch your last red team engagement?
Today we're launching DeceptIQ - the cloud-native canary technology platform built from first principles.
We looked at enterprises who successfully deployed canary technology - what they did, what worked, what they wanted. Coupled with our experience as adversaries, we rebuilt the tried and tested concept from first principles. We spent eight months researching how to fingerprint our own tokens, then doing it again and again.
The result: the most comprehensive, configurable, scalable canary token platform available. over 15 new canary token providers designed to exploit adversary behavior - including 5 ephemeral that each scale to over a million an hour, and 10 new persistent canary tokens.
API-first deployment integrates with custom canary channels to enable visibility and deployment of canary tokens across Kubernetes, CI/CD pipelines, MDM platforms, and many more - at scale!
Our success metric: would we catch ourselves on a red team engagement? With today's launch, we believe we can.
We built DeceptIQ to be what we wish every organization we compromised had in place.

Anthony. retweeted

Got my hands on a stream rip of my DEFCON talk. If you want to see a live demo of #chromealone - check out the talk - youtube.com/watch?v=_qS01oRT…. It covers how to turn Chrome into a Cobalt Strike style C2 along with tips for obfuscation. #malware #redteam #webassembly #chromium

Anthony. retweeted
Thanks to everyone who came out to see my talk! All of my code and the slides for my ChromeAlone presentation are available now at github.com/praetorian-inc/ch…. If you're interested in developing malicious browser extensions give the code a look! #defcon #chromealone #malware

Anthony. retweeted

I'm thrilled to announce that my talk Ghost Calls: Abusing Web Conferencing for Covert Command & Control was accepted to #BHUSA 2025 (CC: @BlackHatEvents)
blackhat.com/us-25/briefings…
Anthony. retweeted

We are so back... to #BlackHat.
Early bird reg is now available for our 2-day training on CI/CD vulns and exploitation.
Don't miss your chance to experience this session featuring guided labs & exercises.
Register before 5/23 and save 15% 🤑 blackhat.com/us-25/training/…
#BHUSA

Anthony. retweeted

Episode 1, featuring Digital Jesus/o.0, is now live 🧙
Now available on YouTube and Spotify: buff.ly/3PXv9n1
Anthony. retweeted
Wrote a short blog post on:
- ETW Threat Intelligence generated by SetThreadContext (hardware breakpoints)
- Kernel debugging and reversing
- Setting HWBPs in a more "stealthy" manner (not the same ETW TI events generated - no detections)
Check it out praetorian.com/blog/etw-thre…
Anthony. retweeted
If you've been wondering what I've been recently up to @praetorianlabs , check out the **FREE** ASM offering I've had to pleasure of build out capabilities for!
praetorian.com/chariot-free-…

Every organization should have foundational cybersecurity capabilities available for free.
Read our press release: praetorian.com/newsroom/free…
Do you have vulnerabilities in your digital environment?
Find out now! Sign up for your FREE ASM account today! praetorian.com/chariot-free-…

Anthony. retweeted

In #BHUSA Briefing "Self-Hosted GitHub CI/CD Runners: Continuous Integration, Continuous Destruction" you'll learn how attackers can exploit your organization's CI/CD pipelines and how you can defend against these attacks. Register now >> bit.ly/3WwSAaZ
