

BCON COLLECTIVE is Bridewell’s cyber threat intelligence team, helping organisations build threat-informed defences through timely, and actionable intelligence.
United Kingdom
Joined March 2023
- Tweets73
- Following42
- Followers793
- Likes16





This blog shares findings from an investigation into Teams-based support impersonation and suspected Edgecution deployment➡️ go.bridewell.com/4eMsOZf
#BCONCollective #CTI

Joshua Penny's article, 'Blatant and Beyond: Mapping Anonymous VPS Services and Their Hosting Infrastructure', analyses infrastructure associated with Blatant Technologies, LLC (AS403005).
Read the full article here 👉 go.bridewell.com/4zvnpNE
#BCONCollective #CTI

2
76
🚨Here are the top malicious infrastructure threats observed during October 2026, based on intelligence collected by BCON.
Last month, CyberStrikeAI was the most frequently observed threat, and Amneisa stealer saw increased activity from September. ➡️go.bridewell.com/4BBcWTb

83


Take a look at our latest live analysis of credential theft malware targeting UK Critical National Infrastructure, pulled directly from the Ransomware. Live PRO API and enriched with infostealer intelligence by BCON Collective.
Read more ➡️ go.bridewell.com/4yttnhf
#CTI #Malware

1
121
🚨BCON Collective tracked 65 ARTEX IPs across 13 locations, led by the US, China and Hong Kong. Some hosts also exposed Cobalt Strike, Gophish or Adaptix signatures. These are investigation leads; compromise is not established.
Read more: go.bridewell.com/4jNlcc3

110
🚨Here are the top malicious infrastructure threats observed during August 2026, based on intelligence collected by our CTI team.
Last month, CyberStrikeAI was the most frequently observed threat, while Cobalt Strike, AdaptixC2 saw increased activity. ➡️go.bridewell.com/3TkHneQ

119
We are tracking an intrusion cluster using email subscription bombing as a precursor to social engineering. One victim received 1,000+ emails in 40 minutes, followed by an external Microsoft Teams chat impersonating IT support.


DPRK IT workers exploit a problem many organisations already have: security signals scattered across Recruitment, HR, IT, IAM, SOC, Procurement and Finance.
Our guide shows you how to join them into one defence ➡️go.bridewell.com/4bUvl1V
#BCONCollective #CTI #DPRKITWorker

Over the coming days we’ll be publishing Defending against DPRK IT Workers: An Implementation and Operational Guide.
The operation crosses Recruitment, HR, IT, IAM, SOC, Procurement and Finance. No single team sees the whole picture.
Watch this space.
#DPRK #InsiderThreat
1
171
View our new live analysis of credential theft malware targeting UK Critical National Infrastructure, pulled directly from the Ransomware. Live PRO API and enriched with infostealer intelligence by BCON Collective. ➡️ go.bridewell.com/4wp4mmo
#BCONCollective #CTI #Ransomware

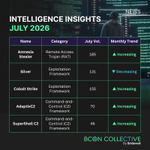
🚨Here are the top malicious infrastructure threats observed during July 2026, based on intelligence collected by our CTI team.
Last month, Amnesia Stealer remained the most frequently observed threat, while Cobalt Strike, AdaptixC2, and SuperShell C2 all saw increased activity.

2
3
220
Read more ➡️ Intelligence Insights: July 2026 bridewell.com/insights/news/…

26
These trends provide valuable insight into the tools and infrastructure threat actors continue to leverage across the cyber threat landscape.
Explore our latest Intelligence Insights to discover the threats security teams should be monitoring. ⬇️
39
Tycoon 2FA quickly returned after a temporary disruption, highlighting how resilient phishing-as-a-service operations have become. Discover what this means for defenders.
Read more ➡️go.bridewell.com/44O4CQJ
#BCONCollective #CTI #Tycoon2FA

2
166
Threat actors continue to exploit trusted brands. We analysed a phishing campaign targeting the hospitality sector and explain what security teams can learn from the attackers' tactics.
Read more ➡️go.bridewell.com/4wYDryu
#BCONCollective #CTI #Phishing
