

Asesor en autocustodia de Bitcoin | Co-fundador de @TusLlavesTusBTC | Tallerista para @BitcoinAr
Buenos Aires, Argentina.
Joined November 2024
- Tweets382
- Following524
- Followers142
- Likes499


₿enjamin retweeted

Singapur se agrega a la lista de países con dispositivos Ledger con implantes con pérdidas de aprox. $2.7 millones de dólares, hasta ahora.

Singapore Police Say Ledger crypto Wallets Sold at Local Retailers Contained Malicious Hardware Implants
Singapore police said on October 28 that some Ledger cryptocurrency hardware wallets purchased from local retailers contained malicious hardware implants capable of stealing users' recovery phrases or private keys. At least two cases have been reported since September 10, resulting in losses of approximately S$3.5 million ($2.7 million). Ledger, a leading French hardware wallet manufacturer, is reviewing the affected cases, while police investigations remain ongoing.


₿enjamin retweeted

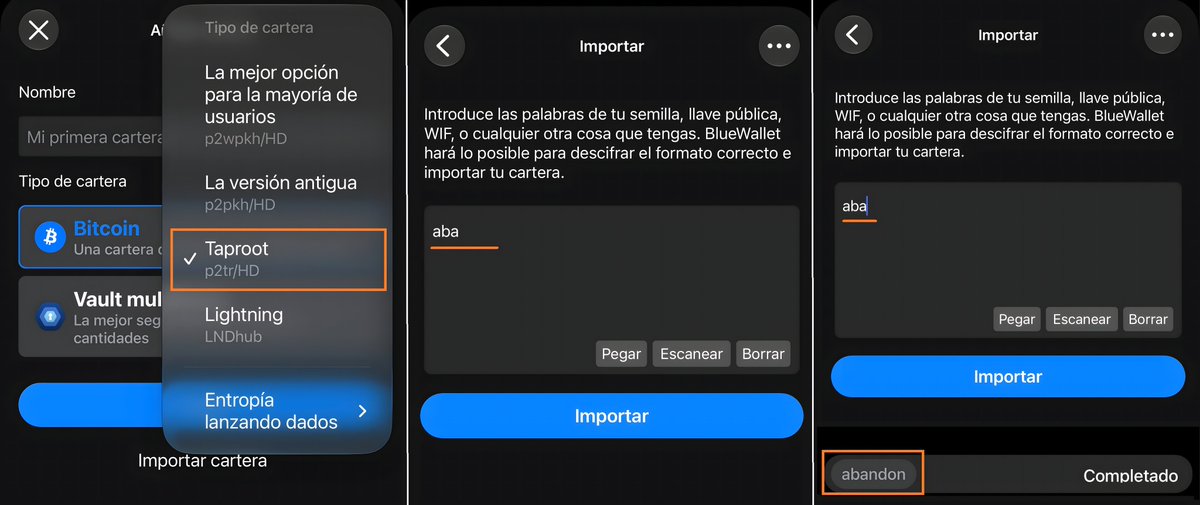
Vi este error en @bluewalletio
No me quedé con la duda: lo reporté en GitHub para que lo puedan revisar.
Probar, documentar + reportar también es una forma de colaborar con la comunidad.
Te cuento qué pasa en el hilo.
₿enjamin retweeted
AI creates abundance. Bitcoin enforces scarcity. One expands humanity’s ability to create value. The other lets us preserve and transfer it across time and space. Digital Intelligence and Digital Capital are complementary, Jason. The world needs both.
Para esto creamos @tusllavestusbtc

asked my grokbot how it would work. its answer:
"a 90 min video call with a bitcoin self-custody guide, you and your heir.
your heir sets up a fresh test wallet with a few sats, same setup as yours (coldcard, trezor, ledger or sparrow multisig)
they recover it from scratch, step by step, on their own device
your real seed never comes out. nobody touches your device or sees your keys
you walk away with a printed recovery guide written for your exact setup, which works even if we disappear
your family learns it before they need it, not after."
Nos vemos en @labitconf 🧡

El equipo de Tus Llaves, Tus Bitcoin estará en LABITCONF 2026 en Buenos Aires.
No te pierdas las ponencias de Benjamin Rosatto (@Benja_BTC), cofundador y tallerista de autocustodia de #Bitcoin
Si vas a la conferencia, no dudes en acercarte.
labitconf.com/speakers/sp585

₿enjamin retweeted
Good news: the Bitcoin Wrench Attack archive just got a lot more accurate.
Bad news: we just doubled the total number of known attacks to over 700.
Kudos to @pizza_bitcoiner for finding hundreds of new attack reports via agentic searches.
jlopp.github.io/physical-bit…
₿enjamin retweeted
“X sufrió un ataque. Z es resistente a ese ataque. Por lo tanto, Z es más seguro.”
Cuidado con este razonamiento.
Z no es más seguro, es resistente a ESE tipo de ataque.
₿enjamin retweeted
Start 9 v0.4.0.2
LEER: a quienes administran su propio nodo Bitcoin con Start9.
StartOS 0.4 es un sistema operativo completamente nuevo, no un simple update.
Para pasar desde 0.3.5.1 existen dos métodos:
➜ Flash Update: mediante USB, que es el método recomendado por Start9.
➜ Over-the-Air: bajar e instala la nueve versión desde el propio servidor, tras reiniciarlo.
Ambos buscan conservar los servicios + datos, pero no ofrecen la misma fiabilidad.
@start9labs advierte que omitir pasos puede provocar pérdida de datos.
Sitio oficial:
docs.start9.com/start-os/upd…

₿enjamin retweeted

🚨Tienes iPhone y te han robado cRiPtO.
Puede que te robaran por instalar esto:
El 19 de septiembre de 2026, las firmas de seguridad SlowMist y OKX confirmaron que las versiones 1.1 y 1.2 de FomoPeek, una app para rastrear movimientos de grandes tenedores de criptomonedas, contenían un módulo capaz de explotar iOS para leer llaves privadas guardadas en otras aplicaciones del mismo teléfono.

🚨 SlowMist TI Alert: FomoPeek App v1.1–1.2 Asset Theft 🚨
We have recently received multiple reports of users having assets stolen. Our investigation found that the affected cases involved private key exposure, and some of the users had previously installed and used @FomoPeek App versions 1.1–1.2.
A joint investigation by the @SlowMist_Team and @okx security teams confirmed that the app contains malicious code.⚠️
Besides its normal features, FomoPeek includes two modules that are unrelated to its stated business functions. One of them contains an #iOS kernel exploitation framework with eight different exploit methods. The framework can automatically choose an attack method based on the device model and iOS version.
‼️Affected iOS versions: iOS 12.0–18.7 and iOS 26.0–26.1.‼️
If the exploit succeeds, the app may escape the iOS sandbox, access and decrypt Keychain data, and read files belonging to other apps on the device.
🔐 This means sensitive data stored on the device, including private keys, seed phrases, login credentials, chat history, and files, may be exposed.
The app also connects to hidden servers that are unrelated to its public-facing services and can receive remote commands.
Based on plaintext traffic captured during our analysis, the attack functionality is currently enabled and runs automatically at regular intervals. In general, devices running older iOS versions are at higher risk.
If you have installed or used FomoPeek versions 1.1–1.2, we recommend that you take action immediately:
1️⃣ Check your accounts and assets for any unusual activity.
2️⃣ On a trusted device where FomoPeek has never been installed, create a new account and generate a new private key and seed phrase.
3️⃣ Move your assets to the new account as soon as possible.
4️⃣ Update your device to the latest available iOS version.
5️⃣ Do not continue using or reinstalling FomoPeek.
6️⃣ If you notice any suspicious asset activity, contact the official support team of the relevant platform and keep the affected device and related evidence for further investigation.


₿enjamin retweeted

Después de los incidentes de Ledger y Coldcard, vemos cada vez más interés en implementar una multifirma multivendor.
¿Como funciona?
Si todo tu bitcoin depende de una sola marca, una falla de ese fabricante te pone en riesgo a ti también.
Si te importa realmente la seguridad la solución es asumir que tu wallet de elección puede fallar, no buscar el dispositivo perfecto.
Con una multifirma multivendor, tu bitcoin necesita más de una llave para moverse, cada una en una hardware wallet de una marca distinta. Si un fabricante falla, tu bóveda no cae con él.
Armarla bien tiene su complejidad, y un error ahí cuesta caro. Por eso no tienes que hacerlo solo.
Así es como funciona nuestra Implementación Guiada 1:1:
1. Llamada de diagnóstico de 15 minutos para entender tu caso.
2. Plan a medida según tu situación y tus objetivos.
3. Sesiones de implementación de 3 a 6 horas, según el caso, hasta dejar lista tu bóveda multifirma.
Tú la configuras, nosotros te guiamos paso a paso. Nunca tocamos tus llaves.
Toma el primer paso agendando una llamada de diagnóstico con nosotros, sin costo: cal.com/team/tltbtc/llamada-…

₿enjamin retweeted
¿Qué novedades hay en las últimas actualizaciones de am-i.exposed?


₿enjamin retweeted
Herencia en Bitcoin
Creé un esquema de herencia en @lianabitcoin que pude restaur en Nunchuk, conservando las mismas condiciones de uso + tiempo para el acceder a los mismos UTXOs.
Un mismo esquema de herencia, dos implementaciones diferentes.
En esta prueba diseñe un esquema de herencia con dos caminos difernetes:
➜ Llave principal: acceso inmediato.
➜ Llave heredera: acceso habilitado después de 150 bloques.


pero esto también... la tarea fundamental es reducir la fricción psicológica. nitter.cf/SahilC0/status/1838697…

₿enjamin retweeted
With 360 Bitcoin wrench attacks cataloged, it's time to take the archive to the next level. Over the weekend I clanked out this interactive dashboard; feedback is welcome!
jlopp.github.io/physical-bit…

₿enjamin retweeted
Gran artículo de Liana sobre la multifirma multivendor como estándar de seguridad en la autocustodia de #Bitcoin.
Algo que hemos empujado mucho @tusllavestusbtc y que aún tiene sus misconcepciones.


After the Coldcard RNG bug, some advised rolling dice or adding a passphrase. Both saved a few users this time. Neither protects against the next flaw.
Multi-vendor multisig should be the new standard.
New article on why, with 5 concrete Liana setups → wizardsardine.com/blog/the-m…
