

security & coffee nerd 🏳️🌈
she/her
Joined August 2021
- Tweets51
- Following111
- Followers1.5K
- Likes30



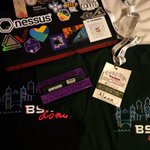

I had the wonderful pleasure of presenting my research at @BSidesLondon : "What's inside the open directories of 96 different threat actors" - a talk exploring the complete home directories and internal workings of many different crime groups, including an alleged APT.

2
15
896
#bugbountytips Here's a simple bash script for getting all wildcard root domains from Bugcrowd. It can be combined with notify and cron to continuously monitor for new targets.


Bug Bounty: Wordlists - Please do them properly.
medium.com/@nynan/bug-bounty…

Whenever I see people talking about /.git/ exposures for #bugbounty, it's only ever mentioned on the root URL (domain[.]com/.git/config). Remember that, even if uncommon, a git leak can happen on any URL path!
#bugbountytips


Ngl, when I first saw this I thought it was gonna be another gimmicky #bugbountytips, but I was pleasantly surprised I actually managed to produce another instance of this, which is fun :)
Cool bypass, shame it's a dupe for me tho ¯\_(ツ)_/¯


when you are looking for bugs like SSRF & Open Redirect.
and there is a blacklisted character.
try to bypassed using other Unicode characters.
I found Open Redirect Bypass Using (。) Chinese dot "%E3%80%82".
poc: redirect_to=////evil%E3%80%82com
credit:@h4x0r_dz
#bugbountytip

Shodan for Bug Bounty - and Why you shouldn't use these 53 Dorks.
#BugBounty #bugbountytips #infosec
medium.com/@nynan/shodan-for…
It's a nice start to this morning's bug hunting when you stumble across working exposed API keys + a super quick hackerone triage :)

I wrote this up a while ago for @Cyjax_Ltd and completely forgot to share it here...
"A comprehensive synopsis of 217 subdomain takeover reports" - looking at strategies, business impacts, mitigations and trends.
#infosec #BugBounty #cybersecurity
cyjax.com/2022/10/24/a-compr…
I was so fortunate to be able to speak at #bsidescymru , it was an incredible event full of so many amazing people and eye-opening conversations.

Automated and Continuous Recon/Attack Surface Management - Amass Track and DB
#BugBounty #bugbountytips #infosec #cybersecurity
medium.com/@nynan/automated-…
Being given the opportunity to speak and attend @BSidesLondon was such an incredible experience!
I met so many amazing new people and it was great to finally showcase @nyxilar's and my investigation into Fangxiao.
cyjax.com/2022/11/14/fangxia…
#BsidesLDN2022


1
7
The new cs.github.com search allows for regex, which means brand **new** regex GitHub Dorks are possible!
Eg, find SSH and FTP passwords via connection strings with:
/ssh:\/\/.*:.*@.*target\.com/
/ftp:\/\/.*:.*@.*target\.com/
#BugBounty #bugbountytips #infosec

Super surreal to see my investigation featured in a @BleepinComputer article. Really happy with how it turned out :)

42,000 sites used to trap users in brand impersonation scheme - @billtoulas
bleepingcomputer.com/news/se…

3
I got so many requests, so I've made a repo where you can find wordlists for all the subdomains that were vulnerable to Subdomain Takeover from 217 bug reports, as mentioned in my recent blog.
#BugBounty #bugbountytips #infosec
github.com/iamNynan/SDTO-rea…

What I learnt from reading 217 Subdomain Takeover bug reports.
#BugBounty #bugbountytips #infosec
medium.com/@nynan/what-i-lea…

I wrote a blog on the most under-rated, underused features of Amass, that you can use to set yourself apart from other bug hunters.
Thanks to @jeff_foley, the creator of Amass, for input on the blog.
#BugBounty #bugbountytips
#infosec #bugbountytip
medium.com/@nynan/how-to-act…
Use Universal Analytics (UA-XXXXXXX) codes from a website's source code, and spyonweb.com/ to find new root domains owned by the company to increase your attack surface.
#BugBounty #bugbountytips
#infosec #bugbountytip


I created a bash one-liner to automate broken link hijacking vulnerabilities which has already resulted in me finding a vulnerability in one of the NCSC (nl)'s assets.
Thanks to @akincibor1 for the inspiration :)
links in 🧵
#BugBounty #bugbountytips
#infosec #bugbountytip


PoC CVE-2022-0817 simple bash one-liner.
mass automated unauthenticated SQli
Copyable version and reference in 🧵
#BugBounty #bugbountytips
#infosec #bugbountytip

copyable version: github.com/iamSm9l/Utils-and…
reference: wpscan.com/vulnerability/692…
3