

CrowdSec is a CTI tool leveraging crowdsourced data to identify and block malevolent IPs in real time worldwide. Join our Discord: https://nitter.cf/t.co/iboAbgMP6x
Joined May 2020
- Tweets2.6K
- Following1.3K
- Followers19.5K
- Likes3.2K




The replay is up 🎬
Thibault Koechlin and Sébastien Blot show how CrowdSec 1.8's WAF tells real browsers from bots in disguise, with a demo of how to set it up: youtube.com/watch?v=rHKs3yAq…
#WAF #botdetection
Today at 4 PM CET, bots take the stand 🤖
Thibault Koechlin (CTO) and Sébastien Blot (DevSecOps) go live to show how CrowdSec 1.8's WAF tells a real browser from a bot pretending to be one.
Bring your questions 👇 youtube.com/live/rHKs3yAquQo
#botdetection #WAF


In just 3 steps, you can set up the CrowdSec WAF, a free and open-source web application firewall:
1. Install the rule collections
2. Turn on the AppSec Component
3. Point your bouncer at it
#WAF #opensource

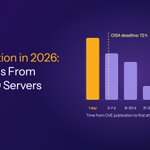
36% of exploited CVEs were attacked within a day of publication. Another 27% within the week.
CISA gives US federal agencies 72 hours to fix the most urgent ones. For more than a third, the attack starts first.
What our network saw in 2026 👇
#cybersecurity #vulnmanagement

8 lessons from 500,000 servers, from Philippe's SANS talk: crowdsec.net/blog/exploitati…


The full breakdown, phase by phase: crowdsec.net/vulntracking-re…


How the 2 free CrowdSec WAF rules work: crowdsec.net/blog/php2shell-…

PHP2Shell (CVE-2026-109618/109619): Unauthenticated attackers can run code on a PHP server. No login, no vulnerable app code needed.
Patch now: 8.5.12, 8.4.27, 8.3.36, 8.2.35.
PHP 8.1 and older: no fix from the PHP project.
php.net/archive/2026.php#202…
Don't wait for a sign of attack: the request returns a normal HTTP 200. In our network data, 36% of exploited CVEs were attacked within a day of publication:
crowdsec.net/blog/exploitati…
What is bot detection, in 30 seconds? 🤖
It's how your site tells real visitors from automated ones before they can scrape your content, buy out your stock, or hammer your login page.
CrowdSec's WAF Bot Detection does it with fingerprinting and proof of work, without getting in the way of real customers.
Watch the quick explainer 👇
Set it up: docs.crowdsec.net/docs/appse…
#WAF #botdetection #cybersecurity #opensource
Console notifications now go straight to your inbox. 📨
Notification rules now support email, so you can create a rule without connecting Slack or Discord first. Set a rule, add your address, done.
Set up your first rule: app.crowdsec.net/notificatio…
Available on Premium.
CrowdSec saw the first requests matching CVE-2026-88771 on September 22, five days before Citrix published it with a fix (and before @watchtowrcyber shared details). It's a CVSS 9.5 flaw in NetScaler ADC and Gateway: no login, default configuration, root on the box.
Our signal counts are low, but don't read that as low risk. Careful operators pick their targets first, and two of the addresses we saw went after this CVE and nothing else.
Patching won't remove anyone already inside. The full story is in this week's Threat Alert 👉crowdsec.net/vulntracking-re…
#cve #cve202688771 #threatalert #cybersecurity

On the night of 7–8 October, a drone attack hit Yandex's data center in Sasovo, Russia.
Our sensors saw it from the other side of the internet: the YandexBot traffic hitting our network went dark.
Here's what the CrowdSec map showed 👇 youtube.com/shorts/GJqUkh4Dw…

Two visitors hit your site. Same browser, same clicks, same speed. One of them is a bot.
Which one? CrowdSec 1.8's WAF can tell, and on October 29, our experts will show you how, live, along with everything else in 1.8.
📅 October 29, 4 PM CET
Get a reminder → youtube.com/live/rHKs3yAquQo
#webinar #WAF #botdetection #cybersecurity