

CERT-In Empanelled & ISO 27001:2022-certified, we offer end-to-end cybersecurity solutions to modern businesses, protecting your digital assets.
Mumbai, Maharashtra, India
Joined June 2020
- Tweets981
- Following120
- Followers103
- Likes48




A software vulnerability is only part of the problem. Not knowing where it exists can make it much harder to manage. In our latest article on LinkedIn, we explore how SBOM works, why it matters, and how it helps improve software supply chain security.
#CyberSecurity #OpenSource

21
What defines CyberNX goes beyond what we do. It starts with the vision that guides us. Our Co-founder, Bhowmik Shah, shares what we stand for and what we aim to build. #CyberNX #Cybersecurity #CyberResilience #Leadership #DigitalSecurity #CyberSecurityLeadership
10
Slow systems? Application issues?
Discover how Full-Stack Observability helps teams identify root causes faster and improve performance with Hamdan Ansari from CyberNX.
👉 Watch the video: youtu.be/igLppAJe82k?si=gKyk…
14
CERT-In has issued a critical advisory warning to NBFCs and financial service providers about cyberattacks targeting payment and disbursement of APIs.
Click here to read more
linkedin.com/feed/update/urn…

20
Quantum computing is reshaping the future of cybersecurity. Bhowmik Shah, CTO & Co-Founder at CyberNX, highlights why crypto-agility must become a strategic priority for businesses.
#Cybersecurity #QuantumComputing #PostQuantumCryptography #CryptoAgility #DataSecurity #CyberNX

12
What matters most in a modern SOC?
0%Faster threat detection
0%Faster incident response
0%Fewer false positives
0%24/7 monitoring
0 votes • Final results 10
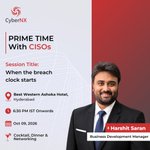
Harshit Saran, Business Development Manager at CyberNX, will be attending Prime Time With CISOs, Hyderabad. With “When the Breach Clock Starts” as the session theme. Meet us and let’s exchange ideas, and explore what’s next in cybersecurity.

17
As @knowalledge , Co-Founder & Director of @CyberNX_Tech , shares, our mission has always been clear: to make cybersecurity more accessible, effective and affordable for organisations of every size.
#CyberLeadership #Director #cybersecurity #InfoSec #cybernx #LeadershipInsights
21
Patient data demands a practical approach to DPDPA readiness. We’ve outlined 6 key areas healthcare organizations should address, from data classification and consent to breach response.
Read the full article linkedin.com/feed/update/urn…
#DPDPA #DPDPACompliance #Healthcare #cybernx

37
AI is reshaping cyber risk, as a weapon, an autonomous agent, and a target. Read our latest article and share your thoughts.
linkedin.com/feed/update/urn…
🤖 Made with AI

15
1 TB of data reportedly exposed of Bank of Baroda.
You don't always need to hack the bank.
Sometimes you just need one identity with years of accumulated access.
That's why identity security is becoming the new perimeter.
#CyberSecurity #BFSI #IdentitySecurity #CyberNX

51
The quantum era is closer than you think. That's why banks must prepare for the future.
In this article, find:
1 - The quantum threat to banking cryptography for CISOs & boards
2 - A BFSI roadmap from CBOM to PQC migration
Read now! linkedin.com/feed/update/urn…

18
Your customers don't get hacked because they're careless.
They get fooled because fake websites now look just as trustworthy as the real ones.
If AI can clone your website in a few hours, your logo is no longer your brand's biggest security asset.
#Phishing #CyberSecurity #AI

27
RBI's 2026 draft on model risk changes the game for banks: it's not just AI anymore, every model (even that old lending spreadsheet) is now in scope.
And using a vendor's model? Doesn't transfer accountability for what it does.
Full breakdown: linkedin.com/feed/update/urn…

1
23
Our Co-Founder, Gopakumar Panicker says, DPDP compliance isn't achieved through policies alone.
It's built into the systems, processes, and controls that govern how personal data is collected, used, stored, and protected.
#DPDPCompliance #DataProtection #CyberSecurity #CyberNX

25
The Accenture breach proves that customer data isn't the only thing attackers are after. Source code, cloud credentials, and DevOps environments are now high-value targets.
Read our latest analysis on LinkedIn. 👇
linkedin.com/feed/update/urn…
🤖 Made with AI

49
Banks aren't the easiest target anymore.
Healthcare. Retail. Manufacturing. Telecom. Government.
No industry is off the radar.
Stop saying, "We're not a target."
If your business has customers, payments, or data...
You already are.

30
Technical expertise is essential. But it isn't the only thing that determines the success of a Red Team engagement.
Here are 5 questions to ask before the first attack is ever simulated👇
linkedin.com/posts/cybernx_c…

1
26
DPDPA's DPO mandate is narrow. The governance questions around it aren't.
Reporting lines, liability, outsourcing accountability, we unpacked what the law leaves open
Read full article at -linkedin.com/feed/update/urn…

25
DPDPA compliance is both a legal job and a security job.
Policies need controls behind them. Controls need testing. Breaches need catching fast enough to report on time.
The regulation demands all of it. Read to know where the handoff happens.
linkedin.com/feed/update/urn…

20