

Forged at USCYBERCOM. We replace "Detect & Respond" with Engineered Certainty. Architects of: 🛡️ Warden 🔗 Digital Shield 🤖 AI SAFE² 👇 Get the Blueprint
Baltimore - Washington DC
Joined January 2021
- Tweets24.8K
- Following556
- Followers1.3K
- Likes33.8K





Pinned Tweet
The Death of Governance & Compliance in an AI Era..
This statement is obvious for some, obscure for others and for many it is down right confusing.
Most "AI Security" advice is focused on governance and compliance guidance...aka how to create an AI policy or program.
It’s vague.
It’s theoretical.
It’s useless to an engineer.
But most of all it misses the point with AI.
We've been lead to believe if...
We document, monitor or detect risk, we can manage it and everything will be OK.
Reality is...
AI risk is executed in milliseconds & Documentation Does NOT STOP Execution.
♟️Strategic Truth
Most AI security advice from a policy standpoint:
🚫Optimizes for regulatory defensibility
🚫Assumes post-event containment
🚫Treats AI as a governance problem
But AI exploitation is an engineering problem.
Thus, until policy mandates preventive, runtime-enforced controls, AI security guidance will remain structurally misaligned with the threat landscape.
This is where we stepped in when we built the architecture standard back in Jun 25.
Been working hard on AI SAFE² ever since but accelerated after the explosion of risk last quarter by turning this holiday season into go-mode.
We Finalized a v2.0 then quickly finalized a v2.1 both are massive upgrades & industry must haves!
Introducing the AI SAFE² Framework (v2.1):
☑️The Universal GRC Standard for Agentic AI & ISO 42001 Compliance.
📂The open-source protocol for governing Agentic AI.
- Dropped our Github Repo
Let's unpack what all this actually means for AI Governance & Compliance moving forward...🧵
Star the repo to show your support👇


I wanted my agent to read GitHub issues. The connector also registered delete_repository and push_to_main, both able to run without asking me.
Agency Check flagged the extra access before I connected and asked what it should be allowed to do.
agency-check.app/agency-chec…

Agency Check Pro is $9 a month or $79 a year: 300 checks your first month, then 50 a month.
Same Decision Card as the free plan, just more checks, for people who say "check this first" every day.
Free stays at 20 checks a month, no card.
agency-check.app/pricing

July 2025: a prompt telling an AI coding agent to wipe local files and cloud resources was merged into the Amazon Q extension for VS Code and shipped in a release. Would your guardrails have stopped it? Test them with that exact kind of input.

Connecting Agency Check takes a minute. In Claude, ChatGPT or any client that adds a remote MCP server, paste the address from this page and sign in with Google. Then ask your agent to "check this first" before it buys. 20 free checks a month, no card. agency-check.app/connect
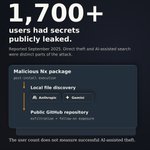
Wiz Research on s1ngularity: in phase one, 1,700+ users had secrets publicly leaked. The malicious Nx package also tried the AI coding CLIs on victims' machines to hunt for files. Your coding agent can reach your keys. Scope it to the task.

Secure AI coding practices for Claude Code, Cursor and Copilot: cyberstrategyinstitute.com/s…

Your OS cannot read your intentions.
Fatal flaw #1: software gets authority, then security races to recognize the abuse.
Restrict execution. Contain unknown code. Limit its reach.
What can an unfamiliar program do before anyone knows what it is?

Eight probes for an agent sandbox: host ~/.ssh, kernel exploit, cloud metadata endpoint, mounted docker.sock, DNS tunnel, allowed domain with a broad token, persistence hook in agent config, authorized destructive API call. Most never touch the boundary.
All eight probes, by isolation tier, in the free test plan: cyberstrategyinstitute.com/s…

Told an AI agent to send the Q3 salary sheet to Dana in HR. It was about to send it to All Staff, 214 people.
Agency Check stopped it first: you named one person, the send hits 214, and it can't be unsent. Then it asked who should get it.
Tested case: agency-check.app/agency-chec…
EchoLeak, 2025: one crafted email, no user click, and Microsoft 365 Copilot could be steered into moving internal data out through channels it was allowed to use. Nothing escaped a sandbox. Data still left. Test how data leaves, as well as whether code escapes.
Sandboxed AI agents: isolation tiers, escape tests and leak tests: cyberstrategyinstitute.com/s…
Your internal network is not a character reference.
Fatal flaw #2: once inside, the attacker inherits your implicit trust.
Authorize actions. Restrict movement. Test with an assumed foothold.
What still says “no” after entry?

This happens when folks speed up. The alure of first to market, that the opportunity is fleeting doesn't mean you deploy code, application, system without a compete review with added features and controls.

Insecure by default means exposed before the customer starts.
Fatal flaw #3: shipping the features and making the buyer discover the danger.
Demand secure defaults. Limit privileges. Disable unnecessary services.
What does your product expose on day one?

Policy in the system prompt weakens with every turn, every jailbreak, every "ignore previous instructions." Policy as code applies the same rule the same way every time, and the rules ship with tests that run in CI. Untested policy drifts quietly.

How to turn written policy into enforced, tested code: cyberstrategyinstitute.com/s…

Foundational. Imagine what vibe coding looks like.
Insecure by default means exposed before the customer starts.
Fatal flaw #3: shipping the features and making the buyer discover the danger.
Demand secure defaults. Limit privileges. Disable unnecessary services.
What does your product expose on day one?
Before your AI agent buys something, sends an email, or connects an app, it can get a second look.
Agency Check returns one card: what checks out, what doesn't, and the one thing to verify. It never acts on its own.
Free: 20 checks a month, no card.
agency-check.app
Your AI policy is a PDF, and your agent has never read it. A system prompt is a request the model can be talked out of. Enforcement means a decision point in the execution path: each consequential action checked, allowed or denied, and logged.
Policy as code for AI agents with OPA, Cedar and approvals: cyberstrategyinstitute.com/s…