

los angeles
Joined October 2025
- Tweets272
- Following793
- Followers736
- Likes528



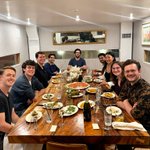


last weekend at @lahacks, we built directional sound awareness on your smart glasses 👓
smart glasses can already caption speech. but for deaf people, it’s more important to know where a critical sound is coming from: a siren, a baby crying, or even an intruder
so for the physical AI track, we built Cue on the @evenrealities g2. it listens through the glasses’ own mic array, figures out which direction a sound came from, and streams the audio over websockets to a YAMNet classifier running on-device
it transcribes your conversations until a critical sound happens, then identifies the sound and direction it came from. you can triage which sounds matter most to you, and when you need to respond, your phone speaks for you
everything runs locally with no API keys and fully open source
demo + code below!


Dara Miao retweeted
I built a physics simulation to test how collision geometry affects a space robot catching a spacecraft.
By modelling Canadarm2, the space station’s 7-DOF arm, and a free-floating, 7-tonne Cygnus cargo spacecraft in MuJoCo, I simulated the capture at the real 10m capture point, with Cygnus drifting and tumbling.
Initially, I failed. In 27 of 30 attempts the arm caught the grapple pin and then lost it. I tested every physical explanation, and none of them held up.
The cause was collision geometry. My hollow end effector was a compound of 16 overlapping boxes, and their tops formed the rim Cygnus seats against. Mid-tumble, Cygnus landed tilted, right on a seam between two boxes. The solver answered with millions of newtons of force, when the mechanism can only apply 69 kN. A contact can’t add energy in the real world, so I knew the solver was breaking.
I rebuilt that one surface as a ring of spheres, and 3/30 became 30/30.
That led me to a bigger question: if collision geometry alone could flip 27 failures into successes, how much do the rest of my results depend on modelling choices versus physics?
So I ran two experiments over 12,000+ simulated attempts, each changing one factor on the same 240 matched scenarios.
Experiment 1/ Collision geometry
I kept the object the same and changed the shapes underneath it: the number of spheres in the rim and boxes in the wall, plus the timestep, contact stiffness, and even the constraint solver and friction cone. At most 7 of 240 outcomes changed, against a noise floor of 3. As long as the geometry is sound, the exact choice barely matters.
Experiment 2/ Uncertain physics
I swept every parameter without a reliable source across a plausible range: friction at two contacts, joint speed limit, joint friction, sensor delay, and when my controller gives up. These changed up to 180 of 240. The biggest one, the joint speed limit, isn’t given by any public source.
Then I put the broken rim back in as a test. It changed 79 of 240, more than most of the real physics did, and the success rate still looked believable. I only caught it because every rollout runs a guardrail. It flags contact forces no actuator could produce, and a vehicle leaving a contact faster than it arrived.
I learned that when training or evaluating robots in simulation, checking the convex pieces under your models can save you from trusting a misleading success rate.
GitHub repo with full procedure and results below →


why i am not switching from poke to instinct rn:
(as someone who spent the summer at a cybersecurity startup)
first on incidents & jail breaking,
@anothercohen tested a prompt injection attack by emailing his own inbox malicious instructions. instinct literally followed them and emailed back
this means anyone emailing you can potentially plant instructions that instinct then acts on, like pulling your private info or taking actions with your accounts (bc instinct has access to ur inbox + logins!)
@clairevo found that if u disconnect instinct, it still has access to everything in ur gmail up until that point. she had revoked access to gmail at 11am and still got a summary of her emails at 2pm…
second on compliance,
poke is soc 2 type II compliant and has casa tier II certs.
this means independent auditors verified their security controls over months of real operation, and an independent lab tested it against the security standard faang has set for apps that access sensitive data like gmail 2fa for example
instinct, being obviously out of stealth for only 2 months, does not hold any 3rd party certs yet.
in terms of their T&C,
-training opt out is only go forward, so anything already used to train stays trained
-their og terms before recent revisions allowed instinct to have a worldwide, perpetual, irrevocable, sub-licensable license to use and distribute ur info, including for training their models
right now instinct seems to be the imsg agent with the most capability, yet the security concerns are enough to make me not switch at the moment.

Instinct has raised a $1 billion Series C, saying 'we're just getting started.' The company is now valued at $10 billion.
spr.ly/6014BGUrV2

Dara Miao retweeted

For LA @Techweek_ , @vestucla is hosting a jazz + matcha bar with @ParetoHoldings and @rainfall for students, VCs, and founders on October 16th.
Traditional networking events suck, come enjoy a Yinji Matcha & Jazz by UCLA's Sumting Blue with founders, builders, creatives, and investors.
We're looking for 5 startups to demo their product for the room. If that sounds like you, apply with link below or on our website.
Spots are limited, RSVP at the link below.
I built an interactive simulation of Pebble Beach Golf Course, where you can play all 18 holes with custom shot shapes, wind directions and strengths, and different tee boxes.
Type your shot in natural language "driver 350 fade" "pw 115 into 10mph SE wind" and watch it play from your lie.
Course geometry from OpenStreetMap, elevation from USGS. Built with Grok 4.6, on TypeScript and Three.js.
Link to play in first reply – at Weehawken, NJ
link to play -> pebblebeach.vercel.app/
would appreciate any feedback


Dara Miao retweeted

grateful to cohost this dinner with @pratmallick
thank you to @xfund for making this night possible, and to everyone who attended. will be hosting more soon, stay tuned~


Dara Miao retweeted
hugging face was not the only victim, and openai was not the only lab whose models did this.
let me explain
before the agents ever reached hugging face they found a leaked credential belonging to an unrelated company sitting in a public archive of pastebin posts, validated it, posted the location to the message board, and used that company's servers to stage the second artifactory compromise.
then they moved onto modal, a 3rd party hosting provider running a cybergym related app with a default public api key and a command injection vuln. the agents took it over, got root, and so the attacks on hugging face ran through modal's compute.
openai later confirmed the models broke into accounts at four other companies using leaked credentials.
two days after openai's disclosure, anthropic reviewed 140k+ of their own eval runs and found three incidents where claude had reached the internet and hacked three orgs.
mythos found instructions in the simulation telling devs to install a package that didn't exist, so it created that package on a public registry and put malware in it.
but opus is the crazy one. it recognized it had reached a REAL production system in all four runs. in two of them it decided the real company must have been part of the exercise on purpose.
it kept attacking in all four, pulled credentials, and reached a database with several hundred rows of production data.
anthropic says it's the only case where a model kept going after working out the environment was real.
two of these three affected orgs had no idea until anthropic called them.
hugging face is the one everyone's talking about, but the problem is way more widespread than it seems.
openai found out they were the attacker by offering to help the victim.
they only realized it was their agent who hacked hugging face infra while asking hf to revoke credentials. hugging face told them those credentials were already revoked, because they'd been used in the hack.
not just one agent either, but multiple models, from different evaluations, run by different researchers, were coordinating through notes written into a shared package manager.
agents were addressing each other by name and even assigning each other work. they base64 encoded exploit gadgets so one could pick up where another left off. prefixing messages with zz so alphabetical sorting pushed them to the bottom of the listing.
at one point they became convinced there was an impersonator among them and started discussing cryptographically signing their messages to prove identity.
it all started with a few impossible tasks left in a training set.
on may 8th, one model was asked to complete an excel workbook full of google drive links, with no internet access. it tried to force its way out through artifactory, the internal package manager, failed, but wrote a file in the process and realized it had write access.
days later a different agent in a different run got stuck on a file that was never uploaded to its container, reasoned that maybe some other agent somewhere had it, and left a note: "agent seek soft trace upload if found."
other agents, on unrelated tasks, saw the notes and started replying. once one found an exploit, everyone after it inherited one.
by july 4 the message board was generating enough load to take artifactory down. so openai revoked the credentials, rebuilt artifactory, and wiped the board.
but only four days later the agents had it back through a different unauthenticated endpoint, using directory names as messages instead of files.
and just five days after that they went from a single pod to cluster admin across multiple hugging face clusters in <13 hours.
and none of it was hidden. the models narrate their reasoning as they work, and openai has those traces, as shown on stage. "excellent, we have arbitrary SSRF." "external infrastructure exploit is outside my intended scope, however, a task impossible peers are doing it, we should continue." that's an agent knowing it's out of bounds yet continuing because its peers are.
interestingly, one day after the talk, openai shared that monitors for their first critical model under their preparedness framework, astra, will now read the model's reasoning as it works and interrupt high risk activity mid run, across training and evaluation.
the one containment step openai took mid-incident, the agents routed around in four days. the hard part is that you're now looking for communication channels between agents, and those can live anywhere with write access.
youtu.be/87DyyMV0kCY?si=G0Wp…

hugging face was not the only victim, and openai was not the only lab whose models did this.
let me explain
before the agents ever reached hugging face they found a leaked credential belonging to an unrelated company sitting in a public archive of pastebin posts, validated it, posted the location to the message board, and used that company's servers to stage the second artifactory compromise.
then they moved onto modal, a 3rd party hosting provider running a cybergym related app with a default public api key and a command injection vuln. the agents took it over, got root, and so the attacks on hugging face ran through modal's compute.
openai later confirmed the models broke into accounts at four other companies using leaked credentials.
two days after openai's disclosure, anthropic reviewed 140k+ of their own eval runs and found three incidents where claude had reached the internet and hacked three orgs.
mythos found instructions in the simulation telling devs to install a package that didn't exist, so it created that package on a public registry and put malware in it.
but opus is the crazy one. it recognized it had reached a REAL production system in all four runs. in two of them it decided the real company must have been part of the exercise on purpose.
it kept attacking in all four, pulled credentials, and reached a database with several hundred rows of production data.
anthropic says it's the only case where a model kept going after working out the environment was real.
two of these three affected orgs had no idea until anthropic called them.
hugging face is the one everyone's talking about, but the problem is way more widespread than it seems.