

The official account of the U.S. Department of War Office of the Chief Information Officer. Linking, replying/following does not = endorsement.
Pentagon, Arlington, VA
Joined September 2016
- Tweets994
- Following459
- Followers13.4K
- Likes137
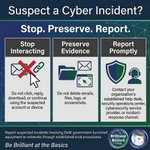


If you suspect a cyber incident on @DeptofWar government-furnished equipment or networks, stop interacting, preserve the evidence, and report it promptly through your organization’s established support or security channel. Early reporting helps protect the mission.
Be Brilliant at the Basics.

Final Call!
Submit your nominations for the 2026 @DeptofWar Chief Information Officer Awards before the application closes today at 1200 Eastern time.
Take the time to recognize the service members, DoW civilians, and federal partners whose contributions strengthen the Department’s information technology, cybersecurity, and mission capabilities.
Review the awards guidance and submit nominations before the deadline.
dodcio.defense.gov/About/Awa…

This week’s Cyber Tip: Back it up before you need it.
Hardware can fail, devices can be lost, and ransomware can make important files unavailable when you need them most. Regular backups help ensure your personal files can be recovered instead of replaced.
Protect your files:
✔ Back up important files routinely.
✔ Keep a copy separate from your primary device.
✔ Make sure you can restore your backup when needed.
Be Brilliant at the Basics.

Reminder!
Nominations for the 2026 @DeptofWar Chief Information Officer Awards close tomorrow, October 30, at 1200 Eastern Time.
The awards provide an opportunity to recognize service members, DoW civilians, and qualifying federal partners whose leadership, innovation, and commitment strengthen the Department’s information technology, cybersecurity, and mission capabilities.
Review the awards guidance, confirm eligibility and required materials, and submit nominations before the deadline.
dodcio.defense.gov/About/Awa…

Securing operational technology within the Defense Industrial Base is a critical component of national security. Implementing compensating controls when immediate patching of mission-critical machinery is not possible represents number five on the @DeptofWar CIO’s Brilliant at the Basics Operational Technology Top-10 best practices list.
To assist our industry partners in executing this practice, we recommend integrating Cybersecurity and Infrastructure Security Agency tools into standard defensive workflows. Utilizing @CISAgov CodeScanAI helps organizations scan for and detect potential security flaws in code during development. Simultaneously, the @CISACyber Known Exploited Vulnerabilities (KEV) Catalog remains the authoritative federal source for tracking vulnerabilities actively exploited by adversaries in the wild. By executing these fundamentals, our industry partners build the cyber resilience necessary to protect critical Department of War capabilities.
- CISA CodeScanAI tool link: cisa.gov/resources-tools/ser…
- CodeScanAI GitHub repository: github.com/codescan-ai/codes…
- CISA Known Exploited Vulnerabilities Catalog link: cisa.gov/known-exploited-vul…

From classroom to career, BOND Advisor September Secrist explains how the DoW Cyber Service Academy helps develop the next generation of cyber and information technology talent.
Watch the reel to learn about CSA scholarship applications and opportunities to build a career protecting @DeptofWar information systems and networks.
cyber.mil/dod-workforce-inno…
Saluting @DC3Forensics for their work fighting international cyber crime. Great work team!

How does DC3 combat cybercrime?
By coordinating with USG partners to freeze $300M+ in illicit nation-state cryptocurrency and identifying $3M tied to terrorist-linked ATM jackpotting.
Details in comments.
#EO14390 #DoW #CyberCrime

Our computers almost always hold personal records, financial information, and access to our online accounts.
In honor of the @DeptofWar's celebration of Cybersecurity Awareness Month, we encourage you to Be Brilliant at the Basics and turn on its firewall. You should download a reputable antivirus software.
Always keep your operating system, applications, and security tools updated.
These simple steps are often overlooked but play a vital role in protecting our information from cyber risks.

It’s time to Be Connected. Today, Principal Director for Command, Control, and Communications Kevin Mulvihill kicks off the last week of Cybersecurity Awareness Month with a reminder to secure wearable devices and the information they collect.
Watch the reel for practical steps to manage privacy settings, limit location sharing, keep devices updated, and avoid connecting personal wearables to government-furnished equipment unless specifically approved.
Help protect yourself, your business, and the @DeptofWar by being Brilliant at the Basics.
Cyber Service Academy (CSA) Scholar Spotlight: Ms. Kathleen “Katie” Gallagher, DoW CSA Scholar Alumni, earned both her undergraduate and master’s degrees at a National Center for Academic Excellence in Cyber (NCAE-C). She is now an IT professional within the @DeptofWar. DoW CSA scholarships provide tuition, stipends, paid summer internships, and enable scholars to start jobs immediately after graduation, moving seamlessly from student to cyber professional. If you are looking to study cyber in college or graduate school, now is the time to apply for the 2027-2028 DoW CSA Scholarship application window!
To learn more or to apply now through Jan. 31, go to cyberworkforce.mil/Academic-…

Harry The Hamster is at it again. Now he’s looking for an open network in your neighborhood. Don’t let your retirement account be his housewarming gift.
Encrypt your home Wi-Fi. Use a strong, unique password. Keep Harry out of the house—and out of your business.
Be Brilliant at the Basics

"It's just charging my phone." That single plug can compromise an entire @DeptofWar mission network. Threat actors weaponize everyday accessories via firmware exploits and payloads the second they touch a port.
Keep your Government Furnished Equipment (GFE) locked down:
- Never charge personal phones, watches, or devices via GFE USB ports.
- Zero personal flash media or thumb drives—ever.
- No unapproved personal Bluetooth or wireless accessories.
- If it requires a driver download, it doesn't plug in.
Cyber defense starts at the port. Be Brilliant at the Basics!

LTG Paul Stanton, @DoW_DISA Director and DCDC Commander, highlights a critical threat we all face every day Social Engineering. SI is making these attacks more sophisticated and harder to spot. Verify before you share and Be Brilliant at the Basics.

Our Director, @USArmy Gen. Paul T. Stanton explains how to spot social engineering and protect your data. Building this awareness is key to being #BrilliantAtTheBasics.
For this week’s @DoW_CIO #CyberSecurityAwarenessMonth campaign we're urging you to stay vigilant & be secure.
Clear calendars, casual clothes, and incredible conversations.
Last Friday, the @DeptofWar CIO Enterprise Technology Excellence (ETE) team gathered for an All-Hands focused entirely on connection, introducing new teammates, sharing unknown facts about one another, and collecting honest ideas on how we can make our everyday work experience even better.
Proud to work alongside such an amazing, dedicated group!

Protecting @DeptofWar warfighters and ensuring they can accomplish the mission demands resilient and rehearsed operational technology (OT) incident response capabilities across the DIB. OT response is fundamentally different because these incidents directly impact physical infrastructure.
Prepare – Contain & Mitigate – Recover – Integrate Lessons
Brilliant at the Basics highlights two valuable resources to bolster partner readiness:
- @DC3Forensics's DIB Vulnerability Disclosure Program: For mitigating public-facing software vulnerabilities.
- @CISAgov ICS310 Training: For building OT threat-detection capabilities.
Links:
DIB-VDP: dc3.mil/Missions/Vulnerabili…
CISA ICS310: cisa.gov/resources-tools/tra…

Calling all USPACOM/DoW cyber personnel: Ready to help shape the future of cyber at the @DeptofWar? If you're in the USPACOM area, join DoW CIO Cyber Workforce leadership at the Hilton Hawaiian Village on Oct. 26 from 10:30 am – Noon. This is a great opportunity to connect directly with DoW CIO Cyber Workforce leadership, share your vision, and discover upcoming pathways for career growth and skill development in our community.
For more information, go to: events.afcea.org/TIP26/Publi…
Bring your ideas and energy—we can’t wait to connect!

In 2026, smartwatches, optical smart glasses, and fitness trackers have become second nature. They optimize our health, streamline notifications, and log our daily habits with incredible precision.
However, every sensor tracking your pulse or step count opens a digital door. This Cybersecurity Awareness Month, it’s time to take a closer look at the physical and cyber-attack surfaces strapped directly to our wrists and faces.
Be Brilliant at the Basics and make it a priority to secure your wearables.

@DoW_CIO retweeted

🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗 go.dhs.gov/5Hi
@DoW_CIO retweeted
We recommend Cisco users disable the Smart Install (SMI) auto-loading feature on all NSS and DIB network devices to mitigate exploitation by remote attackers. Have you taken this action? Read more: media.defense.gov/2019/Jul/1… #CybersecurityAwarenessMonth

ALT The image displays a list titled "SMI Mitigation Actions" with a background of a gear and network motif. The list includes: 1) Disable Smart Install auto-loading feature on all network devices. 2) Review Cisco switch configuration files for deviations from documented pre-existing configurations. 3) Implement deny by default strategy at edge firewall devices and ensure TFTP (UDP port 69) and SMI (TCP port 4786) are denied.