

@boldstartvc: the Inception fund. Helping the bold start. First check for technical founders. Security, AI infra, physical AI, agents & the weird. What’s 🔥 👇
Miami
Joined January 2009
- Tweets10.9K
- Following3.5K
- Followers20.9K
- Likes36.2K


Pinned Tweet
🔥 up to announce @boldstartvc Fund VII
$250M to back bold technical founders building the autonomous enterprise.
From Inception. Before the world believes.
It always starts with an idea that feels insane… until it isn’t.
🎥👇🧵
NO!!!
This would be incredibly damaging to our startup ecosystem and limit choice
Assuming we go this path who is going to offer the best sovereign open weight models? Very few can afford to build and offer.


Hard agree but would be killer if you made them open weight!
So much opportunity for whoever has the best sovereign open weight model

We’ve heard again and again that enterprises don’t want to pour all their valuable IP, data and tacit knowledge into someone else’s model. They want control of their own weights.
2
873
Sure seems that way and glad OpenAI is leading the way
Amazing at finding vulnerabilities but still needs context and deep understanding of systems to patch at scale. Also seeing lots of complaints on cost and still handicapped so can’t defend the way one needs to…
Which means so much opportunity for swarm and intelligence first startups. Market is massive, problems are serious, not winner take all, and will be layered with different players. Keep building 🏗️. Lots to do to keep us all safe 🙏🏼

Ed Sim retweeted

Proteins move, and the best drug discovery models need to learn how. @ToposBio is now running 2-3x more molecular dynamics with @nvidia cuPotential, and up to 7x with its own optimizations. More physics means better training data for its generative models, which is how you go after targets once considered undruggable 🧬 Proud to back @r_zarcone and @khosra from inception.
nitter.cf/ToposBio/status/212243…

Proteins move. Drug discovery moves with them.
With @nvidia and @NVIDIAHealth cuPotential in our OpenMM workflows, we're running ~2-3× more molecular dynamics. Up to ~7× with our own optimizations: more physics to train our generative models on.
More detail on our blog: toposbio.ai/blog/nvidia-cupo…
Sadly yes. We can’t let this happen
Wrote more about it my weekly newsletter Saturday What’s 🔥 #524
👇🏼


The Financial Times acknowledges that the ouster of Nvidia CEO Jensen Huang is a massive blow to the open-source community.
This is a victory for the aspiring monopolists at Anthropic and OpenAI, which have been lobbying the US government to restrict Chinese open-source models -- exploiting "national security" rhetoric to try to ban their main competitors.
Link: ft.com/content/418ca885-fbcf…


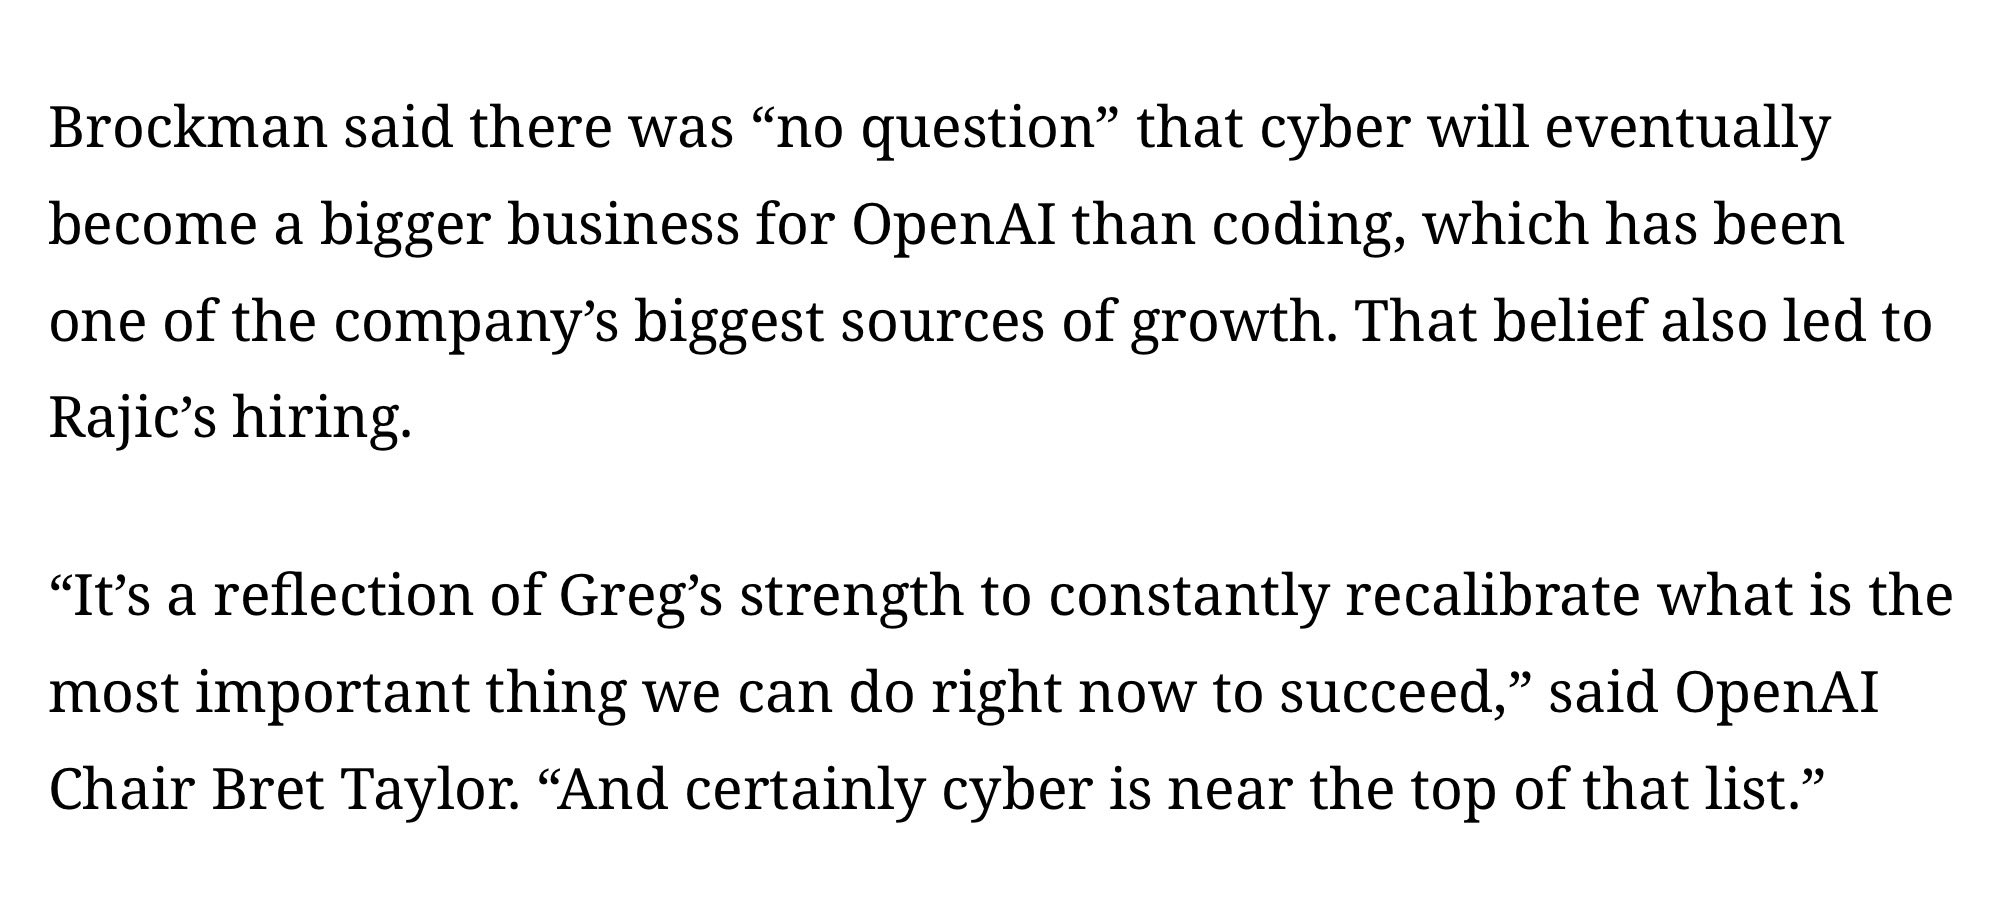
Yep. Been a long time coming. There is no time to wait. The time is now. You have to fight compute with compute. Cybersecurity has turned upside down and so much opportunity for swarm and intelligent first new companies
nitter.cf/edsim/status/208582992…


Hackers are now using LLMs to continuously scan software updates, spot newly fixed bugs, and build attacks before teams can apply the fix — all without human involvement. That’s according to the latest report from the Google Threat Intelligence Group.
We're helping defenders counter automated threats with Google AI Threat Defense, which combines Gemini and other frontier models to find and fix flaws before attackers can exploit them.
Along with some more recent thinking on cybersecurity defense factories
this week felt like sci-fi 👀 agents talking across isolated VMs through CPU cache timing, hardware bugs AI can exploit directly, lifelike voice models running on a laptop
is patching enough anymore? 🤔 sam altman doesn't think so, jason clinton says hold on for 18 months, matthew prince says years of sky-is-falling weeks
black october is real and we have to build the cyber defense factory sooner rather than later, agents running 24/7 and fighting compute with compute 🔥
Here's one take on what this could look like - notice that it will take a village to make this work! Lots of opportunity to build and reimagine and reinvent but the time was yesterday!
full post here: whatshot.vc/p/whats-in-aiinf…

1
205
Did a deeper dive back in August post Blackhat on my weekly newsletter
What's 🔥 #510 dropped - post Black Hat
🚨 The agent swarm future is already here. Most of cybersecurity doesn’t see it yet.
The OpenAI/Hugging Face incident made one thing clear: attackers will scale with tokens and compute. Defense must do the same.
Compute fighting compute 👇
Full post here: whatshot.vc/p/whats-in-aiinf…

1
86
Ed Sim retweeted
Nobody starts a company to negotiate the same SaaS contract for the 50th time. Common Paper's Cloud Service Agreement v3 is out.
10,000+ companies have signed on Common Paper, and these standards close hundreds of millions in deals every year. Less redlining, more closing


Ed Sim retweeted
Don't over-buy HBM, tier it. @netpreme's CTO showed that a separate memory tier for the KV cache delivered about 3x the batch size and 2.4x the peak decode throughput per GPU on GLM-5.3 at 128K context. Memory is the new inference bottleneck.
nitter.cf/netpreme/status/212149…

“Don’t Over-Buy HBM, Tier It!”
In our GLM-5.3 study at 128K context, the modeled memory tier supported ~3× the maximum batch size and 2.4× the peak decode throughput per GPU vs. the PCIe host-memory baseline.
Our Co-Founder & CTO Nikita Lazarev shared the study at SGLang Summit today.
HiSparse retains the full KV cache. A hot buffer stays in GPU HBM; the full cache can live in an external memory tier.
Full talk video Monday, November 16.
Thanks for having us, @sgl_project.
#SGLangSummit #LLMInference

ALT Nikita Lazarev presenting Netpreme's SGLang HiSparse case study at SGLang Summit 2026. The slide compares memory tiers for GLM-5.3 decode at 128K context and highlights the modeled 900 GB/s tier's roughly 3x maximum batch size and 2.4x peak throughput per GPU relative to PCIe host memory.


and more of this from everyone! nitter.cf/ClementDelangue/status…

We’re not going to win by lobbying, plotting, or manipulating. We’re going to win by building, in the open, with the whole community!
Today, with @ggerganov we’re super excited to announce the release of llama.cpp v1, the first major fully stable version of the most used library to run AI models locally, meaning on your phone, your laptop, and your workstation.
It means you can own your intelligence for free, not send your data to anyone and be 100% in control, wherever you are in the world. It shows our commitment to support every hardware, platform and model type out there and makes AI distributed rather than concentrated in a few Silicon Valley orgs.
Huge thanks to the team, the long-time maintainers and every contributor who helped make this happen. Let’s build! 💛🧡💚
2
435
LFG
We’re not going to win by lobbying, plotting, or manipulating. We’re going to win by building, in the open, with the whole community!
Today, with @ggerganov we’re super excited to announce the release of llama.cpp v1, the first major fully stable version of the most used library to run AI models locally, meaning on your phone, your laptop, and your workstation.
It means you can own your intelligence for free, not send your data to anyone and be 100% in control, wherever you are in the world. It shows our commitment to support every hardware, platform and model type out there and makes AI distributed rather than concentrated in a few Silicon Valley orgs.
Huge thanks to the team, the long-time maintainers and every contributor who helped make this happen. Let’s build! 💛🧡💚
cough😷, ahem AI
pivoting to cybersecurity, this is also why when you find thousands of vulnerabilities on your systems, you can't just AI patch all of them without deep understanding of the dependencies and downstream impact
what you shut down could be super important
the problem is that companies have negative time to even respond to vulns and sometimes may have to figure out where they automate and perhaps break a few things and havee more human intervention

no sign today's FAA ground stop was an attack, but it shows how fragile shared infrastructure is ✈️
technical failure, human error or attacker, the cascade looks the same 🤯
@securityscore mapped one airline and found 1,736 entities sharing its risk and all 8 DNS nameservers on a single provider…
what other nationwide infrastructure has this many dependencies?

When every flight in America is grounded, it’s more than an aviation problem. It’s a national security wake-up call.
Today’s nationwide FAA ground stop, reportedly triggered by air traffic control communications problems, demonstrates how dependent our economy is on interconnected critical infrastructure.
At SecurityScorecard, we recently published Shared Skies, a research report using Project Meridian to examine the digital ecosystem surrounding a major U.S. airline.
What we discovered was eye-opening:
1,736 entities shared vendors, networks, or cloud infrastructure with a single airline.
848 entities shared all three.
55% of the connected entities were healthcare organizations, demonstrating how infrastructure dependencies cross industry boundaries.
All 8 authoritative DNS nameservers for the airline’s primary domain relied on a single provider.
These findings don’t establish that those organizations would fail together, but they reveal concentrations of risk that traditional cybersecurity assessments can overlook.
There is currently no confirmed indication that today’s disruption was caused by a cyberattack. But whether the cause is a technical failure, human error, or malicious activity, the lesson is the same.
Cybersecurity is no longer just about protecting individual organizations. It’s about understanding dependencies, anticipating cascading failures, and building resilience across entire ecosystems.
We need to stop looking at critical infrastructure in isolation.
Our skies are shared. So are our risks.
