




I'm looking forward to being back in San Diego in May to teach SEC530! Hopefully I'll get a chance to see old friends and make new connections at the event [and maybe walk across the street to Kansas City Barbeque ;) ].
sans.org/cyber-security-trai…

This survey is set to close on 02/23. You still have a chance to provide input, and be eligible to win a $250 Amazon gift card. :) sans.org/u/1uu2

*Do You Know Where Your Data Is?* I'm participating with @SANS and @CrashPlan on a research project to gain insight into the amount and makeup of data that exists on user endpoints versus central data stores.
*Do You Know Where Your Data Is?* I'm participating with @SANS and @CrashPlan on a research project to gain insight into the amount and makeup of data that exists on user endpoints versus central data stores.
We are especially interested in strategies organizations are using (or have used) to protect against the loss of such data, whether through deletion or an unauthorized change to the original data.
If you have a few minutes please fill out the suvey at sans.org/u/1uu2 - I'd appreciate it, and you'll be eligible to win a $250 Amazon gift card for your time. 😁 #SANSResearch #EndpointSecuriy #Data
TIL - by accident when I fumbled on the keyboard: -CTRL+Shift+PGUP in Chrome, Edge, Visual Studio Code.
Game changer.
I'm looking forward to teaching #SEC530 Defensible Security Arch. and Engineering in Las Vegas! You can sign up at sans.org/u/1rFr, and learn the principles of #ZeroTrust to improve your org's prevention, detection, & response capabilities. 😃


That moment when you realize the person in line behind you is having a nervous breakdown because there’s three feet between you and the person in front of you, and you’re not closing the gap…
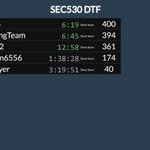
I had a great time last week teaching #SEC530 in Dubai, with an incredible class of engaged students! The Day 6 competition was awesome, ultimately with Team5 (Jans Thomas, Mohammed Aljohani, Abdulaziz ALHarbi, Abdulelah Al Sulais, Wilson Bunga) pulling ahead at the end! :)

I am proud to have a very small part in the CMS (Centers for Medicare and Medicaid Services) CyberVets program, assisting U.S. veterans with training for and finding jobs in federal cybersecurity. :)
linkedin.com/posts/centers-f…
Awesome! A perfect example of time-based security, in a thread that references physical security analogs to IT security. [for info on TBS see ‘Time Based Security’ by Winn Schwartau, ISBN 0962870048]

PSA: Implementing password complexity requirements like 'no repeated characters', 'cannot start with a number', 'no spaces', 'cannot end with a number', etc. do *not* improve security.
Finally, yes we want to use multifactor and there are use cases for passwordless authentication. But passwords are going to be around for a long time. Wherever we need passwords, let's try to be smarter about how we use them.