

🇮🇳 Hacker| CTF With Team:- @5h4d0wbr0k3r5 | Views are my own and do not represent those of my employers.
Your pc
Joined April 2021
- Tweets7.6K
- Following832
- Followers5.6K
- Likes64.2K





Pinned Tweet
I'm now part of the HTB Affiliate Program! 😊
If you use my link to buy any HTB subscription, I will earn a commission at no extra cost to you. If you prefer not to use the link, that's completely fine too.
Thank you for your support!
hacktheboxltd.sjv.io/Gmvygk
#infosec #htb
Hac retweeted

We're giving away a Hogwarts Legacy custom wrapped NVIDIA GeForce RTX 5090 to celebrate its official release with DLSS 5 🪄
To enter:
🟢 Share this post
🟢 Comment #RTXON
Terms and Conditions: nvidia.com/en-us/geforce/con…

Was checking my amazon history and last year I got a am4 motherboard and 32GB ram for 90$ usd WTFFFFFFFFFFF now the 32GB ram is going for 250USD fuckkkk
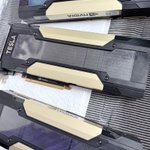
Currently testing the best way to cool my 3 v100 gpus. Also getting 2 more gpus in upcoming weeks. So need to adjust the designs. Will be sharing the files when I figure out the best design too cool multiple gpus.


My experience with @UPS india has been extremely shit. They have no proper communication channel and you have to call them each time to get things working. You guys have no proper way to pay for customs and get confirmation. I have to call your support team multiple time on my customs payment confirmation. Since it's all manual. And It's been almost 20 days and still haven't received my package. Won't be using UPS again. Fedex is much better when it comes to communication and dealing with customs.
A few months back I was distilling from bigger public models and got the older Qwen3.6 27B pretty close to Opus 4.8 on cyber stuff. Thinking of dropping some money on local AI hardware to work on Qwen4 27B when it drops.

A single pod is often enough to own the cluster and the cloud account behind it.
EKS IRSA, AKS Workload Identity, GKE Workload Identity. Same pattern: overprivileged service account annotation, then you are the cloud identity.
Container escape gets you the node. The annotation gets you the account.
pwnedlabs.io/blog/attacking-…
#Kubernetes #CloudSecurity #K8s #RedTeam

GCP privilege escalation is rarely an exploit.
It is an IAM chain. Low-priv identity → service account you can impersonate → project takeover.
The permissions that actually matter:
iam.serviceAccounts.getAccessToken
iam.serviceAccounts.actAs
resourcemanager.projects.setIamPolicy
Token Creator does not look like access. It is access to everything the target identity can reach.
Write-up: pwnedlabs.io/blog/gcp-privil…


I’m doing 15 days on Kubernetes for security people what you actually need to know to attack and defend a cluster.
Day 5 of 15.
Every pod has an ID card.
Most teams never look at it.
That card is a service account token.
Full article below.

“It’s in another namespace. We’re fine.”
That sentence is how attackers walk sideways in Kubernetes.
A namespace organizes names.
It is not a wall.

If your threat model is
“prod is a different namespace,”
you don’t have a threat model.
You have a naming convention.

