

AI Agency 老板|用一队 AI 员工帮中小企业省人、省时、多接单|每天分享真实项目里的 AI 用法,说人话|免费 AI 交流群 👇
Joined October 2017
- Tweets3.4K
- Following1.8K
- Followers40.3K
- Likes9.9K
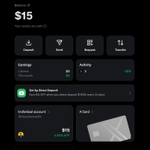




Holy fucking shit!

We believe voice is the most natural way to interact with intelligence, so we created Dessa, the most authentic full-duplex speech model ever built. Talking with it feels like talking with a person…full of emotion, nuance, pauses, and a natural cadence.
block.xyz/dessa


【全網最全】80分鐘搞定 Grok Bot!不用寫程式,打造24小時自動幫你打工的「AI 智能體軍團」!
1/ 我开了一家 AI Agency,团队很小,但我手下有一整队 AI 员工。分享一下它们每天都在干什么,你可以直接照抄 🧵
2/ 邮箱和日历助手:每天帮我整理邮件,先列出要处理的事,回信先写草稿给我看,我点头才发。
3/ 线索助手:自动从邮件里找出新的潜在客户,直接放进 ClickUp 的客户管理里,中间不用人转手。
4/ 会议总结助手:每场会议自动出总结和逐字稿,存档以后所有助手都能查,再也不用翻录音。
5/ 营销团队:一个 AI 当市场总监排内容,一个画师出图,一个剪辑助手做短视频。你现在看到的很多内容就是这样出来的。
6/ ClickUp 助手:建任务、分配、改状态全交给它,我只要说一句话。
7/ 最大的体会是:AI 不是替代人,是让一个小团队做出大公司的产出。关键不在工具,在于先想清楚哪些事值得交给它。
8/ 想知道怎么把这套用到你自己的生意里?进我的免费 AI 交流群,链接在主页 👆
youtu.be/8jkkCniMgBw

李哈利 Harry LΞΞ retweeted
MUST SEE: Amazing moment as President Trump calls Nvidia CEO Jensen Huang while he's on stage at the All-In Summit.
@POTUS on AI Doomerism: “I'm telling you, it's all a hoax… and we're not going to let that happen.”


李哈利 Harry LΞΞ retweeted

Claude Fable 5 will be available again globally tomorrow.
After a series of productive conversations with the US government, we're redeploying the model with a new set of classifiers to target and block more cybersecurity tasks. In the near term, some routine tasks like coding and debugging will fall back to Opus 4.8. We’ll continue to refine these classifiers over the coming weeks to reduce false positives and better distinguish genuine misuse from legitimate requests.
We’ve also begun drafting a consensus framework—with Amazon, Microsoft, Google, and other Glasswing partners—for assessing the severity of AI jailbreaks and how AI developers should respond to them. We invite other industry partners and model providers to join us in this effort.
Finally, we’re scaling up our collaboration with the US government on model testing and safeguards. This will include pre-release access to models and safeguards for evaluation, information sharing on jailbreaks and misuse, and dedicated resources for joint research.
Thank you to our users for your patience, and to our partners across the government, industry, and the research community who worked alongside us to make Fable 5 available again.
Read our full blog: anthropic.com/news/redeployi…

李哈利 Harry LΞΞ retweeted

A preview for Pro users: a new personal finance experience in ChatGPT.
Pro users in the U.S. can securely connect financial accounts, see where their money is going, and ask questions based on the information they choose to connect.
Your full financial picture, now in ChatGPT.
Wtf?!

The US government, citing national security authorities, has issued an export control directive to suspend all access to Fable 5 and Mythos 5 by any foreign national, whether inside or outside the United States, including foreign national Anthropic employees.
The net effect of this order is that we must abruptly disable Fable 5 and Mythos 5 for all our customers to ensure compliance.
Access to all other Claude models is not affected.
We apologize for this disruption to our customers. We believe this is a misunderstanding and are working to restore access as soon as possible.
Read our full statement: anthropic.com/news/fable-myt…


李哈利 Harry LΞΞ retweeted

This is a super exciting release - Claude Fable 5 is the same underlying model as Mythos but with added safeguards. The benchmarks are great and it's SOTA on everything by a margin but I'll add that *qualitatively* also, this is a major-version-bump-deserving step change forward (imo of the same order as Claude 4.5 was in November), peaking especially for long problem-solving sessions on very difficult problems. You can give it a lot more ambitious tasks than what you're used to, the model "gets it" and it will just go, and it's never felt this tempting to stop looking at the code at all (but don't do this in prod!). The model still has quirks that people will run into and the safeguards are configured to be a little too trigger happy for launch, which can hopefully be tuned over time.
I feel a lot of things changing as working software increasingly comes out on a tap. The Jevon's paradox kicks in and I feel my own demand for software growing substantially. You can ask for anything - explainers, visualizers, dashboards, bespoke single-use apps (e.g. a full wandb that is hyper-specific just for your project), you can 10X your test suite, auto-optimize code, run giant research projects with custom HTML for the results, anything! "Free your mind" (Matrix ref). Really looking forward to all the things people build!

Fable 5 is state-of-the-art on nearly all tested benchmarks, with exceptional performance in software engineering, knowledge work, scientific research, and vision.
The longer and more complex the task, the larger Fable 5’s lead over our other models.

ALT Benchmark table titled Mythos 5 & Fable 5, comparing Claude Mythos 5 and Fable 5 against Claude Mythos Preview, Claude Opus 4.8, GPT 5.5, and Gemini 3.1 Pro.
李哈利 Harry LΞΞ retweeted

73 product releases in 52 days. That's not a launch cadence — that's a different kind of company.
I tracked every Anthropic release from Feb 1 to Mar 23 by going through @bcherny, @trq212, @noahzweben, @felixrieseberg, @lydiahallie, @amorriscode, @feldman, @dickson_tsai, and @claudeai. Built a calendar with first-announcement attribution.
Look at the acceleration. February had bursts with gaps between them. March 9 onward is almost every single day — Code Review, Channels, Dispatch, Computer Use, back to back.
The individual features get coverage. The shipping velocity doesn't. It should.

李哈利 Harry LΞΞ retweeted
Software horror: litellm PyPI supply chain attack.
Simple `pip install litellm` was enough to exfiltrate SSH keys, AWS/GCP/Azure creds, Kubernetes configs, git credentials, env vars (all your API keys), shell history, crypto wallets, SSL private keys, CI/CD secrets, database passwords.
LiteLLM itself has 97 million downloads per month which is already terrible, but much worse, the contagion spreads to any project that depends on litellm. For example, if you did `pip install dspy` (which depended on litellm>=1.64.0), you'd also be pwnd. Same for any other large project that depended on litellm.
Afaict the poisoned version was up for only less than ~1 hour. The attack had a bug which led to its discovery - Callum McMahon was using an MCP plugin inside Cursor that pulled in litellm as a transitive dependency. When litellm 1.82.8 installed, their machine ran out of RAM and crashed. So if the attacker didn't vibe code this attack it could have been undetected for many days or weeks.
Supply chain attacks like this are basically the scariest thing imaginable in modern software. Every time you install any depedency you could be pulling in a poisoned package anywhere deep inside its entire depedency tree. This is especially risky with large projects that might have lots and lots of dependencies. The credentials that do get stolen in each attack can then be used to take over more accounts and compromise more packages.
Classical software engineering would have you believe that dependencies are good (we're building pyramids from bricks), but imo this has to be re-evaluated, and it's why I've been so growingly averse to them, preferring to use LLMs to "yoink" functionality when it's simple enough and possible.

