
Inaugural Dan Kaminsky Fellow | Security Researcher for the OSS Ecosystem | Speaker | Dropper of 0days (Responsibly) | @GitHub Star ⭐️ | Opinions=Mine | He/Him
Boston MA
Joined May 2010
- Tweets2.2K
- Following612
- Followers3.7K
- Likes14K




Pinned Tweet
This is my #ZeroDay #PublicDisclosure of a security vulnerability impacting 4+ Million of @zoom_us's users who have the Zoom Client installed on Mac.
Zoom had 90-days + two weeks to resolve this #vulnerability and failed to do so.
medium.com/@jonathan.leitsch…
Jonathan Leitschuh - [email protected] retweeted
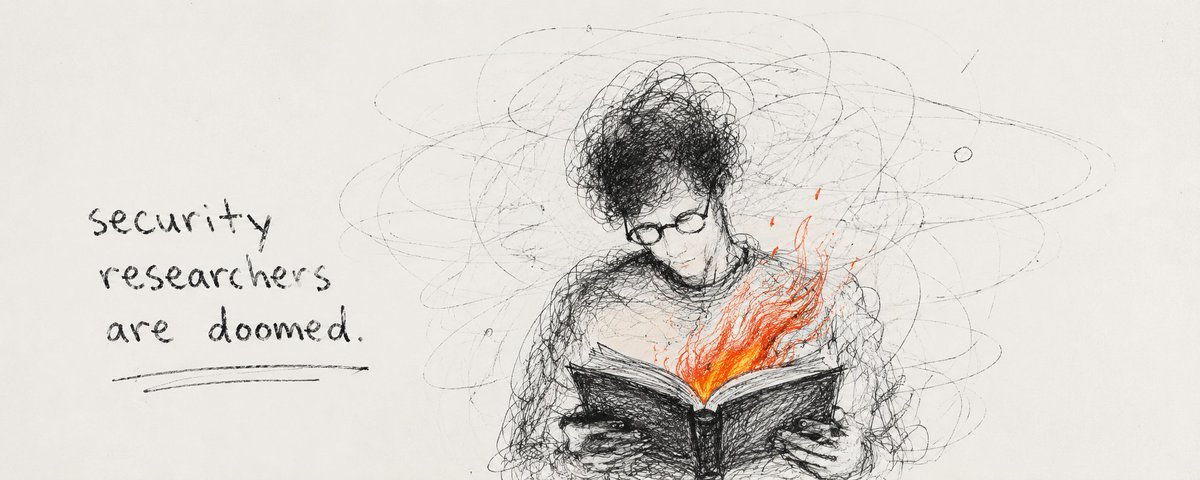
“Security researchers are doomed because of AI.”
I kept hearing versions of this, so I went back through 500 years of people saying the same thing every time a machine learned a human skill.
Some were idiots.
Some were right.
Here’s where I landed.
Jonathan Leitschuh - [email protected] retweeted

This was a great read,
Stellar work @0xLupin

Jonathan Leitschuh - [email protected] retweeted

I had a $400 Wagyu ribeye for lunch today.
I didn't pay for it.
An enterprise account executive from a tier 1 cybersecurity firm paid for it.
He's been trying to sell me a cloud-native endpoint detection platform for 8 months.
We don't need a cloud-native endpoint detection platform.
We don't even have endpoints.
Half of our workforce is using refurbished laptops from 2014 that are physically incapable of running his software.
But I told him we're "evaluating"
That phrase means absolutely nothing.
But in B2B sales, it's the equivalent of ringing a dinner bell.
He's bought me 8 lunches this year.
He asks about our migration timeline.
I stare out the window, sigh deeply, and whisper about decentralized integration bottlenecks.
He furiously takes notes and orders another bottle of sparkling water.
My total compensation package is $200K.
But my caloric ROI is incalculable.
Next week I have a pitch meeting with an AI analytics startup.
I checked their Series B funding round before agreeing to the meeting.
They have $40M in venture capital burning a hole in their pocket.
I'm going to let them buy me omakase.
Then I'm going to tell them our legacy infrastructure is experiencing packet loss and we can't deploy until 2029.
Corporate America is just a vast ecosystem of free meals if you know how to string along desperate account managers.
Jonathan Leitschuh - [email protected] retweeted

I tried the government's new AI "Jobcentre in your pocket" chatbot. Could it write me a CV? It could.
It also suggested that I should consider employment law and whether I've been discriminated against.
Key detail: I'm a parrot.

I'll be discussing *MCPwned* hacking local MCP Servers with browser-based DNS Rebinding during today's #ThursDef with @Recon_InfoSec !
Come hang out at today's fireside chat @ 1:30 PM ET/12:30 PM CT! You won't want to miss this!
Register now - thursdef.com

I found a travel app leaking exact user locations and birthdays via its internal API.
We could pinpoint where people were living and sleeping.
Full write-up 👇
medium.com/bugbountywriteup/…

Jonathan Leitschuh - [email protected] retweeted

BREAKING: MongoDB Introduces Surprise Holiday Feature
FOR IMMEDIATE RELEASE
PALO ALTO, CA — MongoDB is thrilled to announce MongoBleed™, an innovative new feature that proactively shares your database contents with the broader internet community.
"For years, customers asked us: 'How can we make our sensitive data more accessible?'" said a spokesperson we definitely didn't make up. "MongoBleed answers that call. No authentication required. No consent needed. Just pure, frictionless data liberation."
Key Features:
- Zero-Click Sharing: Your passwords share themselves!
- Decade of Trust: We've been quietly beta-testing this since 2015
- Holiday Launch: Because nothing says "Merry Christmas" like your production secrets on GitHub
- Elastic Integration: Built by someone who definitely understood the assignment
Customer Testimonial:
"I was enjoying Christmas dinner when I got paged. My database was sharing our user credentials with the world. It really brought the family together—around my laptop, watching me cry." — Definitely a real IT admin
What's Next?
We're excited to announce our 2026 roadmap includes:
- Automatic password broadcasting to Shodan
- AI-powered secret harvesting (we're pivoting to AI!)
- A Slack integration that just posts your .env files directly to #general
About MongoDB:
MongoDB is the database that believes data wants to be free. Very, very free.
doublepulsar.com/merry-chris…

Anyone have a security contact at @SandboxVR? A friend found a rather large data leak. They've reported it and the company has been, as of yesterday, unresponsive.
.@msftsecresponse published probably one of the most opaque CVE descriptions I've seen: "Improper verification of cryptographic signature in GitHub allows an unauthorized attacker to perform spoofing over an adjacent network."
Like... What is that even supposed to mean?! 🧵

As a result, downstream consumers are just going to continue to get bad CVE data for MSFT vulnerabilities, as demonstrated in this case.
I've included a link to a detailed disclosure of this vulnerability here 👉 github.com/JLLeitschuh/secur…

I may have found an SSRF vulnerability in @TheASF project 'Cloudstack'. Anyone interested in helping me confirm, DM me
Jonathan Leitschuh - [email protected] retweeted

⚠️ Google’s OSV just added 500+ new advisories, not from new vulns, but from fixing a long-standing policy that made disputed CVEs invisible.
Learn more → socket.dev/blog/google-osv-f…


