

Bug Bounty Hunter
Montréal, Québec
Joined June 2016
- Tweets770
- Following507
- Followers9.8K
- Likes6.9K





Submitted my very first bug to @GoogleVRP today and it got accepted and upgraded 💪


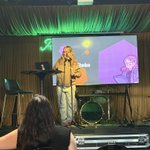
And now it’s my turn listening to @InsiderPhD explaining the basics of recon!


Listening to @JR0ch17 explain the basics of bug bounty hunting at @Hacker0x01’s Glass Firewall event in Austin ✍️✍️

Jasmin Landry retweeted

Last chance to register for #GlassFirewall 2025 happening Oct. 23 in Austin, TX!
Hosted by @CapitalOne + @github + @Hacker0x01
Agenda updates:
-Foundations of Bug Bounty w/ @JR0ch17
-Recon 101 w/ @InsiderPhD
-Intro to Burp Suite w/ Aurielle Catron
-Hardware Hacking w/ Catherine Cassell
-Career Panel ft. leaders from HackerOne, Shopify, and more.
🔗 Register now for this free event: bit.ly/4nDvqdM
#GlassFirewall #WomenInSecurity #Cybersecurity #TogetherWeHitHarder

Jasmin Landry retweeted

Don’t miss the Platform Panel about Triage with:
Michelle Lopez (@Hacker0x01)
Michael Skelton (@codingo_, @Bugcrowd)
Inti De Ceukelaire (@securinti, @Intigriti)
Eddie Rios (@Synack)
Anthony Silva (@YesWeHack)
Moderator: Jasmin Landry (@JR0ch17)
📅 Saturday, August 9 at 3:00 PM
Really excited to be giving a talk at @BugBountyDEFCON this year! Looking forward to seeing everybody there!

We’re excited to announce that Jasmin Landry (@JR0ch17) will be speaking at the Bug Bounty Village at DEF CON 33!
Stay tuned for more details on their talk, you won’t want to miss it.
#BugBounty #DEFCON #BBV #BugBountyVillage
Jasmin Landry retweeted
In this episode, @JR0ch17 breaks down how he consistently lands highs and crits - from SSRFs to less common bugs like XXEs and SQLis. Enjoy🔥
youtu.be/0-o3_NumvbI

Jasmin Landry retweeted

Day 2 is packed with some 🔥 talks! Check out the entire schedule on NahamCon.com! Remember this is 100% free, no tickets or anything needed. Just show up and watch the talks!

Jasmin Landry retweeted

I'm giving a workshop on @CaidoIO at
@NorthSec_io in Montreal next week!
Be sure to check it out if you're in town!


Jasmin Landry retweeted
New video out with @JR0ch17!
We break down an SSRF bypass against a validation pattern you’ll definitely see again — and show how to land critical without cloud metadata. Enjoy🔥
youtu.be/uoKMhb6juSo
Jasmin Landry retweeted

.@CaidoIO and @Hacker0x01 are collaborating on a plugin that streamlines the H1 submission process. We’re envisioning a plugin that gives a simple UI to combine evidence that serves as the foundation of a report and removes most of the writing burden. Link in the comments.
Really a fun bug to work on! Here’s what our day looked like 😂


Wowww! I found a sick bug for my first day full time hacking. 😱
Aptly, it includes prompt injection:
CSRF -> Path Traversal -> access to internal chatbot -> HPP -> prompt injection -> AI outputs XSS which pops on the victim.
Shoutout to @JR0ch17 for the collab!
116 total reports, including 19 criticals! Let’s hope those numbers improve in 2025 as I’ll be doing bug bounty full time!
hackerone.com/stories-of-202…
@Rhynorater looks like I’ll be roaming around in the savanna with you 🦁


🔥 Looking forward to next round! 🇨🇦#TeamCanada

🇨🇦 GO CANADA 🇨🇦! We’ve made it to the Sweet Sixteen in #AWC2024! 🎉🍁 A huge shoutout to @Hacker0x01 for this amazing event! Good job team and let’s keep the momentum going 🏆🚀 #TeamCanada #BugBounty

1
23
2,877
Jasmin Landry retweeted
"What keeps me on programs is the interaction with the people. Good communication, access to unique scopes, setting campaigns with increased payment for findings, getting a real person on reports rather than a bot." Hacker @JR0ch17 chatted with #SecurityAt attendees on some fundamental elements that drive security researchers to programs on the HackerOne platform.

This made me remember an ATO bug I found a few years ago. The app used perl's crypt function as the token generator for password resets, here's the docs for it perldoc.perl.org/functions/c…. You'll quickly notice the problem with it 😂
Or I guess the real problem was that the app was built on perl!

Just discovered "Reset Tolkien" , a shiny new tool from @AethliosIK for cracking time-based secret tokens with the sandwich attack. Random-looking tokens can contain so many flaws, it's great to see more eyes on this area.
aeth.cc/public/Article-Reset…