

The most secure, modular hardware wallet for your crypto. One shell, many keycards. Join our community: https://nitter.cf/t.co/pMHQxid209
Switzerland
Joined January 2019
- Tweets1.5K
- Following342
- Followers4.3K
- Likes2.9K





Keycard Shell retweeted

Privacy is a collective defence.
In my interview with @dif_fractions, we talk @Logos_network's Basecamp, the browser as stage zero of deanonymisation, @Keycard_ , the vanishing endpoint and why metadata resistance has to be architectural.
Live now:
diffractionscollective.com/2…

Keycard Shell retweeted
little know fact: shieldsigner includes @keycard_ support


Keycard Shell retweeted

Tangem is not a hardware wallet (it doesn't bring more security than a mobile phone) and all cards are at risk see donjon.ledger.com/blog/bypas… - if you like the form factor check out @Keycard_ or @satochip

Keycard Shell retweeted

🔥 I ranked 21 Bitcoin signers.
5 years in the shadows: testing hardware wallets, watching Bitcoin Twitter, following every hack, every bug, every vendor drama.
This is where I landed, & some of you won't like it.
My criteria:
🔓 Open code you can verify
📵 Air-gap: QR or microSD over USB, Bluetooth or NFC
🧱 Security model: secure element, stateless or smartcard
📜 Track record, and how the vendor reacts when things break
🔁 Standard backups (BIP39, PSBT, descriptors): no lock-in
🟥 S TIER
Open code, minimal trust in a vendor, and for most of them you can build or flash it yourself. The less you have to trust, the higher it goes.
🟧 A TIER
Serious, Bitcoin-focused tools. You trust the vendor more than in S, and you get polish in return. Yes, Coldcard stays in A after July's entropy bug. The transparent fix and migration guide count too.
🟨 B TIER
Good tools, each with a trade-off: a server in the security model, a newer approach still proving itself, a phone in the loop, or multi-coin roots.
🟩 C TIER
Multi-coin first, Bitcoin second.
⬜ D TIER
Closed code, or recovery models where a company holds part of the keys to your castle.
Now the twist: no signer is the best in the absolute. The right one depends on YOUR threat model. A ranking expires. A method doesn't.
That's the whole idea behind chapter 23 of Bitcoin Hodler: Choosing Your Signer. 📖
Where would you move one device? 👇

ALT https://kavsec.agency
Keycard Shell retweeted

Mis primeras impresiones de @Keycard_ 👇
Antes un resumen de porque la elegí:
• Es una mezcla de @Tangem y @KeystoneWallet
• Firmás con NFC o con QR
• Con QR ves en la pantalla del Shell lo que estás firmando
• La wallet de la tarjeta la podés borrar y generar otra, cada una te da su seed
• Todo open source
Existen más cosas, que no dejan de ser importante, pero no quería hacer un post muy largo, vayan a visitar su web 😉
Wallet con las cuales pueden usarla:
• Para redes EVM pueden usarla junto a @ambire, con QR en la extensión y NFC/QR en el celular, realmente el uso en muy fluido. Existen más opciones por ejemplo @Rabby_io, pero solo es con QR.
• Para BTC @SparrowWallet / @bluewalletio son opciones, pero existen más, en todas es solo con QR
Posibilidades:
• Una wallet diaria que pueden usar con Ambire por NFC
• Una wallet con fondos para hold para usar solo QR, viendo que se firma gracias al Shell
• Firmante de una @safe
Para mí es una muy buena opción, pero por supuesto nunca dejen de hacer ustedes su propia investigación, cualquier cosa preguntan 🫡

Keycard Shell retweeted

Your Nostr key, on a @Keycard_.
keycard-nostr-bunker is a NIP-46 bunker: clients connect over relays, the card signs and decrypts. The key never leaves it.
pipx install keycard-nostr-bunker
github.com/mmlado/keycard-no…
#nostr #NIP46 #Keycard #selfcustody #hardwarewallet #opensource

Keycard Shell retweeted

Keycard Shell Review 2026 – Modular Air-Gapped Hardware Wallet
youtube.com/watch?v=uQrKg-sW…
#Keycard #Coldwallet #Cryptowallet @Keycard_

Keycard Shell retweeted

Keycard Shell 1.4.0 firmware: reproducible ✅
We rebuilt it from source. The firmware matches apart from its signature, and this release's newly published bootloader matches byte for byte once its key field is copied in.
Congrats @Keycard_ @WalletScrutiny
walletscrutiny.com/hardware/…

Keycard Shell retweeted

Or just move to something that's already transparent and open source - @Keycard_

Keycard Shell retweeted

Keycard is a huge underdog!
- Overall works great, very easy, simple, self-explanatory
- Solid build quality
- Interchangeable secure elements (cards)
- Super open wrt software and hardware & schematics even..
- Cheap!
Recommended!
Product link in comment

if there’s an extra component inside your hardware wallet, what reference do you have to spot it?
with Keycard Shell, you have a published reference for what should be inside
Firmware. Circuit schematics. PCB layouts. Component lists. Case designs.
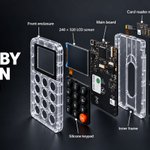
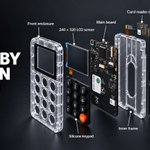
here’s the hardware behind it:
• main board with STM32H573 (ARM Cortex-M33) microcontroller (PSA Level 3 / SESIP3 certified)
• 240×320 TFT IPS color LCD screen
• heavy-duty silicone keypad (numeric + OK/C)
• ISO 7816 smartcard reader module (contact only)
• CMOS global-shutter camera for QR codes
• replaceable Nokia BL-4C 800 mAh battery
• clear ABS case, with public 3D design files so you can print your own
the clear case lets you see parts of the board without taking the device apart
the back cover slides off without tools to access and replace the battery

Keycard Shell retweeted

Another key benefit of @Keycard_ it’s a clear case. So easy to double check the insides
Keycard Shell retweeted

Mobile app supports @Keycard_ NFC signing.
Just tap your Keycard to your phone and complete transactions on the go.
Keycard Shell retweeted

Safe is making it easier and more secure to use with @safe Pro
Start a project with your email and upgrade ownership as you grow with more people and adding fully owned software and device account signers like @ambire and @Keycard_
• See all accounts in 1 Workspace
• Safenet transaction tx verification network as a security layer
• As simple or customized as needed
I'm most looking forward to a version of Safe Pro for individuals with multiple accounts that has features like gasless txs, Safenet, and access controls

Safe Pro is live: the most professional way to self-custody.
If self-custody has become critical for your team, @Safe Pro was built for you.
❇️ Oversee all your Safe accounts in one Workspace
❇️ Monitor transactions continuously with Security Hub
❇️ Implement policy controls on every transaction.
Your assets never leave your custody.
Check out our new website and get Safe Pro now: safe.global/pro


Keycard Shell retweeted

This is the feature that actually stops people getting rekt.
Sync extension and mobile without copy-pasting your seed phrase or private key.
It will be available on @ambire 🔥

Keycard Shell retweeted
LFG. Full @Keycard_ → OpenPGP → @ThurinLabs → Ethereum demo.
OpenPGP signs the identity statement. Ethereum signs the EIP-712 authorization. Everything moves over QR, both proofs verify on the host, and neither private key leaves the card.
Hardware-backed identity is real.
Keycard Shell retweeted

... oh oh...
they actually made the @ambire experience on mobile...
and it's actually just as good as the browser extension...
and the @Keycard_ tap integration *is* as good as advertised...
there is absolutely no reason to suggest to newbies anything other than the keycard shell + ambire as the new onchain meta