
Lokke Moerel retweeted

The ECJ's AG has concluded that compensation under Art 82 GDPR requires that an individual has suffered actual damages - the mere infringement is in itself insufficient, and the mere upset an individual may feel is also insufficient. Read more: https://nitter.cf/t.co/jrsdMX4Nd6 #GDPR
Lokke Moerel retweeted

Uitstekende analyse van @lmoerel over Schrems II.
mofo.com/resources/insights/…
Laten we stoppen met de framing dat transfers naar clouds en derde landen per definitie een security risk zijn. Want dat staat juist oplossingen voor markt-dominantie en de soevereiniteitskwestie in de weg

Lokke Moerel retweeted
Brussels Court of Appeal refers preliminary questions to the ECJ before ruling on IAB Europe's appeal against the Belgian DPA's decision on their processing of personal data under the Transparency and Consent Framework. #dataprivacy #GDPR IAB Europe case: dataprotectionauthority.be/c…
Lokke Moerel retweeted

Great tips post-Dobbs.

MoFo compiled a digital handbook for individuals, #familyplanning clinics, and #tech companies navigating a post-#Dobbs world: https://nitter.cf/t.co/B7sVR3OC81
Lokke Moerel retweeted
The #EDPB has adopted a statement regarding data transfers to #Russia, which states that due to the lack of #EU recognition or an adequacy decision, transfers can only occur "using one of the other transfer instruments provided for in Chapter V.”
edpb.europa.eu/system/files/…
Lokke Moerel retweeted
The Latvian #DPA issued guidance for financial institutions on processing #AntiMoneyLaundering data. #AML. The Global Data Review article can be found here: globaldatareview.com/article…


Lokke Moerel retweeted
The #EDPB published its #guidelines on the calculation of #fines under the #GDPR.
edpb.europa.eu/our-work-tool…
#dataprotection #dataprivacy
Lokke Moerel retweeted
Check out this joint cyber advisory that provides some great insight into the common security weaknesses observed in cyber incidents and ways to mitigate them: cisa.gov/uscert/ncas/alerts/…
Lokke Moerel retweeted
The #CNIL released its criteria for evaluating the legal use of #cookie walls. #GDPR #dataprotection #dataprivacy
cnil.fr/fr/cookies-et-autres…
Lokke Moerel retweeted
This weekend, a New York Act went into effect which now requires employers to provide prior notice of the electronic monitoring of their employees. #NY #workplace #privacy
Read up on SB 2628 here: nysenate.gov/legislation/bil…

Lokke Moerel retweeted
India has updated its Computer Emergency Response Team (CERT) rules to require reporting within 6 hours.
cert-in.org.in/PDF/CERT-In_D…
#cybersecurity
Lokke Moerel retweeted
The UK government is soliciting feedback from the tech industry on its proposal to enhance app security and privacy by introducing a voluntary Code of Practice for app store operators and developers.
gov.uk/government/news/tough…
#UK #privacy #appsecurity

Lokke Moerel retweeted
The Int'l Organization for Standardization (ISO) has released its final standard addressing organizations' use of AI. The U.S. is also paying more attention to this topic, as evidenced by the Dept. of Commerce's recent appointment of 27 experts to the Nat'l AI Advisory Committee.
Lokke Moerel retweeted

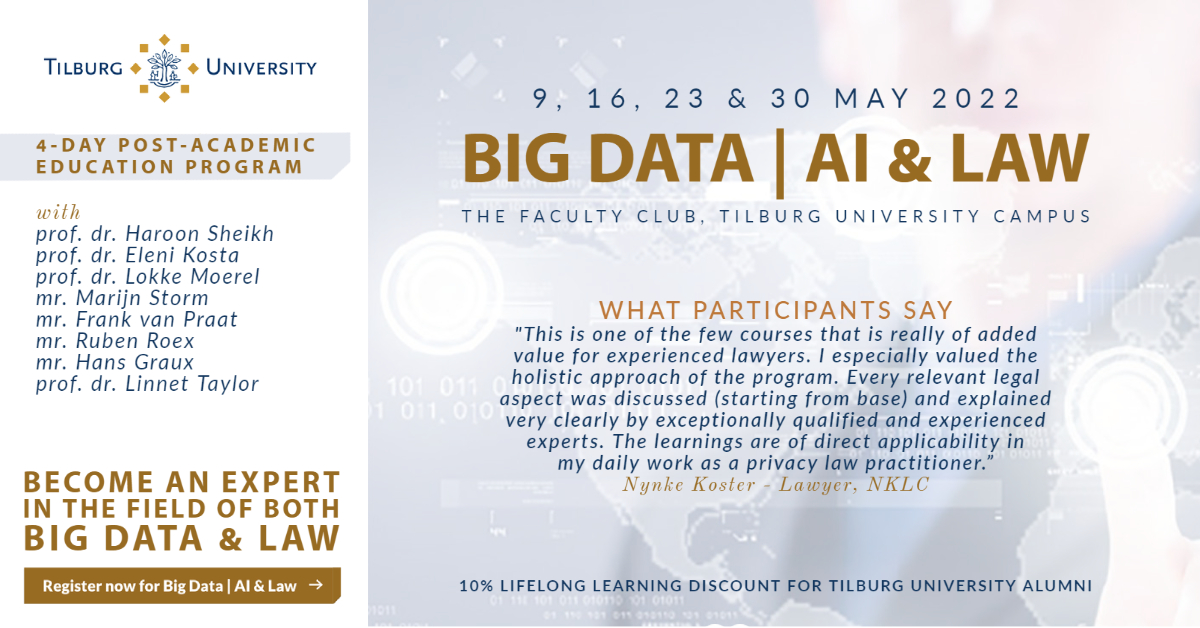
There's still time to register for our unique post-academic course "Big Data | AI & Law" in May. Taught by top professors & practitioners, the program is a valuable opportunity for legal professionals, regulators & others interested in big data & law.
👉lnkd.in/g5WxfMf👈


Lokke Moerel retweeted
MoFo's @aiftimie spoke with @CBSNews about Biden's warning of Russian #cyber #threats to U.S. critical infrastructure.
cbsn.ws/3ttUxX6

Lokke Moerel retweeted
The California AG has clarified that the California Consumer Privacy Act gives individuals the right to know the inferences that a business generates internally about them, unless the business establishes that the inferences are protected trade secrets.
oag.ca.gov/system/files/opin…
Lokke Moerel retweeted
Critical infrastructure entities in the United States will face new #cyberincident reporting requirements as a result of the Cyber Incident Reporting for Critical Infrastructure Act of 2022, enacted by the U.S. Congress on March 10, 2022. Read more: https://nitter.cf/t.co/Pz04gPoIMu
