

Security Researcher | EVM - Solana - Stellar - Starknet - Zk - Maths - Stats - AI tg : LordAlive
Joined December 2024
- Tweets37
- Following99
- Followers203
- Likes301
Pinned Tweet
🏆 1st place in @SiloFinance contest on @cantinaxyz
Competed as @cutthroat_sec with @ParthMandale & @0xAbhay_Eth . Spent almost a week on this Audit. The competition was fierce and all given their best.
Special thanks to my brother @0xVijayReddy for always having my back 🚀.

Look what we got here 👀

The slow part of fuzzing a Solana program is everything around the fuzzer.
Our new open-source skill hands that to your agent: plan the campaign, build the Crucible harness, run it, triage the results.
Built on @asymmetric_re's Crucible. MIT.
github.com/CODESPECT-securit…

5
180
Our @CODESPECT chads were behind the scenes working on this one 🫡
Always great to see the team contributing to building and securing the next generation of Web3.
Show some love and support the work by contributing to the DAO fund. Every bit helps! 🔥

Before you hand your capital to a DeFi agent, you should know if it’s trusted.
That’s why we co-developed the Trust & Security Framework for agentic DeFi with @CODESPECT.
Now we’re taking it further with @CODESPECT and @AtlasYield: the framework is up for a grant on @thedaofund to go open source and fully automated.
Support the proposal and help us make agent trust a public good.
Link in the comments below👇

ALT Help us secure the future of agentic finance. Back our Trust and Security Assessment Framework: an open standard that shows which DeFi agents are safe to use. Built with Codespect & AtlasYield. To qualify: $9,649 to go until the initiative qualifies for TheDAO’s vote. Ethereum mainnet · ETH, USDC, USDT, DAI & more. Donate at initiatives.thedao.fund.
Everyone who's moving from EVM/SVM to @CantonNetwork
here is a Technical writeup.
hackmd.io/7SuG6TztQqiNwJXw75…
#CantonResearch #CantonNetwork #CantonSecurity

LordAlive retweeted

Glad to support Telescope ahead of launch with our AI auditor tool, SpecSabre.
It looks at the code from a different angle, helping Telescope strengthen the operation of their protocol and uncover special edge cases that could arise.

Another layer of security review for Telescope.
@CODESPECT has completed an AI-assisted review of our smart contracts, adding another layer of scrutiny alongside our Quantstamp audit.
We're taking every step to strengthen the protocol before launch.
More soon.

You'll never come across a deal like this again !! Grab it fast.

Just leaving something here for Soroban builders to check
Btw we still have one free slot for our AI harness run. So, if you would like to get your codebase tested on us.
We run the scan, triage it and give you only proper findings, no noise.
51
LordAlive retweeted

@0xRajkumar and me will be giving a talk at @summit_defi . Excited to break down Web3 security monitoring internals from chain data pipelines to real-time incident response. See you all in Mumbai!

Sabanaku77 joins @0xRajkumar on the DSS 2026 agenda.
“Web3 Security Monitoring System Internals: From Chain Data to Incident Response”
Explore the joint talk and add it to My agenda:
defisecuritysummit.org/2026/…
Tickets: luma.com/9qtxqqxx

ALT DSS 2026 speaker announcement card for Sabanaku77: Web3 Security Monitoring System Internals: From Chain Data to Incident Response
A must read 📚
Institutional real-world asset platforms need security review that reflects how they will operate in practice. We worked with @ChainLabCTU (@CVUTFEL) on an institutional RWA platform for tokenised bonds supporting SME financing on EBSI.
The scope covered two Solidity codebases across bond lifecycle logic, identity controls, custody, account abstraction, recovery, and WebAuthn validation. The engagement combined a private CODESPECT review with a SpecSiege community audit contest.
The case study explains how the two review layers supported broader coverage and helped prepare institutional RWA infrastructure for production. The link to the case study is in the reply ⏬

3
68
LordAlive retweeted
The Final Audit Report for our work with @ChainLabCTU is now publicly available.
The assessment covered institutional RWA infrastructure for tokenised bond financing on EBSI, including an ERC-6909 bond platform and an ERC-7579 account-abstraction layer.
Across two Solidity codebases, 7,256 nSLOC, the report records 71 findings:
🪲38 from the private CODESPECT review
🐛33 from SpecSiege.
A notable high-severity finding affected WebAuthn validation and could have allowed a previously observed assertion to authorise an unintended operation. The issue was fixed and the remediation verified. ⏬
LordAlive retweeted
Options protocols rarely fail in one function. They fail when claims, collateral, expiry, vault accounting, hedging, and liquidation stop describing the same obligation.
Our new article covers 8 vulnerability classes and the invariants that catch them.

LordAlive retweeted
1/4
LLM input filters have an architectural weakness.
They must operate faster and more cheaply than the models they protect. This creates a resource gap that can be exploited to bypass safety controls.
⏬⏬⏬
#AISecurity #LLMSecurity

LordAlive retweeted

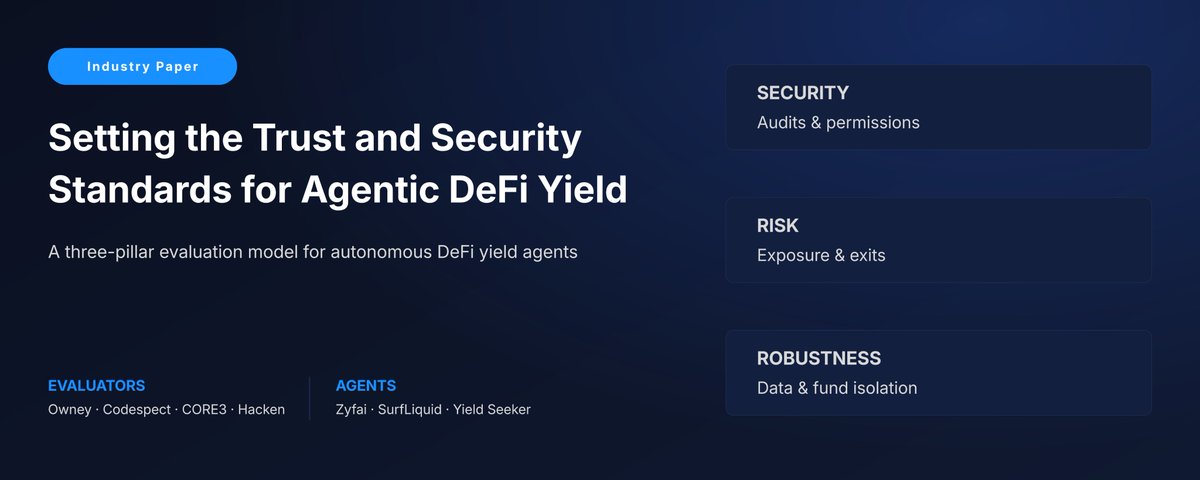
How should we assess the security of DeFi agents?
A framework for the proper review of agentic DeFi was created by @owneydotapp, @CODESPECT, @Core3io and @hackenclub
We are excited to share that we've just released our Trust and Security framework for Agentic DeFi, developed together with CODESPECT, CORE3, and Hacken.
Check out the agent scores on risk.owney.app/ and read the full article here!

LordAlive retweeted
🛡️ SpecSiege (audit contest) is a wrap.
A web3 security community cohort of 50 researchers put @ChainLabCTU`s ERC-6909 bond platform through the wringer, and the results are in.
📊 30 unique valid findings
• 6 Mediums
• 24 Lows
💰 €15,000 in total rewards:
• €13,000 medium pot, fully distributed
• €2,000 lead auditor reward
Congrats to our top 3 👇
🥇 @heavyw8t_ → €3,901.76
🥈 @Huntoor → €1,939.94
🥉 @brandon_shi → €1,821.80
🧵
LordAlive retweeted
The 50 accepted participants for SpecSiege have just been emailed. A strong applicant pool, and an honour to have this group on board.
If you didn't get that email today, hold tight. We had more strong candidates than slots, and we're holding the "not this time" emails until the 50 confirms, that way anyone who'd be next in line moves up from a real waitlist instead of getting a rejection we'd want to walk back. Either way, you'll hear from us.
Thank you for applying.
LordAlive retweeted
Registrations for SpecSiege, the ERC-6909 Bond Platform audit contest, are open until the end of the month (31 May 2026).
Then we'll close registration and choose the group of researchers. We're already amazed by the number of applications, so we'll definitely make the group bigger than we originally planned.
Great to see the community this thrilled. We're still polishing the rules to make the experience as smooth as possible for security researchers. That said, the competition will still be a challenge: the project goes through a full audit with CODESPECT first.
We're open to suggestions, so feel free to message us on X or reach out to @talfao1 directly.
We're really looking forward to kicking this off well!
Researchers who are waiting for the right contest, this is a golden opportunity 🔥. Registrations are now open. Come find bugs and get paid.
As promised. Today, we have a big announcement
We're launching registration for SpecSiege.
It's our double-check format for audits. First, an internal private audit went through the code with a full manual review. Then the community review follows. 10 days of open review on a fairly large codebase, we know, but the chance to work on an ERC-6909 European bond platform, an institutional project, doesn't come around every day.
- €15K total pot (€13K community pool, €2K fixed for the lead researcher).
- If only Lows are discovered, €5K is distributed instead.
Simply find bugs after us and get rewarded. We value your participation. We're not here just to squeeze you.
Link below ⬇️

LordAlive retweeted
CODESPECT is coming to @EthPrague. As a Czech-based company, this is one we never miss.
Last year was great and we're looking forward to another round of amazing talks and catch-ups.
If you want to talk about web3 or web2 security, reach out to @talfao1, @jecikpo, or @w3theo who will be around. Come say hi.

LordAlive retweeted
CODESPECT is proud to support @Solbuildersclub.
We've agreed to provide special perks for community members. If you're part of SBC, you can reach out to us for discounted security services, security guidance, and a free initial consultation on the security behind your project.
Supporting builder communities is core to what we do. @solana is a great example of how strong communities ship great products.
Members can DM us or reach out through the club to get started.
