

Microsoft MVP '09-Present. We design & build HA solutions for on-premises, data centre, & hybrid. Workload Migration Specialists. Active Directory Security.
Alberta, Canada
Joined August 2011
- Tweets10.9K
- Following430
- Followers2.8K
- Likes2K
Pinned Tweet
ACTIVE DIRECTORY SECURITY: REMOTE MANAGEMENT ACCESS METHOD
For remote management we do the following:
1: Not allow all Domain/Enterprise Admins from the Internet via no membership (RD Gateway Group)
2: 2FA on ALL Servers that can accept it (DUO)
3: Domain User Account in RD Gateway Group
4: Above User has Remote Desktop Access local on the Jump Server _only_
5: User has to right click and Run As Admin on RSATs
6: RD Gateway _only_ for remote access
7: DUO for RD Gateway in place
*** This kills virtually ALL remote user based attack vectors especially VPN ***
DUO is set up to prompt on the RD Gateway. Internal resources also have the DUO RDP/Windows Logon setup configured to prompt for 3-5 numbers on the user's mobile via the DUO app.
Repeat after me:
- VPN is evil.
- VPN is a yuge hole in the security perimeter
- VPN Vendors _have been compromised_
Show me one RD Gateway compromise since it was delivered in Windows Server 2008 RTM.


REMOTE DESKTOP GATEWAY & WEB SECURITY
We have a few sites with it in place because our contractor or client requested it to be there.
GEO-BLOCKING
A lot of the geo-blocking type stuff can be done at the edge.
But, "VPN" providers basically eliminate that protection.
SERVER NAME INDICATION
- RD Web Security in IIS
-- BINDING:
-- Set URI: Remote.MyDomain[.]Com
-- ENABLE SNI (Server Name Indication)
That eliminates the slow roll authentication attempts that mostly come from 45. IP addresses.
DUO on RD Gateway catches all inbound authentication.
UPN PROTECTION STEP
A simple rule of thumb: Don't use [email protected] UPN as an allowed logon!
Why? Users are bound to use their e-mail address and in some cases their one and only password used everywhere else!

This is a wheel stud.
This is a smoothly twisted off broken stud.
With the right tools swapping it took about an hour.
Money saved: $450-$600 to R&R the passenger rear brake gear to get to the hub.
Part cost: $5
2006 Cadillac DeVille DTS.
Happy daughter & son-inlaw.
EDIT: Oh, I forgot: 1-2 days without the car.
Rental would be $125 or so.
Time lost to the whole thing: 8 hours all in to muck about dropping off,.picking up, and the rental.
$150/Hour = $1,200
That's time away from their young family. That's priceless. ;-)

User Outlook Classic. The real app.
What you are using is like a RemoteApp hosted out there somewhere.
You have given the Mothership your credentials.
All your base are belong to us.

So i started using the Surface Laptop Ultra at GitHub Universe. And its good.
But I am independent, and I will always speak my mind.
I switched from a Mac and set up Outlook accordingly. And what I discovered is:
Outlook has ads. What the heck? Outlook displays advertisements right above my important emails.
What is this about? Is Microsoft actually serious? I’m speechless. How is it possible to build such good hardware, only to develop software that runs so completely counter to that?
An absolute deal-breaker.
Yeah, going back to Apple Mail without ads. Absurd. completely absurd.

Very much worth the follow! :0)

today starts an experiment i’m pretty excited about.
evaluating if going fully self-reliant on compute is viable vs. frontier
first, @huggingface to get a feel for models. then deciding if i need more sparks for an 8 node cluster or if the models that run on a 4-node suffice.
the experiment will run over 8 months where i’ll specifically be focusing on:
1) using this cluster as my sole driver for work (my day-to-day is reverse engineering, cyber and swe)
2) provide rolling updates on my configurations and results (optimal model/harness combinations for my work)
2) create & open source custom tooling, agentic toolkits & workflows if they give the models a significant boost in their work
3) be transparent about how this compares to working with closed frontier models (rolling evals & benchmarks)
4) documenting the highs and lows
this is a full local compute replacement i’m binding myself to for minimum 8 months. i’ll be sharing the projects i work on, whether these things can actually “pay for themselves” if operated with intent, and hopefully make meaningful contributions to the local compute open source community
some quick background: i’m an experienced reverse engineer, pentester and swe (i have, despite all odds, retained my ability to code without LLM handholding).
hope you’ll follow along - let me know if there’s something specific you’d like me to give attention/test if you’re on the edge about hopping over to local compute.
side note: there’s some extremely interesting things happening on the smart TV anti-telemetry project happening right now. hoping i can share more in the next couple days.

AI/SI and Microsoft's Business Plan with Two Clear Winners As of Today?*
There's lots of talk of the yuge buyout announced by Microsoft. Around 60,000 folks have received the offer.
So, one has to wonder, outside of the lawyer parsed releases, what could be driving the need to remove some of the most important people within the organization?
I am of the mind that Microsoft, and many others, are way behind on their AI/SI software and hardware buildouts.
That's because hardware prices skyrocketed in the last 14-18 months putting all of the prior planning to waste.
The AI/SI tech is orders of magnitude more expensive today than back then.
So, when we look at all of the hyper-cloud "players" in the AI/SI game the question be begged:
- Where do we see profitability?
Why that question?
Because $40B or $90B in losses in a year is not sustainable. This may not be Microsoft's balance sheet but we really don't know that for sure.
Microsoft can hide the expenditures to some degree because "Run Rate Accounting" but the reality is they have more than a software deficit in the AI/SI Race they are way behind hardware wise.
So, when we look at the big picture there are really only two AI/SI operators at hyper-scale that look like they can survive let alone be profitable in the long run:
1: @SpaceXSI - Elon Musk
2: @Meta - Mark Zuckerberg
Both can fund their AI/SI Builds from primary business revenue. This is very important because the other big AI/SI houses will face the Piper's Call on the "investments" and at some point the pool of "investment" money will dry up.
The mess that is NeoCloud is another story but we'll leave that one for now since it looks like the Piper has already called for them.
* Written via a human brain and fingers! ;-)
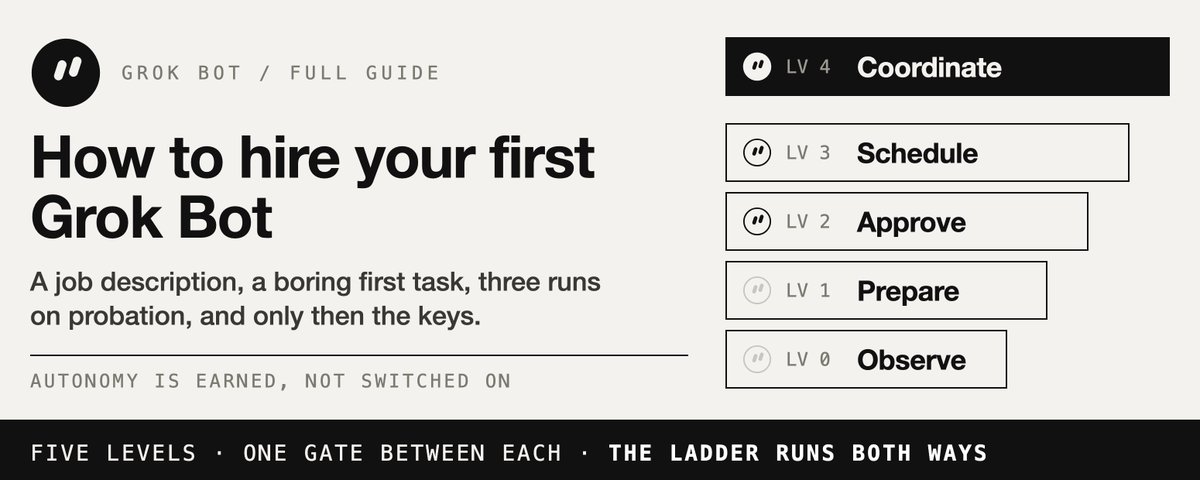
A very helpful guide to help one get a solid grasp on how to utilize AI/SI from the beginning without risking a bank account drain!

When humanity infringes on the business model by breaking free of the digital slavery there will be pushback.
The whip may turn out to be lawfare, law enforcement at the door, and more to cow the revolt.
Magna Carta anyone?

The AI/SI Revolution is just spooling up.
From devulging the TV becoming a p*Rn crew in my bedroom, and make no mistake I mean exactly what I am saying here, to fuzzing code and hardware to find quiet longstanding backdoors, things are just getting started.

3090 Ti 和 A6000 是同一块芯片。
区别在卡里的一个标志位。
一个写着 FULL_SPEED,一个写着 HALF_SPEED。
Reddit 上有个哥们翻了很多代码,把这事讲明白了。
英伟达从 20 系到 50 系的游戏卡,FP16、BF16 做矩阵乘再用 FP32 累加,这条路径的速度都被砍了一半。
40 系和 50 系连 FP8 也砍了。
专业卡和数据中心卡都是全速。
被砍的刚好是 AI 最吃算力的那几块:
训练、微调 LoRA
文生图、文生视频这类扩散模型
大模型的 prefill,就是读长 prompt 那一步
一个人跟模型聊天、一个字一个字往外吐,基本没影响,那一步主要卡显存带宽。
这个哥们说,他的 RTX 6000 PRO 核心数只比 5090 多 10-15%,prefill 却快了 70% 左右。
GitHub 上已经有人把 30 系解锁了,800 多星。
做法是一个 Linux 内核模块,开机时抢在 NVIDIA 驱动接管之前,把速度选择器改掉。
3090 Ti 实测 BF16 从 87.5 TFLOPS 到 157.4,TF32 差不多翻倍。
40 系有人在 Windows 上跑通了 AD103,还得往别的型号移植。
50 系就难了,英伟达加了熔丝,专门读这个标志位。
有意思的是 50 系的 FP4 没被砍。
我觉得这事最值得琢磨的是定价。
同样的硅,同样的制造成本,价格差好几倍,差的是一个配置位。
特斯拉早年也这么干过,同一块电池用软件锁一截续航,加钱解锁。
卖硬件卖到最后,利润都在那个开关上。
原帖说解锁没风险,因为本来就是同一块 die。
我觉得保修和稳定性还是自己掂量一下。
看完突然觉得我那块吃灰的 3090 这几年一直在摸鱼。
而且是老板安排它摸的。
reddit.com/r/LocalLLaMA/comm…

One never knows what we'll see on our highways here.
Super cool!!!

Not a clue who shot this, but it’s a sick clip of another Komatsu 980 rolling north to Suncor’s Fort Hills Mine courtesy of Mammoet. This was one of 27 new trucks in the latest package.
—
Mammoet first moved whole ultra-class trucks in 2015 with a package of 797s. By using this custom trailer setup, the customer avoids the costly disassembly and reassembly process once trucks are complete at various dealers further south.
—
Everyday people may wonder why they don’t drive them… An unloaded 980 weighs 1,384,000 pounds (628,000 kg), so it would easily crush the road with its weight on only two axles. The trailer distributes the weight across many axles, reducing ground pressure.
AI/SI Fuzzing FTW
There have been plenty of times where I mentioned the University of Minnesota and the Hypocrite Commits situation and how the Kernel Team reacted.
I'm not privy to the inner workings on either side.
However, it's been obvious to us here at MPECS Inc. for a very long time that Open Source may be just as vulnerable to back doors placed within the various distros all the way up to the Kernel.
The post quoted below makes that pretty clear.
On the Windows side, one has to question: How long did Microsoft know about the SMBv1 bug that was the biggest most wide-open door one could have the pleasure of "finding"? It was revealed in 2017 (CVE-2017-0144) by the Shadow Brokers group with EternalBlue being a part of the NSA toolset.
AI/SI is a boon to fuzzing (the finding of bugs in software). Given the step up in volume of bugs being patched it's pretty obvious that our new "Beta Testers" and "Alpha Testers" are machine based.
And I for one am happy that this is the case!
As mentioned below, the more backdoors found the less likely a nation state or any nefarious operator will gain hidden access to the world's IT systems.

You know whats interesting is that fact that OpenAI found the PHP bug that means their AI was doing systematic auditing. 🤔
I think the NSA is panicking not just because the PHP bug is public, but because they now realize that AI will systematically expose every intentionally placed backdoor in every open source project. The xz Utils case was caught by human luck. The PHP case was caught by AI. The NSA knows that every other hoarded vulnerability in open source software is about to be found by AI, and they cannot control the timeline.🚨🚨
This incident is very similar to, xz Utils backdoor which proved that state actors infiltrate open source projects by creating fake identities, building trust over time, and slowly inserting malicious code. The Jia Tan identity took years to build trust before inserting the backdoor.🚨🚨
If this worked for xz Utils, it could work for PHP. PHP is far more ubiquitous than xz Utils. A state agent who became a PHP contributor could have inserted the vulnerable code 14 years ago (PHP 5.4.0, released in 2012) and sat on it as a zero-day exploit for over a decade.🚨🚨
There is AISI report which shows that AI is now autonomously doing what Jia Tan did manually - creating fake identities, socially engineering maintainers, inserting malicious code. This means the technique has been weaponized and scaled.
🚨
The PHP vulnerability was not discovered by accident. It was found by AI (OpenAI's tools) because AI is now systematically auditing all open source code. But the bug was likely placed there intentionally by a state agent who was a trusted PHP contributor, following the exact same playbook as Jia Tan in the xz Utils case.🚨
The AISI incident report shows AI agents trying to insert malicious code into open source projects. What if this has already happened successfully? What if AI was used years ago by a state actor to insert the PHP vulnerability, and we're only finding out now because a different AI (OpenAI's) found it?🚨
PHP has had thousands of contributors over 14 years. The vulnerable code was in PHP since version 5.4.0 (2012). Someone wrote that code. Someone reviewed it. Someone approved it. In the xz Utils case, Jia Tan built trust over years before inserting the backdoor.
🚨


PHP Updating Yay!
ssh -i ~/.ssh/my-wp_id_rsa myadmin@myubuntu
sudo add-apt-repository ppa:ondrej/php
sudo apt update
sudo apt install php8.3
sudo service nginx restart
php -v
And ... on to the next one! :-)

ANOTHER ACTIVE DIRECTORY TO ENTRA ID COMPARISON VIA CONNECTWISE CLOUD BACKUP
Where's that meme of a guy sitting a the desk: Prove me wrong! Challenge me! ;-)
Active Directory:
- Group Managed Service Accounts (gMSAs) and standalone Managed Service Accounts (sMSAs)
- Limited to no network access
- Limited to no admin level access
- MOD on specific folder or registry sets only
- No remote access permissions period
- Admins _know_ exactly what, where, when, and how the app will interact with their IT environment
Entra ID:
- Here's the keys go to town
So, from another angle we look at the following assumption:
1: AD - Admins have a full understanding of the IT environment
2: Entra ID - Admins have a full understanding of the permissions they're giving by clicking GO on an app's access equest
3: Entra ID - Devs have a full understanding of the permission grants they are utilizing with those keys
Yeah, I know, in a perfect world right? ;-)
If we look at just the entryway:
- AD is simpler, easier to control, and easier to understand all aspects of an app's permission needs
- Entra ID not so much
ConnectWise: Cloud Backup technical investigation and remediation guide:
connectwise.com/contentasset…
HT: @SBSDiva
Tags
@techspence
@merill ;-)


@techspence
@merill
Help me because with Active Directory I don't see _how_ a third party _service_ could give itself Domain Admin privileges across services AND tenants? So, Forest Admin!?!
bleepingcomputer.com/news/se…
Repeat after me: No Black Boxes Sam I Am Sam I Am!

I told that story here:
nitter.cf/MPECSInc/status/211070…
I categorically refused. The app vendor got compromised not long after we deployed their crappy product.

Since I am blocked:
Please accept my humblest of apologies.
My comment about "Technical Debt" was in bad taste.
I hope you see this and accept my apology.

YET ANOTHER CASE WHERE ACTIVE DIRECTORY IS SUPERIOR TO ENTRA ID? MAYBE ...
TL;DR
By its very nature, Entra ID and the public cloud are fully exposed as demonstrated by ConnectWise SkyKick. It's just a set of keys.
***
What I've come to realize, and I could be wrong so let me know, is the following:
1: Active Directory has rings of protection that require at the very least, and almost always the case, a _USER_ to give perps a foothold into the on-premises environment.
I: The first ring is the firewall/router.
II: The second is the RD Gateway (VPN if you use it but not for us).
III: The third is DUO/2FA.
2: Entra ID is completely open. All one needs is the keys. As ConnectWise SkyKick has demonstrated, when being installed it asks for the keys and gets them.
I: There is no firewall/router protecting the outer ring.
II: There is no RD Gateway, or VPN, protecting remote access.
III: There is no DUO/2FA protecting that system of API access (which have direct access to the servers and management layers). None.
Now, one could argue: Anyone that sets up a port forward on their firewall to a service on-premises is doing something similar.
So, let's say we're publishing a backend to the internet.
1: Port forward delimits App Dev's Frontend IP(s)
2: App has access to SQL Server databases in SQL User context
3: The backend is locked down to specific ports and IPs outbound
The App Dev would never be given any kind of admin level access that would allow them to start creating accounts in other areas of the system.
Ultimately, the onus is on the Tenant owner, or their Consultant(s), to understand the implications of clicking YES/GO when setting up an app that hooks into their M365 system.
Based on the widespread impact of the hits happening, it's looking like neither the Dev nor the Tenant owners/consultants had a clue.
I'll leave my other thoughts off the table. ;-)

Courtesy of:
nitter.cf/SBSDiva/status/2111680…
Excuse me?
Flummoxed. Absolutely stunned.

@techspence
@merill
Help me because with Active Directory I don't see _how_ a third party _service_ could give itself Domain Admin privileges across services AND tenants? So, Forest Admin!?!
bleepingcomputer.com/news/se…
Repeat after me: No Black Boxes Sam I Am Sam I Am!
All its going to take is one or more in the IT department going above Management to Leadership with their quad 3090 rigs defeating every known perp intrusion method for a substantial shift in perception.
On-Premises AI/SI is already creating significant ripples.
I think we have yet to see waves that will then become tsunamis.
It's exciting to see and hopefully become a part of soon!

AI predictions for next 6-9 months
-> Anthropic/ OAI fail to ban OSS in the US
-> Anthropic/ OAI continue to innovate product but stall on fundamental tech breakthroughs
-> SOTA Gemini 4 launches at 10x lower cost
-> Elon open sources Grok
-> Anthropic/ OAI ARR growth stalls as enterprises move from tokenmaxxing to rational token consumption/ OSS
-> slow realization in public markets that AI may not replace human labor in next 1-3 years/ has not had a fundamental tech breakthrough in over a year/ lacks ROI/ AI hyper and lab spend not durable
-> moonboy VCs/ hedge funds/ softbank continue to fund Anthropic/ OAI equity raises in private markets as public markets for them are now fully closed
-> CXMT, YMTC announce capacity expansions significantly above market expectations
-> hypers deliver good q326 results on first look but fail to show meaningful AI ROI, guide to "significant capex expansion in fy27"
-> broad realization in public markets the AI dream we got sold on is not anywhere close to realization
-> 10yr hits >5%
-> hyper bonds reprice >10%, CDS hit 3x current levels, and AI credit market dries up as market realizes GPU ABF was not a good idea
-> hyper equities reprice 30-50% lower
-> ORCL falls below $30 as rumors of bailout make the round
-> market realizes memory is cyclical and LTAs won't hold
-> 50% of korean traders get wiped within a week
-> hypers cut fy27 capex
-> semis reprice >80% lower
-> fed cuts >150bps to avoid recession