




Pinned Tweet
First Rust contest.
First L1 contest.
First place.
I am really happy about this one! Tough competition, deep codebase and a lot learned along the way.
Big thanks to @citrea_xyz and @cantinaxyz for the opportunity 🔥
And huge shoutout to @tqkve and @AifosSi for the solid judging 🫡

The @Citrea_xyz competition results are in. 🪐
Researchers reviewed the first ZK rollup on Bitcoin L1.
Your top-ranked researchers:
🥇 @MartinMarchev: $21,071.01
🥈 @franfraneth: $9,780.99
🥉 @coachpetrus: $6,086.17
Thanks to everyone that contributed. Full leaderboard below.

If your Binance crypto withdrawals are suspended but you need your funds out urgently - try fiat.
Convert USDC/crypto to fiat then withdraw via SEPA/wire. Worked for me.
I guess fiat is having its moment.
Stay safu, fellas!

I got curious about Immunefi's submission fees so I checked their public fee collector.
It received 415,639 USDC across 6 months (from 20 April through 26 October 2026).
These were 8,346 transfers from 2,074 addresses.
The five largest sender wallets paid 32,005 USDC combined:
1. 0x2e804b...12aef8 - 9,945 USDC (258 payments)
2. 0x0059f3...c5e5be - 6,115 USDC (258 payments)
3. 0xb97c45...a1b2b7 - 5,450 USDC (90 payments)
4. 0x55b2e4...7784d0 - 5,400 USDC (54 payments)
5. 0x9889b9...2b51a6 - 5,095 USDC (128 payments)
The median incoming transfer was 25 USDC and the average was about 49.80 USDC.
These are public Ethereum transfers, checked through block 26,278,968.
The fee collector's address is in the comments.

Martin Marchev retweeted

any strong web2 security researchers with solid pentesting experience here?
if you are interested in working with us at Certora, dm me your experience pls
Submitted as High. Confirmed as Low.
$1k is $1k
immunefi.com/s/ss/?severity=…

Martin Marchev retweeted
It's about time @immunefi started refunding submission fees for duplicates of valid findings.
@MitchellAmador, in your own words:
"Immunefi now prices out spam with pay-to-submit mechanics, so a junk report costs the sender something, and the flood thins out."
Fair point! But if a researcher submits a legitimate vulnerability and gets marked as a duplicate simply because someone else reported it first, where's the spam?
What's the justification for keeping the submission fee in this case?
nitter.cf/MitchellAmador/article…

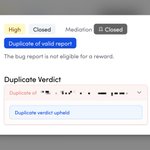
Update: Immunefi upheld the duplicate closure.
Their own fix-bypass policy says a bug that wasn't effectively fixed should be reported.
That's exactly what I did. The PoC in my report still works after the attempted fix.
Yet their mediation response didn't even mention the fix-bypass policy.
So what's the point of having it?
Why would any whitehat spend time checking whether a fix actually works if the answer is still "duplicate, no reward"?
I thought Immunefi was supposed to keep this fair.
Instead, they're keeping their clients happy.


Projects trying to rug whitehats seem to be the norm lately.
I recently found a High severity bug. The project closed it as a duplicate of an earlier report. Which is technically true since both have the same root cause.
The funny part is they already tried to fix it.
And failed.
My PoC demonstrates that their fix can be bypassed and the bug is still exploitable.
@immunefi even has an explicit fix-bypass policy for cases like this:
immunefisupport.zendesk.com/…
But I guess it's easier to close the report than fix the bug and pay the whitehat.


Martin Marchev retweeted

In the era of AI-powered triage, paying more than $10–$20 just to report a bug is EV-negative for both sides.
I've been in this industry for years, on both sides of the table.
If processing a report costs you more than $20, that's a triage problem. Passing that cost on to researchers just rigs the process against them.
This was an issue when we first started the AI slop submissions, now it's not about that anymore, fix your triaging bots and ease your process for to the defending side!
I can't believe i have to write this, tbh, lol!
Projects trying to rug whitehats seem to be the norm lately.
I recently found a High severity bug. The project closed it as a duplicate of an earlier report. Which is technically true since both have the same root cause.
The funny part is they already tried to fix it.
And failed.
My PoC demonstrates that their fix can be bypassed and the bug is still exploitable.
@immunefi even has an explicit fix-bypass policy for cases like this:
immunefisupport.zendesk.com/…
But I guess it's easier to close the report than fix the bug and pay the whitehat.

Not sure what's sadder: finding a fund theft crit and getting duped...
Or realizing the whitehat who found it first missed the full impact.
I'm sorry for both of us, pal 💀

Martin Marchev retweeted

Update Telegram Desktop immediately!
A critical vulnerability has been discovered that allows attackers to gain access to your account and secretly steal files from your computer.
The attack uses links in the format tg://. If a special command is constructed, clicking the link can cause a malicious script to send a selected file to the attacker’s channel - without requiring additional confirmation.

Update: @immunefi refunded the full 95 USDC (both the Studio Review fee and the submission fee) and acknowledged the issue.
They are also looking into why Studio missed the duplicate.
Fair outcome and props for handling the feedback quickly!

I decided to give Immunefi Studio Review a shot before submitting a High severity finding.
The submission for this particular program costs $75 so I decided to pay $20 for a Studio review first to sanity-check the report.
Immunefi Studio came back with "Ready" - "meets standard escalation criteria with no blocking technical flaws".
To be fair, it suggested a couple of improvements to the PoC which I applied to the report before submitting.
So I paid the $75 and submitted.
15 minutes later, my favorite guy Andrew closed it as a duplicate of a report submitted 9 days earlier.
So that's $20 for Studio Review + $75 submission fee = $95 to have one Immunefi bot tell me "send it" and another Immunefi bot tell me "duplicate report".
That's the part I'm struggling with.
Immunefi Studio is explicitly advertised as checking duplicate risk too.
If a duplicate has already been sitting in your system for 9 days and the Review bot can't catch it, but the triage bot catches it almost immediately after submission, then what exactly is the value proposition here?
@immunefi / @MitchellAmador - I genuinely think this is useful feedback if you're still iterating on Immunefi Studio.
But from the whitehat side, this flow feels pretty broken.
Especially when it costs $95 to get to this outcome.

Small @immunefi ask:
When a report is closed as "Duplicate of invalid", show why the original was rejected as invalid.
Right now we only see the original report, NOT the closure reason.
It feels like basic courtesy when I paid 75 USDC to submit.
