

Helping lean security teams protect the email, data, and identities that live in Google Workspace and Microsoft 365.
San Francisco, CA
Joined March 2020
- Tweets799
- Following407
- Followers1.2K
- Likes799




In the last 30 days, 232 suspected North Korean IT-worker personas made contact with 99 organizations we monitor.
66 reached an interview or later. At 42 of the 99 organizations, at least one got as far as an interview or an offer. At four, one reached onboarding: offer letters, background checks, equipment requests, or first-day IT setup.
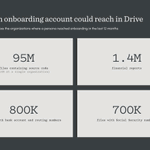
We then looked at what a new account could have opened at those four. At one, about 15 million source code files and 130,000 files with bank or routing numbers were held tightly, shared with almost no one beyond their owners. At another, 68% of roughly 400,000 files containing Social Security numbers were open company-wide or by public link.
Same adversary, very different blast radius.
It also changes how you triage. A watchlist hit at first contact and the same hit at onboarding call for very different urgency, and once an account exists, the hiring investigation and the access investigation may be the same case.
52
Attackers stopped asking for your password.
Passkeys made that phishing much harder, so now the pitch is “just go through this OAuth flow.”
Real Google login. One click on Allow. The token bypasses your identity protections.
@BleepinComputer
1
123
Of 702 HIPAA breaches under HHS investigation, 144 involved email, and 85% of those were account takeovers. We’ll be at HS-ISAC Fall Americas Summit in Tucson, Dec 1 to 3, talking about what’s already sitting in the inbox. Booth #15!
Book time with us: hubs.li/Q04FWgRG0

41
If one fake North Korean employee got into your company tomorrow, could you list everything their account can open?
At one company where a suspected persona reached onboarding, 68% of the files containing Social Security numbers were open company-wide or by public link.
What would you do?
70
Phishing training says check the login page. In this attack, the login page is Google’s. Rajan Kapoor on a suspected Russian OAuth campaign, why a real sign-in screen defeats user intuition, and what to govern instead: hubs.li/Q04FFRw80

58
27 suspected North Korean IT-worker personas reached onboarding at the organizations we monitor over the past year. That means offer letters, background checks, equipment requests, or first-day IT setup.
What they could have opened on day one depends on how sharing was managed before they ever applied.
We looked at four companies where a persona reached onboarding in the last 30 days.
At one, about 15 million files were flagged as source code and 130,000 as containing bank or routing numbers. Almost none of it was shared beyond its owners.
At another, 68% of roughly 400,000 files containing Social Security numbers were open company-wide or by public link. So were 71% of its bank and routing files. Any account inside the company could reach them with no special permission, so a new account wouldn’t have had to look for anything.
At a third, about 1,900 source code files were shared by public link, readable by anyone with the URL.
At the fourth, 21% of financial files and 17% of credit card files were shared beyond their owners.
Same adversary, very different blast radius. Catching the mask at the door matters, but so does knowing which files hold what, who can reach them, and where sharing has drifted wider than intended, before a case starts.

50
Security used to scale with the company. More people, more security.
That’s over. A company can multiply in size in a few months while its security headcount stays flat.
We hosted a panel on this with Dylan Healy of Fleet AI, Frank Wang of Surge AI, and Zach Morris of Lumbra, moderated by our CEO Abhishek Agrawal. Nobody said the answer was to hire more. Four takeaways:
Buy for the company you are about to be. You never want to rip out a stopgap in the middle of hypergrowth.
Give agents the recurring work you would have hired for. Dylan had a team of eight on observability and detections at Roblox. Now, agents handle much of that maintenance.
Make decisions you can undo. Hiring is one of the hardest to reverse.
Stop treating people as a control. Someone will click, and if that ends in a compromised identity, the technical controls failed, not the person.
The fundamentals haven’t changed. Headcount just isn’t how they scale anymore.
1
115
“Imagine waking up to find that work has been moving forward while you were asleep.”
The opening of a recruitment email from a North Korea-linked operator. Not a fake applicant this time. A recruiter, writing to real employees.
There was no urgent warning and no attachment, only a side-income offer: create an account on an AI-training platform, complete the identity verification, and let someone else do the work.
Eight operators, 13 organizations, about 38 employees, five weeks. The emails are below.
🔗 hubs.li/Q04FlGb-0


1
75
Material Security retweeted

Google warns that fully-automated AI attacks are coming soon
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

Two Google Drive files with sensitive data. One is shared company-wide: contained. One is public with SSNs: overexposed.
The agent stages the fix, and here we approve it by hand. Once you trust its verdicts, it can act on its own. 👇
108
Same adversary, very different blast radius. We found suspected North Korean IT-worker personas reaching onboarding at four of the companies we monitor.
At one, almost nothing sensitive was shared beyond its owners.
At another, 68% of the files containing Social Security numbers were open company-wide or by public link.
🔗 hubs.li/Q04FdPcn0

107
Material Security retweeted

"A Thousand Masks: Where the DPRK IT-Worker Threat Meets Your Data" published by @material_sec. #ITWorker material.security/resources/…

Material Security retweeted

Calendar invites stole live Google sessions, even after real MFA approval.
Per @material_sec:
- A live proxy relayed passwords, SMS, TOTP and Tap-Yes
- 897 phishing domains taken down
- Fix: revoke sessions, don't auto-add invites, prefer passkeys
#CyberSecurity #AiTM
material.security/resources/…

Material Security retweeted
Suspected North Korean IT workers reached onboarding at companies with open data - helpnetsecurity.com/2026/11/… - @material_sec #NorthKorea #DPRK #InsiderThreat #CyberSecurity #InfoSec

Welcome to the roster, @togal_ai! Takeoff in minutes, not days on their side - email, files, and account takeover protection on ours.

61
Material Security retweeted

🚨 Hackers used Google Calendar invites to hijack corporate Google sessions—even after victims approved genuine MFA prompts.
The trick: trusted Google links and live phishing proxies that captured authenticated sessions.
897 attacker domains taken down.
Inside the campaign: thehackernews.com/2026/11/ca…

Weeks before we published our research on North Korean IT-worker personas reaching onboarding, Belem Regalado explained access management with a bathtub in a SecurityWeek webinar. Restricting events went from 14% of access changes to 44%, and new sharing still outpaced them.
Then we saw what that looks like when a fake hire gets in. At one of four companies, almost nothing sensitive was shared beyond its owners. At another, 68% of the files containing Social Security numbers were open company-wide or by public link.
🔗 hubs.li/Q04D-rhN0
1
1
111
Most people wear a costume to a Halloween party. One suspected DPRK persona was completing onboarding paperwork at one company while pursuing opportunities at seven others, in the same mask.
18 of the 27 that reached onboarding were in process at other organizations too.
hubs.li/Q04F63VD0
1
80
41% of the suspected DPRK personas we tracked applied at more than one organization. 15 appeared at ten or more. One appeared at nineteen. Each company saw only its own hiring process.
hubs.li/Q04D-t4J0

58