






Merl retweeted

Reading the reconstructed bytecode of the Binance EIP-7702 sweeper (`0x63e8...6fae`) is wild.
This wasn't a generic drainer. It was custom-engineered for Binance 14's architecture:
- Leaves exactly 1 ether behind (`bal - 1 ether`) when sweeping ETH so Binance's automated hot wallet queue wouldn't error on gas and trip alarms.
- Uses raw `staticcall` + `continue` loops with custom error codes (`SweepItemFailed`) so one bricked or blacklisted ERC-20 wouldn't revert the $6B batch.
- Includes a custom `callExecute` function to impersonate Binance 14 as controller of an external vault holding $823M in USDC.
They leave a comment: "robberies could be prevented if getaway cars were slower."
You can't fully blame EIP-7702, but it sped up the attack. Without 7702, draining 64 tokens plus an external $823M vault from a live exchange hot wallet meant fighting moving nonces across 70+ transactions. Defense systems would've killed it after tx #3.
With 7702, Lazarus sprayed 50 consecutive nonces in one type-4 payload, turned an EOA into a custom proxy, and atomically swept billions in a single block.
Ethereum core devs built the ultimate getaway car. Surgical state-sponsored engineering.
This could be etched onchain:
`if (bal > 1 ether) { to.call{value: bal - 1 ether}(""); }`


The Binance $5.6B drain is a masterclass in modern EVM exploitation.
It wasn't a complex logic bug. It was an EIP-7702 delegation hijack:
1. Setup: Attacker funds 0x7c86 via Tornado Cash, deploys a sweep contract (0x63e8), and runs three live dry-runs on external wallets.
2. Execution: Attacker submits an EIP-7702 batch with 50 pre-signed authorizations (nonce n to n+49) to hit Binance 14's moving nonce window.
3. One authorization hits. Instantly, Binance 14 (an EOA) is reprogrammed to run the attacker's contract bytecode.
4. Execution looks totally organic: Binance 14 sweeps itself clean. Internal threshold alerts don't trigger because, from the nodes' perspective, the hot wallet is just executing its own transaction.
5. Binance 16 immediately auto-refills 28,000 ETH due to automated treasury rebalance scripts, feeding the exploit loop.
The cold truth: you cannot forge an EIP-7702 delegation list.
For this to execute, the attacker already held the raw private key or unconstrained signing access to Binance 14's HSM/KMS.
But hey, 5.64 billion drained across ETH, BTC, and Tron. 2.54 billion frozen by Tether, Circle, Ripple, and World Liberty within hours.
Code is law until the stablecoin admin keys log in.
Binance got bailed out by the very centralized choke points the cypherpunks warned you about.
Hardware wallets leak your home address.
Centralized exchanges leak the keys to the kingdom.
Self-custody on native, non-delegated chains remains the only honest baseline.
At least you know what to avoid.
Merl retweeted

Update: Stolen funds from the $6.3B Binance exploit and $388M Bitget exploit were commingled at the same address 45 minutes ago, after arriving via THORChain.
This indicates the same actor is likely behind both incidents.
The Bitget exploit was attributed to DPRK-linked TraiderTraitor, which had overlap with other previous exploits such as Kelp DAO.
Commingling address:
0x15104a9ce0f08a8f0075a0869ae80e795fe0feb7
Bitget exploit context: nitter.cf/zachxbt/status/2104528…


BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379


Merl retweeted

‼️ UPDATE ON THE BINANCE HACK:
Whoever emptied a Binance hot wallet had 50 authorisations signed with that wallet's own private key, on-chain data shows.
Under Ethereum's EIP-7702, an authorisation is a signed permission that lets a wallet hand control of itself to code.
Each one works only for the wallet's next transaction number, its nonce. Binance's wallet was still sending transactions, so that number kept moving.
The sender didn't know which number would be live, so they packed all 50 into one transaction, Blockaid says. One matched.
That one installed a sweeper contract on the wallet. Blockaid found that only the Tornado Cash-funded sender can operate it.
Minutes later it emptied the wallet of $1.6B in USDT, 167,464 ETH and 60+ other tokens.
Only that key, or the system that holds it, can produce those signatures. How the sender got them is unknown.
Across Ethereum, Bitcoin and Tron, at least $5.57B left Binance-linked wallets.
Binance says user funds are "completely safe" but has not explained how.


Merl retweeted
BREAKING: Arbitrum Security Council has executed a transaction to freeze ~$30.5M from the Binance Exploit.
Thanks to all other signers involved.
Exploiter address
0x3E2bf1ac6bf0934BBba6456C341c2EcbCED632d5
Trsanction hash: 0xb69c81774f507d46ce776aeaed8b4d31df96dd66ce6fd05073481011835355d6


Merl retweeted
🚨BREAKING: BINANCE HOT WALLET APPEARS TO BE DRAINED FOR ~$2.53B!
On-chain data shows a large outflow from a Binance hot wallet (Binance 14) involving roughly $2.53 billion across 60+ tokens on Ethereum, including a major ETH transfer.
The transaction that moved the funds was initiated by an address funded via Tornado Cash, with the assets sent to a fresh EOA.
The report remains unconfirmed.
#Malware Afectando a varias entidades 🇦🇷🇲🇽
IOCs
novabaprimeapp.]com
ktx123.]net
ktx456.]com
ktxapp.]com
updates.]ktx123.]net
Lista de APPs (Dividida en KEYBOARD_ALLOWLIST_STATE y KEYBOARD_ALLOWLIST_LEARN_REQUEST)
pastebin.com/raw/MbRNbKwW


Merl retweeted

ordené mis charlas, slides y papers en un solo lugar. hay próximas fechas, material de las que ya di y una ficha propia para cada una. también lo rehice para que se use bien desde el celular: valentorassa.com/charlas


Merl retweeted

🕵️♀️El manual de Lazarus llega a Brasil: Mikedor y OfDor contra el ecosistema financiero latinoamericano
"Principios de 2026, un banco internacional perdió más de 18 millones de USD. El dinero no salió por SWIFT, sino por Pix..."
🎙️ Fabio Marenghi
🕒 10:30 - 11:15
📍 Sala E
Merl retweeted
🏦Sin armas ni rencores - Encadenando vulnerabilidades en un homebanking
¿Puede un IDOR terminar vaciando una cuenta?
🎙️ Diego Ritunnano
🕒 9:45 - 10:30
📍 Sala E
#CyberFinance #Ekoparty #Eko2026

Merl retweeted
Y si los desafíos técnicos no son lo tuyo, también podés ganar un badge exclusivo de #CyberFinance
En 2 de nuestras charlas habrá media flag que forman la correcta.
Vení a validarla el dia Jueves 8 a las 12hs en nuestro village 🐮
Gana la primer persona en validarla 😉

Merl retweeted
Comienza el #CyberFinance CTF! 🔥
Pasá por el Village 🐮
Preguntá por el CTF ⛳️
Prepará tu celu 🤖📱
Los premios se entregan el viernes a partir de las 16.15 hs
Happy hacking 😎


Merl retweeted
A long walk. A legendary run. ✨🇦🇷
#FIFAWorldCup
Merl retweeted
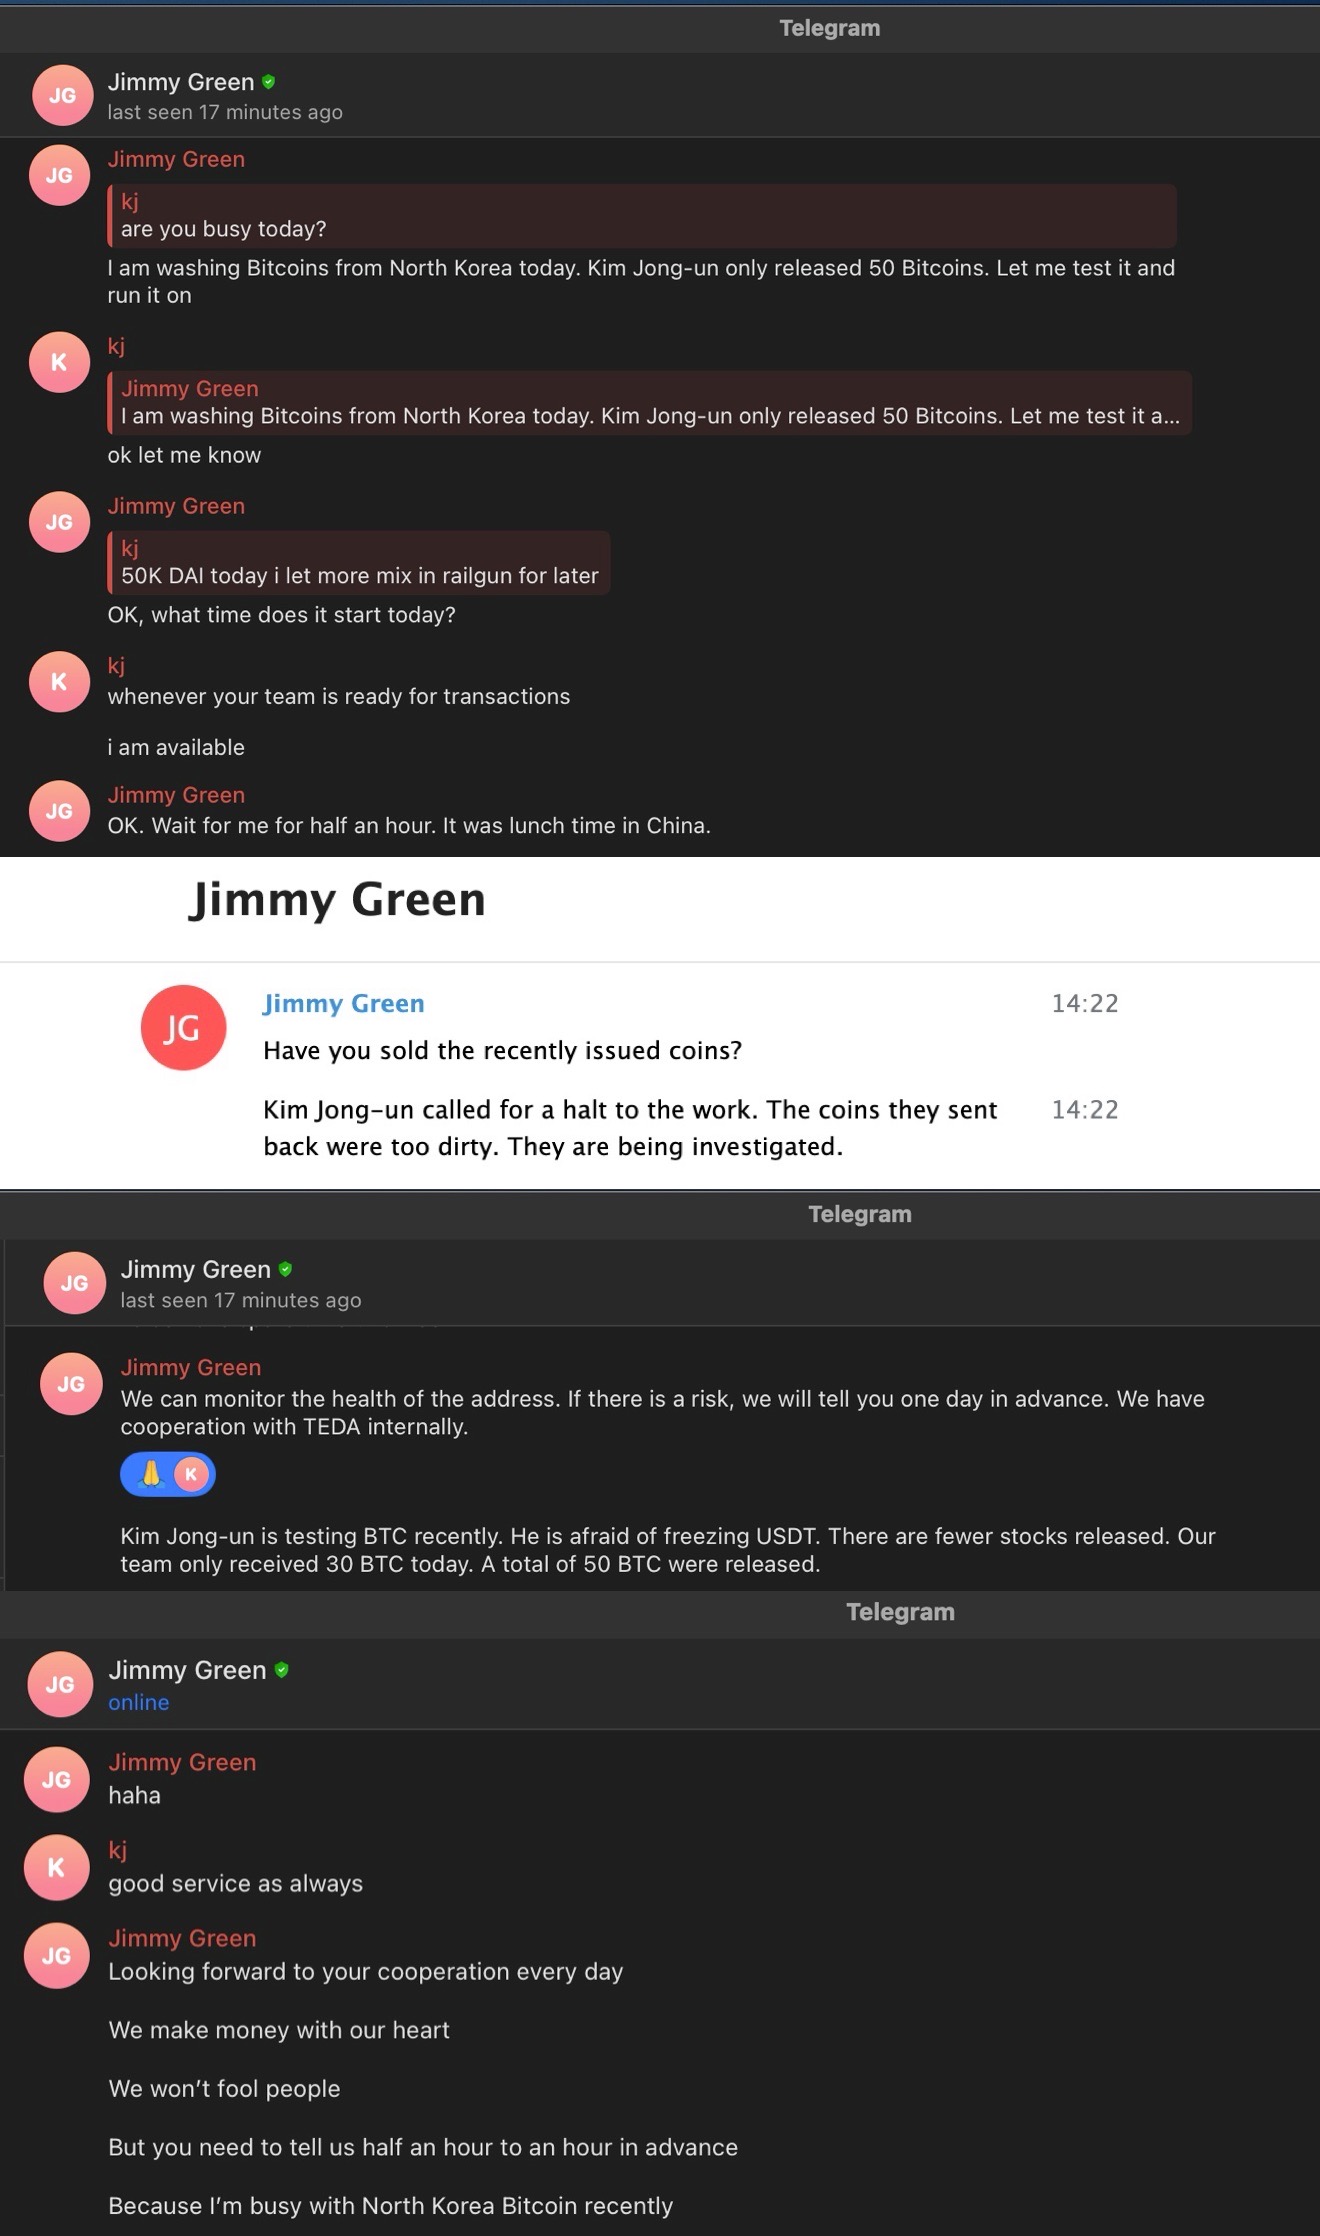
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

Merl retweeted
Todavía no tenés tu entrada para @ekoparty 2026?
Es tu momento!
Sorteamos 1 entrada legacy free y 2 al 50% off 🔥😎
Para participar es fácil, seguinos, dale like y compartí 😉
Sorteo lunes 5 a las 17 hs
Y si ya tenés tu entrada compartí para que alguien más pueda ir también 🫶🏻

Merl retweeted
🧵🔥 Día 3 de @ekoparty 2026 y #CyberFinance vuelve a pisar fuerte con sus charlas. 💳🔐
Más fraude, más amenazas, más casos reales y más conversaciones sobre lo que ya está impactando al ecosistema financiero. ⚡👀
📅 Viernes 9 de Octubre - agenda completa 👇
Merl retweeted
🧵🔥 #CyberFinance — Día 2 en @ekoparty 2026
Estas son todas las charlas que van a formar parte de la jornada 👇💳🔐
📅 Jueves 8 de Octubre - agenda completa 👇