
Reverse Engineer | Mobile Malware Research | Mobile Financial Threats
behind you
Joined November 2012
- Tweets2.3K
- Following1.3K
- Followers850
- Likes2.3K



Pinned Tweet
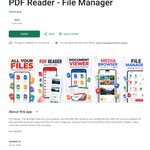
New #Downloader in @GooglePlay🤦♀️ play.google.com/store/apps/d…
Has 50K+ downloads😱
It's NOT FileManager|PDFReader It's malicious downloader for #Banker #ReBot aka #Anatsa #TeaBot #Toddler
Uninstall ASAP and don't let it install any "updates"
FYI @malwrhunterteam @androidmalware2

Mobile Security retweeted

Our latest #zLabs research reveals how ArcticRAT uses AI to analyze stolen financial data, identify banking apps, and extract sensitive information, introducing new risks to mobile security.
Read the full zLabs analysis: okt.to/SFQLrt
#MobileSecurity #AndroidMalware

Mobile Security retweeted
The official IDA MCP Server is here. It's free, open source, and works with any LLM.
Your agent writes IDAPython, uses ~20% fewer tokens, and can share an IDB with you in real time.
𝚞𝚟𝚡 𝚒𝚍𝚊-𝚑𝚌𝚕𝚒 𝚖𝚌𝚙 𝚒𝚗𝚜𝚝𝚊𝚕𝚕
hex-rays.com/blog/hex-rays-i…
(copy-paste: uvx ida-hcli mcp install)

Mobile Security retweeted
New video:
Breaking Obfuscated Binaries with AI Agents: An Attacker's Playbook
I'll showcase my strategies for attacking strong protections that cannot be one-shotted.
youtube.com/watch?v=oGBj1v8t…
Slides & samples:
github.com/mrphrazer/binary-…

Mobile Security retweeted

Today we published WeWorm, our zero-click worm that spreads across iOS and Android.
All it takes is one phone call. You don't have to answer. Seconds later, your WeChat account is compromised, calling your friends and spreading the attack.
We reported the bug to Tencent, and it's now mitigated for all users.
We hope this sets an example. The US and China disagree on plenty, but keeping billions of people safe online shouldn't be one of them.
AI gives us a chance to find and fix these bugs faster than ever. We should work together to make the world safer for everyone.
Our story and demos: calif.io/research/weworm

Mobile Security retweeted

We have conducted a thorough investigation into the Hugging Face incident.
We are releasing a technical report and accompanying blog post that reconstruct the agents’ activity, explain why existing safeguards failed, and detail how we’re preventing recurrence.
openai.com/index/hugging-fac…

Mobile Security retweeted

TLDR: I’ve started a small fund from my Base44 money that’s focused on cancer research and breakthrough therapies.
I’ve invested in 7 incredible companies in the past 4 months and plan to do more as my liquidity allows. Listing my investment thesis below
I welcome anyone like me who has been blessed financially to join me and find ways to finally manage or even end this disease.
Longer -
I honestly believe cancer is humanity's worst enemy.
~40% will be diagnosed with it, and out of which a ~third won’t make it. And numbers are currently not getting dramatically better.
For many it might sound like a statistic
But for some of us who have been there ourselves or had to go through it with a person we love, it’s one of the worst things you can imagine.
I had to go through it with my mom - who passed away 4 months ago and whom I miss and think about every single day since.
This field needs a dramatic push.
The current wave of technology and AI is doing a lot of good in the world,
But cancer therapy is one of those things that are not moving nearly fast enough.
And there’s no good reason for that - AI is creating so much opportunity right now.
Here's my thesis on how things will play out:
For drug development, the bottleneck will shift to
1. Manufacturing
2. Real world testing
"In silico" is going to accelerate incredibly fast. AI is identifying new target proteins and designing new molecules, drastically shortening timelines.
AI will create an abundance / inflation of ideas. It will help design molecules faster than anything historically possible.
This is already happening.
Play with Claude Science or Codex and you'll be surprised at how far you can get with just a few prompts.
We need a better way to *manufacture and test* the 1000s of ideas coming from AI models spitting out potential drug candidates
1. Manufacturing: i.e. how fast can we synthesize a potential drug
Not too far into the future, companies with manufacturing excellence will win over companies with the smartest scientists.
Being able to synthesize a drug candidate fast - together with efficient methods to test efficacy (more on that below), basically means you get more shots at a target hence more chances at succeeding.
This is the same exact lesson the software industry learned about the importance of fast iterations.
Companies like Starget Pharma are leveraging AI heavily to iterate on drug candidates + figured out in-house manufacturing in a way that lets them iterate on drugs almost as fast as if they were a software company iterating on features.
2. Real world testing: i.e. how fast can we get a call on a drug's efficacy.
We need better real-world indicators for drug efficacy than mouse / animal models.
The success rate of animal models -> human clinical trials is less than 8%.
Breaking down this bottleneck will change the entire industry.
Developing an oncology drug and taking it through all clinical trials usually cost >> $ 100m
Thus taking the wrong bet is devastating (but still, happens a lot).
Giving drug development companies the ability to better understand the efficacy and mechanisms of their drugs will change a lot. Esp in the age of abundant drug candidates.
Furthermore - and once those methods proved efficient - Joining forces with regulators to shorten (or even skip) some clinical trials altogether will cut years from the process and save many lives by bringing new drugs to market faster.
CuResponse is pioneering functional testing - taking real cancer biopsies and showing drug efficacy with very high precision. Can be used for precision oncology as well as testing new drugs.
Cellint is providing a fully automated cell-culture R&D platform for companies and researchers.
----
I’d love to see a future where there are “cloud services” for drug development companies.
A company should eventually be able to submit a drug candidate programmatically and receive:
1. The synthesized drug.
2. Testing across cells, tissues, organoids, and tumoroids.
3. Structured results showing what worked, what failed, and why.
4. A recommended next iteration derived from the biological reactions.
I’ve invested in all of the above companies and am searching for additional companies to bring this “cloud services for drug dev” vision to life.
----
Alongside it, I am also investing in direct therapeutic moonshots.
I invested in Baccine, which is developing a bacteria-based cancer immunotherapy platform and deserves an entire separate post.
I’m also a proud LP in Even One Ventures - @sytses ’s fund to fight cancer. Sid and Jacob Stern are an inspiration to me as I’m making my first steps in the field, and I bet their companies will make a massive impact.
And 3 other incredible companies focused on how therapies are delivered - where I’ll elaborate in future posts.
----
I’m still obviously spending most of my time on Base44. Which is a plus for the companies - as we’re able to support them with tools, software, AI agents, etc.
I’m looking for people to join me - invest side by side or help one of the companies.
I don’t have a name for the fund yet, nor an email or a website
I will get to it this weekend and will post it in the comments.
Mobile Security retweeted

Nebula Security is now backed by Y Combinator.
We’re celebrating by bringing you the world’s first Android 17 root demo — “IonStack”, a url click can let attacker fully control your phone.
This is not only an Android root demo. We’re bringing you a full chain browser-to-kernel exploit with two 0-day vulnerabilities affecting Firefox before v151.0.2 and all Linux distros in 15 years. "IonStack" demonstrates how bad actors can control your phone by sending a malicious URL, but good news, Nebula Security found it before attackers do.
Both 0-day were found by our code scanning agent, VEGA, overshadowing any vulnerabilities found by Mythos or any scanner you name it.
VEGA has demonstrated its extraordinary capability in finding critical bugs in the world’s most complicated software: operating systems and browsers. It can spot the same vulnerabilities in your codebase too.
VEGA support full scan and incremental scan that can integrated into your CI/CD flow. We launched VEGA within YC companies and received overwhelmingly positive feedback. Now it is open to all enterprise customers in private beta.
Book a demo with us: nebusec.ai/book-a-demo
Mobile Security retweeted

Samsung fixed the issue in the January 2026 Android security update.
Read here:
lucidbitlabs.com/blog/when-d…

Mobile Security retweeted
We published a technical write-up on CVE-2026-20971: a Samsung Android kernel use-after-free found by our team at LucidBit Labs.
The interesting part: the bug lived inside a defense mechanism.
Mobile Security retweeted
⚠️ ThreatLabz discovered another fake document reader in the Google Play Store with more than 100K downloads, which delivers the Anatsa Android trojan.
Anatsa installer MD5 hash: f72b1a333fa28b133df6476561142d6a
Payload URL: http://66.206.6[.]6:8080/disclaimer.txt
Anatsa payload MD5: 61d25684e6f42e386f40ee60f5c54dca
Anatsa C2: http://162.252.173[.]37:85/api
Google Play URL: play.google[.]com/store/apps/details?id=com.westhorizont.appsforge.filehorizon_explorereaddocuments (currently live)

Mobile Security retweeted
I just published samloader-rs 2.0.0, with full firmware flashing capability!
Thanks to all of your kind words and support, it really meant a lot to me 😃
github.com/topjohnwu/samload…

Mobile Security retweeted

Introducing usbliter8
An A12/A13 SecureROM exploit
A novel iPhone BootROM vulnerability discovered and exploited by our team. It covers the underlying bug, the associated exploitation techniques, and the post-exploitation steps required to achieve application processor's boot-chain compromise.
The exploit leverages both a hardware bug in the USB controller and a specific configuration flaw present in the device firmware.
ps.tc/pages/blog-usbliter8.h…
poc:
github.com/prdgmshift/usblit…

Mobile Security retweeted

NEW: malware developers added nuclear & biological weapons text to to their spyware.
Goal? To trigger LLM safety refusals... so that their spyware wouldn't be analyzed by an AI security scanner.
Cleanest practical example I can think of for why over-indexing on first order safety alignment is risky.
When closed (and open) models ship with aggressive refusals, they will be sprinkled with second-order blindspots that attackers will discover...and exploit.
We are only in the earliest days of attackers leveraging these features, and it wouldn't surprise me if users systems that need to handle complex cybersecurity issues demand that models be less safety-blunted.
In the weeds: @SocketSecurity's post also shows why intention matters in how you design a malware analysis pipeline to avoid prompt manipulation.
H/T to colleagues that shared this with me socket.dev/blog/mini-shai-hu…


Mobile Security retweeted

Android.MagicAd displays background ads without SYSTEM_ALERT_WINDOW.
Bypasses restrictions via system media controls abuse, vendor-specific intents, and Binder IPC abuse on Xiaomi/Vivo/Amazon devices. Distributed in 50+ apps via GetApps/Galaxy Store.
news.drweb.com/show/?i=15262…
Mobile Security retweeted

1/ We are sharing additional details regarding our investigation into unauthorized access to GitHub's internal repositories.
Yesterday we detected and contained a compromise of an employee device involving a poisoned VS Code extension. We removed the malicious extension version, isolated the endpoint, and began incident response immediately.
Mobile Security retweeted

[1/4]🚨 APK Malformation is no longer a niche evasion tactic; it is now a standard in the Android MaaS ecosystem. Observed in 3,000+ samples across families like TeaBot, TrickMo, and SpyNote, it keeps malware fully functional while blinding static analysis tools.

Mobile Security retweeted

📊 Israel–Iran Cyber Conflict Update — 1,074 Attacks Recorded
Our latest analysis of the ongoing cyber conflict (Feb 28 – Mar 22, 2026) shows a continued surge in activity across multiple regions and sectors.
Key Metrics:
• Total incidents: 1,074
• Attacks targeting Israel: 430 (~40%)
• Threat actor groups observed: 38
• Countries impacted: 23
• DDoS rate: 84.8% (dominant attack method)
Top targeted countries:
🇮🇱 Israel (430)
🇰🇼 Kuwait (130)
🇧🇭 Bahrain (70)
🇨🇾 Cyprus (68)
🇷🇴 Romania (51)
Most active groups:
NoName057(16), 313 Team, Keymous Plus, DieNet, Hider_Nex
Most targeted sectors:
Government, Financial Services, Defense, Transportation, Energy
Key Observations:
• Israel remains the primary target
• ICS/SCADA activity indicates growing focus on critical infrastructure
• Pro-Iranian and pro-Russian hacktivist coalitions are operating across multiple regions simultaneously
• Gulf states are increasingly targeted as secondary fronts
#CyberWar #CyberThreatIntelligence #Hacktivism #Infosec #CyberSecurity #ThreatIntel #DarkWeb #OSINT #IranIsrael #CyberConflict

Mobile Security retweeted
🚨 FBI Seizes Handala-Linked Domain in Cyber Operation
The domain handala-redwanted[.]to has been seized by the FBI following a court-authorized action by the U.S. District Court for the District of Maryland.
According to the seizure notice, the infrastructure was allegedly used to conduct or support malicious cyber activities in coordination with a foreign state actor, including potential network intrusions and infrastructure targeting.
The seizure is part of an ongoing effort by U.S. law enforcement to disrupt hostile cyber operations and prevent further exploitation.
⚠️ Authorities warn that individuals assisting or attempting to restore such infrastructure may face criminal prosecution under U.S. law.
#CyberCrime #CyberThreatIntelligence #Infosec #CyberSecurity #ThreatIntel #DarkWeb #OSINT #FBI #CyberOperations
