

Embrace any digitalization challenge—we'll secure your cyber-resilience
Joined April 2015
- Tweets1.4K
- Following868
- Followers3.7K
- Likes337




Pinned Tweet
Free hacker conference Positive Hack Talks is coming to Goa 🇮🇳
🎤 The call for papers is open. Bring your exploit, tool, or research. Travel is covered for selected speakers.
👉 Speak or attend at phtalks.pt.community/goa
#PositiveHackTalks #PHTalks

#PHTalks Goa: CVE-2026-113915, Racing the Media Daemon to Steal Your Hidden Photos on iOS 27.2.
@andrd3v and @amfi_d: a 200-microsecond race in mediaanalysisd lets any app swap in a symlink and read your hidden photos. No prompt.
Dec 10 - Goa - Free
phtalks.pt.community/goa

for the community! 🔥🔥🔥

Launched. Repost if you like it!
Cybersecurity conferences in one place, checked against official sources: events.pt.community
- Open CFPs & deadlines
- Published speaker support
- Topics from past talks
- Nearby events for one trip
Save, share, add to your calendar. No account needed.
A ghost tried to haunt our systems. A witch ran into bugs in her spellware. A vampire had his fangs confiscated for analysis.
Now they’re all in therapy, seeking professional help.
Unfortunately, they picked the wrong professional.
Our bad. Happy Halloween! 👻
First #PHTalks Goa speaker: Haidar Kabibo (@haider_kabibo), Kaspersky Lab.
Talk — RedNova: turning an arbitrary file write into privileged code execution via Windows COM.
Dec 10 - Goa - Free:
phtalks.pt.community/goa

Two critical PHP flaws. Protection before the patch. We developed PT Application Firewall rules hours before PHP updates were released, helping clients reduce risk while preparing to patch. See our response timeline below.

Hackers, bug hunters, researchers — we built our new home! Zero marketing fluff, just good stuff:
✅ @ptdbugs: 350K+ free vulns
✅ 0days & breach intel
✅ @StandoffBB: Bug bounties
✅ The world's cybersecurity calendar
👉 pt.community/

One of our business cards had a busy three days at @GISECGlobal
It passed from hand to hand as we talked about what it takes to make digital sovereignty work.
The answer doesn’t fit on a business card. Watch the film.
#GISEC #GISEC2026
#GISEC is a wrap, but we’ve still got DeCode footage to drop 👀
@amoshkov teamed up with @GodfatherOrwa and @XHackerx007 to build a security token, rip into its firmware and trade bug bounty stories
Watch till the end to find out where we’re heading next youtu.be/YJ7LzoMmFQ8


Positive Technologies Global retweeted

Our workshops will start soon
Is on the schedule
4 per day one one cybersecurity talks
Come join us on Gisec!
At The Decode zone
@PTsecurity_EN @ptsecuriy
See you there!
#CyberSecurity #InfoSec #BugBounty #RedTeam
#HackerCommunity #Standoff #GISEC
#GISEC26 #Decode #PT
The Positive Technologies team will be at @GISECGlobal 2026 tomorrow!
📍 Dubai Exhibition Centre (DEC), Expo City
📢 Stand C140, Hall 5
Check out our full GISEC agenda below:
positivegisec.com/?utm_sourc…
#GISEC #GISEC2026

QKS Group has ranked Positive Technologies among the leading vendors in its SPARK Matrix for XDR, highlighting MaxPatrol Endpoint Security and its integration with SIEM, VM, Sandbox, NAD and ISIM. Independent recognition is always welcome—especially when customers agree. 😎 #XDR

Positive Technologies Global retweeted

Long time no post! Back from CSST in Tianjin 🇨🇳
Was really happy to return to the International #AntiVirus #Conference for a 2nd year in a row!
Talked about "Navigating the Ocean of Network Dumps", basically how to triage terabytes of traffic & keep your sanity as an analyst 👩💻


What’s in Positive Technologies’ DeCode zone at @GISECGlobal?
⚙️ Positive Labs: build&hack an USB security token
🎭 DeepFake Reality: see how AI can replicate your identity
🎤 Stand-up talks with @GodfatherOrwa & @XHackerx007 for real-world insights and tips
C140, Hall 5 #GISEC
Positive Technologies Global retweeted

Emad Abu Jazar of Positive Technologies, highlights the evolving threat landscape and the need for organisations to strengthen their defences while securing AI systems, critical infrastructure and cloud environments - securityreviewmag.com/?p=305… @PTsecurity_EN

Positive Technologies Global retweeted

🚨 New #FamousSparrow campaign: meet SquawkDoor
Our Threat Intelligence team at PT ESC has uncovered a new campaign by the East Asian APT group FamousSparrow. The group used a new backdoor we named SquawkDoor, along with an updated version of their known #SparrowDoor backdoor.
🎣 The group injected malicious JS into websites across multiple countries. Visitors saw a fake "certificate error" in their own language, urging them to download a "new certificate." In reality, the file was an MSI installer — and running it infected victims with the backdoors.
🔍 We took a close look at both tools: how SquawkDoor works, what's changed in SparrowDoor, and how they relate to #HemiGate, #TernDoor, and #CrowDoor. We also found several overlaps with other threat actors from East Asia.
🕵️ Separately, we identified a pentester linked to the group who was preparing attacks. Our Medium article reveals what kinds of applications this hacker had targeted before.
Read: medium.com/@dzaripova1177/th…
#Malware #Backdoor #APT #ThreatActor #EarthEstries #SaltTyphoon #GhostEmperor
🤖 Made with AI
Some access reviews are scheduled.
Others call you at 3 a.m.
#Cybertionary

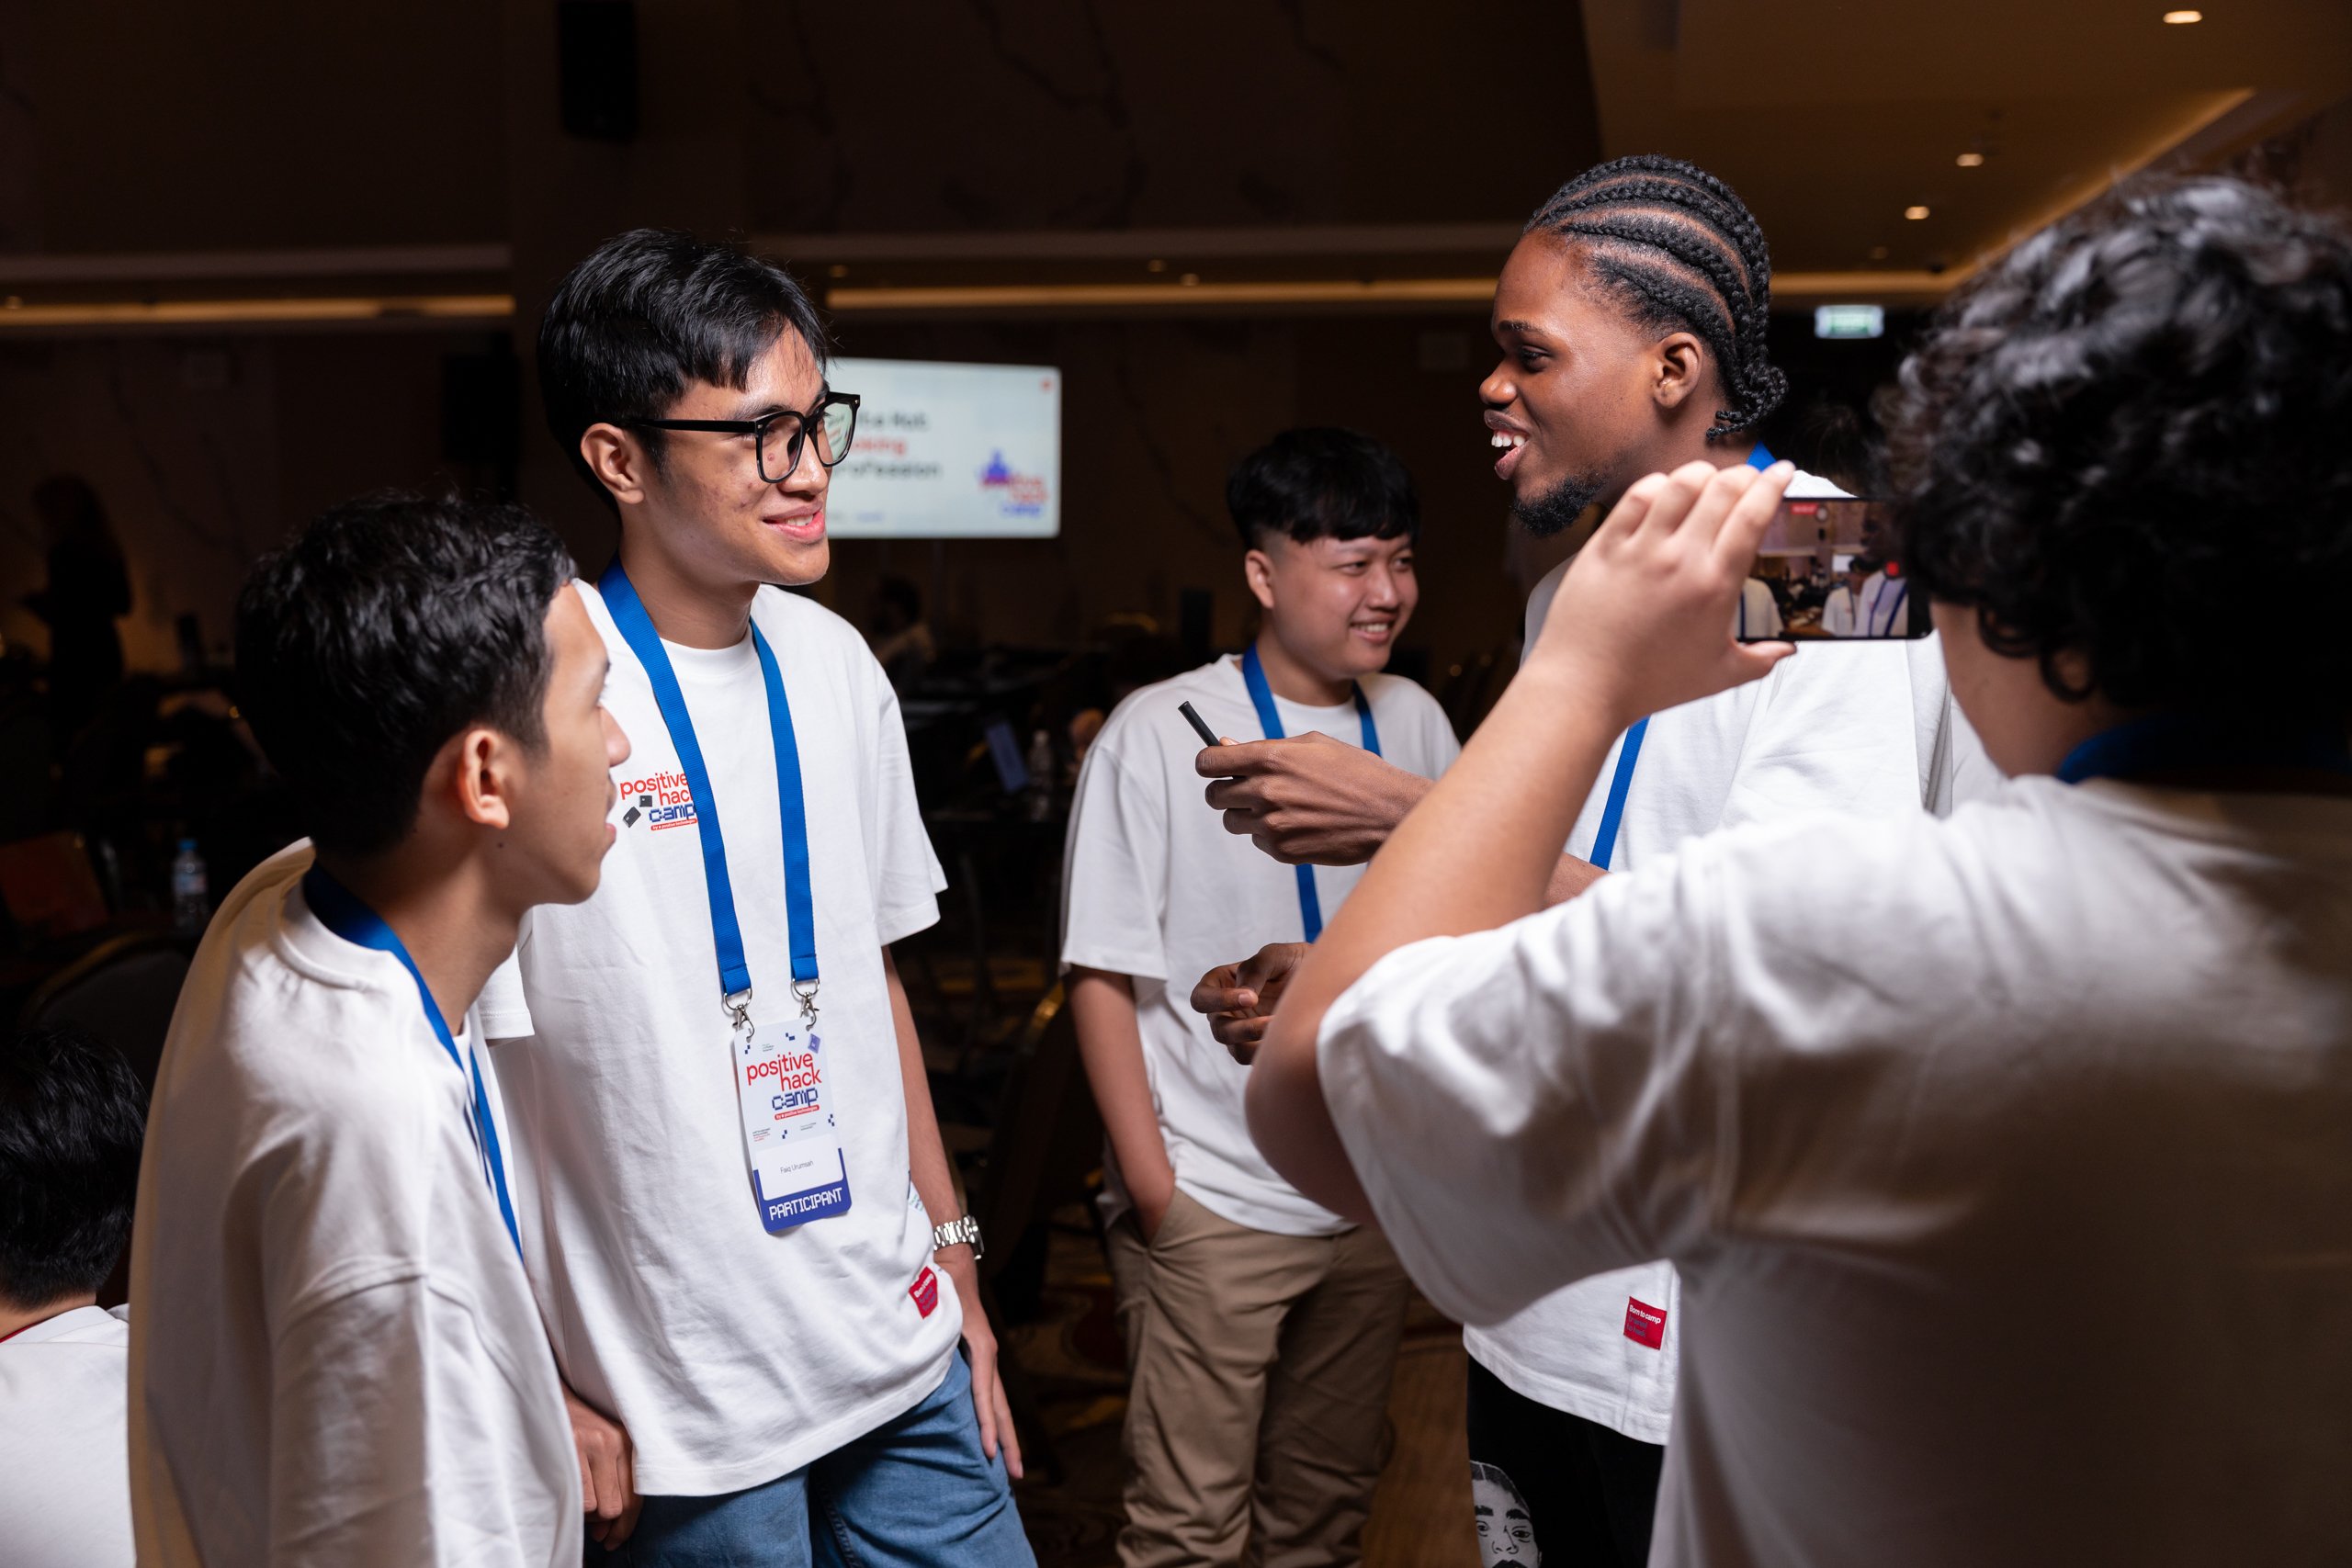
800+ applications.
80+ participants selected.
20 countries represented.
30 hands-on sessions ahead.
#PositiveHackCamp 2026 is officially underway in Moscow 🚀


24M+ sites run PHP. We found where it breaks
@ptswarm found 2 flaws in PHP's core database components. SQL injection (PT-2026-39443, CVSS 8.1) and a null pointer deref that kills the process (PT-2025-52599, CVSS 8.2). SAST won't catch these.
Patch now
dbugs.ptsecurity.com
