

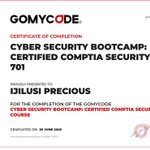
cybersecurity| Offensive | CompTIA Security+| Web Pentesting | C++ & low-level programmer
Lagos, Nigeria
Joined October 2018
- Tweets117
- Following277
- Followers82
- Likes444

percie retweeted
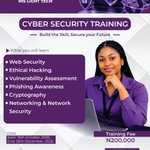
Do you Want to learn how hackers break into systems and how to stop them? His Light Tech is running a hands-on Cyber Security Training for complete beginners. No coding background is needed.
DM or call 08110626106 to secure your spot.
#CyberSecurity #Lagos #TechTraining

Do you Want to learn how hackers break into systems and how to stop them? His Light Tech is running a hands-on Cyber Security Training for complete beginners. No coding background is needed.
DM or call 08110626106 to secure your spot.
#CyberSecurity #Lagos #TechTraining
I Spent the past few weeks building a Python tool that tests APIs for real vulnerabilities, not just flags them. And Here's what it does 🧵
Test 3: JWT forgery; Cracked the server's signing key via wordlist attack (it was "random" 😅)lol,
Then forged a token for the admin account from scratch. No login, no password, full admin access.
Every check goes past "found it" to "here's proof", each one ends by performing a real privileged action using only what the vuln grants.
Full writeups + code here: 👇
github.com/percie1/api-secur…
$APIsec #websec #OWASP #pentesting

The wildest thing I've learned from thid prototype pollutionis you don't always need to control the value an application uses.
Sometimes you only just need to control what happens when the application fails to define one.
Prototype pollution light changed my definition of ‘user-controlled input.’
The attacker doesn't necessarily control the final variable directly.
They can just control the mechanism JavaScript uses to resolve it.
Omoh...
Just discovered prototype pollution and honestly, this vuln is crazy.
You can mess with Object.prototype nd suddenly objects all over the app start inheriting properties you never even gave them.
And the fact that it can turn into XSS, privilege escalation, or even RCE
JS is wild
I Built a small Python quiz game today.
The code worked, but my logic had holes 😂
I learned that "while True" doesn't magically fix your program logic.
You have to understand when to use "continue", "break", "True", and "False".
Today's Python lesson:
A program can run without throwing an error and still have bad logic.
That is the difference between writing code and understanding code.
Tools do not stop breaches, Operators do.
You can have the best SIEM, EDR, firewall, or vulnerability scanner money can buy.
But if nobody knows how to configure it , monitor it, investigate alerts, and respond effectively,
it's just another tool sitting in the stack.
My basic XSS testing workflow now:
1. Find user input
2. Enter a unique test value
3. Check if it's reflected
4. Identify the context
5. Understand how the input is processed
6. Test based on the context
Understanding why something works is much more valuable
spent some time about Cross-Site Scripting (XSS).
How am i just finding XSS isn't just about memorizing payloads.
That the real skill is understanding where your input goes and how the application handles it.
You just never stop learning in this field
#websecurity
AD feels like an entirely different world.
It is less about HTTP requests and more about identities, trust, Kerberos, LDAP, permissions, and how everything connects.
Weeks into Active Directory, The shift is interesting.
Web security taught me to think in terms of requests and responses.
Active Directory is teaching me to think in terms of identities, authentication, trust, and permissions.