





Redge Guardian retweeted

‼️ BREAKING - Google disrupts a 1.3 million-device Android botnet and bans TV box maker Videostrong.
Google says the company deliberately built a backdoor into its devices and sold access to criminals.
The control servers are down. The backdoor is still there.
Full story: thehackernews.com/2026/11/go…

Redge Guardian retweeted

🛡️ W odpowiedzi na utrzymujące się zagrożenie atakami DDoS zaktualizowano rekomendacje dotyczące ochrony dostawców usług internetowych (ISP).
Dokument przygotowany przez Ministerstwo Cyfryzacji we współpracy z UKE i CSIRT NASK zawiera zalecenia, które pomagają zwiększyć poziom cyberbezpieczeństwa i ograniczać skutki cyberataków.
📄Szczegóły: gov.pl/web/cyfryzacja/aktual…
#Cyberbezpieczeństwo #Rekomendacja


Redge Guardian retweeted

Chowanie głowy w piasek i udawanie, że jesteśmy odporni na cyberprzestępstwa nie na wiele się zda. Dotyczy to bynamniej nie tylko branży lokalnych operatorów telekomunikacyjnych. telko.in/udawanie-ze-nikt-ni…

Redge Guardian retweeted

Imagine being able to launch a DDoS attack without knowing how to execute one.
No complex infrastructure. No advanced technical skills. Just a website, a few clicks, and a cryptocurrency payment.
That was NightmareStresser.
One of the longest-running DDoS-for-hire services has now been dismantled, with the FBI seizing its domains in a coordinated international operation.
But here's what makes this case particularly interesting.
When competing services were disrupted in 2018, NightmareStresser grew stronger.
Now it's gone. But the demand for these services hasn't necessarily disappeared with it.
Taking down cybercrime infrastructure can disrupt an entire operation. The question is whether it can prevent another one from taking its place.
We take a closer look at the takedown, the scale of NightmareStresser, and what could come next.
Read the full article: cqureacademy.com/blog/the-ni…
#Cybersecurity #DDoS #CyberCrime #ThreatHuntingCQURE

"Massive DDOS attacks on ISPs – A look into Kimwolf and Aisuru" pretalx.balticnog.org/bnog-2…

78
Redge Guardian retweeted
⚡ U.S. seizes two NightmareStresser domains tied to hundreds of thousands of DDoS attacks and attempts.
The DDoS-for-hire service was assessed to have been used worldwide since 2022.
Operation PowerOFF details → thehackernews.com/2026/09/us…

Redge Guardian retweeted
Cyberprzestępcy wzięli na cel lokalnych operatorów telekomunikacyjnych. telko.in/pan-zabka-wali-ddos…

Redge Guardian retweeted

‼️ UPDATE: LG Electronics says it will suspend smart TV apps that secretly turn hundreds of millions of TVs into residential proxy nodes, after researchers found the proxy SDKs in more than 42% of apps in LG's webOS store and over a quarter of Samsung's Tizen apps, routing unknown third parties' internet traffic through users' home connections.
Residential proxy firms pay developers to bundle these SDKs, then rent the resulting home IP addresses to customers who often use them for large-scale scraping aka stealing your shit (also for AI training).
Proxy nodes are being embedded at scale in hardware people don't treat as computers and can't easily inspect, and LG's cleanup does nothing for Samsung's Tizen store, where the same problem is present.


❗️🚨 An Israeli company has backdoored hundreds of millions of households through countless Smart TV apps, and they're quietly turning Samsung and LG TVs into exit nodes for AI web-scraping. Your TV is relaying strangers' web traffic from your home IP, your bandwidth, your address attached to whatever those scraping jobs touch.
Roku, Fire TV and Google TV banned the practice. Samsung and LG didn't. The culprit is Bright Data's proxy SDK, which rides inside Tizen and webOS apps, 200+ on webOS alone. Datacenter IPs get blocked, home IPs don't.
Include Security reverse-engineered the SDK and found its relay protocol has no message signing, authentication, or device attestation. Their words: less secure than typical malware command-and-control.
To make things worse, they found that in iOS the relay tunnel binds straight to the physical network interface, so it routes around any VPN the user is running.
Bright Data's config also ships per-country tiers. Devices in Uzbekistan and Oman are cleared to relay down to 1% battery, with data caps up to 60x the worldwide default.
Before the BaCkDoOrEd replies land: technically you agreed. In practice you were enrolled into a global proxy network you were never given the information to refuse. And these exit nodes drag down your IP's reputation, potentially leaving you with blocks from providers.


Redge Guardian retweeted

Młodzili dorabiali sobie po szkole. Problem w tym, że wybrali cyberprzestępczą drogę i zapukało do nich CBZC. Najmłodszy członek grupy miał... 12 lat❗️😳
Nieletni oferowali w Internecie usługę odpłatnego przeprowadzanie masowych ataków typu DDoS. Ogłoszenia można było znaleźć np. w mediach społecznościowych.
[Więcej w komentarzu👇]
Fot. CBZC


Redge Guardian retweeted
Dutch authorities have dismantled a botnet comprising at least 17 million infected devices, including computers, smartphones, tablets, and IoT devices.
More than 200 servers in the Netherlands supported the operation. Police seized a subset of the infrastructure, and the hosting provider subsequently took the network offline.
Read: thehackernews.com/2026/05/du…

Redge Guardian retweeted

‼️According to the press release they seized 53 sites, arrested 4 individuals, 21 countries were involved, 25 search warrants were issued, and over 75k users identified.
europol.europa.eu/media-pres…


Redge Guardian retweeted

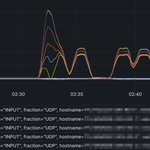
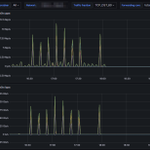
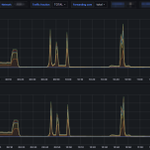
Over the last 24 hours, multiple ISPs using NetSense reached out to us with the same strange pattern.
A noticeable chunk of subscribers suddenly started generating outbound UDP traffic to:
- port 80
- port 443
- and even port 0
Mostly towards a small set of external ASNs / IP ranges.
A few things made this stand out:
→ Upload traffic spiking higher than download
→ Bursts of upload traffic, then pause, then again
→ Same behavior replicated across many users at the same time
→ Different regions of India
→ Very consistent destination patterns
QUIC can explain some UDP/443.
But UDP/80 and especially UDP/0? That’s definitely not normal Internet behavior.
This points strongly towards:
compromised devices at scale: routers, CPEs, IoT, etc which are acting in coordination.
What’s interesting is not just the pattern, but the simultaneity across different networks.
That usually means one of two things:
- a large botnet waking up
- or a new exploit spreading quietly across edge devices
(And yes — having flow visibility helps. Being able to quickly look at NetFlow/IPFIX data and spot patterns like this makes a big difference in response time.)
Now the real question:
Are others seeing this too?
If you operate an ISP / broadband network:
- Any unusual spikes in outbound UDP?
- Traffic hitting port 0?
- Similar destination concentration (specific ASNs / regions)?
Would be useful to compare notes.
Feels like one of those early signals you don’t want to ignore.

Redge Guardian retweeted
Twórcy narzędzi do cyberataków zatrzymani 🚔👇
Funkcjonariusze @PolicjaCBZC zatrzymali osoby zajmujące się tworzeniem, odpłatnym udostępnianiem i handlem oprogramowaniem przeznaczonym do ataków typu #DDoS.
Jeden z nich w ten sposób zarobił ponad 670 tys. zł 👀
👉 Więcej w komentarzu: cyberdefence24.pl/armia-i-sl…
@InfoSecurity_24 @PolskaPolicja


300 Gbit/s DDoS mitigation on a 1U box? Easy, if you have 400Gbit uplink, decent EPYC CPU and Guardian dataplane.

1
260
Redge Guardian retweeted

🚨 Operation Eastwood targets pro-Russian cybercrime network NoName057(16) and shuts down over one hundred criminal servers in global operation.
Read more in our press release ⤵️
europol.europa.eu/media-pres…

Redge Guardian retweeted

🇪🇺 EU intensifies its response to Russian hybrid threats & destabilising activities abroad:
⚠️New restrictive measures against 21 individuals & 6 entities
⚠️Targetting tangible assets linked to malicious activities, such as vessels or real estate
More 👇shorturl.at/DgRU1


Redge Guardian retweeted
💪 Europol just dismantled 6 major DDoS-for-hire services used to launch thousands of global attacks—for as little as €10 a hit.
🔹 4 arrested in Poland
🔹 9 domains seized by the U.S.
🔹 Operation PowerOFF strikes again.
These slick platforms let anyone pay to flood schools, gov sites & gaming servers offline, no tech skills needed.
🔗 Read → thehackernews.com/2025/05/eu…
