

Threat Researcher at @socradar | Malware Researcher | Threat Hunter | CTI ¦ Former @ElevenPaths @Panda_Security 📖Book: https://nitter.cf/t.co/ZmIUPBuNKG
Joined December 2020
- Tweets796
- Following402
- Followers5K
- Likes6.4K




Pinned Tweet
📡New research inside #DarkVision #RAT | #DarkVisionRAT, one of the most capable yet underanalyzed RATs currently active. Available on underground forums since 2020, used by countless #TA ever since
⛓️ #Phishing | Fake link | Fake sw > ZIP/RAR | Other #Malware > #Loader > #DarkVisionRAT > Load Modules/DLL > Priv. Escalation / Persistence / Proc. Injection > #C2 > Add plugins > Steal info + Remote Access
🔎Full research: rexorvc0.com/
#ThreatIntelligence #CTI #Threathunting #Threat


#TTP
📩[T1566.001] Spear-Phishing
📇[T1204.002] XLTM file
📜[T1059.005] VBA Macro
🧩[T1140] Decode/Deob (NOT + XOR)
⚙️[T1106] URLDownloadToFileA
🛡️[T1518.001] Security Software Discovery (driver check)
📥[T1105] Download next stage
🎭[T1036.008] DLL as .mp3/.mp4/.ico
⚓️[T1053.005] Scheduled Task
🧬[T1218.011] Rundll32 execution
🔎[T1082] Discover device info
📦[T1518] Installed software discovery
🔐[T1573.001] AES-128-CBC
📡[T1071.001] C2
📤[T1041] Exfil


#IOC
54715f6d79797cadc8ccbcd8e8bd22d0
2b420e55cacf0a6cdb04f13e6c16c79b
bb24a56a74aef6c04dc6546c531d9dfe
f8a825417341cbbce3f94c5dfda7f4d
95977ade6a6df5dc3abad813490fa855
7cc4698bc503d7e9a0cbe0d340776df1
...
🔗VT: virustotal.com/gui/collectio…
🔗Graph: virustotal.com/graph/ga98b6e…

🚨 New research: KeyHunter Operation & leepsmarts TA 🔑
STRU found an exposed server behind an AI-assisted operation with 247 open LLM gateways mapped, Harvard alumni data processed, Stanford application payment links. Evidence at 20 institutions. 🧵1/3
#ThreatIntelligence #CTI

#TTP
🔎[T1596.005] FOFA/Shodan target seeding
🗝️[T1552.001] Credentials in exposed .env files
🔓[T1078.004] Harvested cloud/LLM API keys
⚡[T1496] LLM compute hijacking
🪪[T1585.002] Bulk e-mail account registration
🧱[T1090] SOCKS5 proxy pools
🎯[T1190] CVE-2026-41940 (staged, no execution seen)
💳[T1657] Card validation + seed-phrase drainer
📡[T1102.002] Telegram as agent control channel
...
🧵2/3


#IOC
209[.]112[.]91[.]74
173[.]231[.]39[.]244
123[.]60[.]2[.]245
14[.]47[.]118[.]194
66[.]42[.]94[.]67
...
🧵3/3
🔗More at: socradar.io/blog/keyhunter-o…

#APT & #TA 2026 mid year global report from QianXin
Summary of attacks by relevant #APT, #Ransomware, etc. Highlights from groups such as #Turla, #APT28, #Bitter, #Lazarus, #OilRig, #Gentlemen, #Interlock and more
🔗Link: ti.qianxin.com/uploads/2026/…
📄Translated Report:
github.com/vc0RExor/Malware-…
#Threat #Campaign #Report #CTI #malware #intel


New extortion campaign, STRU team found a #TA who breached a major Japanese real estate company and pivoted to ~20 other sites via shared hosting.
🪙 Stolen: plaintext passwords, financial data, customer records. Victims extorted via site defacement. The TA shares his findings on social media
We also found a weaponized #PHP2Shell copy (CVE-2026-109618/109619) staged on their server
🔗Full Research: socradar.io/blog/php2shell-w…
#ThreatIntelligence #CTI #CyberSecurity #SupplyChain #DataBreach #InfoSec #Japan #Threat


#TTP
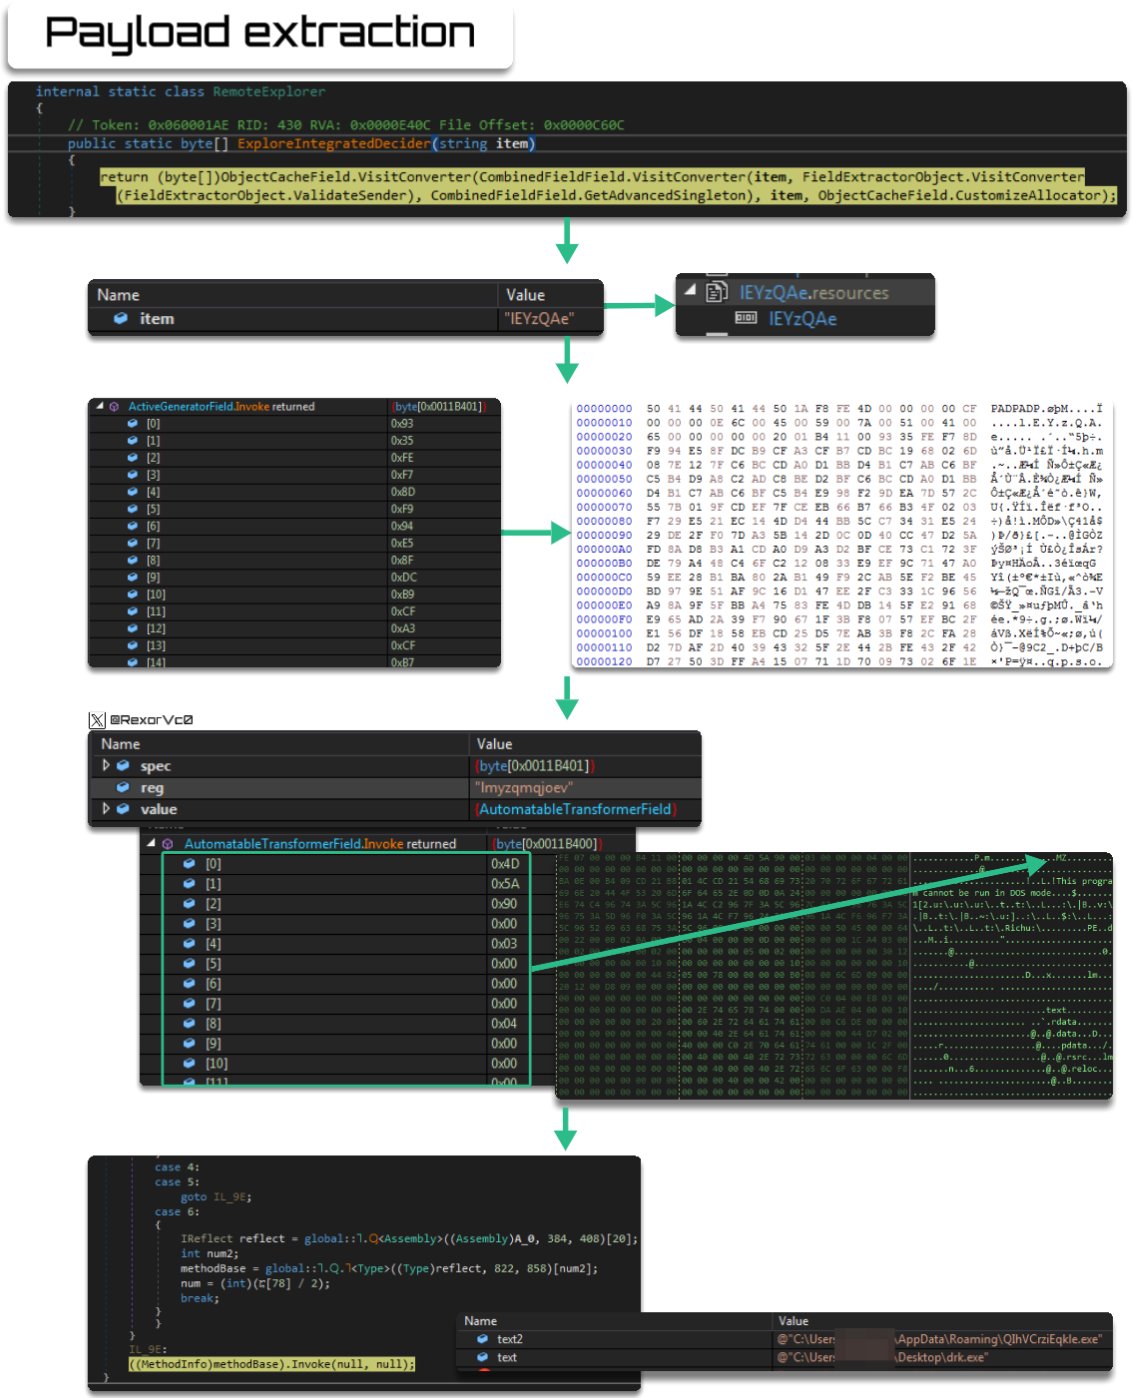
📩[T1566.001] SpearPhishing
📄[T1059.001] PS persistence script
🦠[T1059.003] Shell with cmd.exe as injection
⚓️[T1547.001] Registry Run Keys with obfuscated PowerShell
🛗[T1548.002] COM Elevation Moniker
🧩[T1027] Obfuscated Files or Information
💉[T1055.002] Process Injection
📚[T1555.003] DLL injection into browser process
🔎[T1497] CreateToolhelp32Snapshot in anti-Debug/Analysis thread
🪪[T1082] OS version, local IP, admin status
📤[T1041] WinHTTP POST
📡[T1095] TCP protocol with proprietary framing and handshake


#IOC
2a67ec9b4db3954e30b1fa26fe87dea4f89ce4d011415e00d48f3200c9fe1f88
6700075bf252fbc09453df6f543d36bbd7f7a011ed2b5bf7fc86df1c4b634c8d
B1c7d89f04a4a9a2729f6030b581e5a7cfb2afe766b36c80cfad5ece7ecccfed
Fb76ed9669c3c728806fa4d349e46bcec2e51f474ac829269e3713f3909c051b
70aacb6ae4c62d3913af232c5f67f17f532c8379adfa0d1ab0185620fb62627f
9a0369f05cd24b818b5885b3866643d168f6f4216724641ca540613972e9e682
8edac9f53baffdb318253b4874a7776339c322e46ca88f32c169199556109550
92ad02bd0ce9160a8ad87ffd7fba019a366b4e70056b3e8bd35c706abdb4a2ff
...
🔗More at: rexorvc0.com/
🔗And: virustotal.com/gui/collectio…

🚨 Threat actor unmasked: CyberXero 🎭
STRU has identified a new Russian IAB #TA operating two distinct pipelines targeting critical infrastructure in Ukraine and other countries, alongside WordPress sites worldwide.
Using PentAGI, +50 agents, Cobalt Strike and dedicated #crypto monetization infrastructure and Telegram notification.
👽 Blogpost: socradar.io/blog/cyberxero-a…
🔗 Full report: socradar.io/resources/report…
#ThreatIntelligence #CTI #ThreatResearch #AI #IAB #threat #campaign

#TTP
🔎[T1590.002] Enumeration of domains
🗡️[T1588.005] Exploits usage
🔮[T1078.003] Admin accounts
🧩[T1110.003] Psw spraying
🕷️[T1082] System info discovery
🧲[T1047] Remote exec
👥[T1136.001] Creation of rogue accounts
🪄[T1102.002] TG for real time notification
📡[T1041] Info Exfiltration
...


#IOC
92a789444708fa1cb4cc5a89e0aa6cc7a279b62a7b8a4d2857255a18197d0090
a5ae0aab352871bc0b038b3aa43b03eb223425628c884af7b9fc592cd34eb86c
71e21094c1ac1cf0275c91ed377965e248bca1c12711f6dd20e2682681fc1192
59c535f47ab4d35f6d9fc8b8aec4a72438ea0b89e5a4dcea74b05d2d32cfa483
...
🔗More at: socradar.io/blog/cyberxero-a…

🚨 New Research: VectraRAT 🐀
We at STRU have identified a previously undocumented #RAT operating under the #MaaS model.
The dev has been active for years. This isn't their first build. Previously known as #Nyxel. VectraRAT combines #RAT capabilities with #Stealer functionality, managed through a centralized panel to control multiple victims simultaneously.
Active campaigns confirmed. Victims identified worldwide and #USA among the top targets.
👽 Blogpost: socradar.io/blog/vectrarat-u…
🔗 Full report: socradar.io/resources/whitep…
#ThreatIntelligence #CTI #ThreatHunting #Malware #Threat #TA #Campaign

#TTP
🎣 [T1566.002] Spearphishing via ClickFix lures
📜 [T1059.001] PS execution bypass
🛡️ [T1548.002] UAC Bypass based on UACME #41
👥 [T1134.004] Parent PID Spoofing via computerdefaults.exe
🎭 [T1036.005] Masquerading as Tax lures
🔑 [T1555.003] Credentials theft from browsers
⌨️ [T1056.001] Keylogging
📋 [T1115] Clipboard hijack & crypto address swap
🖥️ [T1219] HVNC hidden desktop session
📡 [T1095] TCP over port 3308
🔄 [T1568] Dynamic C2 update via callback.json


#IOC
e2db5db12564d2a9da7ef3a57aa23d95782f5eaddc8bd35eb7c35ae6b844a0f0
dede8bfb55c2e6479d89b1e73e0712791cf16a7179325804fc4bc13f708d08ae
ddbd636f6dfd475dc0c75bf9f6f873fa35b9062dee9d37b3377ae7b9acdcd0c9
b926cfcd3f4b07fe6001c39f46e40225ff8000411198d13782538d770c54ae5e
bff3583d04f0d5603ced9831eb7c45c1923bd90e2f7d5e5d2b32942d38cf6dc5
c708d413720848f8788f43a4f47ddce016fca9af10c9ba4113f47bf2c9244dc5
[...]
🔗More at: platform.socradar.com/
🔗Full report: socradar.io/resources/whitep…
#APT #APT36 #TransparentTribe #CrimsonRAT #threat #malware
📍🇵🇰
💥🇮🇳🌏
⛓️ #Phishing > #ISO | #ZIP > #LNK (Fake pdf.lnk) > #BAT + cmd.exe > Decoy PDF > Drop in %APPDATA% | Mv LOCALAPPDATA + Self-Delete > Exec payload | RegKey + Startup Persistence > #CrimsonRAT | #Golang #RAT > #C2
🔗360 Advanced Threat Research: mp.weixin.qq.com/s?__biz=MzU…

#TTP
📩[T1566.001] Spear-Phishing
💿[T1553.005] ISO
📇[T1204.002] Mal LNK
⚙️[T1059.003] BAT + cmd.exe
📜[T1059.001] PowerShell
🎭[T1036] Fake PDF and .txt
⚓️[T1547.001] RegKey + Startup Persistence
🧹[T1070.004] Self-delete files
📂[T1083] File & Dir Discovery
📤[T1041] Exfil over C2
📡[T1095] RAT communication


1
3
1,025
#IOC
4c64d98210c7fc53b91ffe8572db9187
411460a835461658ea596a9f52826e65
1d0a37a19233bc64d31f77697247e8f1
72b34401413cd684b7ba0a36f626811b
1b5d96e5b41d9720a4b35919a807bc34
41724f263cac4520874765b11027eaa1
8cd05fd628ed7927871e9dd53d4e613b
43ec61c2a96acef6e36a4b69b8f8e333
...
🔗VT: virustotal.com/gui/collectio…
