Springz (@SpringZ_FSG) profile picture
Joined September 2022
Photo by Springz (@SpringZ_FSG)Photo by Springz (@SpringZ_FSG)Photo by Springz (@SpringZ_FSG)Photo by Springz (@SpringZ_FSG)Photo by Springz (@SpringZ_FSG)Photo by Springz (@SpringZ_FSG)Photo by Springz (@SpringZ_FSG)Photo by Springz (@SpringZ_FSG)Photo by Springz (@SpringZ_FSG)
NIKKE PC launcher incident: calm progress update, with real good news. 🙂 ✅ What's done • Traced the attacker's servers (89.127.233.127 and 89.126.250.172) to one Iceland host, 1984 ehf (RIPE records; reverse DNS shows rented VPS). • Sent evidence-based abuse reports to the host and to the domain registrar (PublicDomainRegistry). • 1984 answered in about a minute (ticket #493052) and says the server is shut down. The email is in the picture, cropped. 🟢 What's good • The official CDN files are clean, and an independent tester's fresh install loaded nothing from the attacker's domain. • So far, nobody has posted evidence of stolen data being misused. Not proof, so stay careful. • Both providers are being asked about related servers and domains, so a proper DNS and firewall block list can follow. 🔜 What to expect next • The registrar reviews the domain (hours to days). A takedown on one side alone can just move the domain, so the registrar matters most. • If the domain gets suspended, I'll confirm it in DNS and registry data before saying so. • Official player guidance from Level Infinite and SHIFT UP is still pending. I'll update the guide when it lands. Known indicators to block at DNS or firewall: insightjs[.]com, analytics.insightjs[.]com, insightjs[.]org, 89.127.233.127, 89.126.250.172. Blocking doesn't clean a PC that already ran the agent: check Launcher\intl_service\debug.log for k2f_chan first. No overnight miracle, but the right pieces are moving. Please don't spam or harass the host or registrar: they're cooperating, and one clear report works better. Credit: MotherSphere's report and everyone who checked and shared evidence. Guide with checks, steps and sources: - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
56
534
22
4,300
270,354
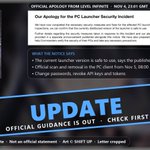
Big news in the NIKKE PC launcher incident: official guidance is out. 🙂 Level Infinite (NIKKE's publisher) just posted an apology and a follow-up notice. Here is what it says, and what it means for you. ✅ What's confirmed • A third party tampered with PC launcher files, and PCs and account data may have been exposed. The scope is still being investigated. • The publisher says the current launcher version is safe to use. Our own checks agree: the official CDN files are clean. • From Nov 5, 08:00 JST (Nov 4, 23:00 GMT) the official PC client scans for the malware and offers to remove it. Close Chrome and other browsers first. • Change the passwords of accounts used on that PC, and revoke API keys and tokens. Compensation is announced, and Customer Support handles losses. 🔍 My tip The official scan deletes what it finds. If you want to keep your evidence, copy Launcher\intl_service\debug.log first (search it for k2f_chan), then run the scan. That's my suggestion, not an official step. Don't wipe or uninstall before checking. 🔜 Still open Scope of the damage, how the CDN was reached, and the manual check guide the publisher promised. The attacker's domain is not suspended yet: my reports are with the host and the registrar. I'll update the guide and say so here when anything changes. Guide with checks, steps and a summary of the official notice: github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
11
28
398
30,641
Update: the official manual check guide is out. English: nitter.cf/NIKKE_en/status/211811… Nuance: the official notice calls the current launcher safe but never explicitly says to reinstall it. If you uninstalled, that's your call. Do the manual check first.
【Manual Security Check Instructions for the PC Launcher】 Commanders, This is the GODDESS OF VICTORY: NIKKE Operations Team. We sincerely apologize for the great concern and distress caused by the recent PC launcher security incident. If you have launched the Windows PC launcher at least once since September 27, 15:41 (UTC+9), we ask that you perform a security check and take any necessary measures. You can complete the security check and necessary actions more conveniently using the security feature (ACE) provided through the official PC client. For instructions on how to use this feature, please refer to the [PC Launcher Security Incident and Follow-Up Measures] announcement. If you do not currently have the PC launcher installed or wish to perform a security check without using the launcher, please refer to the instructions below and follow the recommended steps. This security incident was limited to the PC launcher and did not affect the mobile version of the game. Therefore, Commanders who have only played the mobile version do not need to take any additional security measures related to this incident. For detailed instructions and important precautions, please refer to the official website: nikke-en.com/newsdetail.html… If you continue to experience any unusual activity even after completing all the steps above, please contact our Customer Support team. Once again, we sincerely apologize for the additional burden and inconvenience of having to carry out these security checks yourself. #NIKKE
17
1,026
Sources, official posts: • Korean follow-up measures notice: nitter.cf/NIKKE_kr/status/211811… • SHIFT UP's Kim Hyung-tae on the launcher update: nitter.cf/jamm3rd/status/2118119… • Level Infinite's English apology: nitter.cf/NIKKE_en/status/211811…
【Our Apology for the PC Launcher Security Incident】
3
2,346
【PC Launcher Security Incident and Follow-Up Measures】 We have identified that some files in the NIKKE Windows PC launcher were recently tampered with by a third party, potentially allowing malicious programs to run when the launcher was launched. As a result, your PCs and account information may have been exposed to security risks. We are continuing to investigate the extent of the potential damage and review appropriate response measures. We are also conducting a thorough review of our network security environment, including our CDN, to determine how the PC launcher files were compromised. We will take all necessary precautions to prevent further damage and ensure that this issue does not happen again. We deeply regret that this security incident has caused Commanders significant concern and distress, when our responsibility should have been to provide a safe gaming environment. We take full responsibility for failing to uphold your trust and sincerely apologize. The following details will be provided on our official website: - A summary of the key developments and actions taken based on the information confirmed so far - Instructions on how to perform security checks, protect your accounts, and report any loss - Strengthening security to prevent future incidents For more details: nikke-en.com/newsdetail.html… If you believe you may have been affected by this issue or sufferred from any loss, please contact our Customer Support team. We will review each inquiry carefully and respond as promptly as possible. Once again, we sincerely apologize for the great concern and distress this incident has caused. Level Infinite
138
353
42
2,703
291,134
Apenas pra complementar, fiz esse passo a passo aqui: Fazer varredura completa no sistema Desinstalar o Nikke Excluir o instalador do jogo Reiniciar o PC Baixar novo instalador Reinstalar do zero. Feito isso tudo, ao abrir o arquivo de debug na pasta do Launcher, a k2f some.
NIKKE PC launcher incident: calm progress update, with real good news. 🙂 ✅ What's done • Traced the attacker's servers (89.127.233.127 and 89.126.250.172) to one Iceland host, 1984 ehf (RIPE records; reverse DNS shows rented VPS). • Sent evidence-based abuse reports to the host and to the domain registrar (PublicDomainRegistry). • 1984 answered in about a minute (ticket #493052) and says the server is shut down. The email is in the picture, cropped. 🟢 What's good • The official CDN files are clean, and an independent tester's fresh install loaded nothing from the attacker's domain. • So far, nobody has posted evidence of stolen data being misused. Not proof, so stay careful. • Both providers are being asked about related servers and domains, so a proper DNS and firewall block list can follow. 🔜 What to expect next • The registrar reviews the domain (hours to days). A takedown on one side alone can just move the domain, so the registrar matters most. • If the domain gets suspended, I'll confirm it in DNS and registry data before saying so. • Official player guidance from Level Infinite and SHIFT UP is still pending. I'll update the guide when it lands. Known indicators to block at DNS or firewall: insightjs[.]com, analytics.insightjs[.]com, insightjs[.]org, 89.127.233.127, 89.126.250.172. Blocking doesn't clean a PC that already ran the agent: check Launcher\intl_service\debug.log for k2f_chan first. No overnight miracle, but the right pieces are moving. Please don't spam or harass the host or registrar: they're cooperating, and one clear report works better. Credit: MotherSphere's report and everyone who checked and shared evidence. Guide with checks, steps and sources: - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
1
1
473
A security warning inside the NIKKE launcher does NOT prove your PC was hacked. That warning comes from a page at insightjs[.]org that went up on Nov 3, after the incident was already public. The researcher's report says the page calls itself an independent notice. It shows up when the launcher's modified script can't reach the attacker's server. Block the attacker's address, or have their server go offline, and you see it. So the warning means one thing: the modified script loaded. That's exposure to the first stage, not proof the remote-control program ran. And no warning doesn't mean you're fine either. The real check is debug.log. Search it for k2f_chan before you uninstall or wipe anything. Calm. Check first. Then decide: github.com/SpringZali/nikke-…
10
6
1
143
20,416
Good news to follow up: nitter.cf/SpringZ_FSG/status/211…
NIKKE PC launcher incident: calm progress update, with real good news. 🙂 ✅ What's done • Traced the attacker's servers (89.127.233.127 and 89.126.250.172) to one Iceland host, 1984 ehf (RIPE records; reverse DNS shows rented VPS). • Sent evidence-based abuse reports to the host and to the domain registrar (PublicDomainRegistry). • 1984 answered in about a minute (ticket #493052) and says the server is shut down. The email is in the picture, cropped. 🟢 What's good • The official CDN files are clean, and an independent tester's fresh install loaded nothing from the attacker's domain. • So far, nobody has posted evidence of stolen data being misused. Not proof, so stay careful. • Both providers are being asked about related servers and domains, so a proper DNS and firewall block list can follow. 🔜 What to expect next • The registrar reviews the domain (hours to days). A takedown on one side alone can just move the domain, so the registrar matters most. • If the domain gets suspended, I'll confirm it in DNS and registry data before saying so. • Official player guidance from Level Infinite and SHIFT UP is still pending. I'll update the guide when it lands. Known indicators to block at DNS or firewall: insightjs[.]com, analytics.insightjs[.]com, insightjs[.]org, 89.127.233.127, 89.126.250.172. Blocking doesn't clean a PC that already ran the agent: check Launcher\intl_service\debug.log for k2f_chan first. No overnight miracle, but the right pieces are moving. Please don't spam or harass the host or registrar: they're cooperating, and one clear report works better. Credit: MotherSphere's report and everyone who checked and shared evidence. Guide with checks, steps and sources: - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
666
NIKKE launcher update: the attacker's server was a rented VPS at 1984 ehf (Iceland), not a VPN. It was reportedly shut down on Nov 3, but the domain's DNS is still hosted there, so I'm sending an abuse report. Please don't spam or harass anyone: a host isn't the attacker.
5
6
159
16,158
Good news to follow up: nitter.cf/SpringZ_FSG/status/211…
NIKKE PC launcher incident: calm progress update, with real good news. 🙂 ✅ What's done • Traced the attacker's servers (89.127.233.127 and 89.126.250.172) to one Iceland host, 1984 ehf (RIPE records; reverse DNS shows rented VPS). • Sent evidence-based abuse reports to the host and to the domain registrar (PublicDomainRegistry). • 1984 answered in about a minute (ticket #493052) and says the server is shut down. The email is in the picture, cropped. 🟢 What's good • The official CDN files are clean, and an independent tester's fresh install loaded nothing from the attacker's domain. • So far, nobody has posted evidence of stolen data being misused. Not proof, so stay careful. • Both providers are being asked about related servers and domains, so a proper DNS and firewall block list can follow. 🔜 What to expect next • The registrar reviews the domain (hours to days). A takedown on one side alone can just move the domain, so the registrar matters most. • If the domain gets suspended, I'll confirm it in DNS and registry data before saying so. • Official player guidance from Level Infinite and SHIFT UP is still pending. I'll update the guide when it lands. Known indicators to block at DNS or firewall: insightjs[.]com, analytics.insightjs[.]com, insightjs[.]org, 89.127.233.127, 89.126.250.172. Blocking doesn't clean a PC that already ran the agent: check Launcher\intl_service\debug.log for k2f_chan first. No overnight miracle, but the right pieces are moving. Please don't spam or harass the host or registrar: they're cooperating, and one clear report works better. Credit: MotherSphere's report and everyone who checked and shared evidence. Guide with checks, steps and sources: - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
2
2,343
Another user report, folks: the warning screen AND the k2f lines on their PC. I'm NOT hiding it. That's why I say PAUSE THE LAUNCHER. And he's right: Shift Up should post an official statement. NOW. Until then: stay calm, no random fixes. SAD!
Replying to @SpringZ_FSG
I actually got this screenshot around 11 am pacific time on my pc, following the instructions on the github post i got the “k2f_chan” on the debug log of my cache folder. If this is a false flag the least @NIKKE_en could do is to post an official statement.
10
6
1
229
19,592
Good news to follow up: nitter.cf/SpringZ_FSG/status/211…
NIKKE PC launcher incident: calm progress update, with real good news. 🙂 ✅ What's done • Traced the attacker's servers (89.127.233.127 and 89.126.250.172) to one Iceland host, 1984 ehf (RIPE records; reverse DNS shows rented VPS). • Sent evidence-based abuse reports to the host and to the domain registrar (PublicDomainRegistry). • 1984 answered in about a minute (ticket #493052) and says the server is shut down. The email is in the picture, cropped. 🟢 What's good • The official CDN files are clean, and an independent tester's fresh install loaded nothing from the attacker's domain. • So far, nobody has posted evidence of stolen data being misused. Not proof, so stay careful. • Both providers are being asked about related servers and domains, so a proper DNS and firewall block list can follow. 🔜 What to expect next • The registrar reviews the domain (hours to days). A takedown on one side alone can just move the domain, so the registrar matters most. • If the domain gets suspended, I'll confirm it in DNS and registry data before saying so. • Official player guidance from Level Infinite and SHIFT UP is still pending. I'll update the guide when it lands. Known indicators to block at DNS or firewall: insightjs[.]com, analytics.insightjs[.]com, insightjs[.]org, 89.127.233.127, 89.126.250.172. Blocking doesn't clean a PC that already ran the agent: check Launcher\intl_service\debug.log for k2f_chan first. No overnight miracle, but the right pieces are moving. Please don't spam or harass the host or registrar: they're cooperating, and one clear report works better. Credit: MotherSphere's report and everyone who checked and shared evidence. Guide with checks, steps and sources: - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
144
Follow-up to the post above. IMPORTANT: please read before you do anything to your PC. 🚨 Shift Up still hasn't confirmed what's going on with the NIKKE PC launcher. Please pause the launcher and wait. That's all you need to do right now. Note on the post above: it's from earlier today, and the public analysis has since added reports from other victims, so the "one PC" line is outdated. One more reason to wait for the official word. But there's a second problem, and it's real 👇 Panic is being used against people. I'm hearing from people in the community, especially the Asian community, that scammers are already sharing suspicious GitHub links, "fixes" and "cleaners" to scared players. I can't verify every report, but it's a well-known trick, so be careful. Please: • Don't download or run anything you don't understand • Don't follow a guide step by step just because it's going around • If you're not sure what a step does, don't do it. Ask someone you trust first. You can ask me too • Simple checks, like opening a log file to read it, are fine. Deleting system files or running downloaded tools is where people get hurt • If you already ran something you're unsure about, disconnect from the internet and ask for help before doing anything else Two facts to hold on to: 1) Shift Up has not confirmed anything yet 2) Some people may end up infected by fake "fixes" installed in a panic, which makes it harder to tell what is actually going on I don't know how big this is, and nobody else does yet. Waiting costs you nothing. Running the wrong thing can cost you a lot. Pause the launcher. Stay calm. Wait for the official word. I'll update here the moment there's news. Repost so more people see this.
Everyone, let's slow down for a second. The Nikke PC "supply chain attack" has ZERO official confirmation. Not from Level Infinite. Not from Shift Up. Nothing. What it does have: one PC. A few screenshots. A string to search for in a log file. No malware sample. No file hashes. No technical proof anyone can verify. Panic spreads faster than facts. Don't be part of it. Here's what we actually know 👇
Readers added context they thought people might want to know
Multiple independent analyses confirm modified official Level Infinite CDN files for the NIKKE PC launcher since Sep 2026, enabling a remote access tool with specific IOCs like "k2f_chan" logs; no official statement from Shift Up or Level Infinite. gist.github.com/MotherSphere/d… nikke.gg/how-to-check-i… github.com/WormW/nikke_ma…
24
64
6
622
78,304
Good news to follow up: nitter.cf/SpringZ_FSG/status/211…
NIKKE PC launcher incident: calm progress update, with real good news. 🙂 ✅ What's done • Traced the attacker's servers (89.127.233.127 and 89.126.250.172) to one Iceland host, 1984 ehf (RIPE records; reverse DNS shows rented VPS). • Sent evidence-based abuse reports to the host and to the domain registrar (PublicDomainRegistry). • 1984 answered in about a minute (ticket #493052) and says the server is shut down. The email is in the picture, cropped. 🟢 What's good • The official CDN files are clean, and an independent tester's fresh install loaded nothing from the attacker's domain. • So far, nobody has posted evidence of stolen data being misused. Not proof, so stay careful. • Both providers are being asked about related servers and domains, so a proper DNS and firewall block list can follow. 🔜 What to expect next • The registrar reviews the domain (hours to days). A takedown on one side alone can just move the domain, so the registrar matters most. • If the domain gets suspended, I'll confirm it in DNS and registry data before saying so. • Official player guidance from Level Infinite and SHIFT UP is still pending. I'll update the guide when it lands. Known indicators to block at DNS or firewall: insightjs[.]com, analytics.insightjs[.]com, insightjs[.]org, 89.127.233.127, 89.126.250.172. Blocking doesn't clean a PC that already ran the agent: check Launcher\intl_service\debug.log for k2f_chan first. No overnight miracle, but the right pieces are moving. Please don't spam or harass the host or registrar: they're cooperating, and one clear report works better. Credit: MotherSphere's report and everyone who checked and shared evidence. Guide with checks, steps and sources: - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
107
UPDATE on the NIKKE PC launcher: a step forward. NIKKE's official account posted a notice. What it says: • They identified an anomaly indicating the launcher's script files may have been tampered with by a third party. • In response, they pushed client fixes and updates around 02:30 on Nov 4. • They're investigating the scope of impact and will share guidance in a separate notice. Credit where it's due: they acknowledged it, apologized, and shipped a fix. So my zero official confirmation post is now outdated. Facts changed, so here's my update. Still missing: what was accessed, who was affected, and what players should do. That's what the guidance notice is for, and they say it's coming. Personally, I'm re-downloading the launcher and getting back into the game now that the client fix is out. That's my own call, not an all-clear. If you'd rather wait for Shift Up's guidance first, that's a perfectly good choice, no judgment. Two simple rules meanwhile: no random "fixes" from strangers, and if your debug.log shows k2f_chan lines, change your passwords from a clean device. No panic. Just facts, and I'll keep updating.
Everyone, let's slow down for a second. The Nikke PC "supply chain attack" has ZERO official confirmation. Not from Level Infinite. Not from Shift Up. Nothing. What it does have: one PC. A few screenshots. A string to search for in a log file. No malware sample. No file hashes. No technical proof anyone can verify. Panic spreads faster than facts. Don't be part of it. Here's what we actually know 👇
Readers added context they thought people might want to know
Multiple independent analyses confirm modified official Level Infinite CDN files for the NIKKE PC launcher since Sep 2026, enabling a remote access tool with specific IOCs like "k2f_chan" logs; no official statement from Shift Up or Level Infinite. gist.github.com/MotherSphere/d… nikke.gg/how-to-check-i… github.com/WormW/nikke_ma…
12
16
397
31,342
Good news to follow up: nitter.cf/SpringZ_FSG/status/211…
NIKKE PC launcher incident: calm progress update, with real good news. 🙂 ✅ What's done • Traced the attacker's servers (89.127.233.127 and 89.126.250.172) to one Iceland host, 1984 ehf (RIPE records; reverse DNS shows rented VPS). • Sent evidence-based abuse reports to the host and to the domain registrar (PublicDomainRegistry). • 1984 answered in about a minute (ticket #493052) and says the server is shut down. The email is in the picture, cropped. 🟢 What's good • The official CDN files are clean, and an independent tester's fresh install loaded nothing from the attacker's domain. • So far, nobody has posted evidence of stolen data being misused. Not proof, so stay careful. • Both providers are being asked about related servers and domains, so a proper DNS and firewall block list can follow. 🔜 What to expect next • The registrar reviews the domain (hours to days). A takedown on one side alone can just move the domain, so the registrar matters most. • If the domain gets suspended, I'll confirm it in DNS and registry data before saying so. • Official player guidance from Level Infinite and SHIFT UP is still pending. I'll update the guide when it lands. Known indicators to block at DNS or firewall: insightjs[.]com, analytics.insightjs[.]com, insightjs[.]org, 89.127.233.127, 89.126.250.172. Blocking doesn't clean a PC that already ran the agent: check Launcher\intl_service\debug.log for k2f_chan first. No overnight miracle, but the right pieces are moving. Please don't spam or harass the host or registrar: they're cooperating, and one clear report works better. Credit: MotherSphere's report and everyone who checked and shared evidence. Guide with checks, steps and sources: - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
121
Everyone, let's slow down for a second. The Nikke PC "supply chain attack" has ZERO official confirmation. Not from Level Infinite. Not from Shift Up. Nothing. What it does have: one PC. A few screenshots. A string to search for in a log file. No malware sample. No file hashes. No technical proof anyone can verify. Panic spreads faster than facts. Don't be part of it. Here's what we actually know 👇
Readers added context they thought people might want to know
Multiple independent analyses confirm modified official Level Infinite CDN files for the NIKKE PC launcher since Sep 2026, enabling a remote access tool with specific IOCs like "k2f_chan" logs; no official statement from Shift Up or Level Infinite. gist.github.com/MotherSphere/d… nikke.gg/how-to-check-i… github.com/WormW/nikke_ma…
158
178
40
2,080
476,685
Good news to follow up: nitter.cf/SpringZ_FSG/status/211…
NIKKE PC launcher incident: calm progress update, with real good news. 🙂 ✅ What's done • Traced the attacker's servers (89.127.233.127 and 89.126.250.172) to one Iceland host, 1984 ehf (RIPE records; reverse DNS shows rented VPS). • Sent evidence-based abuse reports to the host and to the domain registrar (PublicDomainRegistry). • 1984 answered in about a minute (ticket #493052) and says the server is shut down. The email is in the picture, cropped. 🟢 What's good • The official CDN files are clean, and an independent tester's fresh install loaded nothing from the attacker's domain. • So far, nobody has posted evidence of stolen data being misused. Not proof, so stay careful. • Both providers are being asked about related servers and domains, so a proper DNS and firewall block list can follow. 🔜 What to expect next • The registrar reviews the domain (hours to days). A takedown on one side alone can just move the domain, so the registrar matters most. • If the domain gets suspended, I'll confirm it in DNS and registry data before saying so. • Official player guidance from Level Infinite and SHIFT UP is still pending. I'll update the guide when it lands. Known indicators to block at DNS or firewall: insightjs[.]com, analytics.insightjs[.]com, insightjs[.]org, 89.127.233.127, 89.126.250.172. Blocking doesn't clean a PC that already ran the agent: check Launcher\intl_service\debug.log for k2f_chan first. No overnight miracle, but the right pieces are moving. Please don't spam or harass the host or registrar: they're cooperating, and one clear report works better. Credit: MotherSphere's report and everyone who checked and shared evidence. Guide with checks, steps and sources: - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… - github.com/SpringZali/nikke-… Follow me and star the repo to get updates.
1
135
Springz retweeted
More harm was likely done by telling panicked people to reformat their drives... In an enterprise environment, during a security incident, you should just unplug your device from the network and wait for cyber to investigate. Or in this case, wait for a patch. Some folks probably lost pictures of the late beloved granny. Losing customer data is a huge no, no. That said, we aren't in an enterprise environment. So 🤷‍♂️. Kudos to the folks that did sound the alarm early though.
2
2
12
76
Texas voter: I want to have a leader who I can trust. Q: So who do you trust? Texas voter: I'm actually conservative, but I'm voting for Talarico.
155
747
17
13,437
726,657
Midterms are mostly in the books and a lot changed. I'm not cheering and I'm not panicking. My rule: judge the person, not the jersey. I'll watch what the winners actually do. Thread on why I'm curious about Texas.
2
1
102
144,242
6/ Want to do this together? Pick one person you're unsure about and look up their record: votes, past posts, who they work with, what they've actually done. Drop your sources below. Let's compare notes calmly. No points for yelling.
1
1
36
7/ People voted for different reasons, and most were thinking about their own lives, not a team. I'm not here to fight anyone. If you disagree, tell me why, with a source if you can. I'll read it.
1
33