

Cybersecurity Chronicles 🌐 | Breaking down the latest in security news, #hacking #darkweb #Cybersecurity #InfoSec #HackingNews
Planet Earth
Joined January 2024
- Tweets2.5K
- Following6
- Followers1.1K
- Likes34





Once or twice a year, Phrack drops and half of infosec loses a weekend. Issue 73 has sandbox escapes, metamorphic compilers, and a history of the 2000 SSH1 exploit. Which talk are you starting with?.


41
🚨 Admin Takeover in Tensei Framework (CVE-2026-129552, CVSS 9.8)
Static hardcoded JWT secret combined with arbitrary role injection lets unauthenticated attackers mint admin tokens.
⚡ Action: Upgrade @tensei/auth past v0.11.5.
thehackerwire.com/vulnerabil…
#NodeJS #AppSec

2
5
207
🚨 Critical RCE in Dassault 3DEXPERIENCE (CVE-2026-93664, CVSS 10.0)
Deserialization flaw & 2 command injections in Station Launcher App allow remote code execution.
⚡ Action: Apply vendor security updates now.
thehackerwire.com/vulnerabil…
#AppSec #InfoSec
🚨 RCE in WordPress Estatik Plugin (CVE-2026-125795, CVSS 9.8)
Improper include/require control allows unauthenticated remote attackers to execute arbitrary PHP code and seize site control.
⚡ Action: Update Estatik to >= v4.3.7.
thehackerwire.com/vulnerabil…
#WordPress #BugBounty

12
781
The Tor Project has released an emergency security update, version 0.4.9.17, in response to an ongoing distributed denial-of-service (DDoS) attack affecting most relay TOR operators across its network.

A brief note on the ongoing DDoS attack that is targeting HSDir relays: We have issued an emergency release and ask relay operators to update to Tor 0.4.9.17 as soon as possible. forum.torproject.org/t/secur…
While the attack can make some Onion Services harder to reach, with current measurements showing some slowdown, we have not observed widespread disruption. We have no evidence that the attack has deanonymized users or compromised their anonymity.

144
🚨 Auth Bypass in Cyrus SASL (CVE-2026-129483, CVSS 9.3) - PoC Out
Sending A = N forces a zero shared key in SRP mechanism, allowing attackers to log in as any user without credentials.
⚡ Action: Update Cyrus SASL packages now.
thehackerwire.com/vulnerabil…
#Linux #InfoSec

1
8
456
🚨 Top 10 Critical CVEs This Week (CVSS 8.8–10.0)
Key threats disclosed:
• Apache HTTP: Pre-auth RCE
• Netcore Router: CVSS 10.0 (CISA KEV)
• Azure SRE: IMDS token SSRF
• IBM Maximo AI: Code exec
📌 Bookmark for patch triage.
#Cybersecurity #ThreatIntel

125
🚨 RCE in DrayTek Vigor Routers (CVE-2026-129453, CVSS 9.9) - PoC Out
Heap overflow in mainfunction.cgi allows remote code execution on edge perimeter routers.
⚡ Action: Restrict WAN access; patch firmware >= 1.5.1.7.
thehackerwire.com/vulnerabil…
#NetworkSecurity #InfoSec
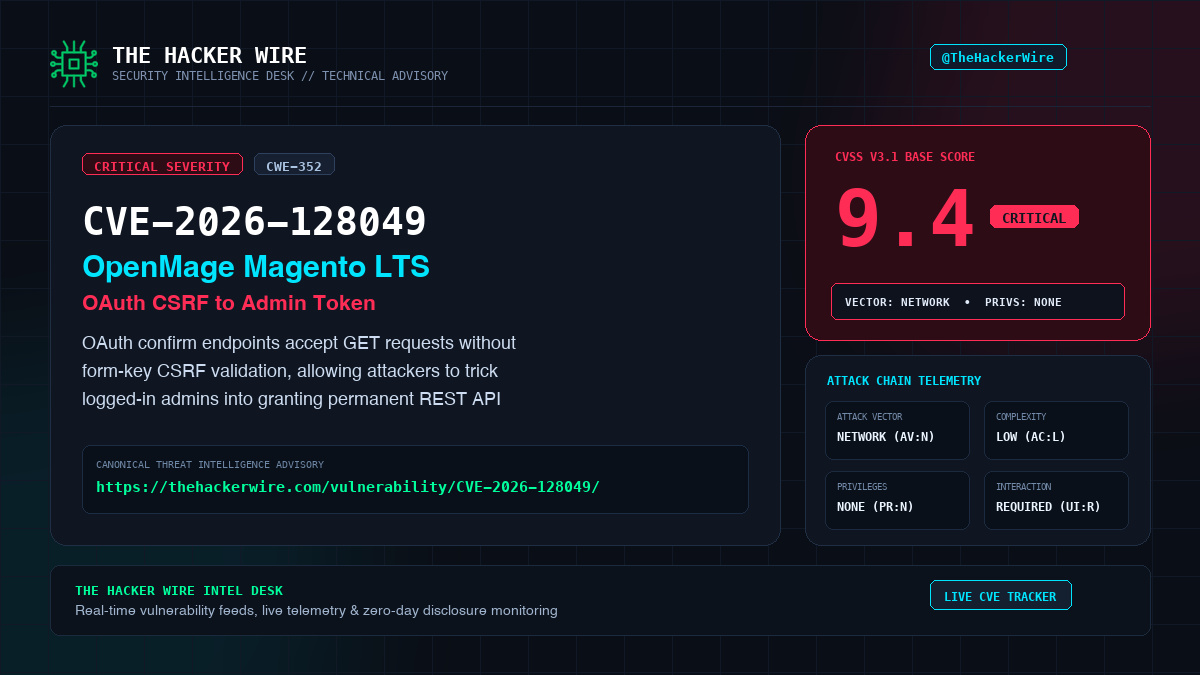
🚨 OAuth CSRF in OpenMage Magento LTS (CVE-2026-128049, CVSS 9.4)
GET confirm flaw lets attackers trick logged-in admins into authorizing OAuth tokens, gaining permanent REST API access to stores.
⚡ Action: Update to >= v20.18.2.
thehackerwire.com/vulnerabil…
#Ecommerce #AppSec
🚨 Admin Takeover in WWBN AVideo (CVE-2026-126542, CVSS 9.8)
Matching OAuth display names without email checks lets attackers log in as admin via Twitter/LinkedIn without a password.
⚡ Action: Update AVideo to >= 29.8.
thehackerwire.com/vulnerabil…
#OpenSource #WebSec

1
2
263
🚨 Unauth API in AsiaInfo BSS (CVE-2026-125297, CVSS 9.8)
Flawed API accepts unauthenticated requests, letting remote attackers create admin accounts & hijack telecom systems.
⚡ Action: Update to >= 9.2.41.
thehackerwire.com/vulnerabil…
#Telecom #NetSec

1
143
🚨 Auth Gate Bypass in Algernon (CVE-2026-68548, CVSS 9.4)
Case-sensitive prefix matching fails on NTFS & APFS disks. Requests for /Admin evade security checks to execute protected Lua scripts.
⚡ Action: Update to >= v1.17.10.
thehackerwire.com/vulnerabil…
#Golang #AppSec

🚨 Backdoor & Root RCE in Copeland XWEB (CVE-2026-124004+)
Industrial refrigeration servers contain hardcoded admin password (xwebevonewgeneration) & pre-auth root RCE. Zero patch (EoL).
⚡ Action: Remove from WAN immediately.
thehackerwire.com/vulnerabil…
#IoT #ICS

183
🚨 Buffer State Hijacking in Zephyr RTOS (CVE-2026-82391, CVSS 9.1)
HTTP/2 static file serving replaces receive buffer bounds, corrupting the frame parser state machine to hijack IoT devices.
⚡ Action: Update Zephyr RTOS now.
thehackerwire.com/vulnerabil…
#IoT #Embedded

3
3
366
🚨 Auth Bypass in Arista EOS RIPv2 (CVE-2026-121367, CVSS 9.6)
Silent RIPv2 exposure on management interfaces lets adjacent attackers inject routes & hijack network traffic.
⚡ Action: Update Arista EOS firmware.
thehackerwire.com/vulnerabil…
#NetOps #Routing

1
174
🚨 Stack Overflow in Arista EOS BGP (CVE-2026-121289, CVSS 9.8)
Crafted packets crash the BGP daemon, tearing down sessions & allowing remote code execution on core routers.
⚡ Action: Apply Arista EOS hotfix.
thehackerwire.com/vulnerabil…
#Arista #NetSec

🚨 Missing Auth in Ivanti CSA (CVE-2026-121683, CVSS 9.4)
Unauthenticated remote attackers can add & delete trusted EPM certificates in CSA 5.0.8, hijacking gateway trust.
⚡ Action: Apply latest Ivanti CSA patch.
thehackerwire.com/vulnerabil…
#Ivanti #NetSec

2
2
401
🛡️ Daily Security Brief — Nov 14, 2026
Tracking 6 IBM API Connect critical disclosures:
• Auth Bypass: Crypto signature failure (CVE-2026-17301, 9.8)
• File Read: Definition SSRF (CVE-2026-17299, 9.6)
Tracker: thehackerwire.com/vulnerabil…
#ThreatIntel #InfoSec

🚨 K8s Container Escape in BuildPiper (CVE-2026-127080, CVSS 9.4)
Improper checks let deploy users mount hostPath: / read-write, breaking container isolation to hijack nodes & entire clusters.
⚡ Action: Update to >= v2.7.0 now.
thehackerwire.com/vulnerabil…
#Kubernetes #DevOps

🚨 Critical Cloud SSRF in IBM API Connect (CVE-2026-17298, CVSS 9.9)
Server request processing flaw lets remote attackers pivot across cloud boundaries to compromise backends!
⚡ Action: Update to 12.1.2.0 immediately.
thehackerwire.com/vulnerabil…
#CloudSecurity #API

157