

Award-winning managed IT, cybersecurity, cloud & secure AI for UK SMEs and the mid-market. Cyber Essentials to Copilot, done properly. Always-on support.
London, UK
Joined February 2011
- Tweets3.4K
- Following1.5K
- Followers4.3K
- Likes522




Pinned Tweet
6 things every UK SME should have locked down this year:
1. MFA on every admin account, not just email
2. Immutable, tested backups (test the restore, not just the backup)
3. Cyber Essentials as a baseline, not a badge
4. An incident plan people have actually read
5. AI with guardrails: know what Copilot and chatbots can access before you roll them out
6. Someone whose job it is to own all of the above
Save this. Stuck on #6? That's us.
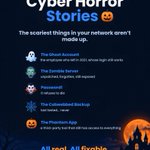
Tomorrow is Halloween and the last day of Cyber Awareness Month. Forget ghosts and ghouls, these are the monsters actually lurking in most business networks. All five are real and common. The reassuring bit: all five are fixable. Which one is haunting yours? 🎃

That's Cyber Awareness Month: phishing, MFA, ransomware, and handling an incident. If you take one thing into November, make it this: pick the single biggest gap and close it. Not sure where that is? That's what our free cyber health check is for. What will you fix first?
The most valuable hour after an incident is the one most firms skip: the honest review. What got in, what slowed the response, what we'll change. Without it, you patch the one hole and get caught the same way next time. Do you capture the lesson, or just move on?
In an incident, how you communicate matters as much as the fix. Staff need to know what to do, customers need honesty, and if personal data is involved the ICO gives you 72 hours to report. Silence and spin both make it worse. Would your team know who speaks, and when?
When an incident hits, the first hour decides a lot. Instinct says pull the plug, but powering off can destroy the evidence you need. Isolate from the network instead, and call the people you lined up in advance: IT, your insurer, legal. Who's on your call list today?
Most cyber attacks on small businesses aren't clever. They're a reused password, a missed patch, or one clicked link. The fixes are boring and they work. The hard part is doing them consistently, not knowing what they are. What's the basic yours keeps putting off?

Final week of Cyber Awareness Month: handling it when something goes wrong. Every business has an incident eventually. The ones that cope decided in advance who does what, who to call, and what to tell customers. Panic is optional. Do you have a plan, or just hope?
Source: The Hacker News. thehackernews.com/2026/10/ur…

Monday's critical PHP flaws are now under mass attack: exploit attempts jumped from tens of thousands to millions, with botnet malware in the payloads. The reassuring part: patched servers are holding; no confirmed breaches. The gap is patching speed. Have you patched?
Source: The Hacker News. thehackernews.com/2026/10/ur…
Ransomware recap: assume you're a target, keep an offline backup you've tested, close the basics (MFA, patching, remote access), and remember paying is no guarantee. The real test is recovery time, not luck. Not sure what yours is? A quick cyber health check shows you.
Ransomware rarely kicks the door in. It walks through a phished password, an exposed remote-access port, or an unpatched server. The same boring basics stop it: MFA, patching, and locking down remote access. Which of those three is weakest for you?

The ransom is rarely the biggest cost of ransomware. It's the days or weeks of downtime and clean-up. And paying is no guarantee: decryption often fails or crawls, and it marks you as a payer. Recovery beats ransom every time. Do you have a tested way back?
Most UK firms hit by ransomware had backups. The problem: they'd never tested a restore, or the backups were online and got encrypted too. A backup you haven't restored from is a hope, not a plan. Keep one copy offline or immutable. When did you last test a full restore?
This week: ransomware. The mindset shift that matters: stop asking 'will we be hit' and start asking 'how fast could we recover.' Most can answer the first, not the second. Tested backups and a clear plan turn a disaster into a bad day. Could you recover by Friday?
MFA recap: turn it on everywhere, not just email; prefer an app or key over SMS; don't forget VPN, admin and finance. The cheapest, highest-impact move in security. Want to know your gaps? A quick cyber health check maps them. What's still on your list?
Most businesses switch on MFA for email and stop there. The gaps attackers love: remote access and VPN, admin accounts, finance systems, and that one legacy app nobody wants to touch. MFA is only as good as its coverage. Which systems still log in with just a password?