


Btw i always do great things then spark turned off
Will be back tomorrow
God create us to beat our selfs
26
Words can't explain how much im happy cuz im back
I just used another technic for studying,i was using this on my mid school reversed learning it's not normal but make me curious to know the question answer so i go search for answer and get it
Thank God
30
1/7 basics
Linux looks interesting tbh
-rwxrwxrwx
user then group then others
chmod vs chown
ip insted of ifconfig
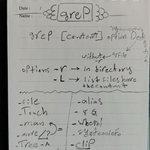
Grep
Tree
Cd /d
Crontab
Var/log
38
1/7 basics
I just reviewed network basics and it's seems cool
-tcp is not secure itself but it's using 3 ways handshake
-i look up for STP (spanning tree protocol) but ithink i have some issues with understand it
- i understand the osi model more better than before
33

ZERO retweeted

I once got to the final stage interview for what I thought was my DREAM job. I even crushed the final. Then I got stock email saying they went with another candidate. No feedback. I was crushed.
Then 5 months later I did $40k their BBP over 2 weeks.
Things happen for a reason.
ZERO retweeted

كيف قدرنا نكتشف ثغرة؟
🔴Secondary Context Leads to Full Company Takeover
كيف قدرنا نوصل انا و لا
🔺 تحكم كامل على اكثر من 3,000 الاف شركة وجميع الفروع المسجلة
🔺جميع بصمات وهويات الموظفين والمستخدمين
🔺 وصول وتحكم كامل على جميع حسابات المستخدمين
🔺اضافة بيانات حساسة الى قاعدة البيانات
🔺وصول الى جميع الدومينز الداخلية
🔺 وكيف قدرنا نتخطى الثغرات السابقة من خلال التكنيك هذا
نسمي بالله ونبدا
خلونا بالبداية نشرح كيف قدرنا نكتشف الثغره قبل كل شيء عشان تكون الصورة واضحة
اثناء فحصنا للموقع قدرت اني اسبب خطأ من خلال تلاعبي بال Request وطلع لي Error غريب بال Response مثل مانلاحظ
مثل مانلاحظ ان ال path بال Response مختلف تماما عن ال path الي موجود بال Request
من اول نظرة عرفنا انه هذا ال path الي يتم استعماله ك Backend API فالعملية الي تصير نفس كذا
اول سؤال جاء ببالي هل ممكن اني اوصل الى ال Backend API ؟
طيب عمر قبل سؤالك ذا وش الفايده اذا وصلت الى ال backend API؟
بكل اختصار دايما ال Backend API يكون عباره عن Internal domain
بمعنى اذا قدرت توصل له يمديك توصل الى مسارات وبيانات واشياء مره كثيره وهذا الي راح نشوفه بالمقالة (;
في اول محاولتنا الى الوصول الى ال Backend API حاولنا انه نسوي traversal بمعنى انه نحاول نخلي ال Backend يوصله path محدد
ولكن للأسف كان فيه WAF يمنعنا من انه نسوي Path traversal
وهنا حاولنا ندور تخطي بأكثر من طريقة ولكن للأسف كان ال WAF يمنعنا
كملت عملية البحث وقلت خل اشيك على ال JS Files شفت بال JS files ال domain معرف (الي فيه WAF)
ولكن لقيت ايضا API domain اخر معرف وقررنا نشيك عليه
بعد ماشيكت عليه طلع نفسه نفس ال API الأساسي ولكن ماكان فيه أي WAF!
على طولت رحت اجرب اني اسوي Path traversal
تكملة ⬇️


ZERO retweeted

إِنَّ اللَّهَ ومَلَائِكَتَهُ يُصلُّونَ عَلَى النَّبِيِّ يَا أَيُّهَا الَّذينَ آمَنُوا صَلُّوا عَلَيْهِ وَسَلِّمُوا تسلِيماً .
ZERO retweeted

Bug Bounty Tips: Extract API Endpoints and Construct Complex HTTP Requests from JavaScript Files Using AI
Stuck analyzing complex JS files while manually hunting on a target and can't figure out how to construct those GET/POST requests? 🤯 No fancy tools needed!
👉 Quick tip: Copy the JS file from your Chrome Dev Console, save it locally, and upload it to ChatGPT. Use this prompt:
"Could you read this JavaScript file and help me construct GET/POST endpoints?"
Then, ask for specific requests like:
"Can you help me construct the API request for getUserDetails with a raw HTTP example based on the JavaScript file uploaded?" and other similar questions based on the functionality you're looking into within the JavaScript source code.
You’ll be amazed by the results as ChatGPT constructs these complex GET/POST requests with parameters based on the AI code review—making what seemed impossible at first glance possible! 🚀
Once you have this information, you can start manually testing the endpoints with your cookies to test for IDORs, SQLi, CSRF, Privilege Escalations, XSS, etc.
#BugBountyTips #SourceCode #Infosec #HackerOne #BugCrowd 🕵️♂️🎯