

Security for code that moves money. Blockchain & Smart Contract , Applications Security Experts • Building security tools.
Securing Digital Assets
Joined May 2024
- Tweets438
- Following65
- Followers981
- Likes606






Pinned Tweet
🏆 The results are in!
Out of 180 teams, 10 have been selected for the $40,000 Crypto World's Fair Audit Grant!
Congratulations to all the winners! 🎉
@PredgeAI @PHPRail @GetPrivacySafe @corium_so @Heresprotocol @whoigital @akashi_finance @chartrunner_xyz @tryrunner @VentrionLabs
Proud to make this happen alongside @colosseum @SuperteamEarn @superteam @solana @ethereum @Zcash @arbitrum @RobinhoodCrypto @base @HyperliquidX
Didn't make the list? If you're still looking for a security assessment, we'd be happy to chat and offer special discounted rates to participating teams.
Keep building! 🚀

$6.3B. One major security failure.
The Binance incident proves that even the biggest players aren't immune.
No smart contract exploit. Just a reminder that security is only as strong as its weakest layer.

23
22
505

Apply soon 🙌


Your Colosseum build survived the hackathon.
Now see if it survives an audit.
@vaultlinesec is offering up to $4,000 in audit services per project to Solana teams getting ready to launch or scale.
Security is what lets builders and users trust Web3, so we're giving back to the ecosystem that's supported us.
We're offering 10 audit grants worth up to 4,000 USDC each to Solana projects from the Colosseum Hackathon, to help teams launch and scale securely.
📅 Apply by Oct 31
📣 Winners announced Nov 2
@superteam @colosseum

Huge thanks to @Wigby for helping make this happen 🙏
superteam.fun/earn/listing/v…
#Solana #Web3Security #Colosseum #SuperteamNL #SmartContractAudit

2
7
178

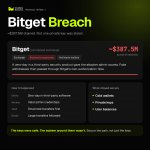
Bitget breach: ~$387.5M drained.
No private keys stolen.
The attack came through compromised third-party software.
Secure the entire system, not just the keys.
Read here : vaultlinegroup.com/blog/bitg…

5
105
Another reminder that in Web3, the attack surface goes beyond the code.
From unshipped fixes to oracle manipulation and module vulnerabilities — every layer matters.
🔐 Build. Review. Test. Secure.

1
5
79


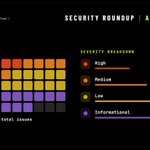
Not every crypto hack starts with a code bug.
Sometimes, the real weakness is in the economics, oracles, and governance.
Here’s what recent incidents reveal.

1
4
75

🚨 IMPORTANT REBRANDING ANNOUNCEMENT 🚨
We’re excited to announce that 0xTeam Space is now Vaultline Security.
Same engineers. Same mission. A bigger vision.
Blockchain. Application. AI. One firm. Full-stack security.
New name. Same fight.
Solving Security’s Hardest Problems.
Welcome to Vaultline Security. 🛡️

1
7
394
AI agents are starting to trust and act on behalf of other AI agents.
But when trust becomes automated, security becomes critical.
Read 👉 0xteam.space/blog/when-ai-ag…

1
4
69
AI agents are starting to trust and act on behalf of other AI agents.
But when trust becomes automated, security becomes critical.
Read👉 0xteam.space/blog/when-ai-ag…

4
58
Smart contract audits were built for code.
But AI agents are changing the attack surface.
When an autonomous agent can access wallets, call contracts, use APIs, and make decisions, security can no longer stop at the smart contract.
The question is no longer just “Is the code secure?”
It’s also “Can the agent be trusted with what it can do?”
Read more 👇
0xteam.space/blog/beyond-cod…

1
4
79
Some of the biggest exploits in Web3 history didn’t just come from bad code.
Cross-chain bridges have become one of the industry’s biggest attack surfaces—putting billions at risk.
We break down some of the most expensive cross-chain bridge hacks and what we can learn from them.
Read the full blog
0xteam.space/blog/most-expen…

5
71
