

Aut viam inveniam aut faciam.
California
Joined August 2024
- Tweets935
- Following103
- Followers4.3K
- Likes1.6K




Very nice writeup and chain, which lead from SSRF to RCE! ♟️
sonicwall.com/blog/plex2shel…

Hey @Bugcrowd, what’s the point of the RaR feature if requests go unanswered? I’ve been waiting over two months for a response now
P.S. If you need a hand clearing the queue, I’m happy to help
Critical of the week: logged 💥
Tip: If you find something weird or maybe something that doesn't have much impact on it's own, chances are high that there will be something bigger, if you keep digging👆👃


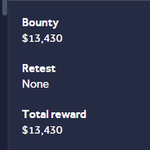
First 5-digit bounty! Finally hit that High on GitLab after multiple dupes! 💥💥
Persistence pays off.


Very helpful video on how to attack complex/hardened systems by @alisaesage, if you didn't see it yet 🧠
This applies to web bug bounty hunting as well!
youtube.com/watch?v=AbWdNaOF…
Found this very interesting article about SSRF and abusing microservices - maybe it's gonna help someone!
synack.com/exploits-explaine…

Here is a payload which might work for you, if you got an XSS, but it's blocked by Cloudflare WAF💥
Was able to bypass Cloudflare WAF with this and escalated it ultimately to ATO!

Is it just me or do various bug bounty platforms feel increasingly worse?
First response and triage experience has gone downhill big time. I have multiple P2/High severity reports that are 15-30 days old that weren’t even looked at by triage yet..
Here is a little dork for you, if you wanna learn a thing or two about Client-Side Vuln Hunting!
site:blog.criticalthinkingpodcast… "client-side"
Another nice filter bypass - Can recommend!
I just pwned the "Dojo #50 - Bucket Vault" challenge on @YesWeHack!
dojo-yeswehack.com/challenge…

Another high-impact GitLab vuln found 💥
Ended up duplicate, but this one involved a nice server-side filter bypass.
Getting closer, I’m not stopping until I land that paid High on GitLab!

A nice IDOR that gave access to essentially every user's private data 💥
Reported -> Triaged -> 2 months later marked as "Internal Duplicate" by the company🫠
Tip: Go deep into the app, you might find endpoints for paid features that are still accessible

Just published a new writeup about a nice chain that led to credit card theft, including a stored XSS, cookie tossing and cookie jar action 💥
Unfortunately, this was marked as informational and my disclosure request was denied lol
medium.com/@YourFinalSin/fro…

This is a very interesting approach on bypassing DOMPurify via String.replace
It was for a CTF, but I'm pretty sure it could come in very handy 💀
Kudos to @_tomek7667, insane job!
youtube.com/watch?v=mniM5H5x…

First report accepted and paid on GitLab! 💥
Tip: Learn as much as you can about your target from public data/reports, before you start hunting on them

Was playing around with prompt injections today and leaked ChatGPT 5.2 internal tooling, metadata and parts of the System Prompt 💥


The best writeups I stumbled upon today when reading up about stuff - mainly postMessage related:
- monke.ie/p/exfiltrating-data…
- spaceraccoon.dev/universal-c…
- imperva.com/blog/imperva-red…
Although I think the Imperva one could've been an ATO 🤔